


 Pierluigi Paganini
 November 24, 2021
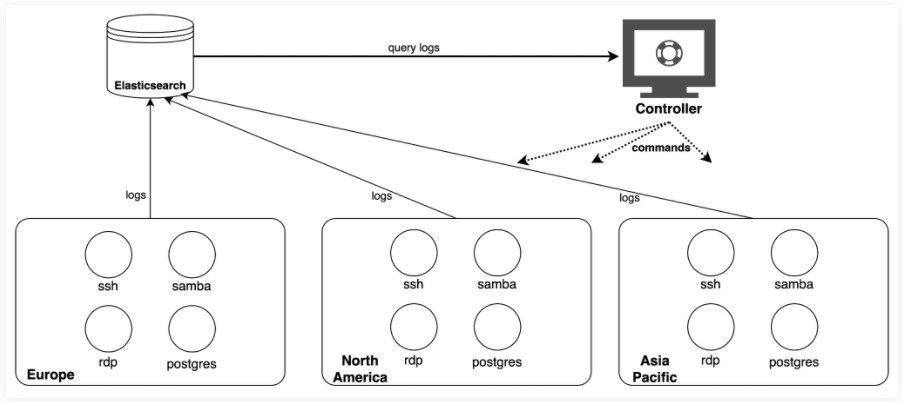
Researchers deployed multiple instances of vulnerable systems and found that 80% of the 320 honeypots were compromised within 24 hours. Researchers from Palo Alto Networks deployed a honeypot infrastructure of 320 nodes to analyze how three actors target exposed services in public clouds. The company set up the honeypots between July 2021 and August 2021 to […]
 Pierluigi Paganini
November 24, 2021
A vulnerability in Oracle VM VirtualBox could be potentially exploited to compromise the hypervisor and trigger a denial-of-service (DoS) condition. A vulnerability in Oracle VM VirtualBox, tracked as CVE-2021-2442, could be potentially exploited to compromise the hypervisor and trigger a DoS condition. The vulnerability was discovered by Max Van Amerongen from SentinelLabs, it received a CVSS […]
 Pierluigi Paganini
November 23, 2021
A flaw in CloudLinux’s Imunify360 security product could have been exploited by an attacker for remote code execution. Cisco’s Talos researchers discovered a remote code execution vulnerability, tracked as CVE-2021-21956, in CloudLinux’s Imunify360 security product. Imunify360 is a security platform for web-hosting servers that allows to implement real-time protection for website and web servers. The […]
 Pierluigi Paganini
November 23, 2021
A researcher has released a proof-of-concept exploit code for an actively exploited vulnerability affecting Microsoft Exchange servers. The researcher Janggggg has published on Sunday a proof-of-concept exploit code for an actively exploited vulnerability, tracked as CVE-2021-42321, in Microsoft Exchange servers. The CVE-2021-42321 is a high-severity remote code execution issue that occurs due to improper validation of […]
 Pierluigi Paganini
November 23, 2021
A researcher publicly disclosed an exploit for a new Windows zero-day local privilege elevation that can allow gaining admin privileges. A security researcher has publicly disclosed an exploit for a new Windows zero-day local privilege elevation vulnerability that can be exploited by threat actors to achieve admin privileges in Windows 10, Windows 11, and Windows […]
 Pierluigi Paganini
November 23, 2021
US CISA and the FBI issued a joint alert to warn critical infrastructure partners and public/private organizations of ransomware attacks during holidays. The Cybersecurity and Infrastructure Security Agency (CISA) and the FBI warn critical infrastructure partners of ransomware attacks during the holiday season. During this period offices are often closed and employees are at home, […]
 Pierluigi Paganini
November 22, 2021
Iranian airline Mahan Air was hit by a cyberattack on Sunday morning, the “Hooshyarane Vatan” hacker group claimed responsibility for the attack. Iranian private airline Mahan Air has foiled a cyber attack over the weekend, Iranian state media reported. The airliner’s flight schedule was not affected by the cyberattack. “Our international and domestic flights are […]
 Pierluigi Paganini
November 22, 2021
The Securities and Exchange Commission (SEC) warns investors of attacks impersonating its officials in government impersonator schemes. The Securities and Exchange Commission (SEC) is warning investors of scammers impersonating SEC officials in fraudulent schemes. According to the alert issued by the SEC’s Office of Investor Education and Advocacy (OIEA), crooks are contacting investors via phone […]
 Pierluigi Paganini
November 21, 2021
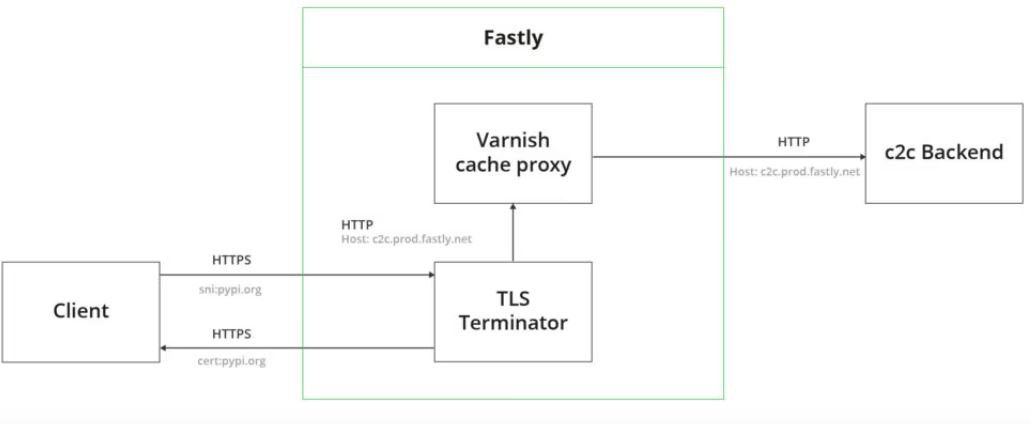
Researchers discovered 11 malicious Python packages in the PyPI repository that can steal Discord access tokens, passwords, and conduct attacks. JFrog researchers have discovered 11 malicious Python packages in the Python Package Index (PyPI) repository that can steal Discord access tokens, passwords, and even carry out dependency confusion attacks. Below is the list of malicious […]
 Pierluigi Paganini
November 21, 2021
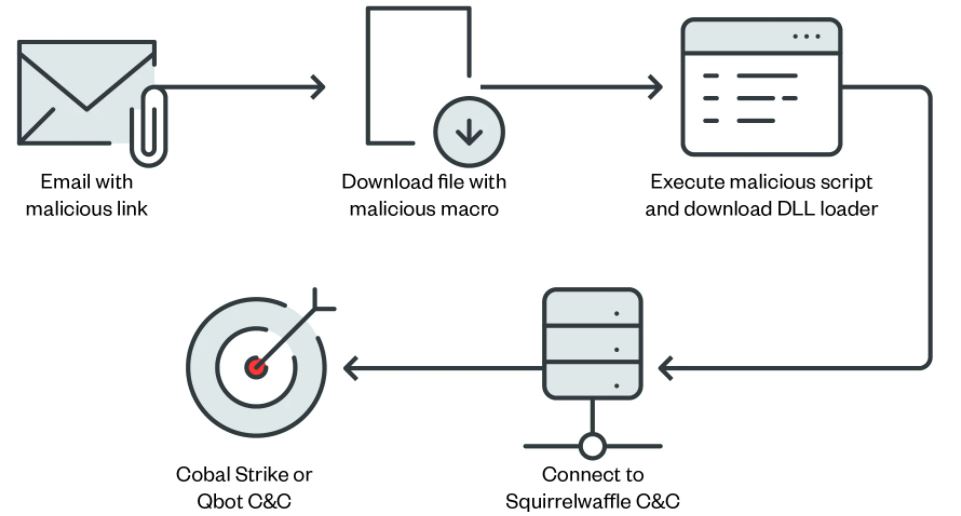
A malware campaign aimed at Microsoft Exchange servers exploits ProxyShell and ProxyLogon issues and uses stolen internal reply-chain emails. A malware campaign aimed at Microsoft Exchange servers exploits ProxyShell and ProxyLogon issues and uses stolen internal reply-chain emails to avoid detection. The campaign was uncovered by TrendMicro researchers that detailed the technique used to trick […]




