


 Pierluigi Paganini
 November 19, 2021
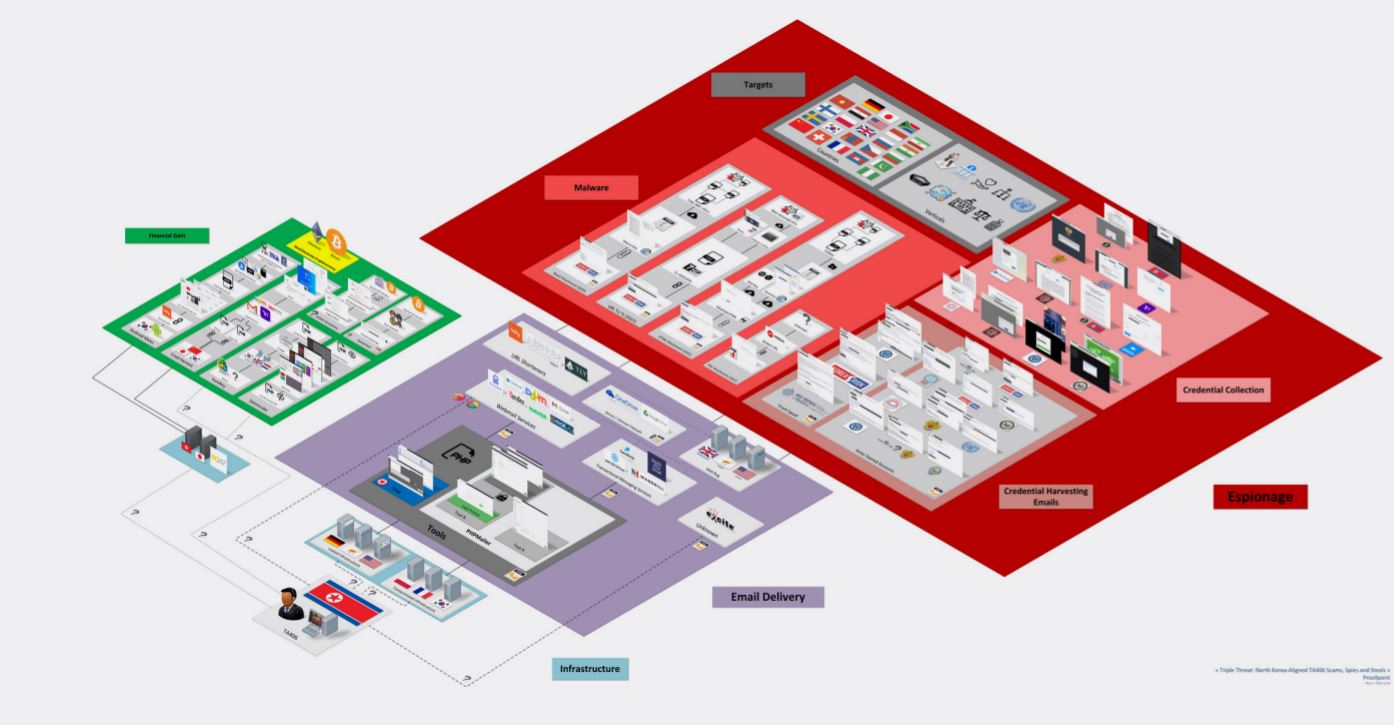
North Korea-linked TA406 APT group has intensified its attacks in 2021, particularly credential harvesting campaigns. A report published by Proofpoint revealed that the North Korea-linked TA406 APT group (Kimsuky, Thallium, and Konni, Black Banshee, Velvet Chollima) has intensified its operations in 2021. The TA406 cyber espionage group was first spotted by Kaspersky researchers in 2013. At the end of October […]
 Pierluigi Paganini
November 19, 2021
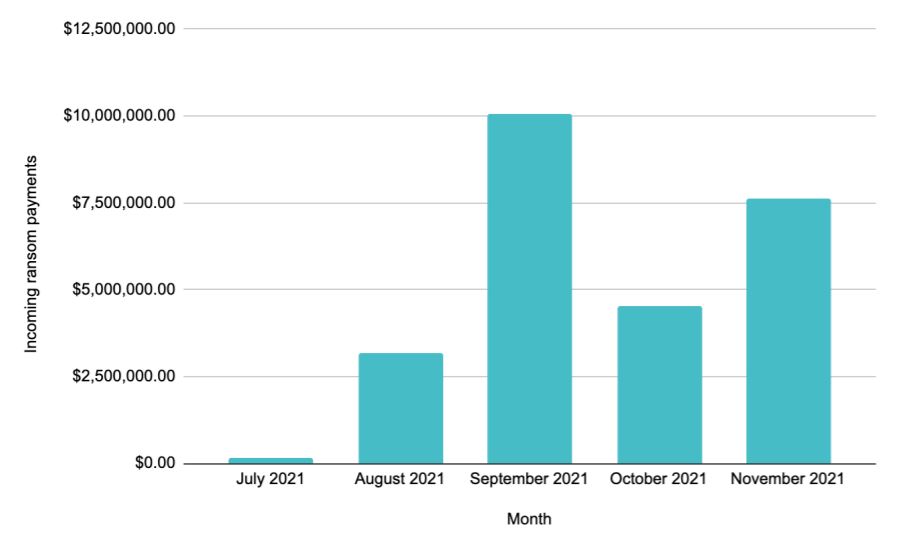
Researchers revealed that Conti ransomware operators earned at least $25.5 million from ransom payments since July 2021. A study conducted by Swiss security firm Prodaft with the support of blockchain analysis firm Elliptic revealed that the operators of the Conti ransomware have earned at least $25.5 million from attacks and subsequent ransoms carried out since […]
 Pierluigi Paganini
November 18, 2021
Researchers discovered threat actors installing a Linux backdoor on compromised e-commerce servers after deploying a credit card skimmer into e-stores. Security researchers from Sansec Threat Research Team discovered a Linux backdoor during an investigation into the compromised of an e-commerce server with a software skimmer. The attackers initially conducted a reconnaissance phase by probing the […]
 Pierluigi Paganini
November 18, 2021
Threat actors have launched a phishing campaign targeting more than 125 TikTok ‘Influencer’ accounts in an attempt to hijack them. Researchers from Abnormal Security uncovered a phishing scam aimed at hijacking at least 125 TikTok ‘Influencer’ accounts. The original phishing email used a TikTok copyright violation notice lure, the messages instructed the victims responding to […]
 Pierluigi Paganini
November 18, 2021
U.S., U.K. and Australia warn that Iran-linked APT groups exploiting Fortinet and Microsoft Exchange flaws to target critical infrastructure. A joint advisory released by government agencies (the FBI, the Cybersecurity and Infrastructure Security Agency (CISA), the Australian Cyber Security Centre (ACSC), and the United Kingdom’s National Cyber Security Centre (NCSC)) in the U.S., U.K., and […]
 Pierluigi Paganini
November 17, 2021
Netgear addressed a code execution vulnerability, tracked as CVE-2021-34991, in its small office/home office (SOHO) devices. Netgear addressed a pre-authentication buffer overflow issue in its small office/home office (SOHO) devices that can be exploited by an attacker on the local area network (LAN) to execute code remotely with root privileges. The flaw, tracked as CVE-2021-34991 […]
 Pierluigi Paganini
November 17, 2021
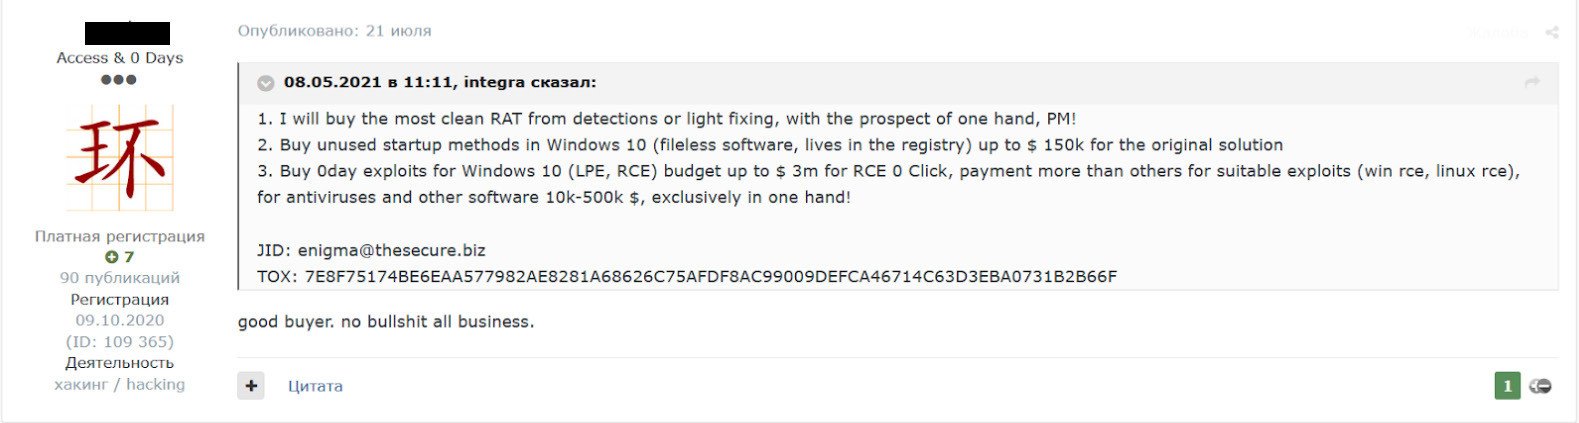
Researchers detailed the multi-millionaire market of zero-day exploits, a parallel economy that is fueling the threat landscape. Zero-day exploits are essential weapons in the arsenal of nation-state actors and cybercrime groups. The increased demand for exploits is fueling a millionaire market where these malicious codes are incredibly expensive. Researchers from Digital Shadows published an interesting […]
 Pierluigi Paganini
November 17, 2021
The researchers at Microsoft Threat Intelligence Center (MSTIC) are warning of increasingly sophisticated operations carried out by Iranian threat actors. The Microsoft Threat Intelligence Center (MSTIC) shared the results of their analysis on the evolution of Iran-linked threat actors at the CyberWarCon 2021. Over the past 12 months, MSTIC experts observed increasingly sophisticated attacks orchestrated […]
 Pierluigi Paganini
November 15, 2021
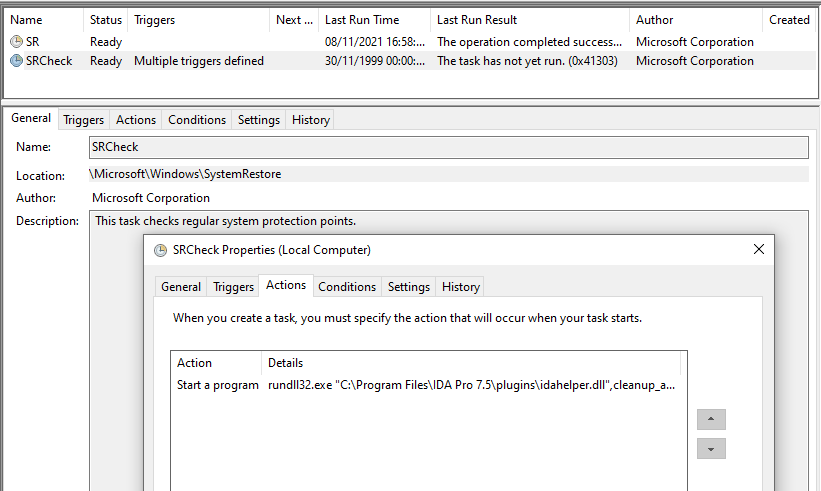
North Korea-linked APT Lazarus targets security researchers using a trojanized pirated version of the popular IDA Pro reverse engineering software. ESET researchers reported that the North Korea-linked Lazarus APT group is targeting cyber security community with a trojanized pirated version of the popular IDA Pro reverse engineering software. Threat actors bundled the IDA Pro 7.5 […]
 Pierluigi Paganini
November 15, 2021
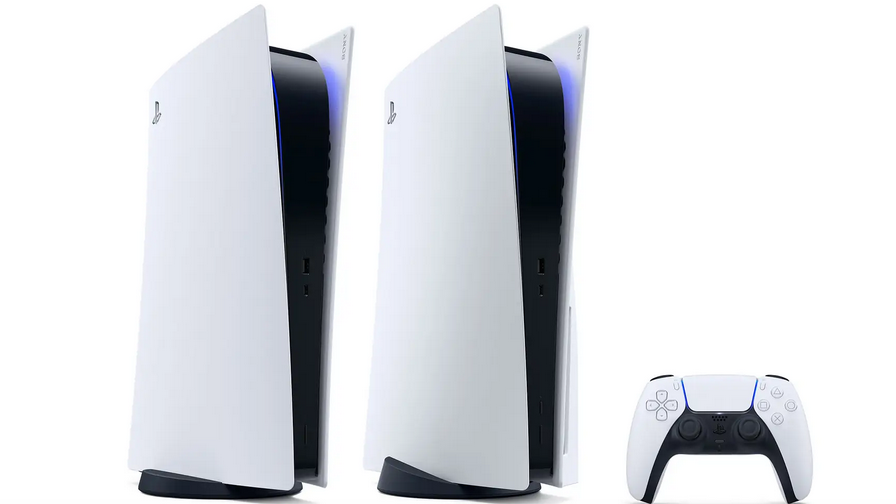
Threat actors stole PS5 root keys using kernel exploits demonstrating the need to improve the security of the popular gaming console. Threat actors stole Sony PS5 root keys from the popular gaming console using two exploits for kernel vulnerabilities. The two exploits weren’t disclosed to the company, the hackers published both exploits on Twitter on […]





