


 Pierluigi Paganini
 October 29, 2021
Google has released Chrome 95.0.4638.69 for Windows, Mac, and Linux to address two actively exploited zero-day vulnerabilities. Google has released Chrome 95.0.4638.69 for Windows, Mac, and Linux to address two zero-day vulnerabilities, tracked as CVE-2021-38000 and CVE-2021-38003, actively exploited in attacks in the wild. Google fixed a total of seven vulnerabilities with the latest release […]
 Pierluigi Paganini
October 28, 2021
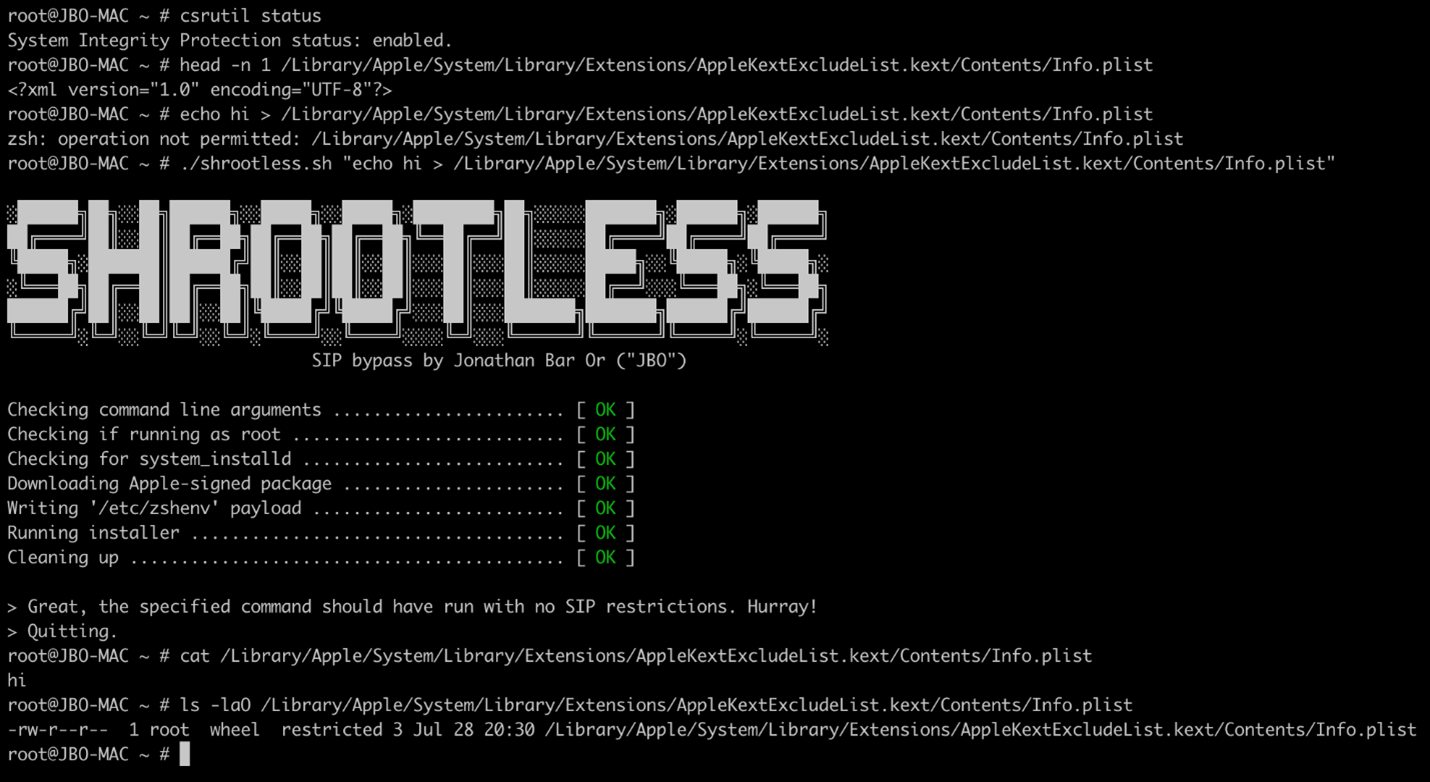
Microsoft finds a flaw in macOS, dubbed Shrootless (CVE-2021-30892), that can allow attackers to bypass System Integrity Protection (SIP). Microsoft discovered a vulnerability in macOS, dubbed Shrootless (CVE-2021-30892), that can allow attackers to bypass System Integrity Protection (SIP) and perform malicious activities, such as gaining root privileges and installing rootkits on vulnerable devices. System Integrity Protection (also referred to […]
 Pierluigi Paganini
October 28, 2021
A vulnerability in the popular the OptinMonster plugin allows unauthorized API access and sensitive information disclosure. A high-severity vulnerability (CVE-2021-39341) in The OptinMonster plugin can allow unauthorized API access and sensitive information disclosure on roughly a million WordPress sites. The flaw was discovered by Wordfence researcher Chloe Chamberland on September 28, 2021, and the development […]
 Pierluigi Paganini
October 28, 2021
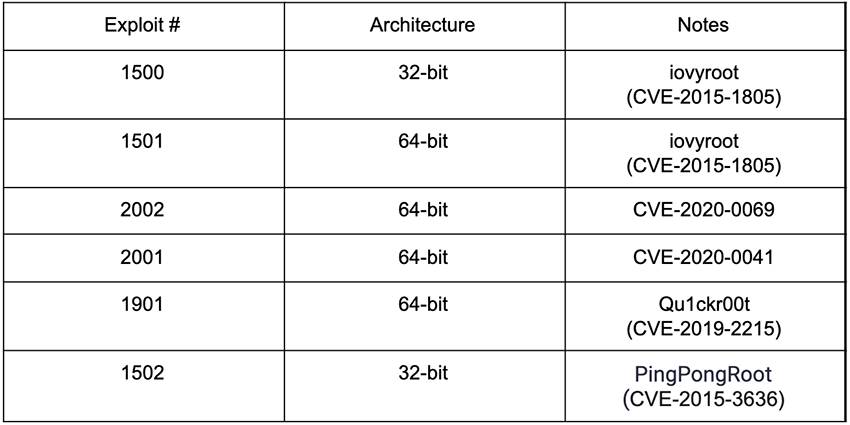
AbstractEmu is a new Android malware that can root infected devices to take complete control and evade detection with different tricks. Security researchers at the Lookout Threat Labs have discovered a new Android malware, dubbed AbstractEmu, with rooting capabilities that is distributed on Google Play and prominent third-party stores (i.e. Amazon Appstore and the Samsung Galaxy Store). The malware […]
 Pierluigi Paganini
October 27, 2021
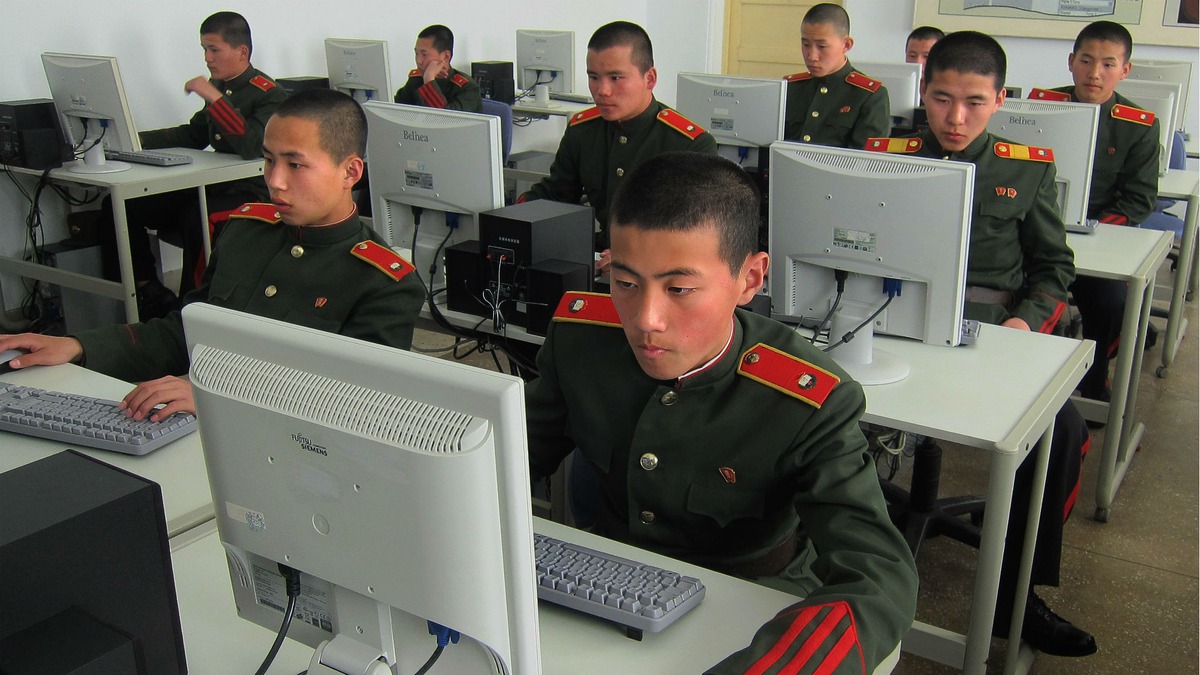
North Korea-linked Lazarus APT group is extending its operations and started targeting the IT supply chain on new targets. North Korea-linked Lazarus APT group is now targeting also IT supply chain, researchers from Kaspersky Lab warns. The activity of the Lazarus APT group surged in 2014 and 2015, its members used mostly custom-tailored malware in their attacks. […]
 Pierluigi Paganini
October 27, 2021
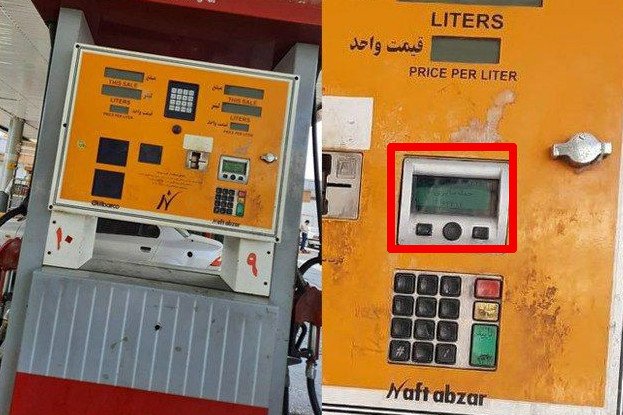
A cyberattack has disrupted gas stations from the National Iranian Oil Products Distribution Company (NIOPDC) across Iran. A cyber attack has disrupted gas stations from the state-owned National Iranian Oil Products Distribution Company (NIOPDC) across Iran. The attack also defaced the screens at the gas pumps and gas price billboards. In multiple cities, the billboards […]
 Pierluigi Paganini
October 26, 2021
A researcher from the security firm CyberArk has managed to crack 70% of Tel Aviv’s Wifi Networks starting from a sample of 5,000 gathered WiFi. CyberArk security researcher Ido Hoorvitch demonstrated how it is possible to crack WiFi at scale by exploiting a vulnerability that allows retrieving a PMKID hash. Hoorvitch has managed to crack […]
 Pierluigi Paganini
October 26, 2021
The FBI published a flash alert to warn of the activity of the Ranzy Locker ransomware that had already compromised tens of US companies. The FBI published a flash alert to warn of Ranzy Locker ransomware operations that had already compromised at least 30 US companies this year. The gang has been active since at […]
 Pierluigi Paganini
October 26, 2021
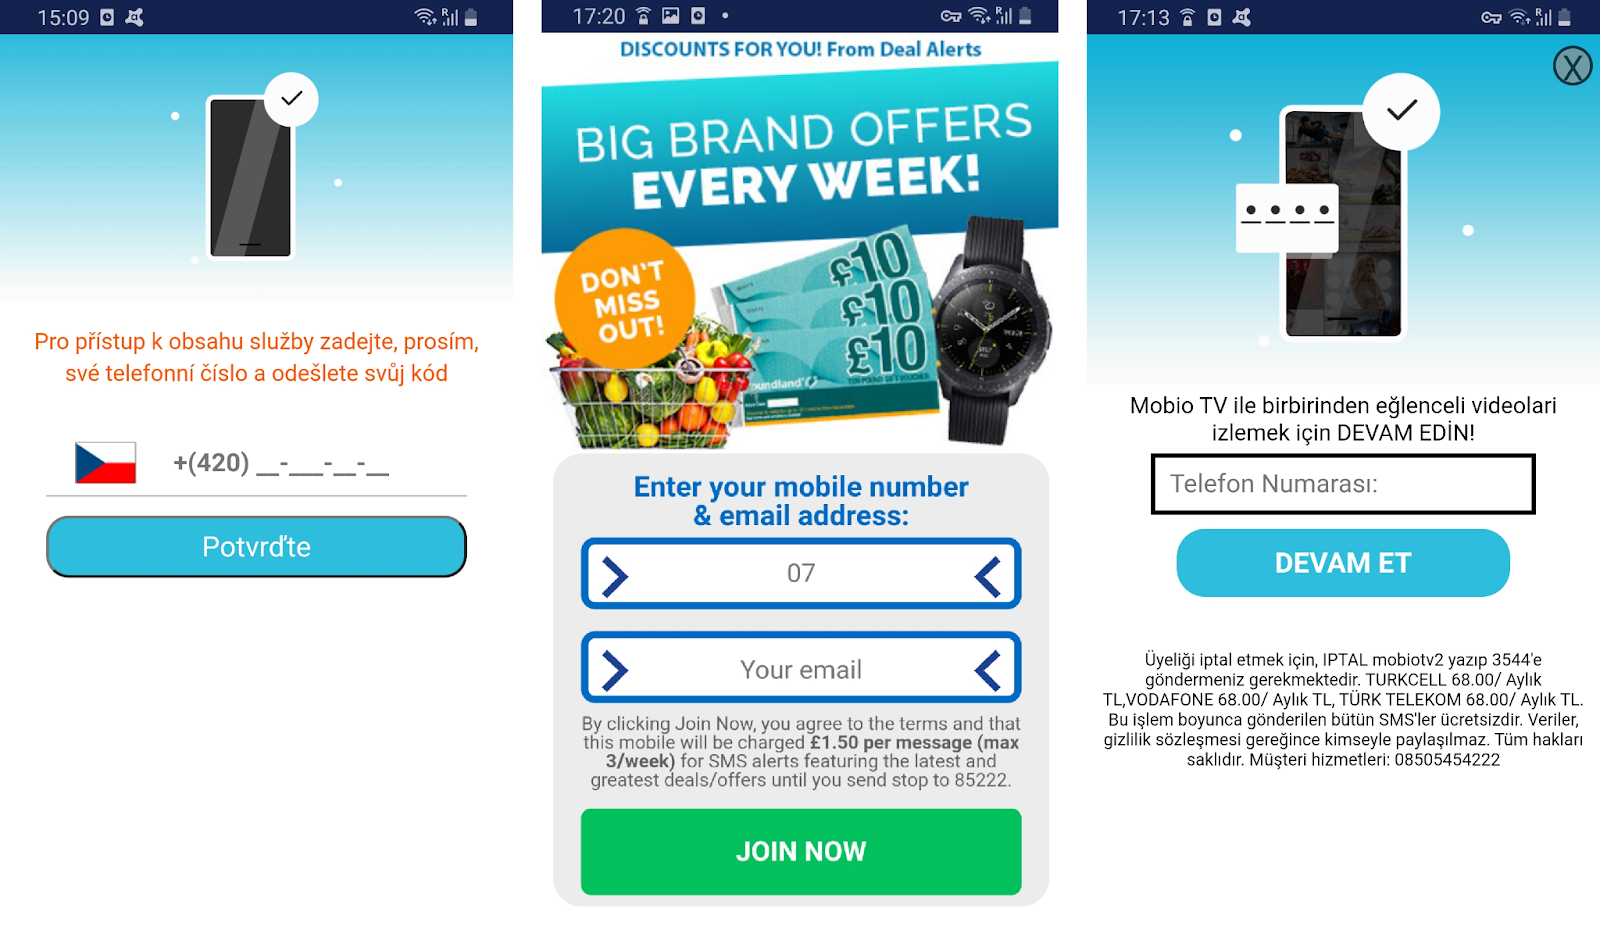
UltimaSMS, a massive fraud campaign is using Android apps with million of downloads to subscribe victims to premium subscription services. Researchers from Avast have uncovered a widespread premium SMS scam on the Google Play Store, tracked as UltimaSMS, the name comes from the first apps they discovered called Ultima Keyboard 3D Pro. Threat actors used at […]
 Pierluigi Paganini
October 25, 2021
US CISA urges administrators to address a critical remote code execution flaw, tracked as CVE-2021-41163, in Discourse installs. Discourse is a popular open-source Internet forum and mailing list management software application. The US CISA published a security advisory to urge administrators to fix a critical remote code execution flaw, tracked as CVE-2021-41163, in Discourse installs. The […]




