


 Pierluigi Paganini
 October 19, 2021
Symantec spotted a previously unknown nation-state actor, tracked as Harvester, that is targeting telecommunication providers and IT firms in South Asia. Symantec spotted a previously unknown nation-state actor, tracked as Harvester, that is using a custom implant, dubbed Backdoor.Graphon, in attacks aimed at telecommunication providers, IT firms, and government entities in South Asia. At this […]
 Pierluigi Paganini
October 18, 2021
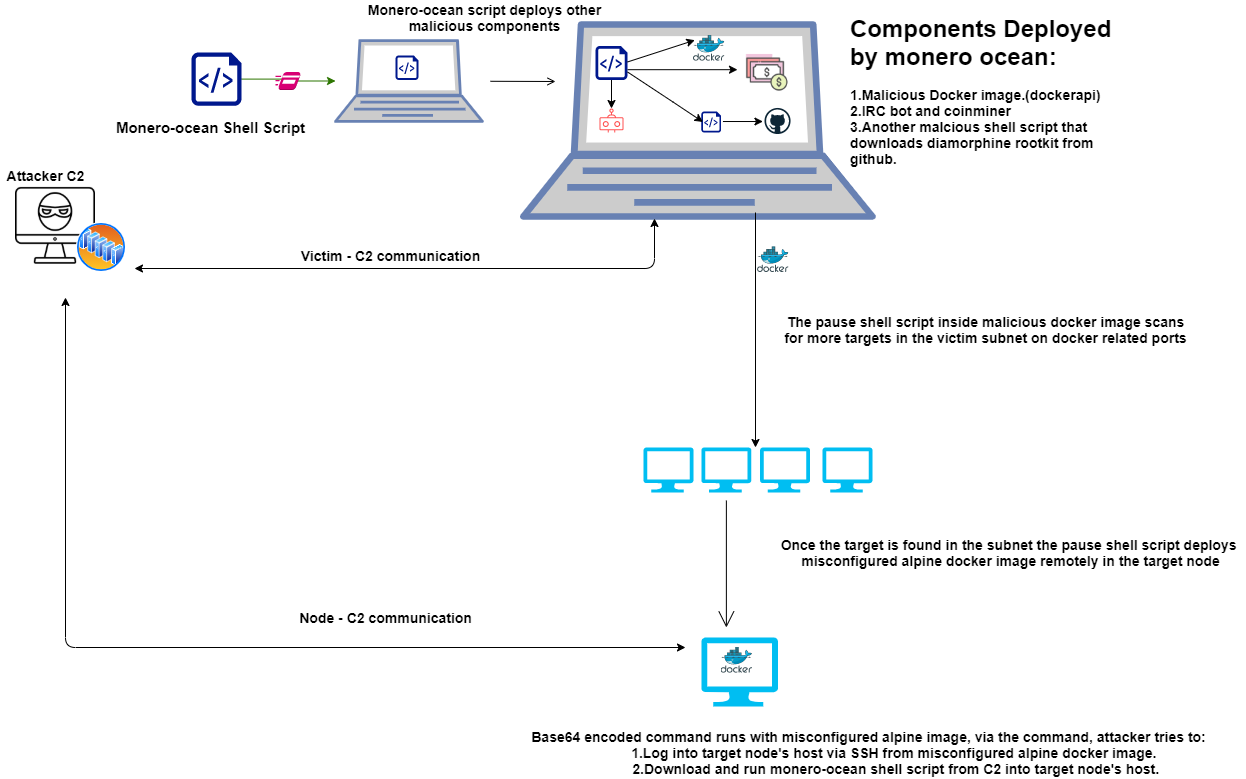
The Uptycs Threat Research Team spotted a campaign in which the TeamTNT threat actors deployed a malicious container image on Docker hub. The Uptycs Threat Research Team recently identified a campaign in which the TeamTNT threat actors deployed a malicious container image (hosted on Docker Hub) with an embedded script to download Zgrab scanner and masscanner—penetration testing tools […]
 Pierluigi Paganini
October 18, 2021
Experts discovered several unprotected installs of open source event monitoring solution Prometheus that may expose sensitive data. JFrog researchers have discovered multiple unprotected instances of open source event monitoring solution Prometheus that may leak sensitive data. The solution scrapes real-time metrics from multiple endpoints, it is used by several major organizations such as Uber. Prometheus’ […]
 Pierluigi Paganini
October 18, 2021
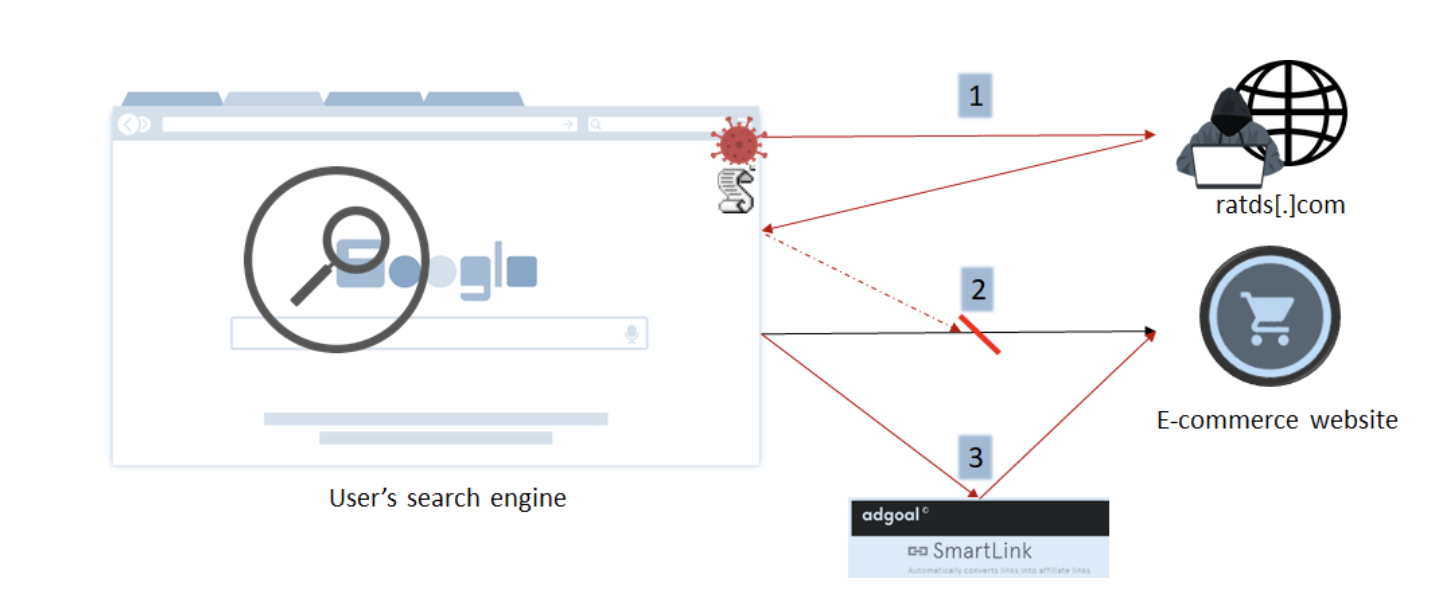
Researchers warn of an Ad-Blocking Chrome extension that was abused by threat actors to Injecting Ads in Google search pages. Researchers from Imperva have spotted a new deceptive ad injection campaign that is targeting users of some large websites leveraging an AD-blocking extension, named AllBlock, that is available on both Chrome and Opera browsers. Ad […]
 Pierluigi Paganini
October 17, 2021
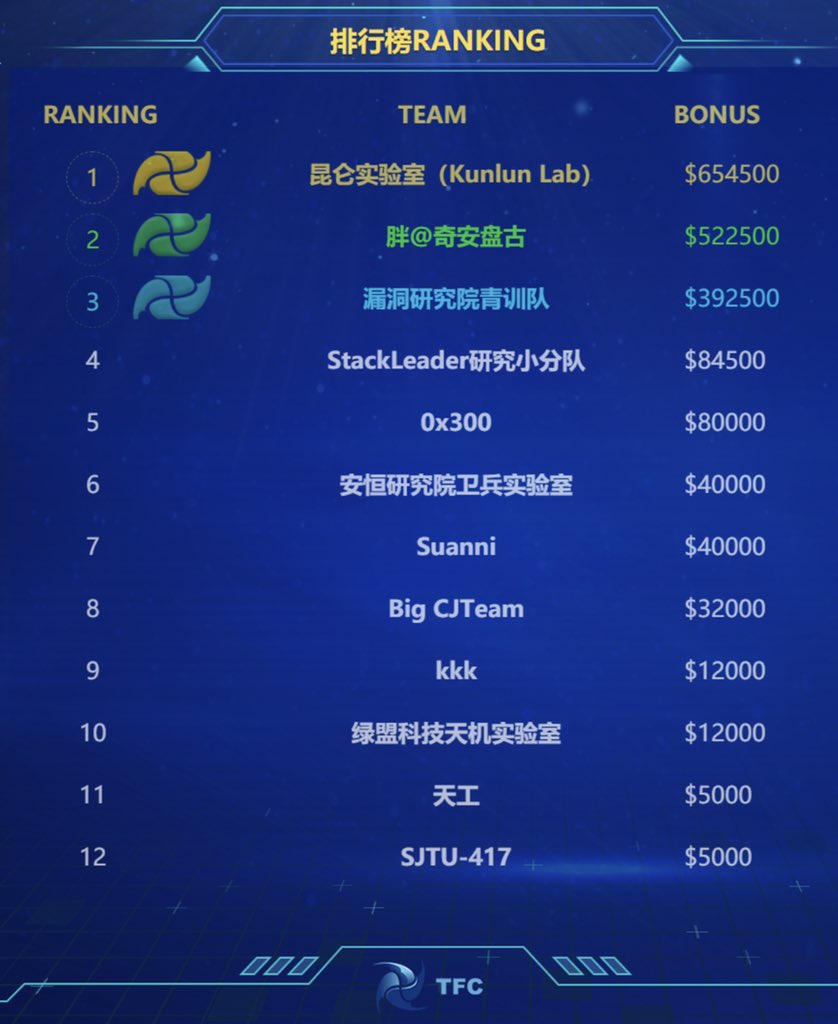
White hat hackers earned $1.88 million at the Tianfu Cup hacking contest by finding vulnerabilities in popular software. The Tianfu Cup is the most important hacking contest held in China, this year white hat hackers earned $1.88 Million demonstrating vulnerabilities in popular software. The edition of this year took place on October 16 and 17 […]
 Pierluigi Paganini
October 16, 2021
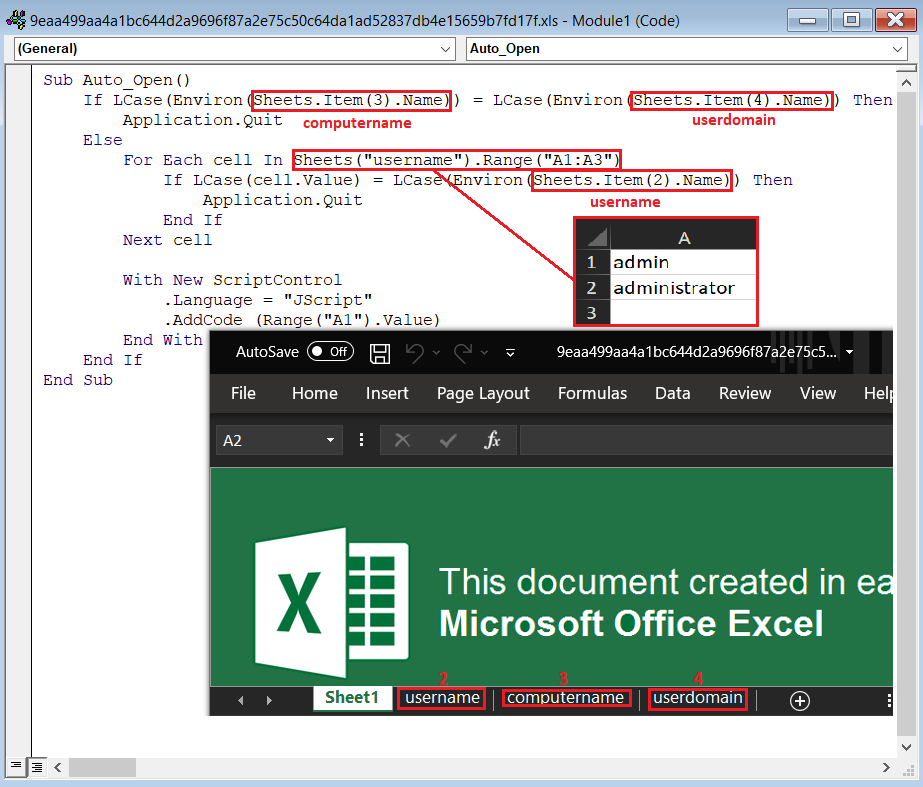
Russia-linked TA505 group leverages a lightweight Office file to spread malware in a campaign, tracked as MirrorBlast, aimed at financial institutions. Russia-linked APT group TA505 (e.g. Evil Corp) is leveraging a lightweight Office file in a new malware campaign, tracked as MirrorBlast, targeting financial institutions in multiple geographies. TA505 hacking group has been active since 2014 […]
 Pierluigi Paganini
October 15, 2021
A group of researchers from the Graz University of Technology and CISPA Helmholtz Center for Information Security devised a new side-channel attack that affects AMD CPUs. Researchers Moritz Lipp and Daniel Gruss of the Graz University of Technology and Michael Schwarz of the CISPA Helmholtz Center for Information Security devised a new side-channel attack that […]
 Pierluigi Paganini
October 15, 2021
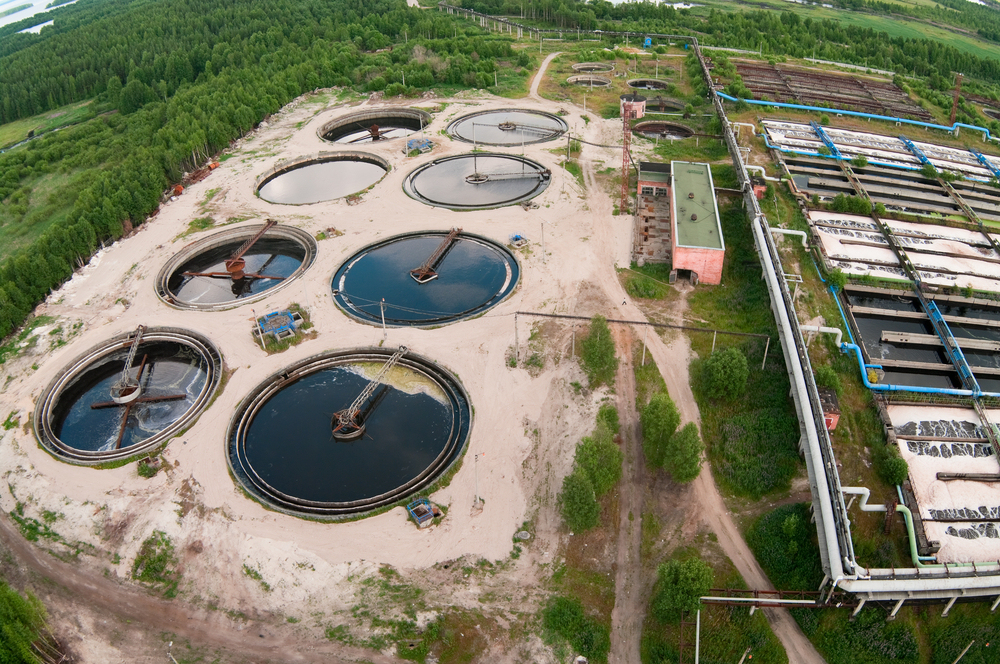
A joint cybersecurity advisory published by US agencies revealed that three ransomware attacks on wastewater systems this year. A joint cybersecurity advisory published today by the FBI, NSA, CISA, and the EPA revealed three more attacks launched by Ransomware gangs against US water and wastewater treatment facilities (WWS) this year. This is the first time that these attacks […]
 Pierluigi Paganini
October 14, 2021
The Hillel Yaffe Medical Center in Hadera, Israel, was hit by a ransomware attack that was defined by Israel’s National Cyber Directorate as a “major” attack. The Hillel Yaffe Medical Center in Hadera, Israel was hit by a ransomware attack that impacted the system of the hospital. Local media outlets reported that the hospital has […]
 Pierluigi Paganini
October 13, 2021
Apple has silently addressed a zero-day vulnerability that could allow attackers to gain access to sensitive user data. Apple has silently addressed zero-day vulnerability with the release of iOS 15.0.2, the vulnerability could allow attackers gain access to sensitive user information. The flaw was reported to the IT giant by software developers Denis Tokarev seven […]





