


 Pierluigi Paganini
 July 19, 2021
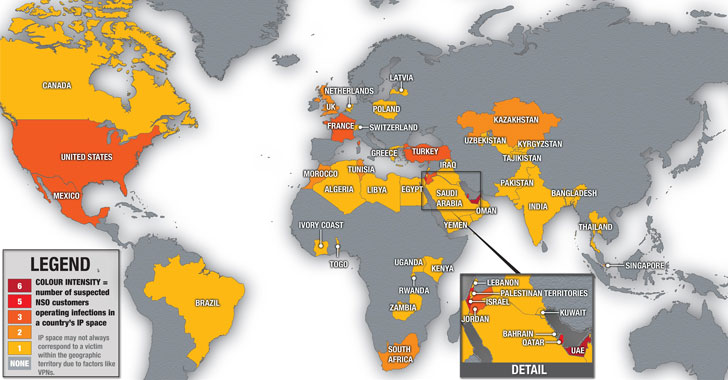
Pegasus Project investigation into the leak of 50,000 phone numbers of potential surveillance targets revealed the abuse of NSO Group’s spyware. Pegasus Project is the name of a large-scale investigation into the leak of 50,000 phone numbers of potential surveillance targets that revealed the abuse of NSO Group’s spyware. Pegasus is a surveillance malware developed by […]
 Pierluigi Paganini
July 19, 2021
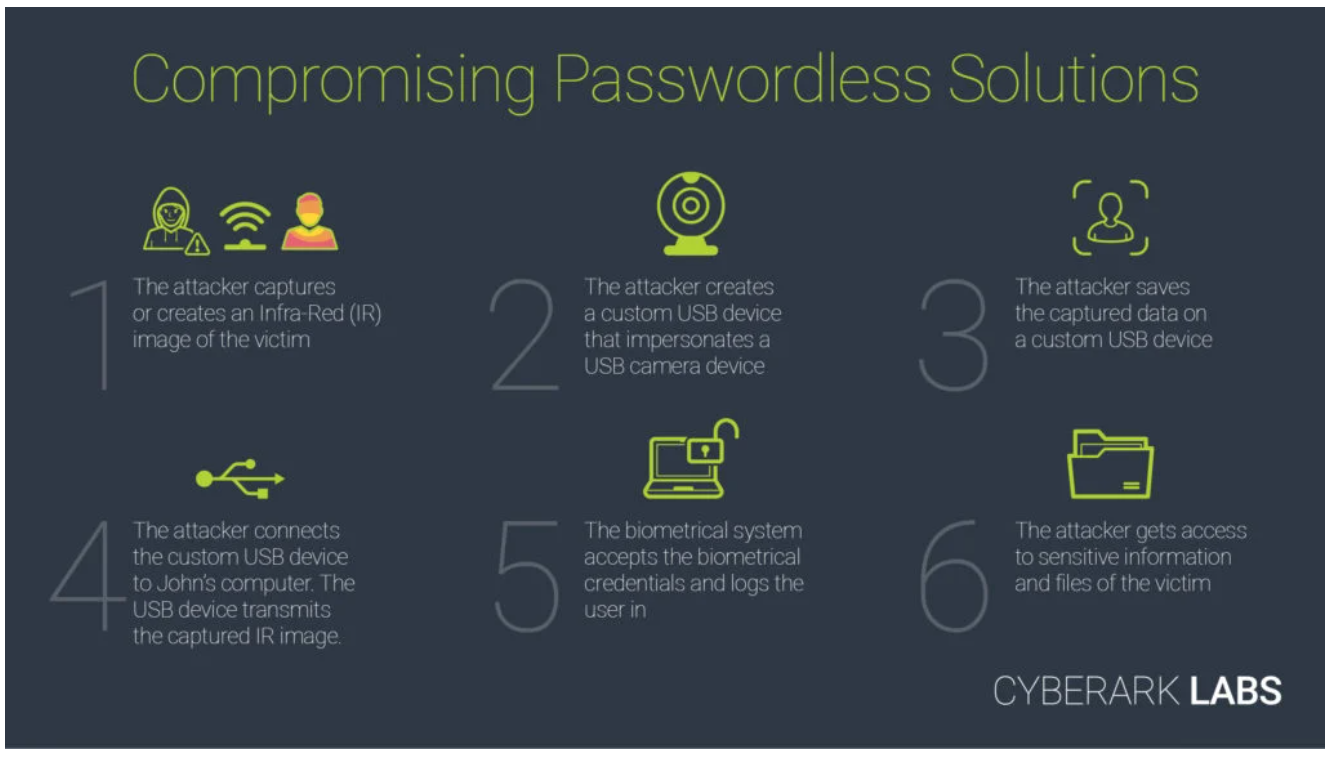
Security researchers demonstrated how to bypass the Windows Hello facial recognition that is used in Windows 10 as a login mechanism. Security researchers at CyberArk Labs discovered a security bypass vulnerability, tracked as CVE-2021-34466, affecting the Windows Hello facial authentication process, An attacker could exploit the vulnerability to login systems running the Windows 10 OS. […]
 Pierluigi Paganini
July 18, 2021
Cyberspace Administration of China (CAC) issued new vulnerability disclosure regulations that oblige experts to report zero-days to the government. The Cyberspace Administration of China (CAC) has issued a new exacerbated vulnerability disclosure regulation that requires white hat hackers uncovering critical zero-day flaws in computer systems to first report them to the government authorities within two […]
 Pierluigi Paganini
July 17, 2021
Network equipment vendor D-Link has released a firmware hotfix to fix multiple vulnerabilities in the DIR-3040 AC3000-based wireless internet router. Network equipment vendor D-Link has released a firmware hotfix to address multiple vulnerabilities affecting the DIR-3040 AC3000-based wireless internet router. An attacker could exploit the flaws to execute arbitrary code on unpatched routers, crash the devices, or gain access […]
 Pierluigi Paganini
July 15, 2021
Zero-day exploit broker Zerodium is looking for 0day exploits for the VMware vCenter Server Zero-day exploit broker Zerodium announced it is looking for zero-day exploits for VMware vCenter Server. vCenter Server is the centralized management utility for VMware, and is used to manage virtual machines, multiple ESXi hosts, and all dependent components from a single centralized location. The company will […]
 Pierluigi Paganini
July 14, 2021
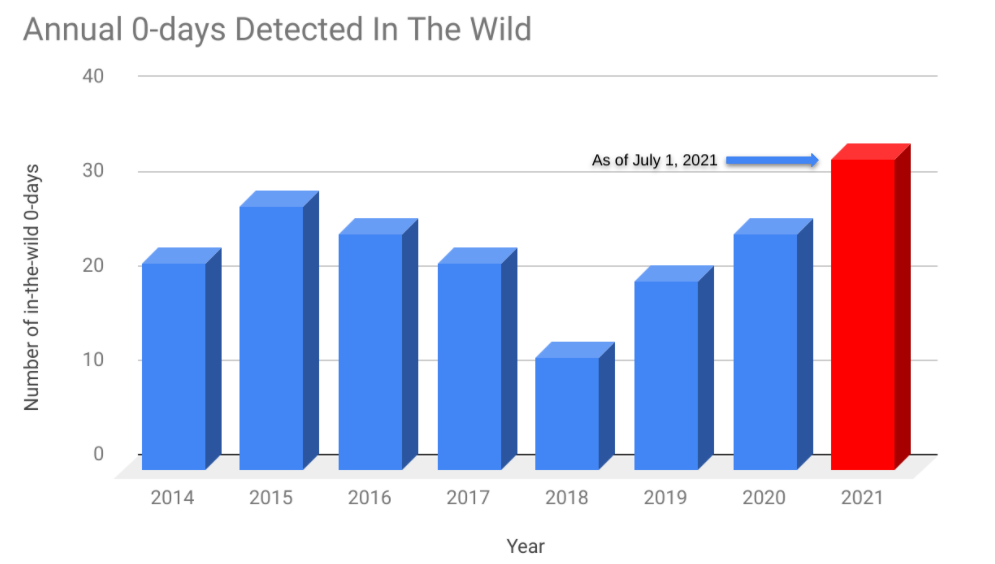
Google security experts revealed that Russia-linked APT group targeted LinkedIn users with Safari zero-day. Security researchers from Google Threat Analysis Group (TAG) and Google Project Zero revealed that four zero-day vulnerabilities have been exploited in the wild earlier this year. The four security flaws were discovered earlier this year and affect Google Chrome, Internet Explorer, and WebKit browser […]
 Pierluigi Paganini
July 14, 2021
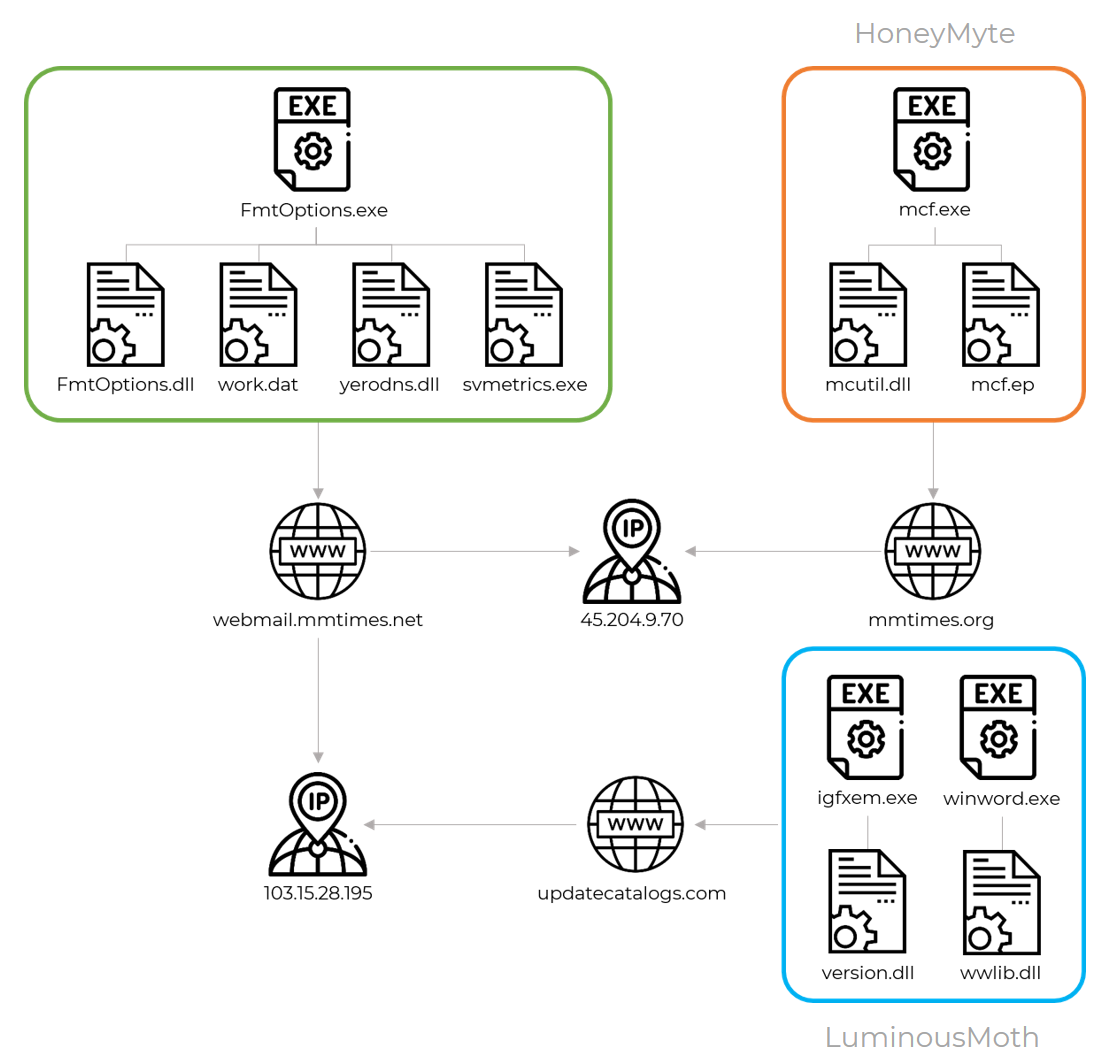
LuminousMoth: Kaspersky uncovered an ongoing and large-scale APT campaign that targeted government entities in Southeast Asia, including Myanmar and the Philippines. Kaspersky experts uncovered an ongoing and large-scale cyber espionage campaign, tracked as LuminousMoth, aimed at government entities from Southeast Asia, including Myanmar and the Philippines government entities. The LuminousMoth campaign has been linked by […]
 Pierluigi Paganini
July 14, 2021
Microsoft attributes the recent attacks that have targeted SolarWinds file transfer servers to a China-linked APT group that the experts tracked as DEV-0322. Microsoft said that the recent attacks against SolarWinds file transfer servers were carried out by a Chinese hacking group tracked as DEV-0322. This week SolarWinds addressed a zero-day remote code execution flaw (CVE-2021-35211) in Serv-U products which […]
Pierluigi Paganini
July 12, 2021
SolarWinds confirmed that a threat actor is actively exploiting a new zero-day vulnerability in Serv-U products and urges customers to fix it. SolarWinds addressed a zero-day remote code execution flaw in Serv-U products which is actively exploited in the wild by a single threat actor. SolarWinds was informed of the zero-day by Microsoft, the issue affects Serv-U Managed File Transfer […]
 Pierluigi Paganini
July 11, 2021
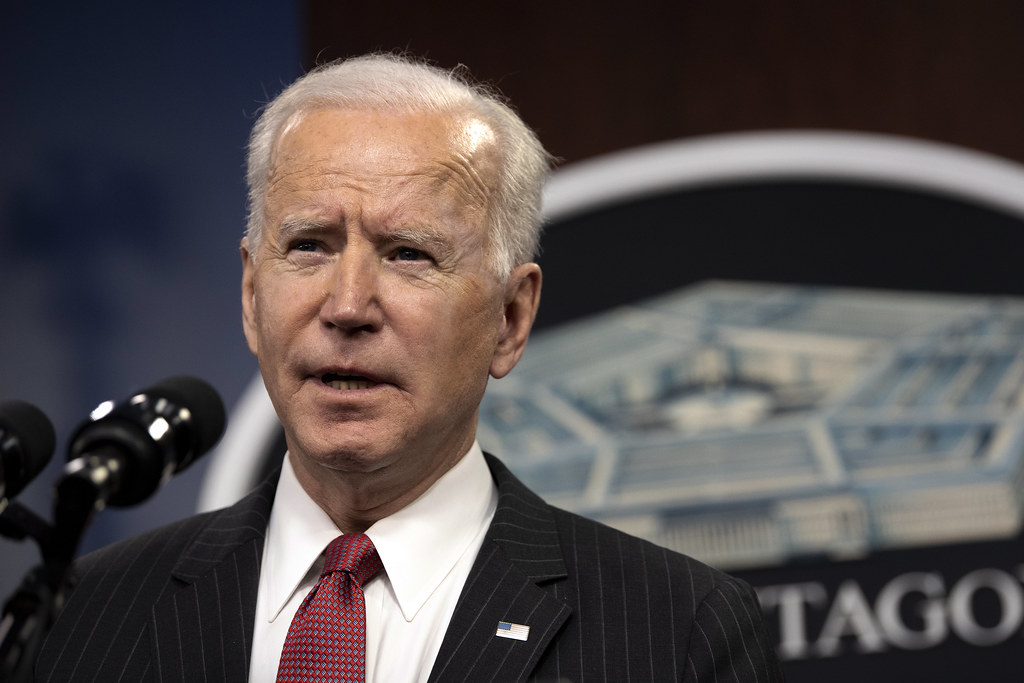
President Joe Biden expressed concerns about ransomware attacks carried out by Russian gangs during a phone call with President Vladimir Putin. The recent wave of ransomware attacks carried out by Russian gangs like REvil and Darkside worries US authorities and was discussed by Presidents Biden and Putin during a phone call. The ransomware attacks against […]






