


 Pierluigi Paganini
 August 02, 2021
Did you ever stop to think that the office smart TV used for company presentations, Zoom meetings, and other work-related activities may not be so trustworthy? In our latest video, we demonstrate an attack scenario that can occur within any organization – hacking a smart TV. The video shows an insider plugging a USB Rubber […]
 Pierluigi Paganini
August 02, 2021
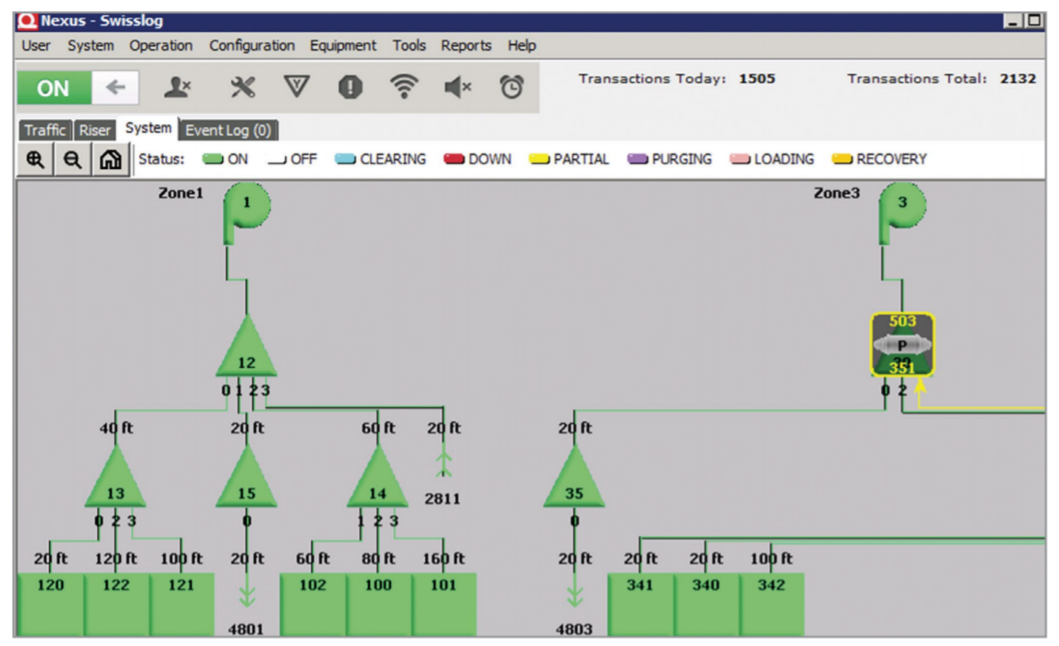
Cybersecurity researchers disclosed multiple flaws, dubbed PwnedPiper, that left a widely-used pneumatic tube system (PTS) vulnerable to attacks. Researchers from cybersecurity Armis disclosed a set of nine vulnerabilities collectively tracked as PwnedPiper that could be exploited to carry out multiple attacks against a widely-used pneumatic tube system (PTS). The Swisslog PTS system are used in […]
 Pierluigi Paganini
August 02, 2021
An attacker could exploit a vulnerability in the WordPress Download Manager plugin, tracked as CVE-2021-34639, to execute arbitrary code under specific configurations. Researchers from Wordfence team discovered a vulnerability, tracked as CVE-2021-34639, affecting the WordPress Download Manager plugin that could allow attackers to execute arbitrary code under specific configurations. The flaw could allow authors and […]
 Pierluigi Paganini
August 01, 2021
Kaspersky experts spotted a previously undocumented Chinese-speaking threat actor, tracked as GhostEmperor, that is targeting Microsoft Exchange flaws in attacks on high-profile victims. Kaspersky spotted a new Chinese-speaking threat actor, tracked as GhostEmperor, that is targeting Microsoft Exchange vulnerabilities in attacks aimed at high-profile victims. The long-running operation carried out by the group mostly targeted […]
 Pierluigi Paganini
July 30, 2021
Researcher published an exploit code for a high-severity privilege escalation flaw (CVE-2021-3490) in Linux kernel eBPF on Ubuntu machines. The security researcher Manfred Paul of the RedRocket CTF team released the exploit code for a high-severity privilege escalation bug, tracked as CVE-2021-3490, in Linux kernel eBPF (Extended Berkeley Packet Filter). A local attacker could exploit the flaw to […]
 Pierluigi Paganini
July 30, 2021
The recent attack against Iran’s national railway system was caused by a wiper malware dubbed Meteor and not by a ransomware as initially thought. According to research from Amnpardaz and SentinelOne, the recent attack against Iran’s national railway system was caused by a wiper malware dubbed Meteor and not by ransomware as initially thought. Meteor was a previously undetected strain of malware, but experts […]
 Pierluigi Paganini
July 29, 2021
Experts disclose details about a critical flaw in Microsoft Hyper-V, tracked as CVE-2021-28476, that can allow executing arbitrary code on it. Researchers Peleg Hadar of SafeBreach and Ophir Harpaz of Guardicore disclose details about a critical flaw in Microsoft Hyper-V, tracked as CVE-2021-28476, that can allow triggering a DoS condition ot executing arbitrary code on it. The flaw resides in […]
 Pierluigi Paganini
July 28, 2021
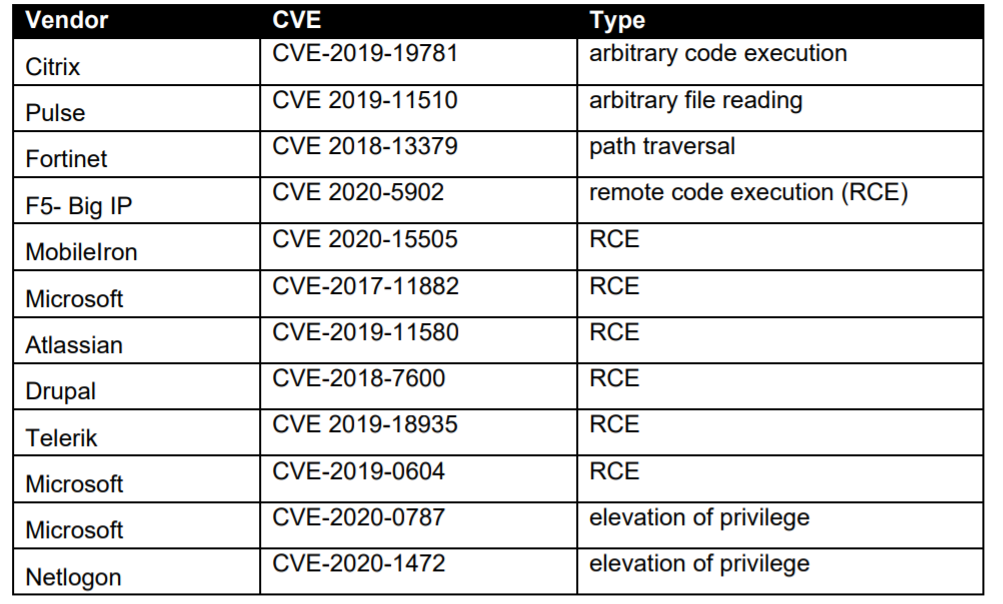
A joint report published by US, UK, and Australian cyber security agencies warns of the top routinely exploited vulnerabilities in 2020. The U.S. Cybersecurity and Infrastructure Security Agency (CISA), the Australian Cyber Security Centre (ACSC), the United Kingdom’s National Cyber Security Centre (NCSC), and the U.S. Federal Bureau of Investigation (FBI) published a Joint Cybersecurity […]
 Pierluigi Paganini
July 27, 2021
Researchers discovered flaws in Zimbra email collaboration software that could allow attackers to compromise email accounts by sending a malicious email. Cybersecurity researchers have discovered multiple security vulnerabilities, tracked as CVE-2021-35208 and CVE-2021-35208, in Zimbra email collaboration software. An unauthenticated attacker could chain these vulnerabilities to fully takeover a Zimbra webmail server of a targeted organization. An […]
 Pierluigi Paganini
July 25, 2021
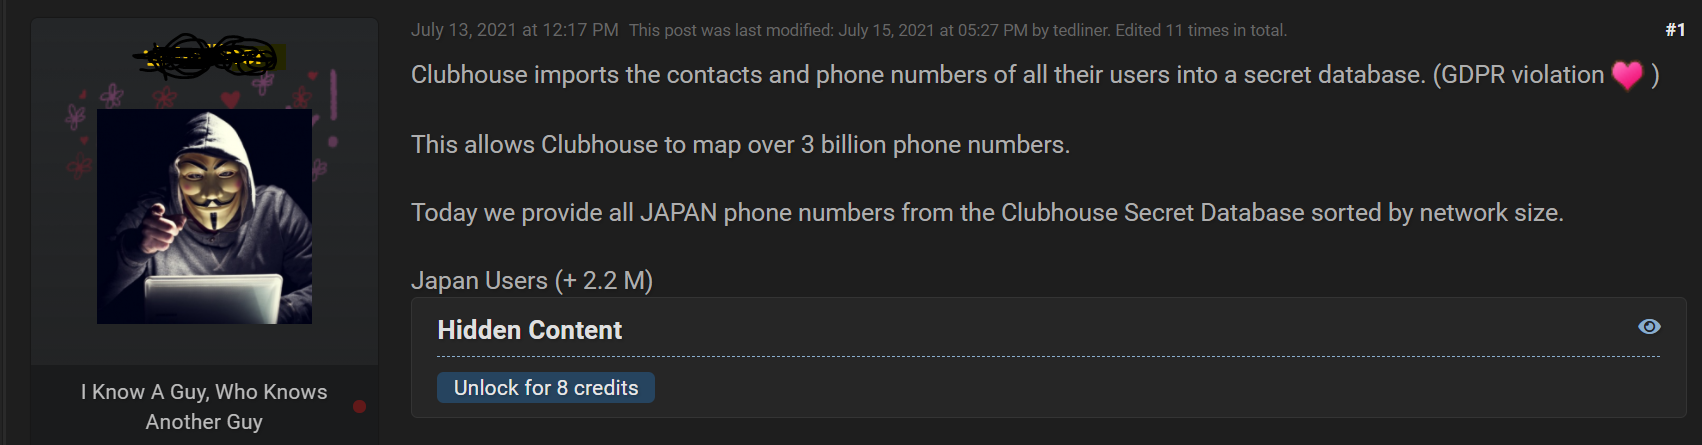
A threat actor is offering for sale on hacking forums the secret database Clubhouse containing 3.8B phone numbers. Clubhouse is a social audio app for iOS and Android where users can communicate in voice chat rooms that accommodate groups of thousands of people. The audio-only app hosts live discussions, with opportunities to participate through speaking and listening. Conversations are prohibited by Clubhouse’s guidelines […]






