


 Pierluigi Paganini
 May 06, 2026
Palo Alto Networks warns of a critical PAN-OS flaw (CVE-2026-0300) that is under active attack, allowing unauthenticated remote code execution. Palo Alto Networks has warned that a critical PAN-OS vulnerability, tracked as CVE-2026-0300 (CVSS score of 9.3), is actively exploited in the wild. The flaw is a buffer overflow that allows unauthenticated remote code execution, […]
 Pierluigi Paganini
May 06, 2026
A malicious PyTorch Lightning update (v2.6.3) on PyPI spread briefly, stealing credentials and raising major concerns about AI supply chain security. A malicious update of the PyTorch Lightning library exposed developers to credential theft and remote compromise. Attackers uploaded version 2.6.3 to the Python Package Index (PyPI), where it spread among developers before maintainers removed […]
 Pierluigi Paganini
May 05, 2026
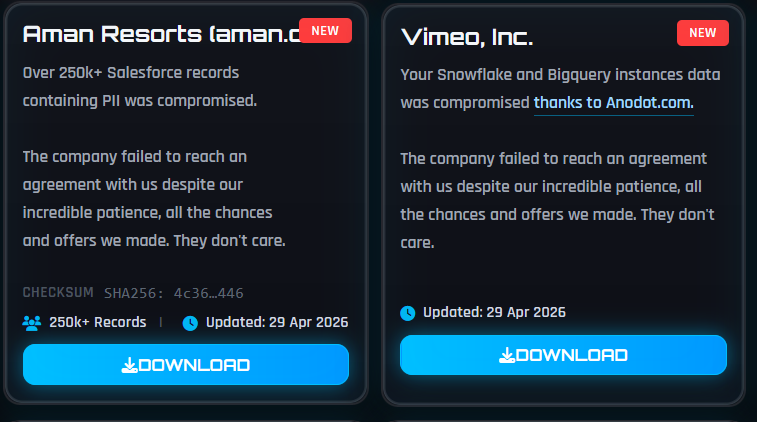
Hackers stole data of 119,000 Vimeo users in April. The breach, linked to a third‑party vendor, exposed personal details. Vimeo confirmed a data breach after the ShinyHunters gang stole personal information of 119,000 users in April 2026. According to Have I Been Pwned, the attackers accessed user data through a compromise at Anodot, a third‑party […]
 Pierluigi Paganini
May 05, 2026
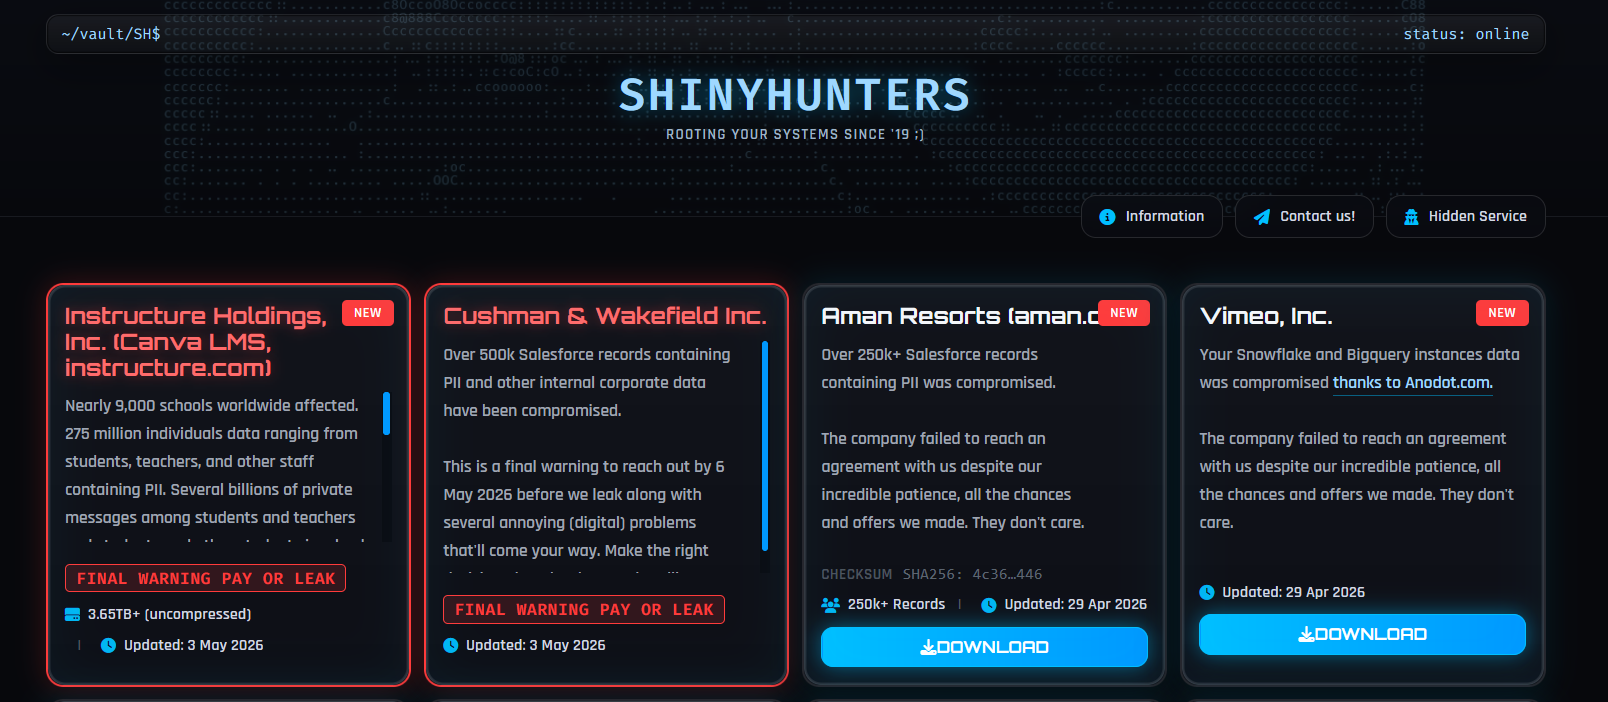
Instructure, maker of the Canvas learning platform, is investigating a cyber incident that exposed users’ personal data. Instructure is a U.S.-based educational technology company best known for developing Canvas, one of the world’s most widely used learning management systems (LMS). The U.S. firm confirrmed a cybersecurity incident that exposed users’ personal information. The company is working with external […]
 Pierluigi Paganini
May 04, 2026
Attackers exploit a critical cPanel flaw to target government and MSP networks across Southeast Asia and several countries, including the U.S. and Canada. A threat actor is exploiting critical cPanel vulnerability CVE-2026-41940 to target government and military organizations in Southeast Asia, along with MSPs and hosting providers in countries like the Philippines, Laos, Canada, South […]
 Pierluigi Paganini
May 04, 2026
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds a flaw in Linux Kernel to its Known Exploited Vulnerabilities catalog The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a flaw in the Linux Kernel, tracked as CVE-2026-31431 (CVSS score of 7.8), to its Known Exploited Vulnerabilities (KEV) catalog. Recently, Xint Code researchers warned of a serious Linux […]
 Pierluigi Paganini
May 04, 2026
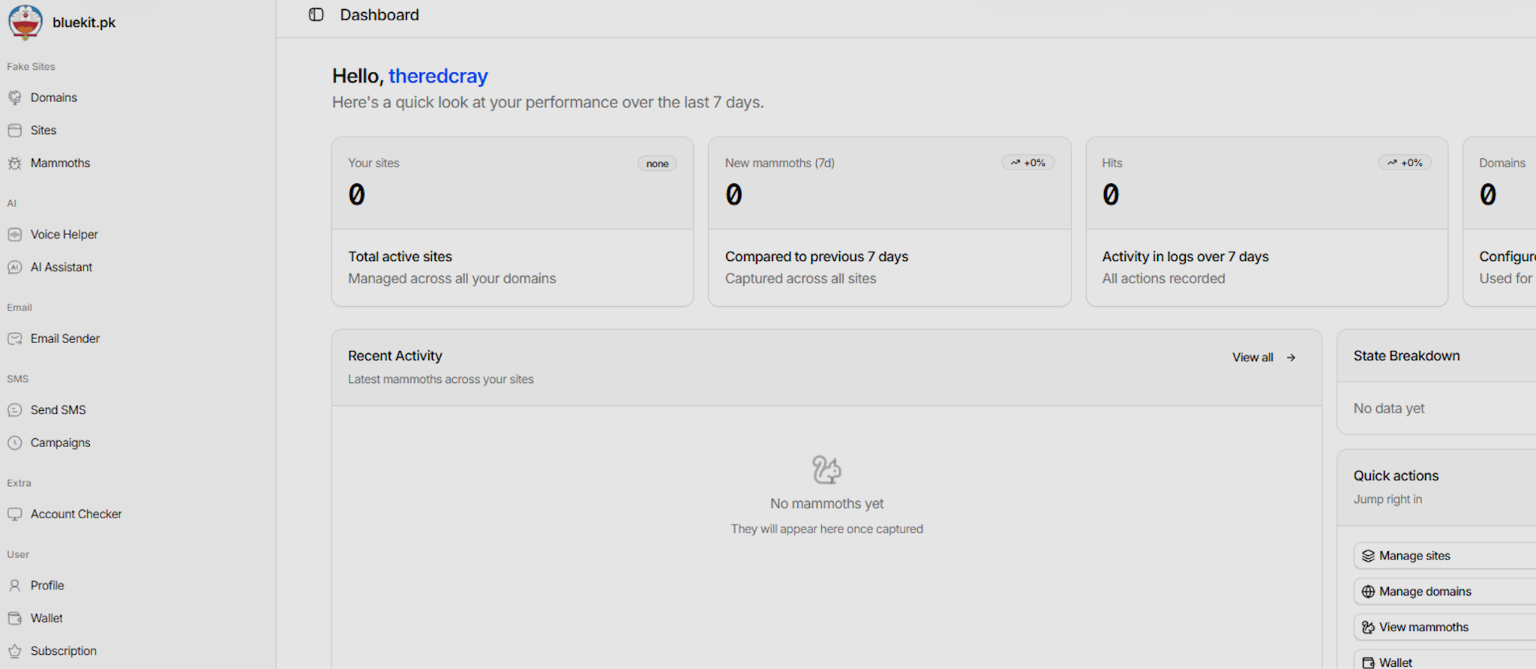
Bluekit is a new phishing kit with AI features, automated domain setup, and tools like spoofing, voice cloning, and 40+ attack templates. Bluekit is a newly discovered phishing kit still in development that includes advanced features such as an AI assistant and automated domain registration. According to Varonis, it offers over 40 website templates along […]
 Pierluigi Paganini
May 03, 2026
April 2026 breach at Sistemi Informativi (IBM Italy) raises concerns over Chinese-linked cyber ops in Europe, including Salt Typhoon. In late April 2026, the Italian cybersecurity landscape was shaken by a significant breach targeting Sistemi Informativi, a company wholly owned by IBM Italy that provides IT infrastructure management for key public and private institutions. The […]
Pierluigi Paganini
May 03, 2026
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds a flaw in WebPros cPanel to its Known Exploited Vulnerabilities catalog The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a flaw in Microsoft Defender, tracked as CVE-2026-41940 (CVSS score of 9.3), to its Known Exploited Vulnerabilities (KEV) catalog. cPanel is a widely used web hosting control panel that lets […]
 Pierluigi Paganini
May 01, 2026
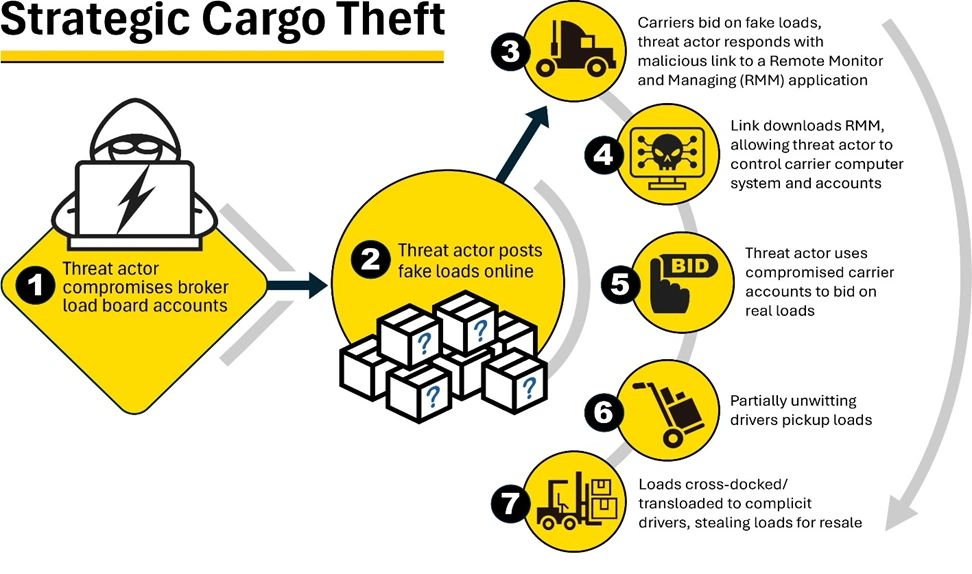
The FBI warns of rising cyber cargo theft, with hackers targeting brokers and carriers. Experts say digital attacks are replacing traditional cargo theft. The FBI has issued a Public Service Announcement (PSA) about a surge in cyber-enabled cargo theft, with hackers increasingly targeting brokers and carriers. This trend confirms earlier findings from Proofpoint and alerts […]






