 Pierluigi Paganini
 November 13, 2018
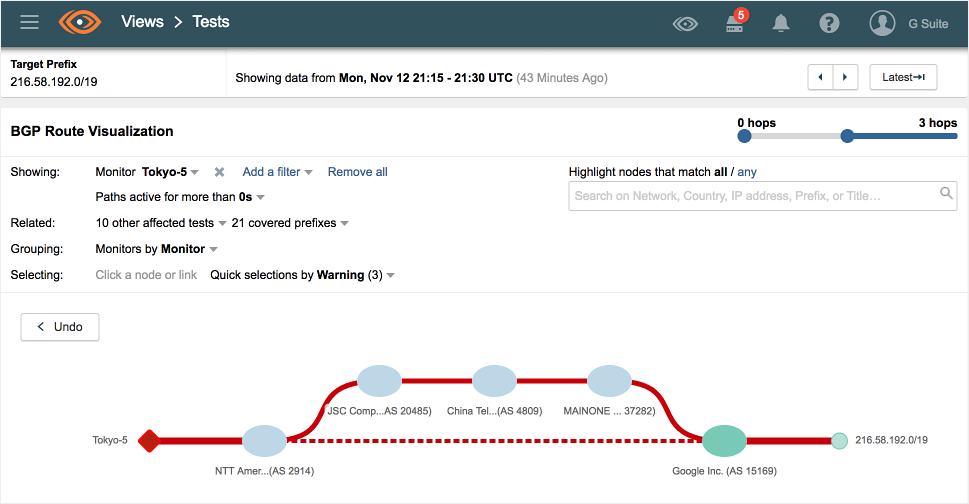
Google services were partially inaccessible on Monday due to a BGP leak that caused traffic redirection through Russia, China, and Nigeria. A BGP leak caused unavailability of Google service on Monday, the traffic was redirected through Russia, China, and Nigeria. At the time it is not clear if the incident was the result of an […]
 Pierluigi Paganini
November 13, 2018
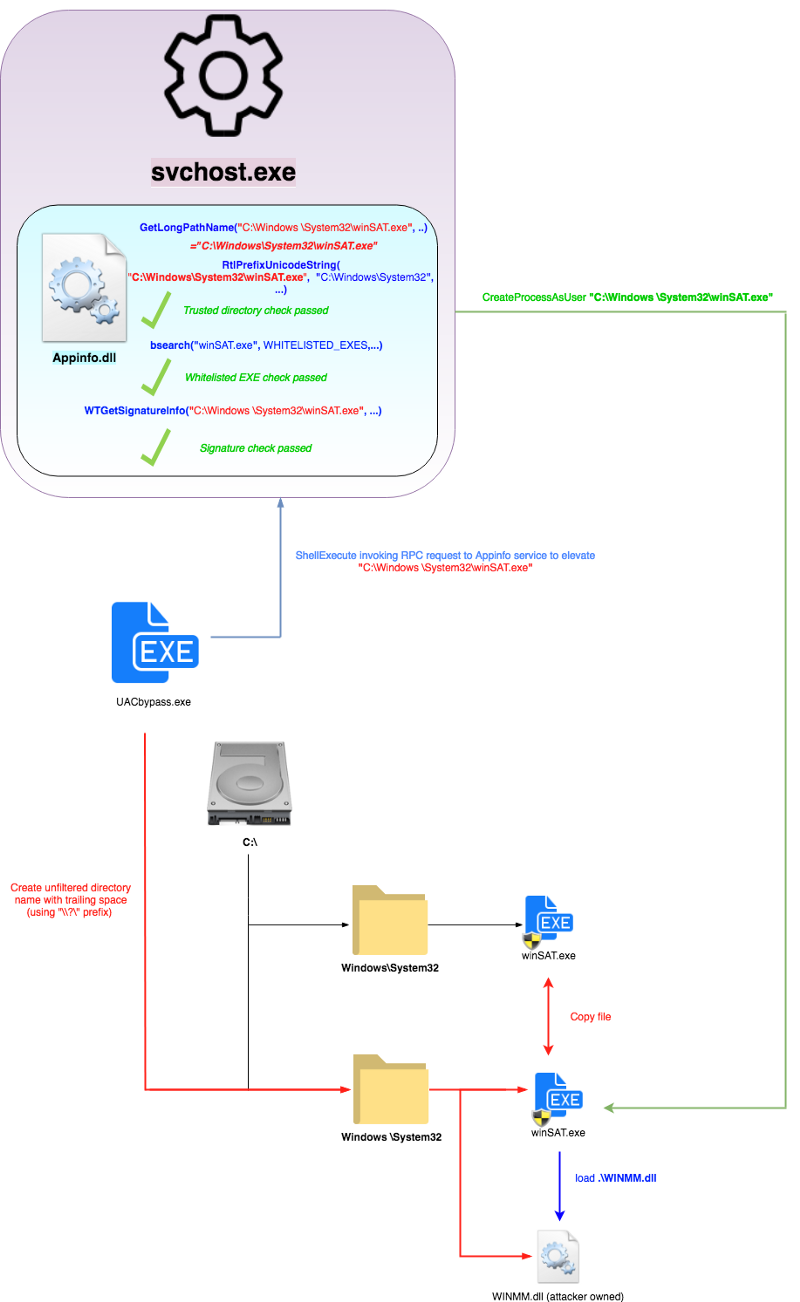
David Wells, a security expert from Tenable, devised a method to bypass Windows’ User Account Control (UAC) by spoofing the execution path of a file in a trusted directory. A security researcher from Tenable has discovered that is possible to bypass Windows’ User Account Control (UAC) by spoofing the execution path of a file in a trusted […]
 Pierluigi Paganini
November 12, 2018
According to Android Ecosystem Security Transparency Report the number of potentially harmful applications has fallen from 0.66% in Lollipop to 0.06% in Pie Google published the first Android Ecosystem Security Transparency Report that revealed that the number of potentially harmful applications (PHAs) discovered on Android 9 Pie devices has been reduced by half compared to the previous versions. According […]
 Pierluigi Paganini
November 12, 2018
A critical security vulnerability affects a GDPR compliance plugin for WordPress has been already exploited in the wild to take control of vulnerable websites. Users warn of cyber attacks exploiting a critical security vulnerability in the WordPress GDPR Compliance plugin for WordPress to take over of websites using it. The WordPress GDPR Compliance plugin was used by more than […]
 Pierluigi Paganini
November 11, 2018
Experts at Volexity discovered that a recently patched remote code execution flaw (CVE-2018-15961) affecting the Adobe ColdFusion has been exploited in the wild. Security experts from Volexity reported that attackers in the wild are exploiting a recently patched remote code execution vulnerability affecting the Adobe ColdFusion. The flaw, tracked as CVE-2018-15961, is an unrestricted file upload vulnerability, successful exploitation could lead to […]
 Pierluigi Paganini
November 11, 2018
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. Let me inform you that my new book, “Digging in the Deep Web” is online with a special deal 20% discount Kindle Edition Paper Copy Once again thank you! Apple T2 security chip in new MacBooks disconnects Microphone […]
 Pierluigi Paganini
November 10, 2018
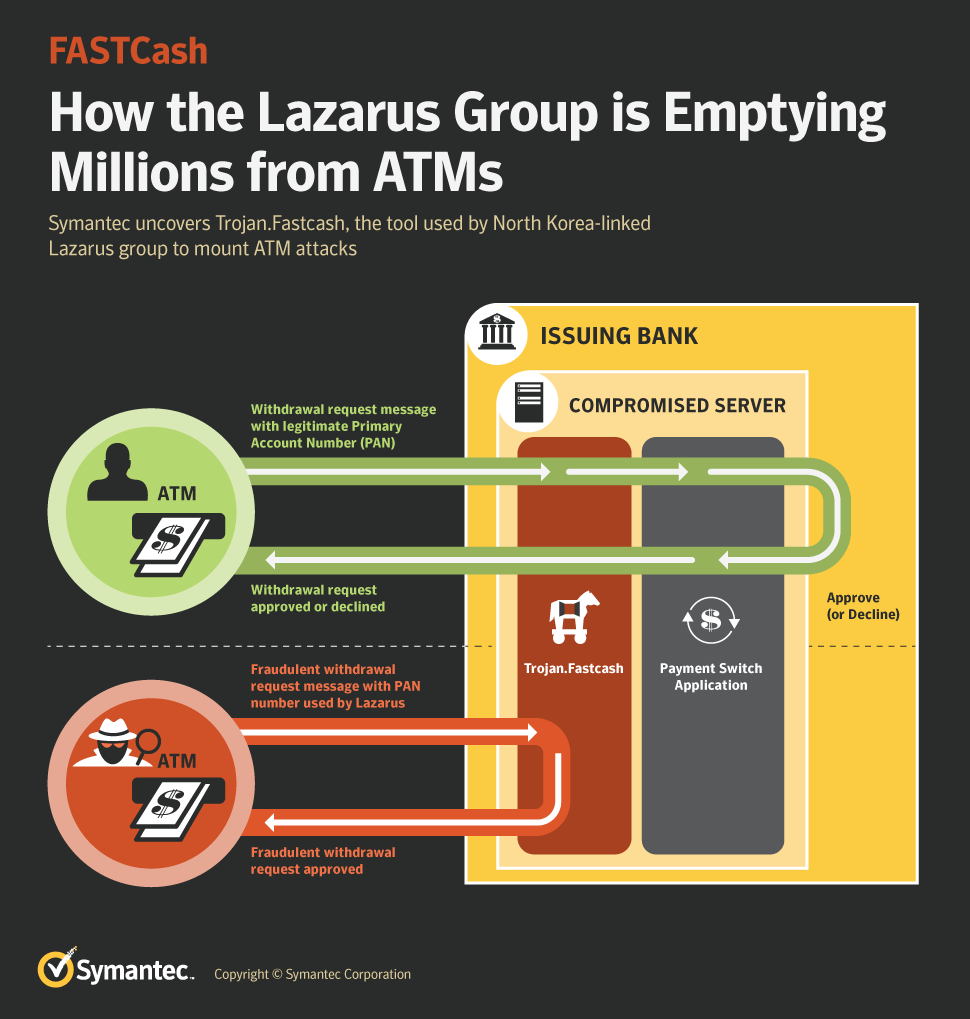
North Korea-linked Lazarus Group has been using FastCash Trojan to compromise AIX servers to empty tens of millions of dollars from ATMs. Security experts from Symantec have discovered a malware, tracked as FastCash Trojan, that was used by the Lazarus APT Group, in a string of attacks against ATMs. The ATP group has been using this malware […]
 Pierluigi Paganini
November 10, 2018
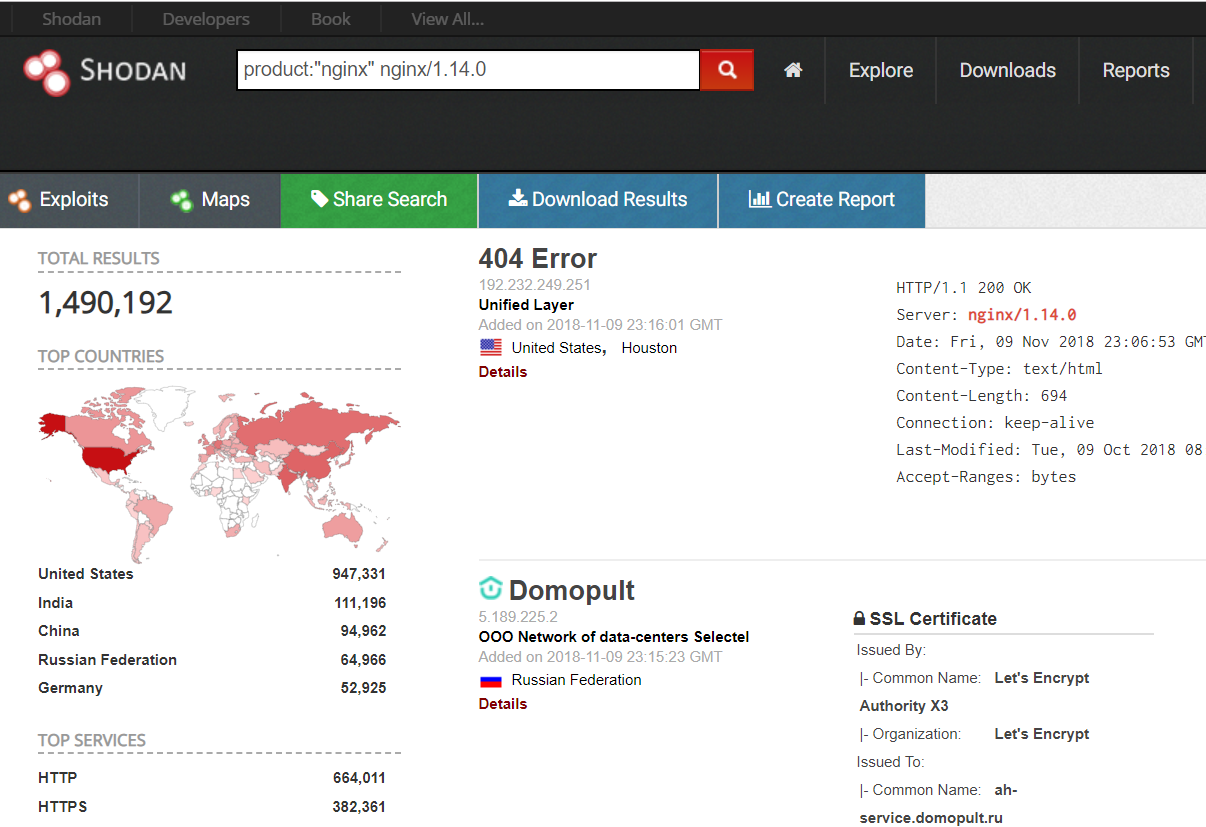
Nginx developers released security updates to address several denial-of-service (DoS) vulnerabilities affecting the nginx web server. nginx is an HTTP and reverse proxy server, a mail proxy server, and a generic TCP/UDP proxy server, it is used by 25.28% busiest sites in October 2018. Nginx development team released versions 1.15.6 and 1.14.1 to address two HTTP/2 implementation vulnerabilities that can […]
 Pierluigi Paganini
November 09, 2018
VMware released security patches for a critical virtual machine (VM) escape vulnerability that was recently discovered at a Chinese hacking contest. VMware has released security patches for a critical virtual machine (VM) escape vulnerability (CVE-2018-6981 and CVE-2018-6982) that was recently discovered by the researcher Zhangyanyu at the Chinese GeekPwn2018 hacking contest. The cause for the […]
 Pierluigi Paganini
November 09, 2018
Snowden warns of abuse of surveillance software that also had a role in the murder of the Saudi Arabian journalist Jamal Khashoggi. The popular US whistleblower Edward Snowden has reported the abuse of surveillance made by many governments, he blamed the Israeli company NSO Group for developing and selling surveillance software to Saudi Arabia. Speaking […]