 Pierluigi Paganini
 June 22, 2026
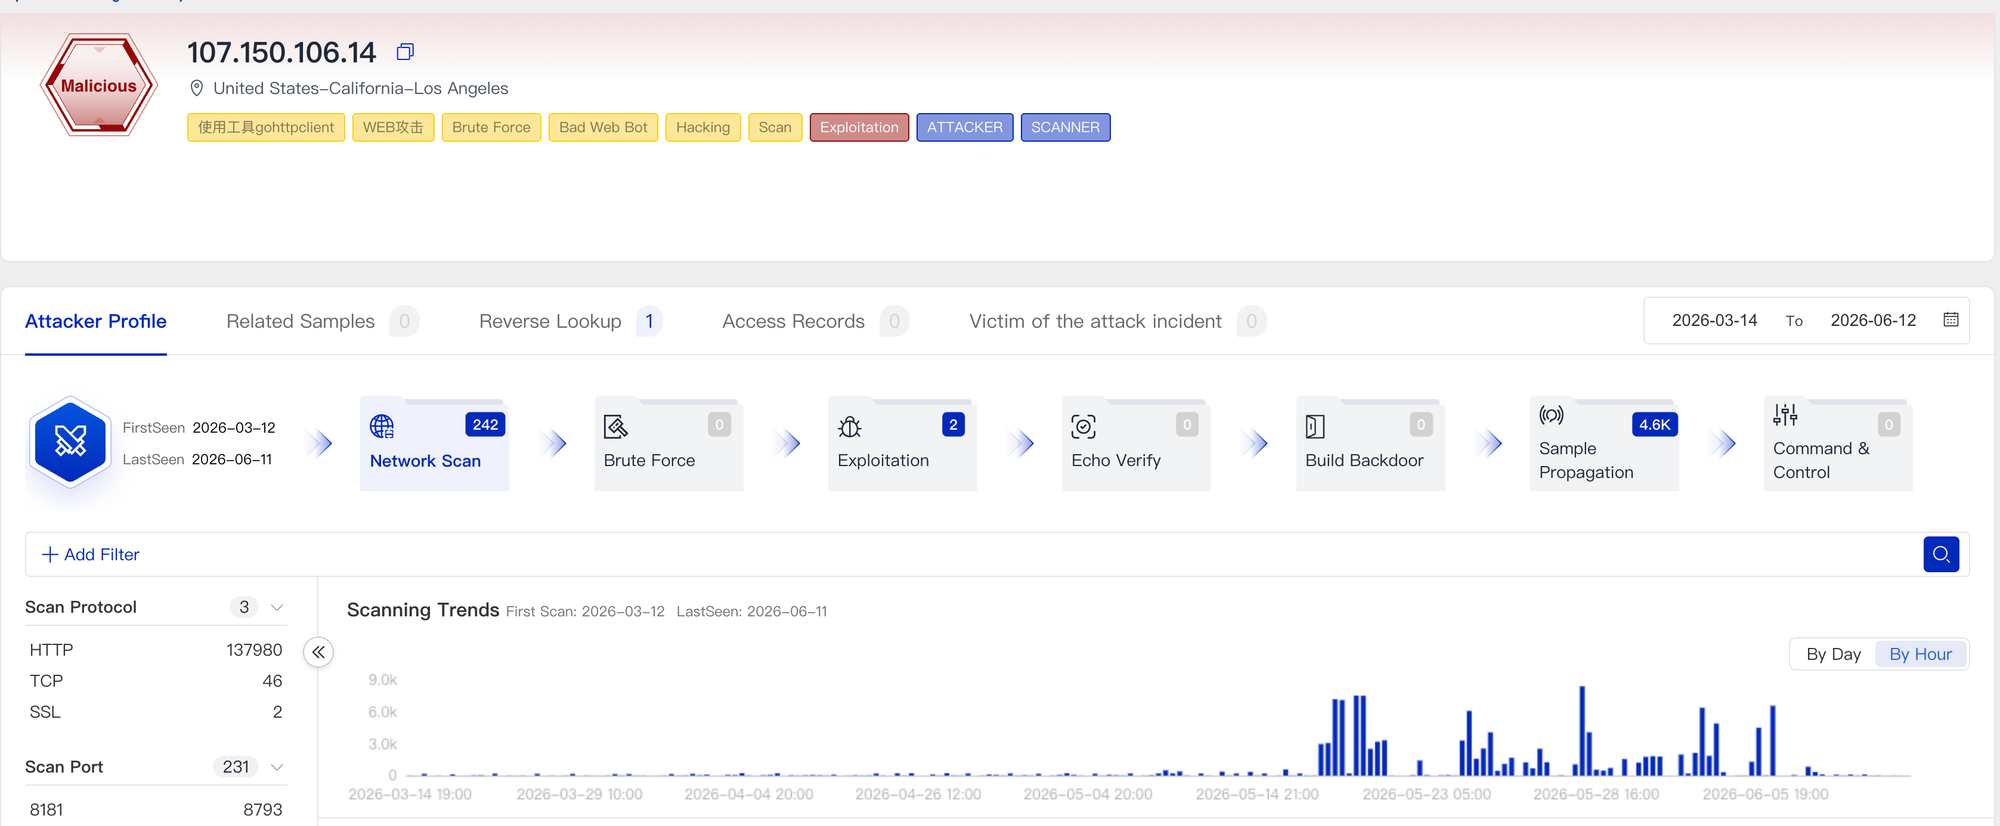
AryStinger hijacks outdated routers via old flaws, turning 4,300+ devices into a stealth network for reconnaissance and intrusion support. On March 12, 2026, QiAnXin’s XLab threat detection system flagged a single IP address, 107.150.106.14, spreading a Linux binary through two vulnerabilities that were disclosed in 2013 and 2016 respectively. The binary had zero detections on […]
 Pierluigi Paganini
June 22, 2026
usbliter8 is an unpatchable BootROM exploit affecting A12/A13 devices, enabling code execution and extending checkm8-like risks to newer iPhones. Security researchers at Paradigm Shift published a working exploit on June 18, 2026, called usbliter8, that achieves arbitrary code execution inside the SecureROM of Apple’s A12 and A13 chips. SecureROM is the first code that runs […]
 Pierluigi Paganini
June 21, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter OptinMonster supply chain attack hits 1.2 million sites Public and Private Medical Community Targeted by China-Nexus Threat Actor Pursuing Artificial Intelligence, Cyber, Medical, and National Defense Research Rokarolla : Android Banker with Complete Device […]
 Pierluigi Paganini
June 20, 2026
The Gentlemen equips affiliates with a centralized EDR-killer suite, rapidly weaponizing BYOVD exploits to disable security tools before ransomware attacks. ESET published a detailed breakdown of The Gentlemen‘s technical infrastructure on June 18, the result of months of incident-level investigation corroborated by the group’s own internal data leak from May 2026. Since emerging in late […]
 Pierluigi Paganini
June 20, 2026
FortiBleed exposed credentials for 74,000 Fortinet devices, with attackers actively exploiting the leak to target systems worldwide. On June 18, CISA issued an emergency alert after reports surfaced that credentials for approximately 74,000 Fortinet firewalls and VPN gateways had been leaked in what researchers are calling FortiBleed. The agency confirmed that threat actors were actively […]
 Pierluigi Paganini
June 19, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Splunk Enterprise flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Splunk Enterprise flaw, tracked as CVE-2026-20253 (CVSS score of 9.8), to its Known Exploited Vulnerabilities (KEV) catalog. The flaw CVE-2026-20253 is an improper authentication vulnerability in the PostgreSQL sidecar service of […]
 Pierluigi Paganini
June 19, 2026
A simple website flaw exposed members, political profiles, login tokens, and dating data from Peter Thiel ‘s secretive Dialog network. Dialog, a private invitation-only organization cofounded in 2006 by billionaire tech investor Peter Thiel, has spent two decades refusing to disclose its membership. That position became harder to maintain last week when Swiss hacktivist maia […]
 Pierluigi Paganini
June 19, 2026
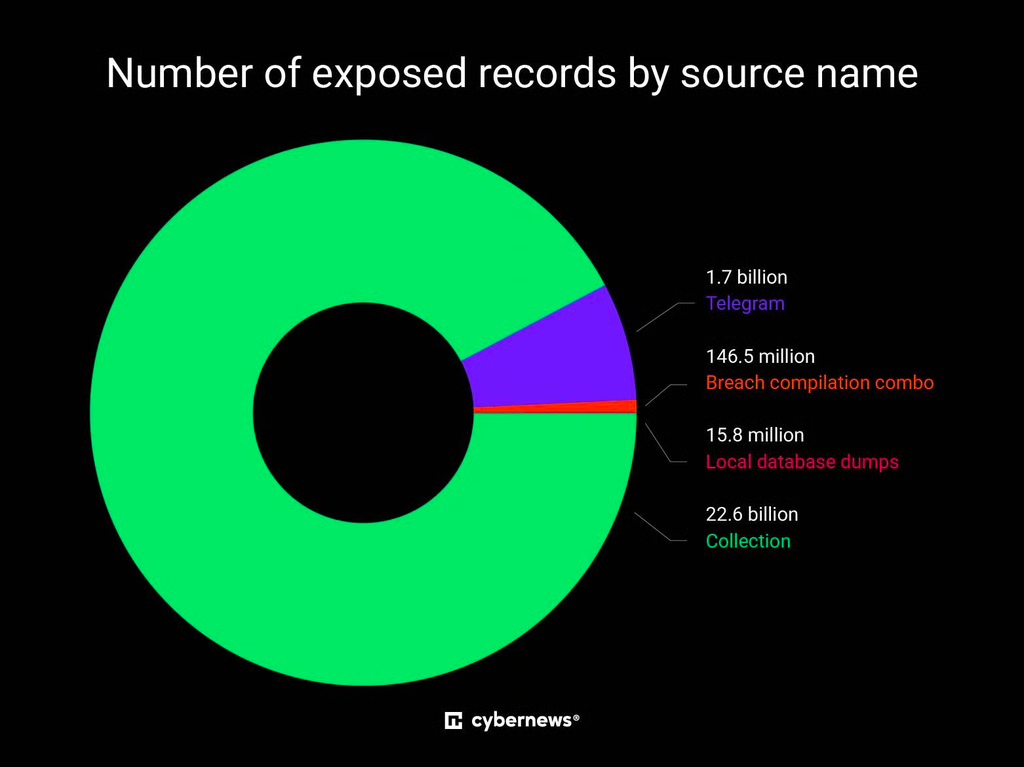
24 Billion Records Left Open Online: Passwords, Emails, and Everything Else Exposed database with 24 Billion records revealed stolen credentials from infostealers, Telegram channels, and breach collections, risking account takeovers. Cybernews researchers found an exposed Elasticsearch cluster on June 12th containing 24 billion records and more than 8.3 terabytes of data. They triple-checked the numbers. […]
 Pierluigi Paganini
June 18, 2026
Cisco addressed CVE-2026-20181, a critical ISE vulnerability that lets authenticated admins execute commands and gain root access. Cisco addressed a critical command execution vulnerability, tracked as CVE-2026-20181 (CVSS score of 9.1), affecting Identity Services Engine (ISE) and ISE-PIC. The flaw stems from improper validation of user-supplied input, allowing an authenticated attacker with administrative credentials to […]
 Pierluigi Paganini
June 18, 2026
F5 released emergency updates for critical NGINX flaws (CVE-2026-42530, CVE-2026-42055) that could enable unauthenticated code execution. F5 has issued out-of-band patches for multiple NGINX vulnerabilities, including two critical flaws, respectively tracked as CVE-2026-42530 and CVE-2026-42055 (CVSS 9.2). The bugs affect HTTP modules and can be exploited remotely without authentication to trigger memory corruption, potentially causing […]