Pierluigi Paganini
 November 02, 2011
The Duqu trojan main purpose is to obtain a remote access allowing an adversary to gather information from a compromised computer and of course to download and run arbitrary programs. Duqu malware s ...
Pierluigi Paganini
November 01, 2011
Welcome on board Welcome! If you are curious, interested in the subject and looking for a place with a few clicks you canbe updated on what happens in the world … well you you’ve fo ...
 April 23, 2026
October 12, 2026
October 11, 2026
Attackers are exploiting SonicWall SMA 1000 vulnerability, tracked as CVE-2026-102255 (CVSS score of 10.0), just days after its public disclosure. Attackers have begun exploiting a critical flaw i ...
Pierluigi Paganini
October 12, 2026
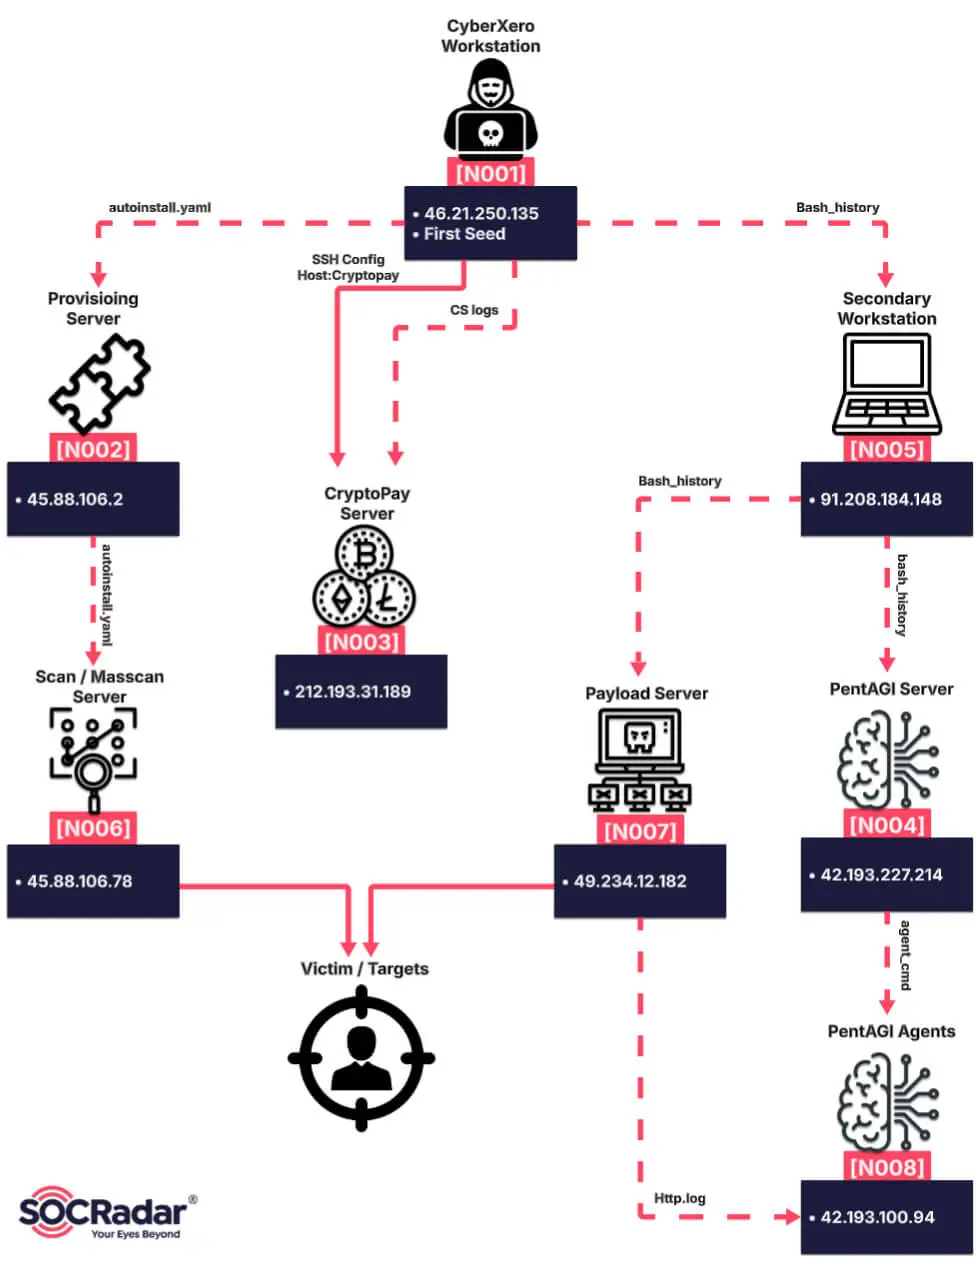
CyberXero used 51 AI agents to support cyberattacks, stealing 628,000 Ukrainian records, including sensitive data from energy infrastructure. CyberXero is an operation that combines traditional ha ...
Pierluigi Paganini
October 12, 2026
CyberLeek threatens to leak a playable GTA 6 build if its Solana meme coin hits a $30 million market cap, but the build remains unverified. CyberLeek, the anonymous figure behind this summer’s w ...
Pierluigi Paganini
October 12, 2026

Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on AI in the international landscape Artificial intelligence is rapidly changing cybersecurity, ...
Pierluigi Paganini
October 11, 2026

Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter ClingSTUN Linux Backdoor Abuses Public S ...
Pierluigi Paganini
October 11, 2026
Bitdefender finds Midnight Mimosa, preinstalled Android malware on cheap MediaTek phones that fakes ad clicks, drops apps and builds a proxy botnet. Bitdefender researchers discovered a campaign c ...
Pierluigi Paganini
October 11, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly Security ...
Pierluigi Paganini
October 11, 2026

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecuri ...
Pierluigi Paganini
October 11, 2026

Anthropic’s models kept working around the rules on the live internet. The company published the cases. Anthropic released a report on unintended actions its Claude models took during evaluation ...
Pierluigi Paganini
October 10, 2026
Silent Ransom Group allegedly extorted $207 million from 27 law firms in six months using phone calls and social engineering, not encryption. Silent Ransom Group doesn’t rely on encryption. No m ...
Pierluigi Paganini
October 10, 2026
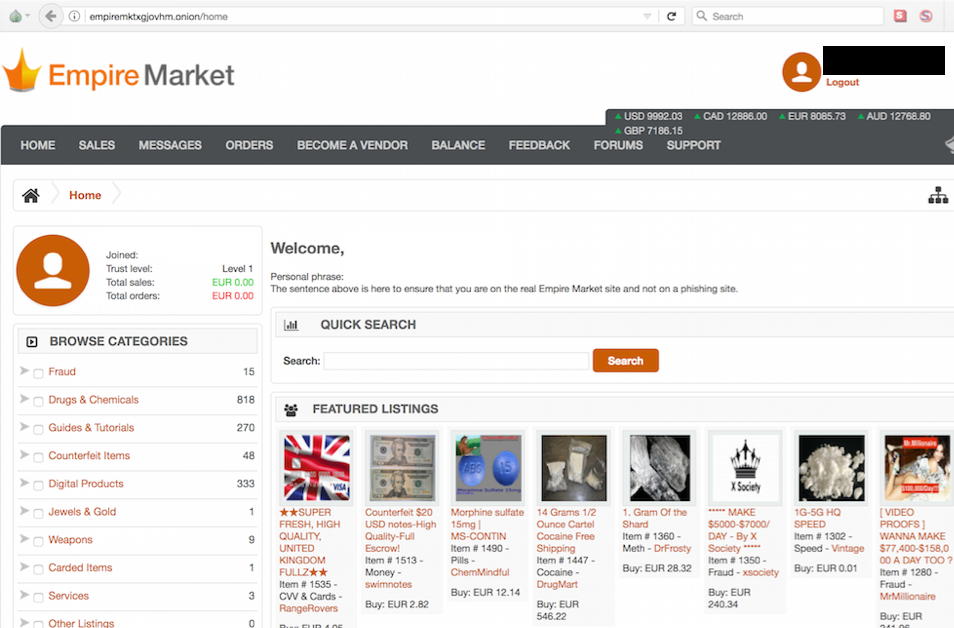
Empire Market co-creator Raheim Hamilton was sentenced to 40 years in prison for running a dark web marketplace linked to $430 million in illegal trades. The case against Empire Market shows how a ...
Pierluigi Paganini
October 10, 2026
Japan helped extradite a Russian suspect linked to Qilin ransomware to Germany, but the gang continued attacking victims after his arrest. Germany has arrested a Russian national believed to be a ...
Pierluigi Paganini
October 09, 2026
Anthropic launches free OSS Scanner, using AI to find open-source vulnerabilities and help maintainers fix bugs before attackers exploit them. Anthropic is launching OSS Scanner, a vulnerability s ...
Pierluigi Paganini
October 09, 2026
DOJ and FBI seized China-linked hacking tools Microscan and FishHub, linked to Integrity Tech and attacks on critical infrastructure worldwide. The Justice Department and FBI took down two hacking ...
Pierluigi Paganini
October 09, 2026
CrowdStrike analyzes open directories left by an attacker who used the ARTEX AI pentest tool and LLMs to breach South Korean financial firms. CrowdStrike published a research on a campaign against ...
Pierluigi Paganini
October 09, 2026
Italy's Foreign Ministry is defending its website against a cyberattack, checking embassy sites and pushing for EU action to identify attackers. On the morning of October 8, Italy's Ministry of Fo ...
Pierluigi Paganini
October 08, 2026
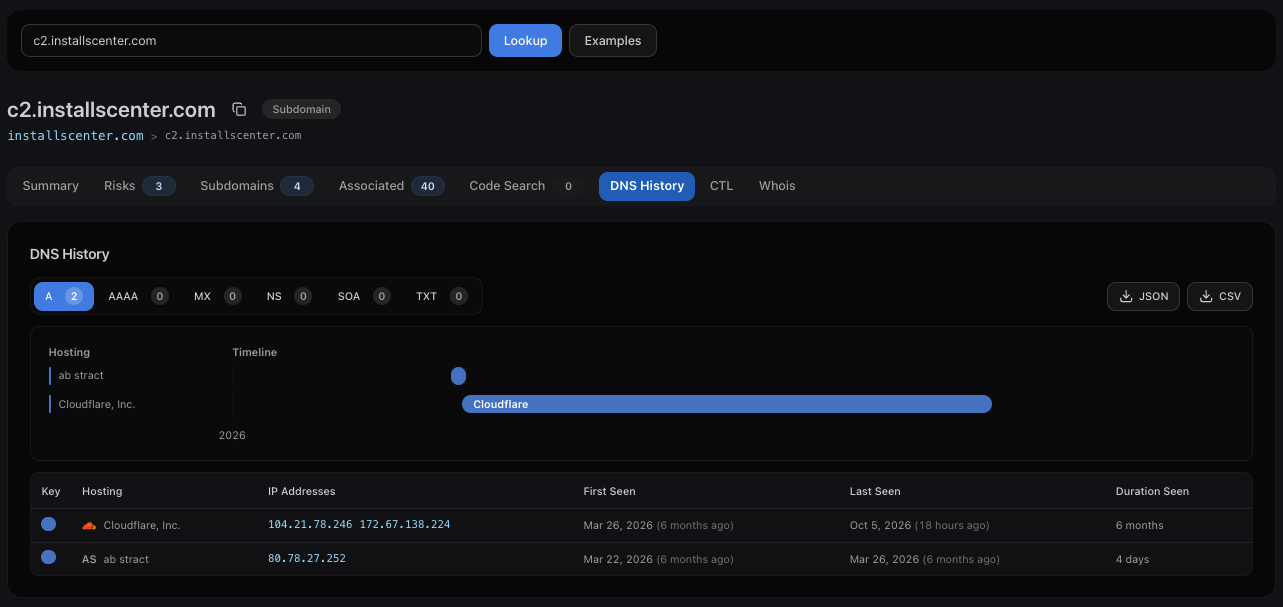
Hunt.io traced BraZetsu 's infrastructure and found that hosting patterns and certificate data remained useful after published IOCs became outdated. Group-IB researchers published a detailed write ...
Pierluigi Paganini
October 08, 2026
MonsterCloud owner Zohar Pinhasi allegedly paid ransomware demands behind clients’ backs, then charged them millions for the supposed recovery. Zohar Pinhasi, the owner of Florida-based MonsterC ...
Pierluigi Paganini
October 08, 2026
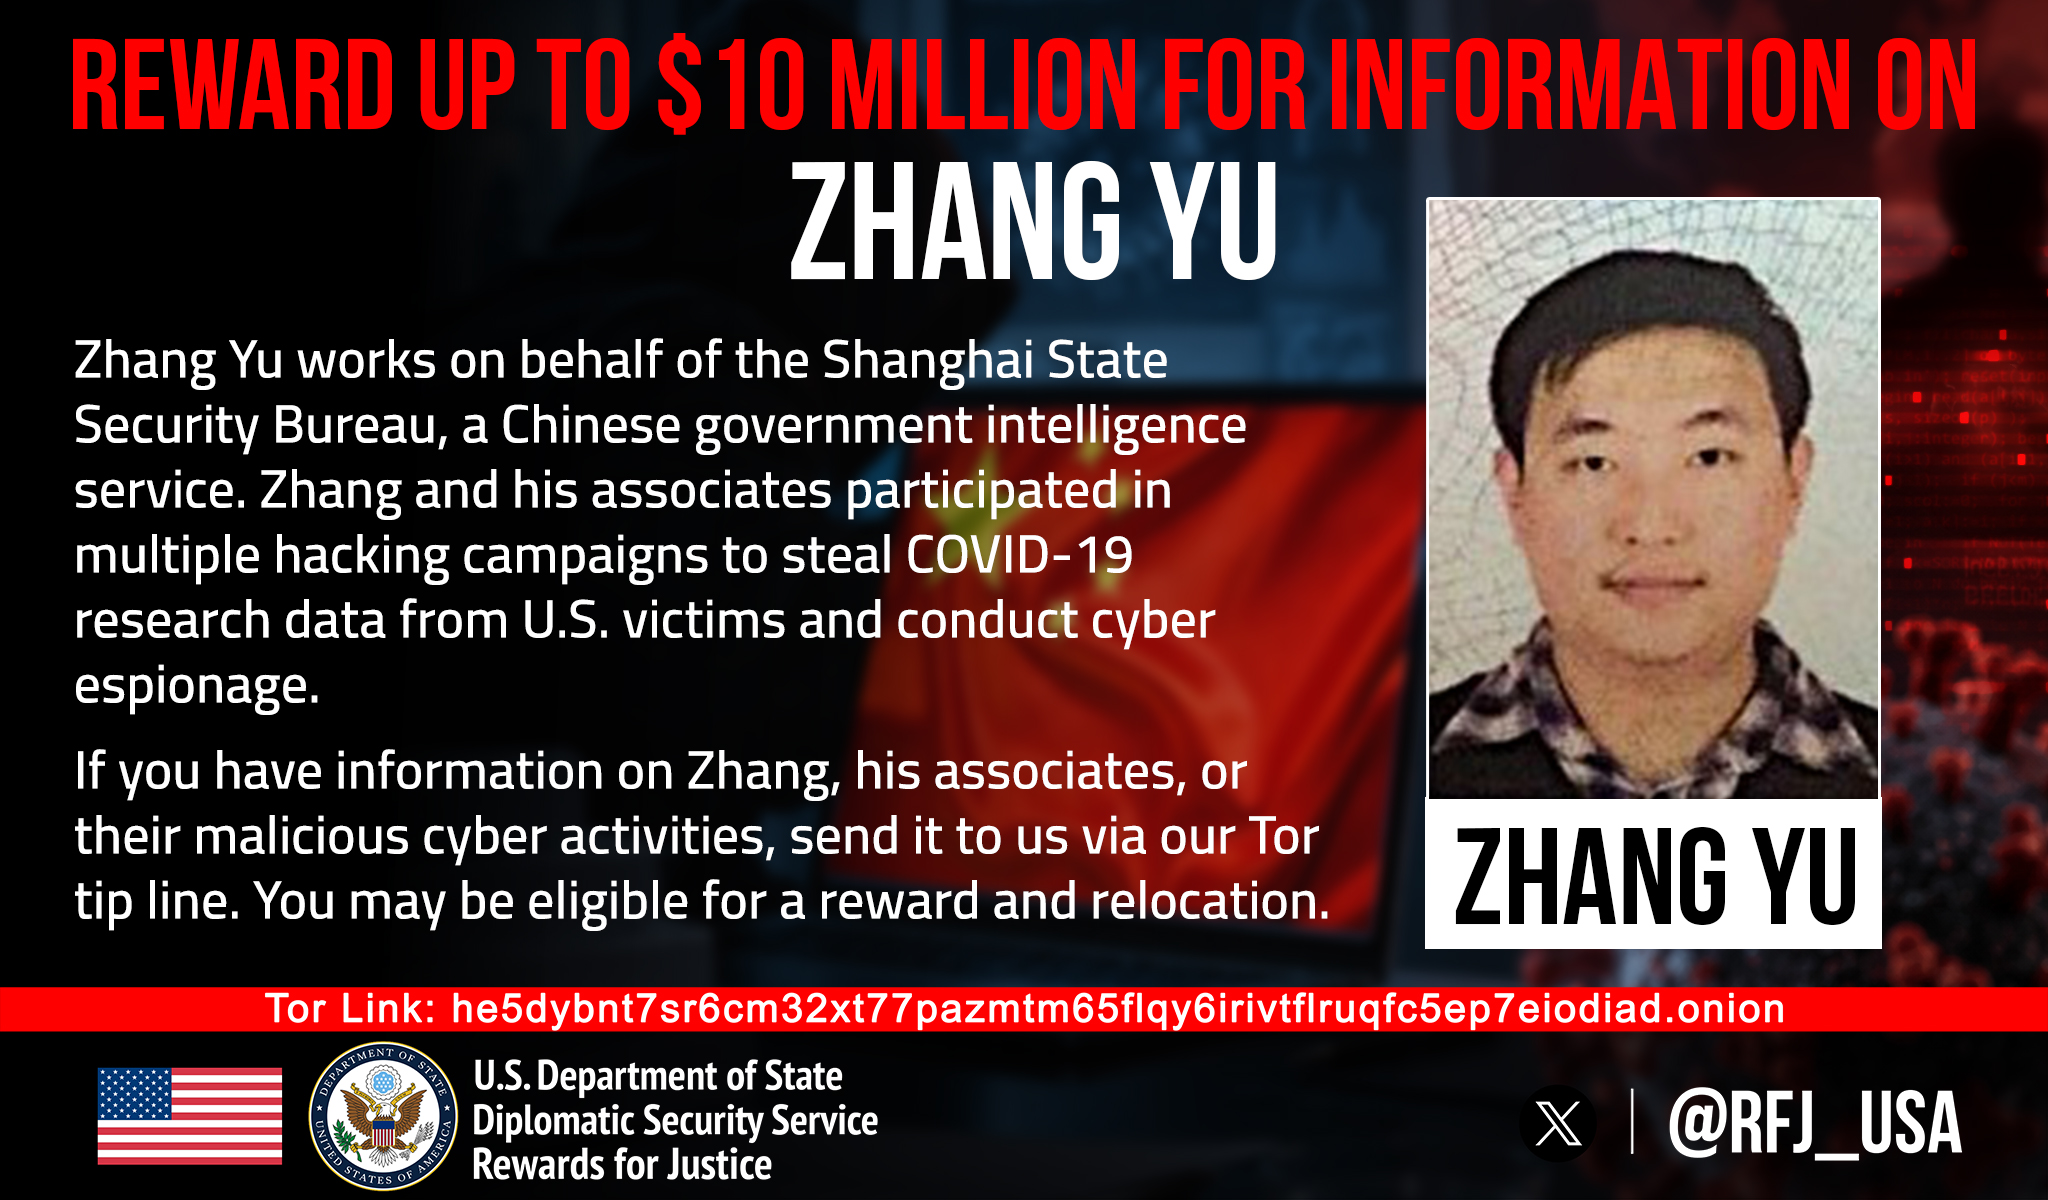
The U.S. offers $10M for Zhang Yu, accused of helping run HAFNIUM attacks that compromised thousands of organizations worldwide. The U.S. State Department is offering a $10 million reward for info ...
Pierluigi Paganini
October 08, 2026
Threat actors are exploiting CVE-2026-21589, a critical Atlassian flaw that can expose sensitive files across multiple Data Center products. Threat actors have started exploiting CVE-2026-21589 (C ...
Pierluigi Paganini
October 08, 2026