Pierluigi Paganini
 March 03, 2013
Another noisy attack has alerted IT community, online note service Evernote is the latest firm to get hacked. The company provides the popular service to around 50 million users, the attackers acces ...
Pierluigi Paganini
March 02, 2013
In recent weeks I wrote about an interesting article posted on Webroot by security expert Dancho Danchev, a careful observer of cyber criminal activities in the underground. The researcher describ ...
Pierluigi Paganini
March 01, 2013
Recent studies of principal security firms revealed that phishing activities in the last years have increased exponentially, cybercrime is targeting every sector from industry to government institutio ...
Pierluigi Paganini
February 28, 2013
It’s a very difficult period for security researchers that in the last months have discovered various cyber espionage campaigns that hit governments, private businesses and intelligence agencies all ...
 April 23, 2026
September 15, 2026
September 15, 2026
September 15, 2026

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Cisco Secure Email Gateway flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security ...
Pierluigi Paganini
September 15, 2026

Cisco warns of a critical zero-day in Secure Email Gateway, exploited in the wild to gain root access through malicious emails. Cisco disclosed a critical zero-day, tracked as CVE-2026-76461 (CVSS ...
Pierluigi Paganini
September 15, 2026
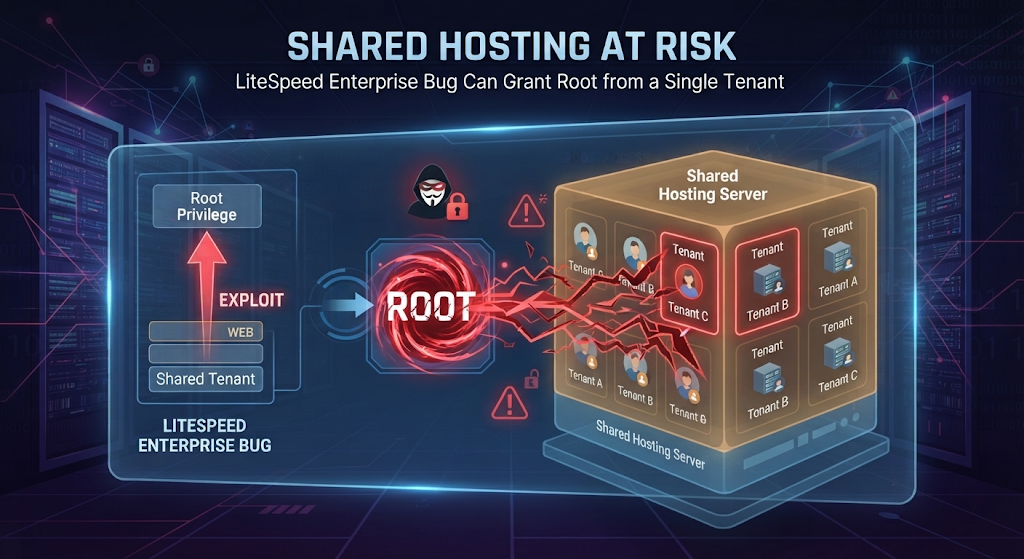
Critical LiteSpeed Enterprise flaw lets one shared hosting account gain root, bypassing CageFS; patch now to 6.3.7 via forced update. cPanel warned that a critical flaw in LiteSpeed Enterprise can ...
Pierluigi Paganini
September 15, 2026

Two China-linked groups ran identical Chrome/Windows zero-day exploits against NGOs, before Chrome's patch shipped, deploying different backdoors each. Two China-linked threat actors used the same ...
Pierluigi Paganini
September 15, 2026
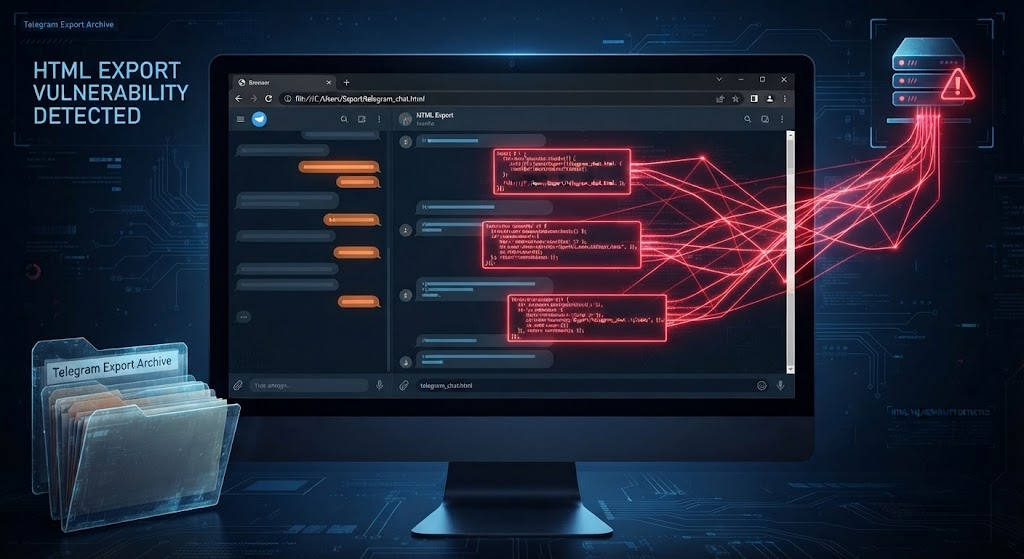
A Telegram Desktop flaw let bots inject JavaScript into exported chats, enabling data theft and page manipulation. Old HTML exports remain unsafe. A vulnerability in Telegram Desktop could have tu ...
Pierluigi Paganini
September 15, 2026
Japan 's Digital Agency disclosed a VPN breach exposing 246,000 government employee records across 23 ministries. Detected June 25, publicly disclosed September 11. Japan 's Digital Agency disclos ...
Pierluigi Paganini
September 15, 2026
Frontier AI is compressing the attack lifecycle from vulnerability discovery to exploitation, forcing defenders to detect, patch and respond at machine speed. Cybersecurity has always been a race ...
Pierluigi Paganini
September 14, 2026
China rejects Amodei’s AI slowdown proposal, calling it fearmongering and a US attempt to contain China’s technology sector. The debate over whether the world should slow down the development ...
Pierluigi Paganini
September 14, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds GitLab, JFrog Artifactory, and ConnectWise ScreenConnect flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecu ...
Pierluigi Paganini
September 14, 2026

Two critical Check Point VPN flaws score 9.8 and could enable remote code execution. Patch now and restrict VPN access before exploitation begins. The Dutch NCSC warns that two critical vulnerabil ...
Pierluigi Paganini
September 14, 2026

Anthropic CEO calls for AI slowdown, proposes embedded evaluators and global coordination. Geopolitical competition with China makes a voluntary pause structurally fragile. Dario Amodei published ...
Pierluigi Paganini
September 14, 2026

Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter REVSTEALER ramps up Breaking the Seal ...
Pierluigi Paganini
September 13, 2026

A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly Security ...
Pierluigi Paganini
September 13, 2026
CVE-2026-85706, a CVSS 10.0 GitLab path traversal, was under active exploitation within 24 hours of disclosure. GitLab disclosed CVE-2026-85706 (CVSS score of 10.0) on September 10, 2026, a path t ...
Pierluigi Paganini
September 13, 2026

Ukrainian lawyer and Conti malware developer Oleksii Lytvynenko was sentenced to four years in U.S. prison for ransomware attacks. Oleksii Oleksiyovych Lytvynenko had, by most accounts, a fairly o ...
Pierluigi Paganini
September 13, 2026
AI is becoming an operational force for cybercrime, surveillance, propaganda, fraud and weapons development, lowering the cost and scale of attacks. Artificial intelligence (AI) is becoming more t ...
Pierluigi Paganini
September 12, 2026

Researchers found 36,769 exposed AI endpoints, but only 2% had an HTTP authentication gate. Running AI locally is supposed to give organizations more control. Models, prompts and documents stay on ...
Pierluigi Paganini
September 11, 2026
Three threat groups are exploiting two Cisco FMC flaws to steal credentials, gain root access and deploy Qilin ransomware. Cisco Talos says three separate threat groups are exploiting two recently ...
Pierluigi Paganini
September 11, 2026

A critical SonicWall flaw was rapidly weaponized, with a UK Council attack linked to a campaign that exposed credentials and enabled Active Directory theft. On July 17, 2026, the Borough Council o ...
Pierluigi Paganini
September 11, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Cisco, Google Chromium V8, Fortinet, and Citrix NetScaler flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecu ...
Pierluigi Paganini
September 10, 2026