Pierluigi Paganini
 September 15, 2026

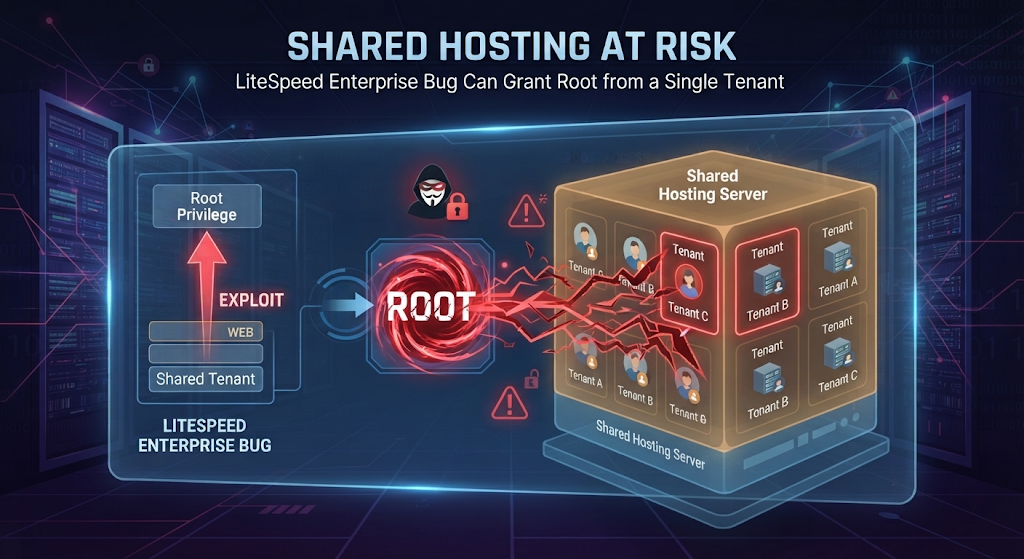
cPanel warned that a critical flaw in LiteSpeed Enterprise can let a low‑privilege website user break out of their account and gain root on the whole server. On a box where dozens or hundreds of customers live side by side, that’s not a theoretical risk. It’s a full cross‑tenant compromise. Attackers could then access or modify other websites and the server itself.
“We have received notice that a critical privilege-escalation vulnerability has been identified in LiteSpeed Web Server Enterprise. On shared-hosting servers, a malicious low-privilege website user could potentially gain root-level access to the server. This could allow an attacker to access or alter other hosted websites and the server itself.” reads the advisory.
“This issue can bypass expected account isolation controls, including CageFS, allowing a malicious website user to potentially escape its restricted environment and gain root-level access to the server.”
The flaw affects versions before 6.3.7 and can bypass the isolation that keeps hosting accounts apart, including CageFS. CageFS is the CloudLinux layer that gives each account a restricted view of the filesystem so it can’t peek at other users or server configs.
If this flaw truly defeats that boundary, then one bad tenant can read or change other sites and take control of the machine.
Neither cPanel nor LiteSpeed disclosed technical details about the vulnerability. LiteSpeed’s September 11 announcement for 6.3.7 just mentions “Security improvements, bug fixes, and more!” and the changelog lists three security changes without calling out a privilege‑escalation issue.
There’s no CVE or severity rating yet, and it’s unclear whether attackers are already exploiting the flaw.
Both cPanel and LiteSpeed urge admins to run this command to update their installs:
/usr/local/lsws/admin/misc/lsup.sh -f -v 6.3.7
LiteSpeed warns that version 6.3.7 may take some time to reach the stable auto-update channel. As of September 15, the download page still listed 6.3.6 as the latest stable version. Forcing 6.3.7 means temporarily leaving the stable update channel, which can be restored later.
There’s no workaround for systems you can’t patch immediately. The advisory only covers the Enterprise edition; OpenLiteSpeed, the open‑source variant, had no matching update as of September 15.
LiteSpeed-related flaws have now been linked to three root-level escapes on cPanel shared-hosting servers since May.
This year, LiteSpeed fixed two flaws in its cPanel plugin, CVE-2026-48172 and CVE-2026-54420, which were being actively exploited in the wild. CISA added both issues to is Known Exploited Vulnerabilities catalog.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, LiteSpeed)


Security / September 15, 2026