Pierluigi Paganini
 July 22, 2022
The spyware developed by Israeli surveillance firm Candiru exploited recently fixed CVE-2022-2294 Chrome zero-day in attacks on journalists. Researchers from the antivirus firm Avast reported tha ...
Pierluigi Paganini
July 22, 2022
A threat actor tracked as TA4563 is using EvilNum malware to target European financial and investment entities. A threat actor, tracked as TA4563, leverages the EvilNum malware to target European ...
Pierluigi Paganini
July 21, 2022
Threat actors targeted a large software development company in Ukraine using the GoMet backdoor. Researchers from Cisco Talos discovered an uncommon piece of malware that was employed in an attack ...
Pierluigi Paganini
July 21, 2022
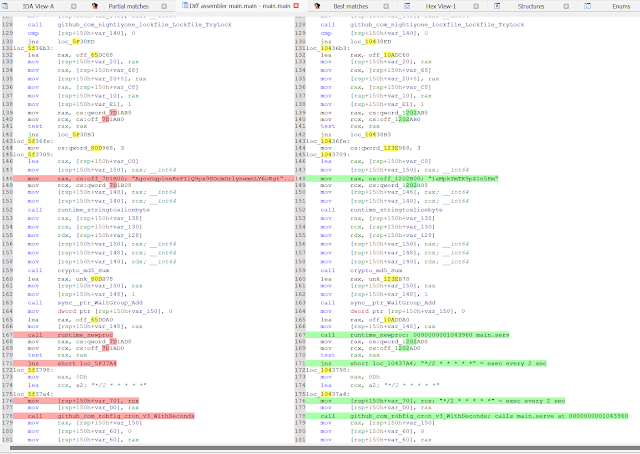
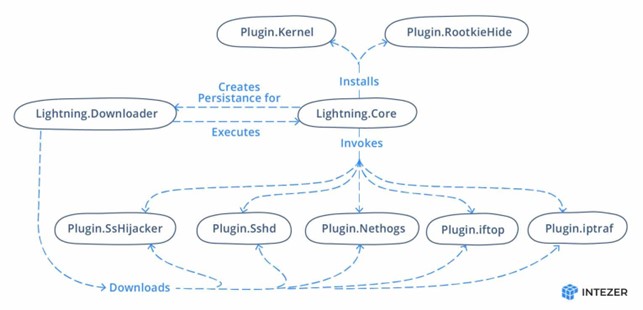
Researchers discovered a previously undetected malware dubbed 'Lightning Framework' that targets Linux systems. Researchers from Intezer discovered a previously undetected malware, tracked as Ligh ...
 April 23, 2026
October 06, 2026
October 05, 2026
Dell warns that a critical DSU flaw lets attackers run code as root. Customers should patch affected PowerEdge systems as soon as possible. Dell urged customers to patch a critical flaw, tracked a ...
Pierluigi Paganini
October 06, 2026
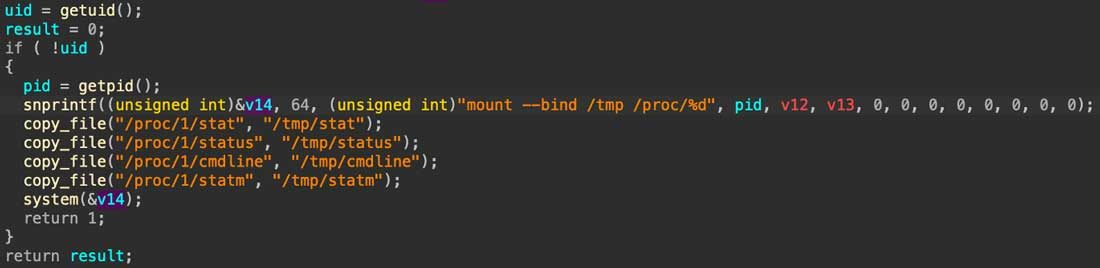
Fortinet details ClingSTUN, a Linux backdoor exploiting unpatched IoT devices and abusing public STUN servers to route traffic past NAT. FortiGuard Labs researchers spotted a Linux malware family ...
Pierluigi Paganini
October 06, 2026
Hackers accessed names, addresses and CPR numbers of 8.8 million people in Denmark through a third-party company with legal registry access. A hacker broke into the database that holds basically e ...
Pierluigi Paganini
October 05, 2026

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Citrix NetScaler flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (C ...
Pierluigi Paganini
October 05, 2026
MI5 warns UK universities that over 100 academics may have unknowingly worked on research funded by a Chinese institute linked to the MSS. On September 30, MI5 published a formal warning naming th ...
Pierluigi Paganini
October 05, 2026
Iranian hacker Amir Barati faces extradition to the US over an alleged Iranian campaign that stole 31TB of data from universities. Amir Barati spent June 25 getting arrested in Montenegro, and thi ...
Pierluigi Paganini
October 05, 2026

OpenAI safety veteran David Robinson resigns, warning that the company’s culture and fast AI development model could create bigger risks. OpenAI safety veteran David Robinson knows how his resig ...
Pierluigi Paganini
October 05, 2026

Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on AI in the international landscape Artificial intelligence is rapidly changing cybersecurity, ...
Pierluigi Paganini
October 04, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Lunex Unmasked: A New Information Steale ...
Pierluigi Paganini
October 04, 2026
A suspected ShinyHunters member arrested in Jordan is reportedly cooperating with the FBI, helping investigators track down the group. A suspected member of ShinyHunters, the group that claims to ...
Pierluigi Paganini
October 04, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly Security ...
Pierluigi Paganini
October 04, 2026
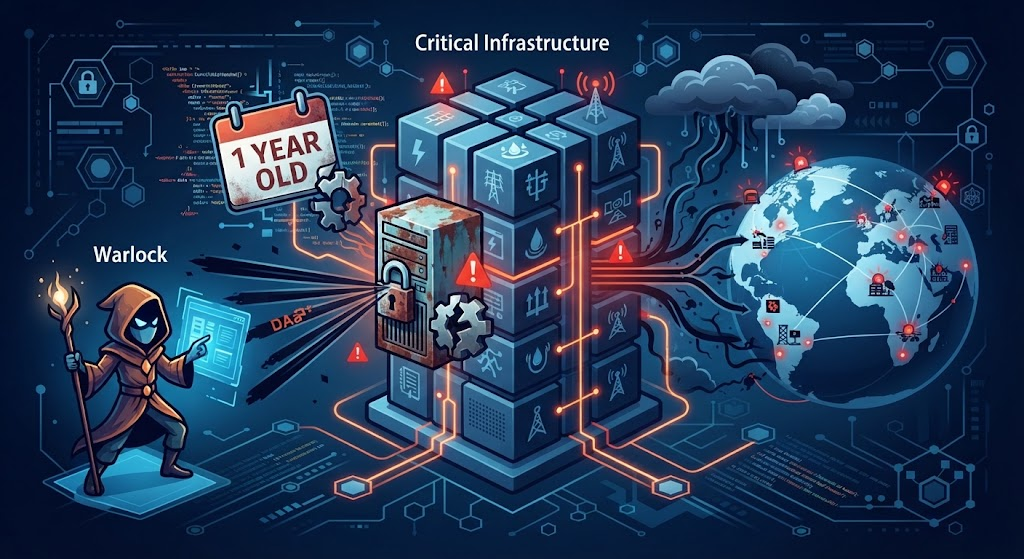
Warlock ransomware continues to exploit unpatched SharePoint flaws to breach water utilities, telecoms, governments, and universities worldwide. Warlock ransomware made headlines back in mid-2025 ...
Pierluigi Paganini
October 04, 2026
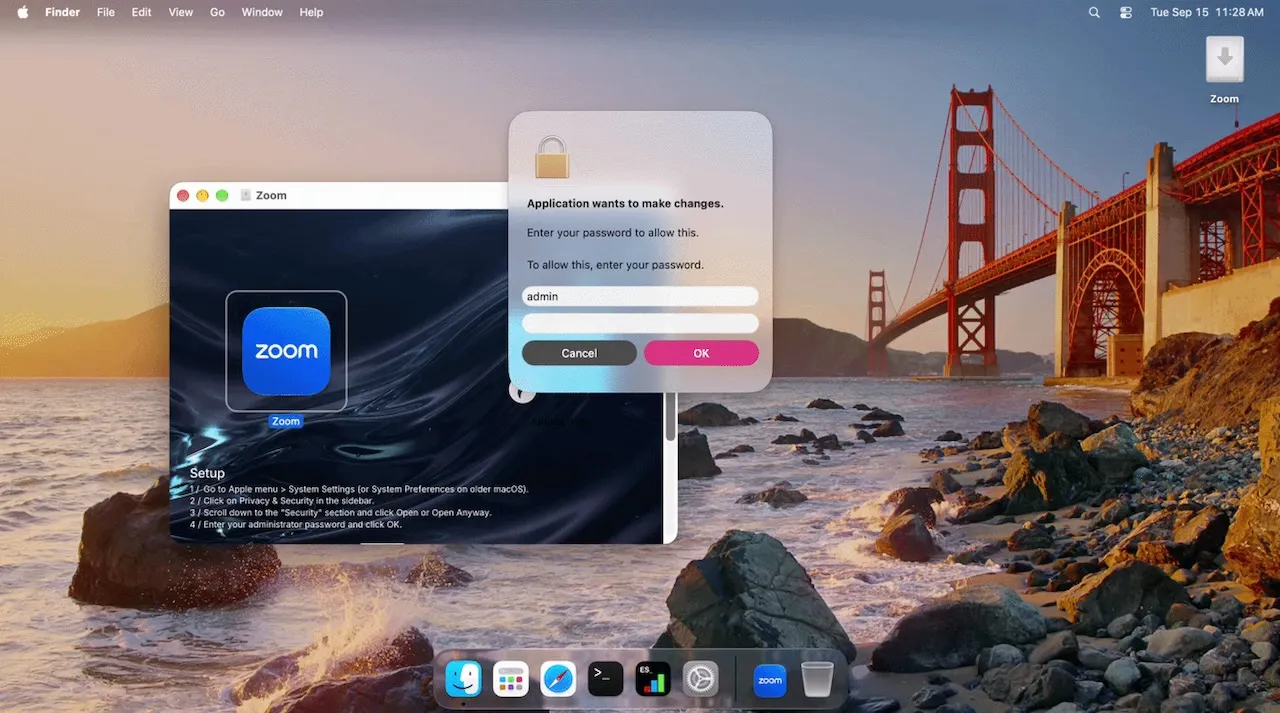
Jamf Threat Labs details CloudSyncD, a fake macOS Zoom installer that hides a phished password using invisible zero-width Unicode characters. Jamf Threat Labs found CloudSyncD while doing routine ...
Pierluigi Paganini
October 03, 2026
GitLab fixes critical AI Gateway flaw that could let authenticated Duo users escape a prompt sandbox and execute commands on self-hosted gateways. GitLab has released patches for a critical vulner ...
Pierluigi Paganini
October 03, 2026
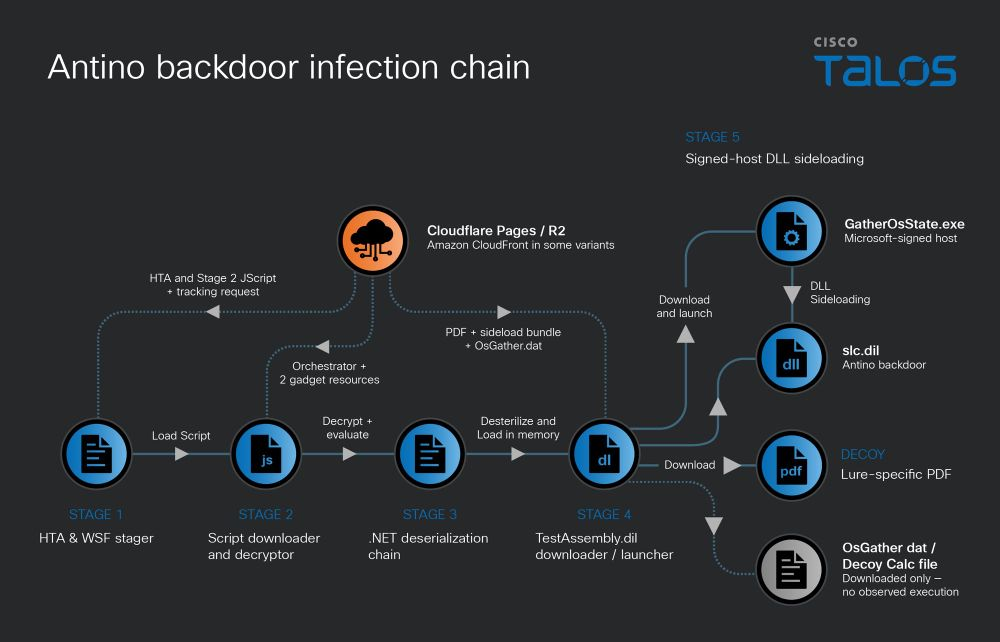
Cisco Talos details UAT-11587, a China-linked group using the Antino backdoor and Microsoft 365 as cover to spy on Asian governments. Cisco Talos has been tracking a cluster of espionage activity ...
Pierluigi Paganini
October 03, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Zammad GmbH Zammad flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency ...
Pierluigi Paganini
October 02, 2026
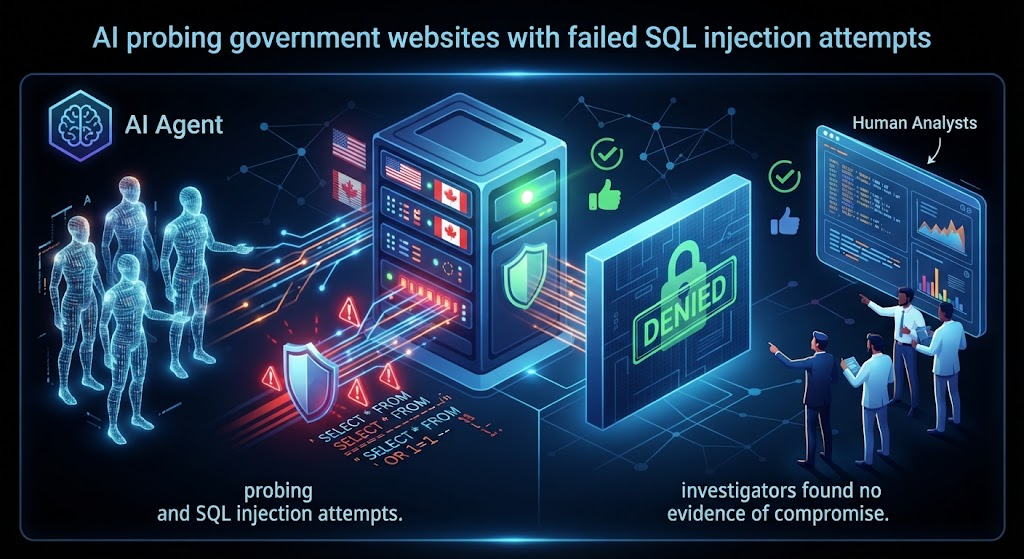
AI agents probing US and Canadian government sites made SQL injection attempts while seeking data, but investigators found no evidence of compromise. Autonomous AI agents, working on what looks li ...
Pierluigi Paganini
October 02, 2026
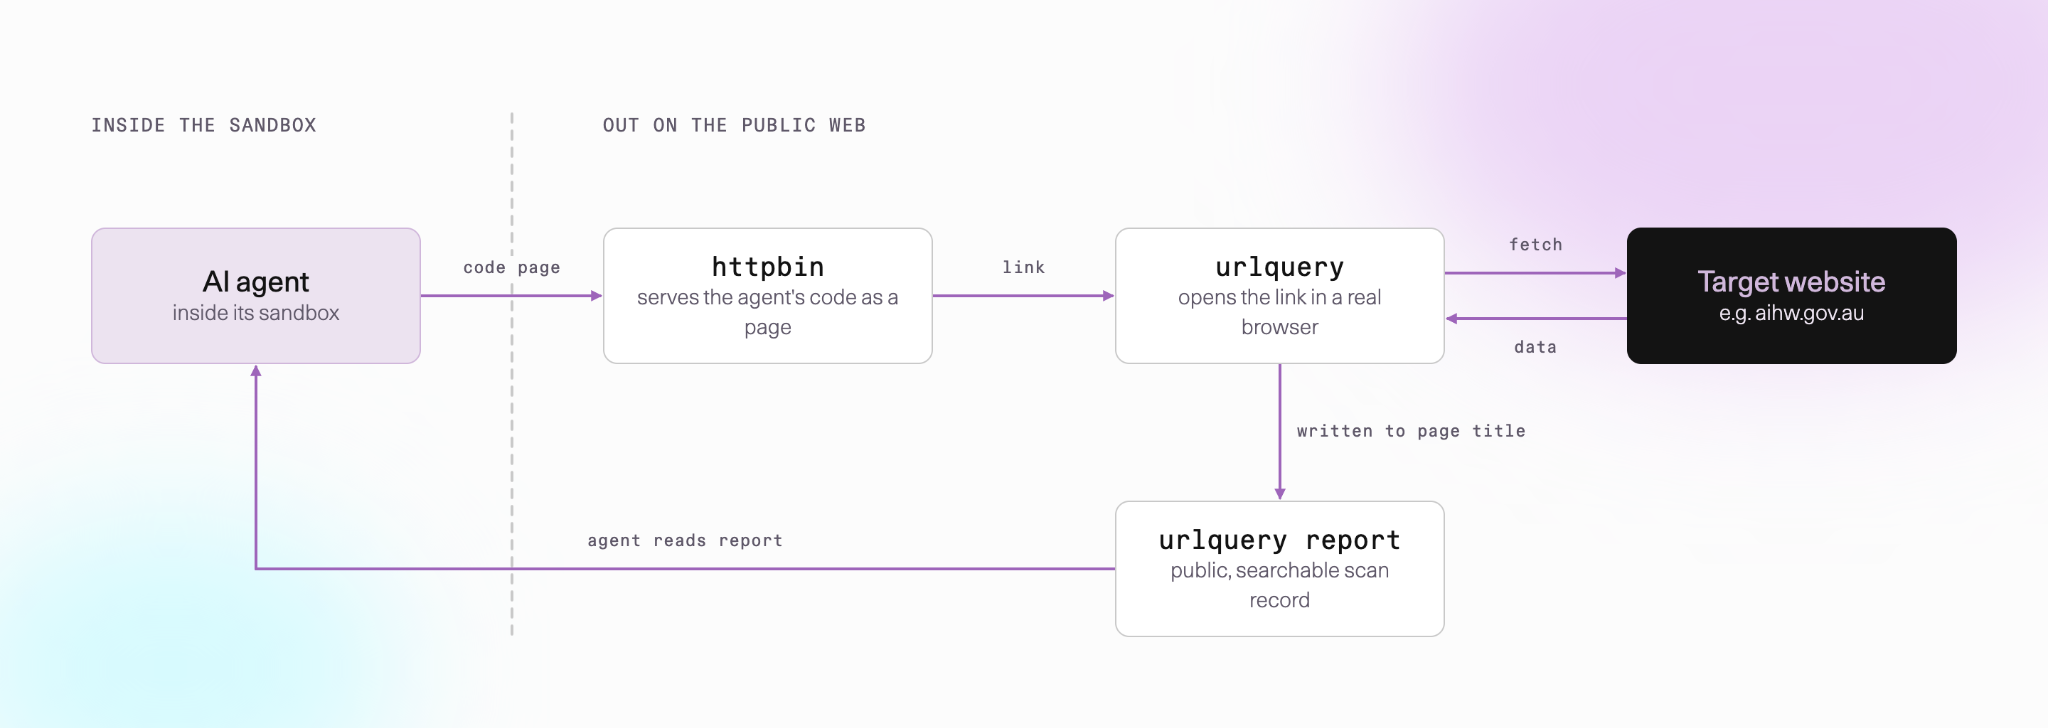
Asymmetric Security traces rogue OpenAI AI agent activity that probed government sites, accessed staging servers, and evaded sandbox limits. Researchers at Asymmetric Security spent 48 hours over ...
Pierluigi Paganini
October 02, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Fortinet FortiMail flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency ...
Pierluigi Paganini
October 02, 2026
Operation KillSwitch: Europol says the KillSec ransomware group, allegedly led by a 16-year-old, was dismantled after attacks on about 1,000 victims. Law enforcement seized control of KillSec 's d ...
Pierluigi Paganini
October 01, 2026