19290 results
 Pierluigi Paganini
 May 27, 2024
Organizations had to re-examine the traditional business perimeter and migrate to cloud-based tools to support distributed workforces. What is the impact? The almost overnight shift to remote work, driven by the COVID-19 pandemic, has profoundly impacted how businesses use technology. Organizations across the globe had to adapt and adapt quickly. They had to re-examine the […]
 Pierluigi Paganini
May 27, 2024
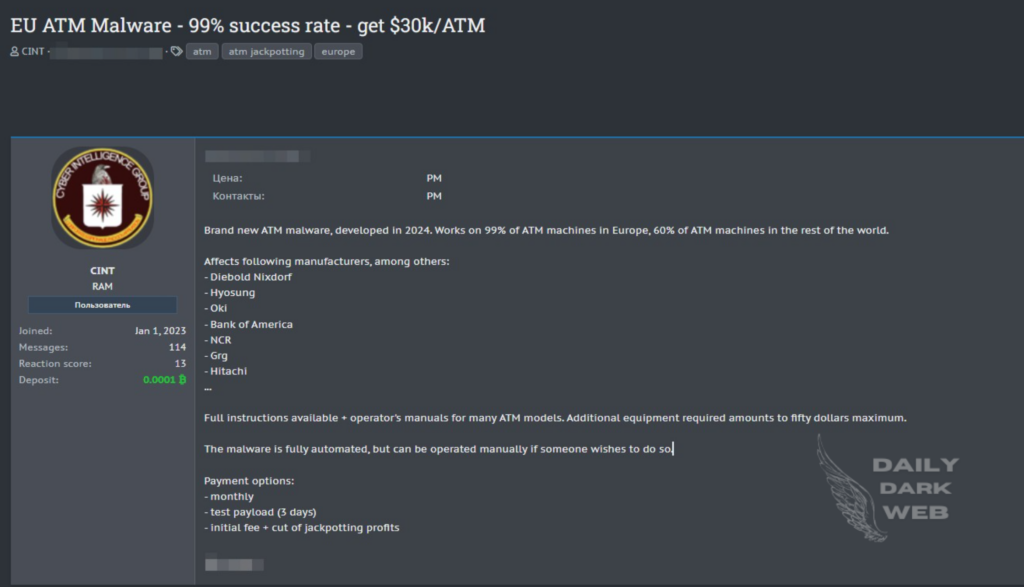
Experts warn of a new ATM malware family that is advertised in the cybercrime underground, it was developed to target Europe. A threat actor is advertising a new ATM malware family that claims to be able of compromised 99% of devices in Europe. The threat actor is offering the malware for $30,000, he claims that […]
 Pierluigi Paganini
May 27, 2024
Cisco addressed a SQL injection vulnerability in the web-based management interface of the Firepower Management Center (FMC) Software. Cisco addressed a vulnerability, tracked as CVE-2024-20360 (CVSS score 8.8), in the web-based management interface of the Firepower Management Center (FMC) Software. The vulnerability is a SQL injection issue, an attacker can exploit the flaw to obtain […]
 Pierluigi Paganini
May 26, 2024
The Ukraine CERT-UA warns of a concerning increase in cyberattacks attributed to the financially-motivated threat actor UAC-0006. The Computer Emergency Response Team of Ukraine (CERT-UA) warned of surge in in cyberattacks linked to the financially-motivated threat actor UAC-0006. UAC-0006 has been active since at least 2013. The threat actors focus on compromising accountants’ PCs (which […]
 Pierluigi Paganini
May 26, 2024
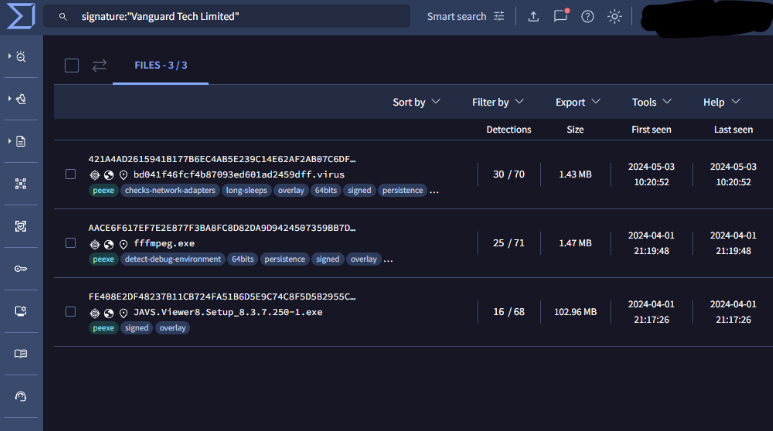
Malicious actors compromised the JAVS Viewer installer to deliver the RustDoor malware in a supply chain attack. Rapid7 researchers warned that threat actors added a backdoor to the installer for the Justice AV Solutions JAVS Viewer software. The attackers were able to inject a backdoor in the JAVS Viewer v8.3.7 installer that is being distributed from […]
 Pierluigi Paganini
May 25, 2024
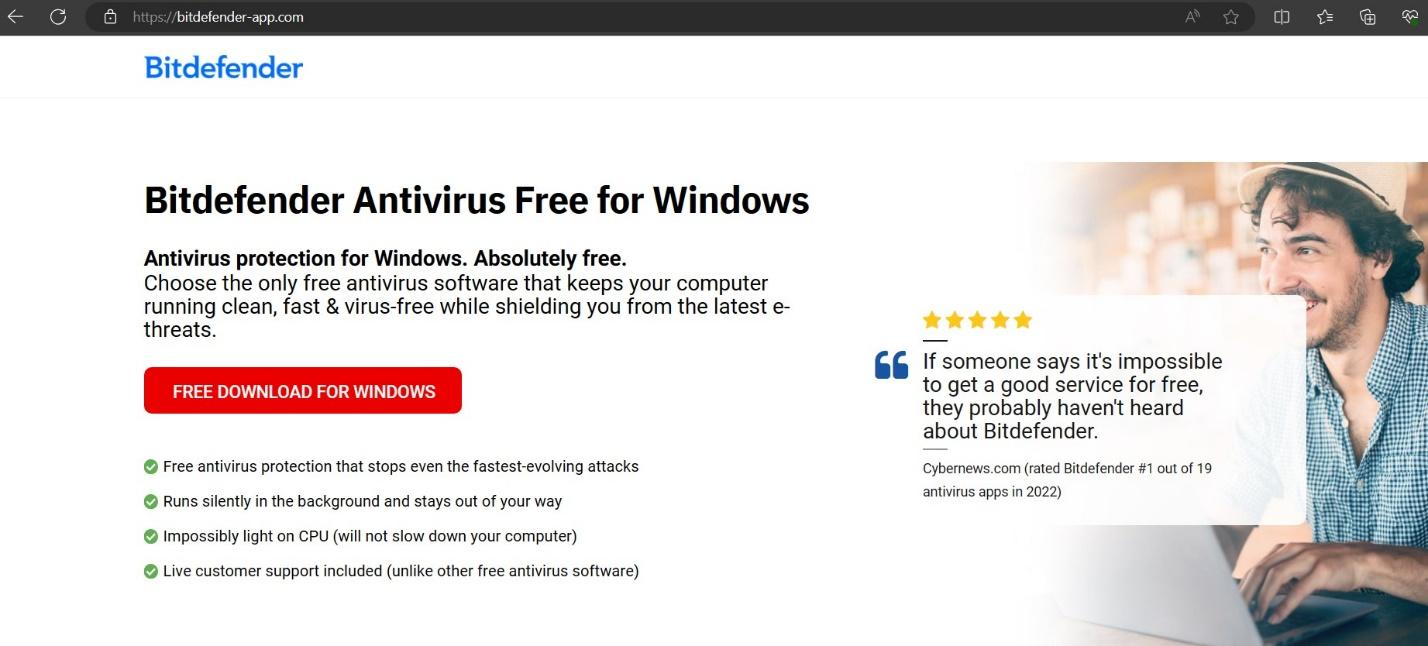
Threat actors used fake AV websites masquerading as legitimate antivirus products from Avast, Bitdefender, and Malwarebytes to distribute malware. In mid-April 2024, researchers at Trellix Advanced Research Center team spotted multiple fake AV sites used to distribute info-stealers. The malicious websites hosted sophisticated malicious files such as APK, EXE and Inno setup installer, including Spy […]
 Pierluigi Paganini
May 25, 2024
The MITRE Corporation revealed that threat actors behind the December 2023 attacks created rogue virtual machines (VMs) within its environment. The MITRE Corporation has provided a new update about the December 2023 attack. In April 2024, MITRE disclosed a security breach in one of its research and prototyping networks. The security team at the organization […]
 Pierluigi Paganini
May 24, 2024
GitLab addressed a high-severity cross-site scripting (XSS) vulnerability that allows unauthenticated attackers to take over user accounts. GitLab fixed a high-severity XSS vulnerability, tracked as CVE-2024-4835, that allows attackers to take over user accounts. An attacker can exploit this issue by using a specially crafted page to exfiltrate sensitive user information. The vulnerability impacts versions 15.11 before […]
 Pierluigi Paganini
May 24, 2024
UK data watchdog is investigating Microsoft regarding the new Recall feature in Copilot+ PCs that captures screenshots of the user’s laptop every few seconds. The UK data watchdog, the Information Commissioner’s Office (ICO), is investigating a new feature, called Recall, implemented by Microsoft” Copilot+ PCs that captures screenshots of the user’s laptop every few seconds. […]
 Pierluigi Paganini
May 23, 2024
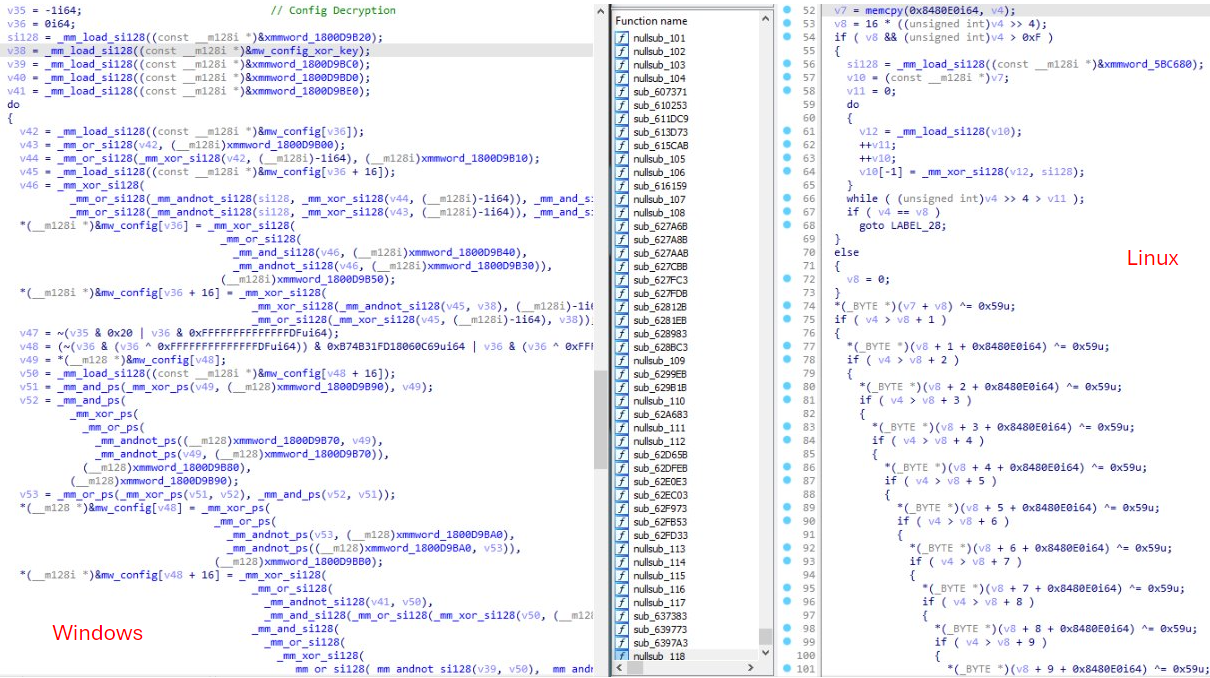
Tinexta Cyber’s Zlab Malware Team uncovered a backdoor known as KeyPlug employed in attacks against several Italian industries During an extensive investigation, Tinexta Cyber’s Zlab Malware Team uncovered a backdoor known as KeyPlug, which hit for months a variety of Italian industries. This backdoor is attributed to the arsenal of APT41,a group whose origin is […]