19288 results
 Pierluigi Paganini
 September 30, 2023
The U.S. Federal Bureau of Investigation (FBI) warns of dual ransomware attacks aimed at the same victims. The U.S. Federal Bureau of Investigation (FBI) is warning of dual ransomware attacks, a new worrisome trend in the threat landscape that sees threat actors targeting the same victims two times. “As of July 2023, the FBI noted […]
 Pierluigi Paganini
September 30, 2023
Progress Software has addressed a critical severity vulnerability in its WS_FTP Server software used by thousands of IT teams worldwide. Progress Software warned customers to address a critical severity vulnerability, tracked as CVE-2023-40044 (CVSS score 10), in its WS_FTP Server software which is used by thousands of IT teams worldwide. “The WS_FTP team recently discovered […]
 Pierluigi Paganini
September 30, 2023
A child abuse site has been taken down following a request to German law enforcement by Cybernews research team. A hacker collective, who wanted to remain anonymous, has been relentlessly hunting online crooks who benefit from videos of children being abused. This week, they discovered a website dedicated to pedophiles – it was full of […]
 Pierluigi Paganini
September 29, 2023
Experts warn of a critical zero-day vulnerability, tracked as CVE-2023-42115, in all versions of Exim mail transfer agent (MTA) software. A critical zero-day vulnerability, tracked as CVE-2023-42115 (CVSS score 9.8), affects all versions of Exim mail transfer agent (MTA) software. A remote, unauthenticated attacker, can exploit the vulnerability to gain remote code execution (RCE) on Internet-exposed […]
 Pierluigi Paganini
September 29, 2023
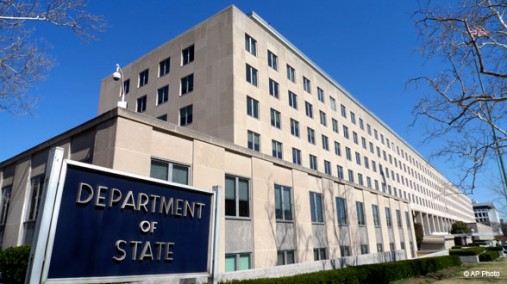
China-linked threat actors stole around 60,000 emails from U.S. State Department after breaching Microsoft’s Exchange email platform in May. China-linked hackers who breached Microsoft’s email platform in May have stolen tens of thousands of emails from U.S. State Department accounts, a Senate staffer told Reuters this week. During a briefing by U.S. State Department IT officials, […]
 Pierluigi Paganini
September 29, 2023
The World Baseball Softball Confederation (WBSC) left open a data repository exposing nearly 50,000 files, some of which were highly sensitive, the Cybernews research team has discovered. On June 5th, our researchers discovered a misconfigured Amazon Web Services (AWS) bucket storing nearly 48,000 files. A bucket is a container for storing data within AWS’s cloud […]
 Pierluigi Paganini
September 29, 2023
US CISA added the flaw CVE-2018-14667 in Red Hat JBoss RichFaces Framework to its Known Exploited Vulnerabilities catalog. US Cybersecurity and Infrastructure Security Agency (CISA) added the critical flaw CVE-2018-14667 (CVSS score 9.8) affecting Red Hat JBoss RichFaces Framework to its Known Exploited Vulnerabilities Catalog. The issue is an Expression Language (EL) injection via the UserResource resource, […]
 Pierluigi Paganini
September 28, 2023
Cisco released security updates for an actively exploited zero-day flaw (CVE-2023-20109) that resides in the GET VPN feature of IOS and IOS XE software. Cisco warned customers to install security updates to address an actively exploited zero-day vulnerability, tracked as CVE-2023-20109 (CVS 6.6), that resides in IOS and IOS XE software. The vulnerability resides in […]
 Pierluigi Paganini
September 28, 2023
Johnson Controls International suffered a ransomware attack that impacted the operations of the company and its subsidiaries. Johnson Controls International plc is a multinational conglomerate with a diversified portfolio of products and services primarily focused on building technologies and solutions. The company provides HVAC (heating, ventilation, and air conditioning), solutions for building automation, fire and […]
 Pierluigi Paganini
September 28, 2023
Google released security updates to address a new actively exploited zero-day vulnerability, tracked as CVE-2023-5217, in the Chrome browser. Google on Wednesday released security updates to address a new actively exploited zero-day flaw in the Chrome browser which is tracked as CVE-2023-5217. The CVE-2023-5217 is a high-severity heap buffer overflow that affects vp8 encoding in […]