


19284 results
 Pierluigi Paganini
 May 29, 2023
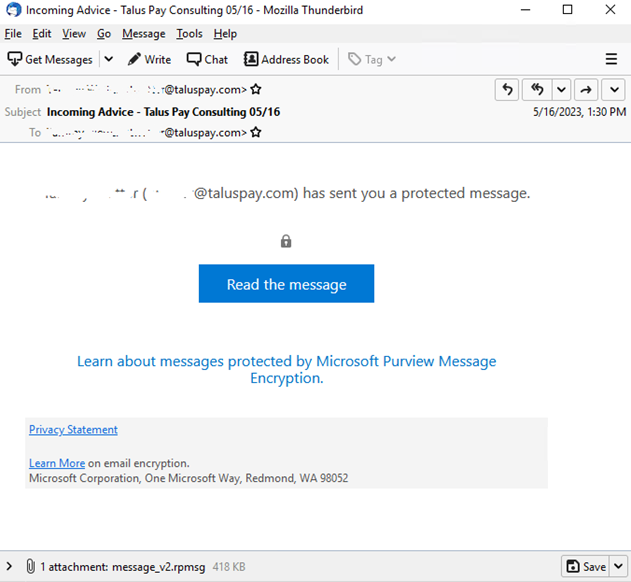
Experts warn of phishing attacks that are combining the use of compromised Microsoft 365 accounts and .rpmsg encrypted emails. Trustwave researchers have observed threat actors using encrypted RPMSG attachments sent via compromised Microsoft 365 accounts in a phishing campaign aimed at stealing Microsoft credentials. RPMSG files are used to deliver e-mails with Rights-Managed Email Object Protocol enabled. […]
 Pierluigi Paganini
May 28, 2023
Swiss electrification and automation technology giant ABB confirmed it has suffered a data breach after a ransomware attack. ABB has more than 105,000 employees and has $29.4 billion in revenue for 2022. On May 7, 2023, the Swiss multinational company, leading electrification and automation technology provider, suffered a cyber attack that reportedly impacted its business operations. […]
 Pierluigi Paganini
May 28, 2023
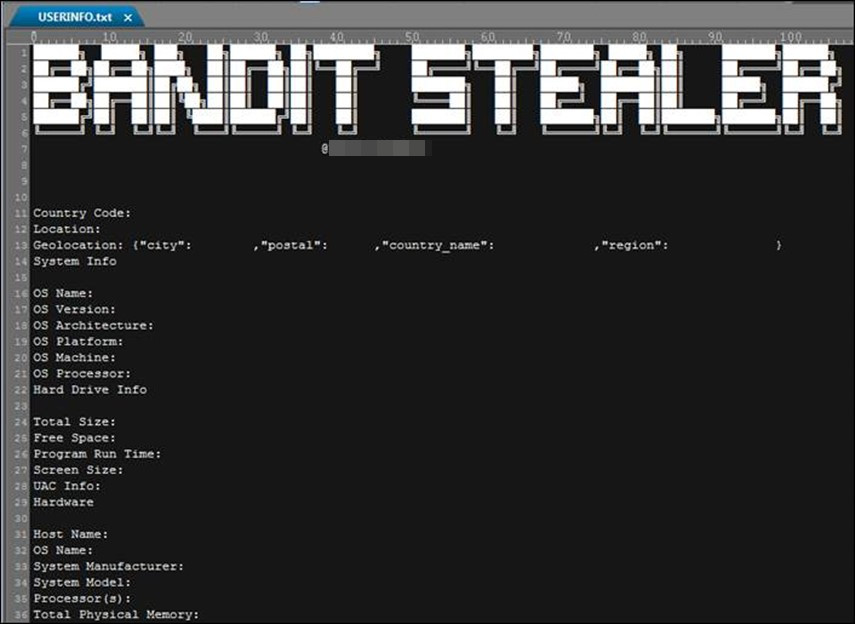
Bandit Stealer is a new stealthy information stealer malware that targets numerous web browsers and cryptocurrency wallets. Trend Micro researchers discovered a new info-stealing malware, dubbed Bandit Stealer, which is written in the Go language and targets multiple browsers and cryptocurrency wallets. At this time, the malware only targets Windows systems, but experts pointed out […]
 Pierluigi Paganini
May 28, 2023
US CISA added recently patched Barracuda zero-day vulnerability to its Known Exploited Vulnerabilities catalog. US Cybersecurity and Infrastructure Security Agency (CISA) added a recently patched Barracuda zero-day vulnerability to its Known Exploited Vulnerabilities Catalog. This week, the network security solutions provider Barracuda warned customers that some of its Email Security Gateway (ESG) appliances were recently breached […]
 Pierluigi Paganini
May 27, 2023
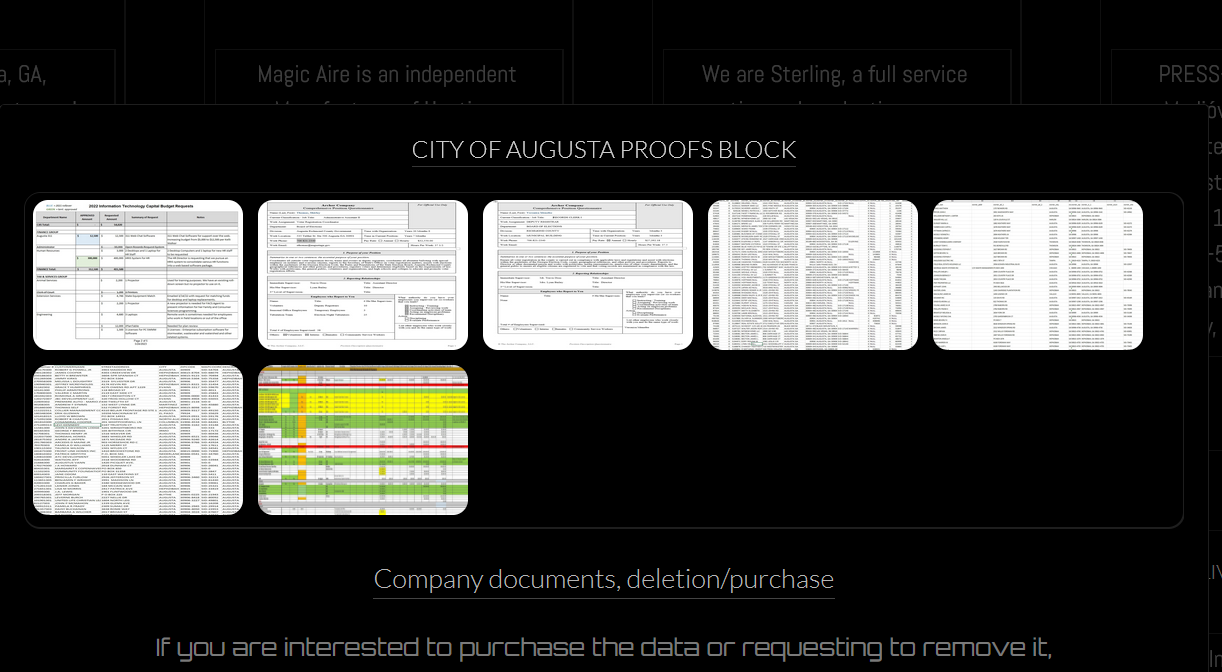
The city of Augusta in Georgia, U.S., admitted that the recent IT system outage was caused by a cyber attack. While the City of Augusta revealed that a cyberattack caused the recent IT outage, the BlackByte ransomware gang has claimed responsibility for the attack. The attack took place on May 21, the administrator at the City […]
 Pierluigi Paganini
May 27, 2023
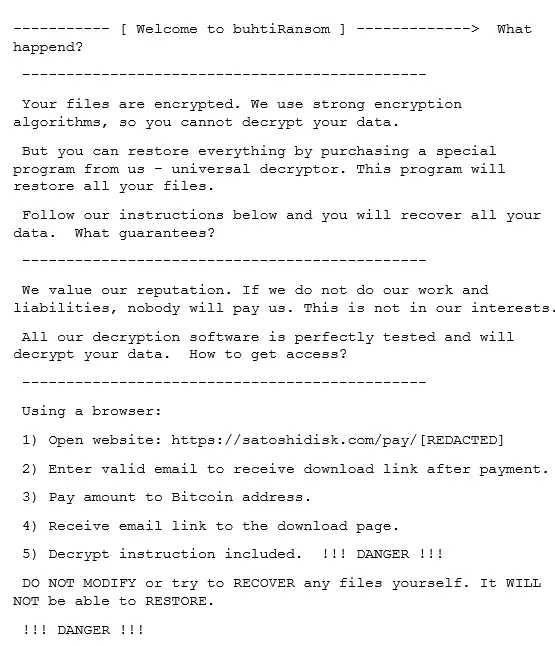
The recently identified Buhti operation targets organizations worldwide with rebranded LockBit and Babuk ransomware variants. Researchers from Symantec discovered a new ransomware operation called Buhti (aka Blacktail) that is using LockBit and Babuk variants to target Linux and Windows systems worldwide. The ransomware operation hasn’t its own ransomware payload, however, it uses a custom information […]
 Pierluigi Paganini
May 02, 2023
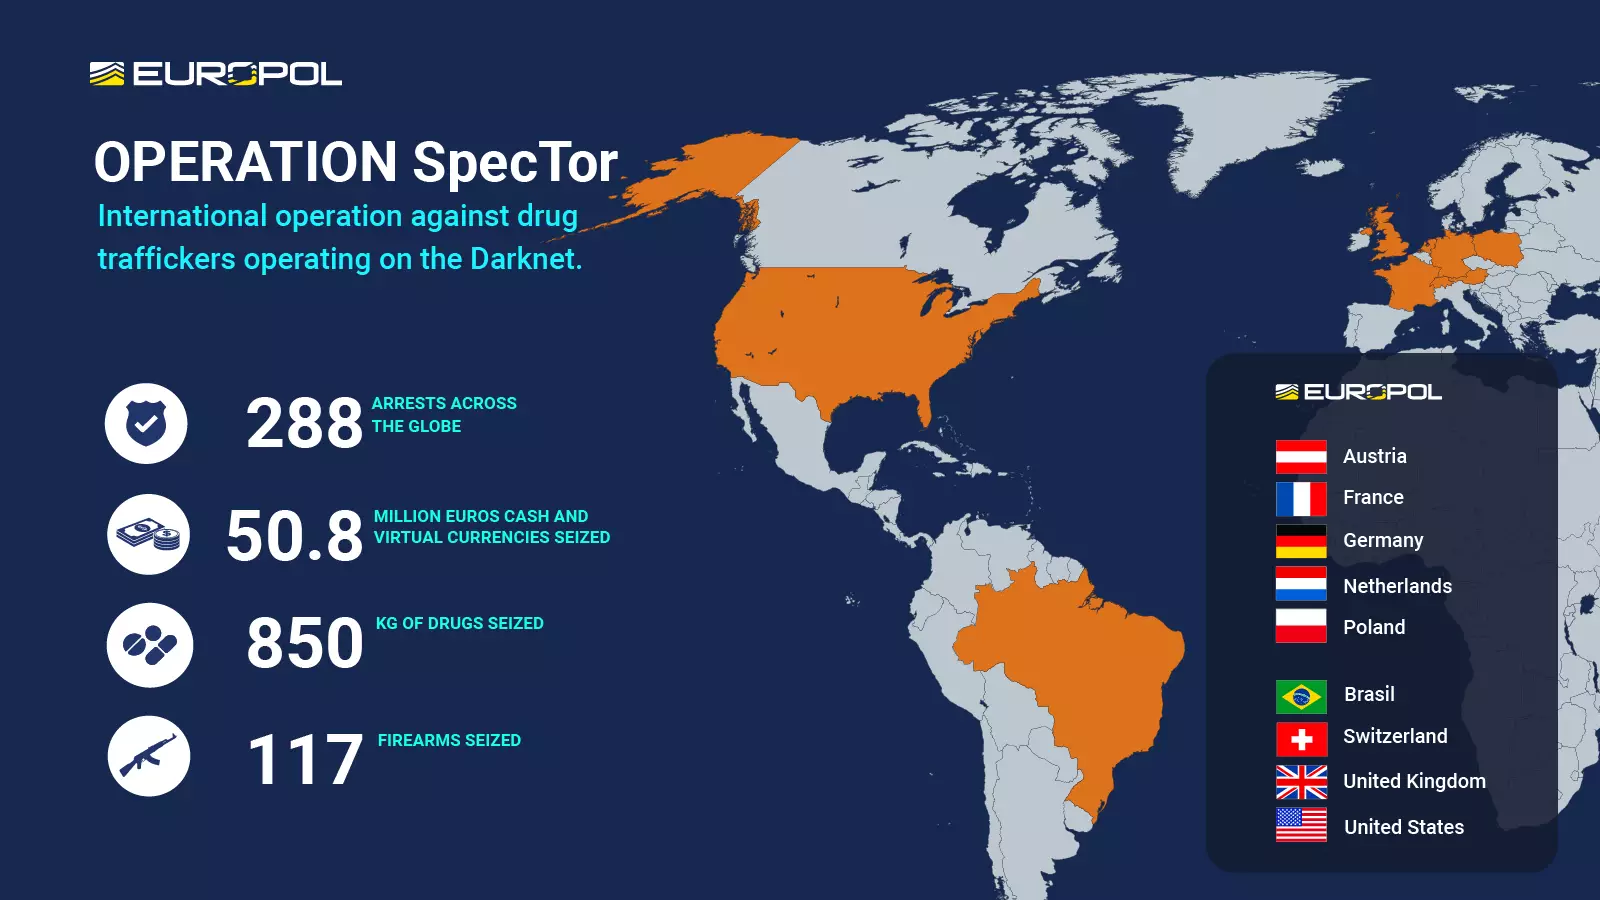
International law enforcement operation SpecTor resulted in the seizure of an online marketplace and the arrest of nearly 300 people. In an international law enforcement operation coordinated by Europol, codenamed ‘SpecTor’, the police seized the illegal dark web marketplace ‘Monopoly Market.’ The law enforcement agencies from nine countries (Austria, France, Germany, the Netherlands, Poland, Brazil, […]
 Pierluigi Paganini
May 02, 2023
Apple has released its first Rapid Security Response update, but many iPhone users reported problems during the installation of the iOS Security Response. On June 2022, Apple announced that the Rapid Security Response feature would be available starting with iOS 16.4.1, iPadOS 16.4.1, and macOS 13.3.1 operating systems. Once a Rapid Security Response has been […]
Pierluigi Paganini
May 02, 2023
US Cybersecurity and Infrastructure Security Agency (CISA) added TP-Link, Apache, and Oracle vulnerabilities to its Known Exploited Vulnerabilities catalog. U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added the following three new issues to its Known Exploited Vulnerabilities Catalog: CVE-2023-1389 (CVSS score: 8.8) – TP-Link Archer AX-21 Command Injection Vulnerability. The CVE-2023-1389 flaw is an unauthenticated […]
 Pierluigi Paganini
May 01, 2023
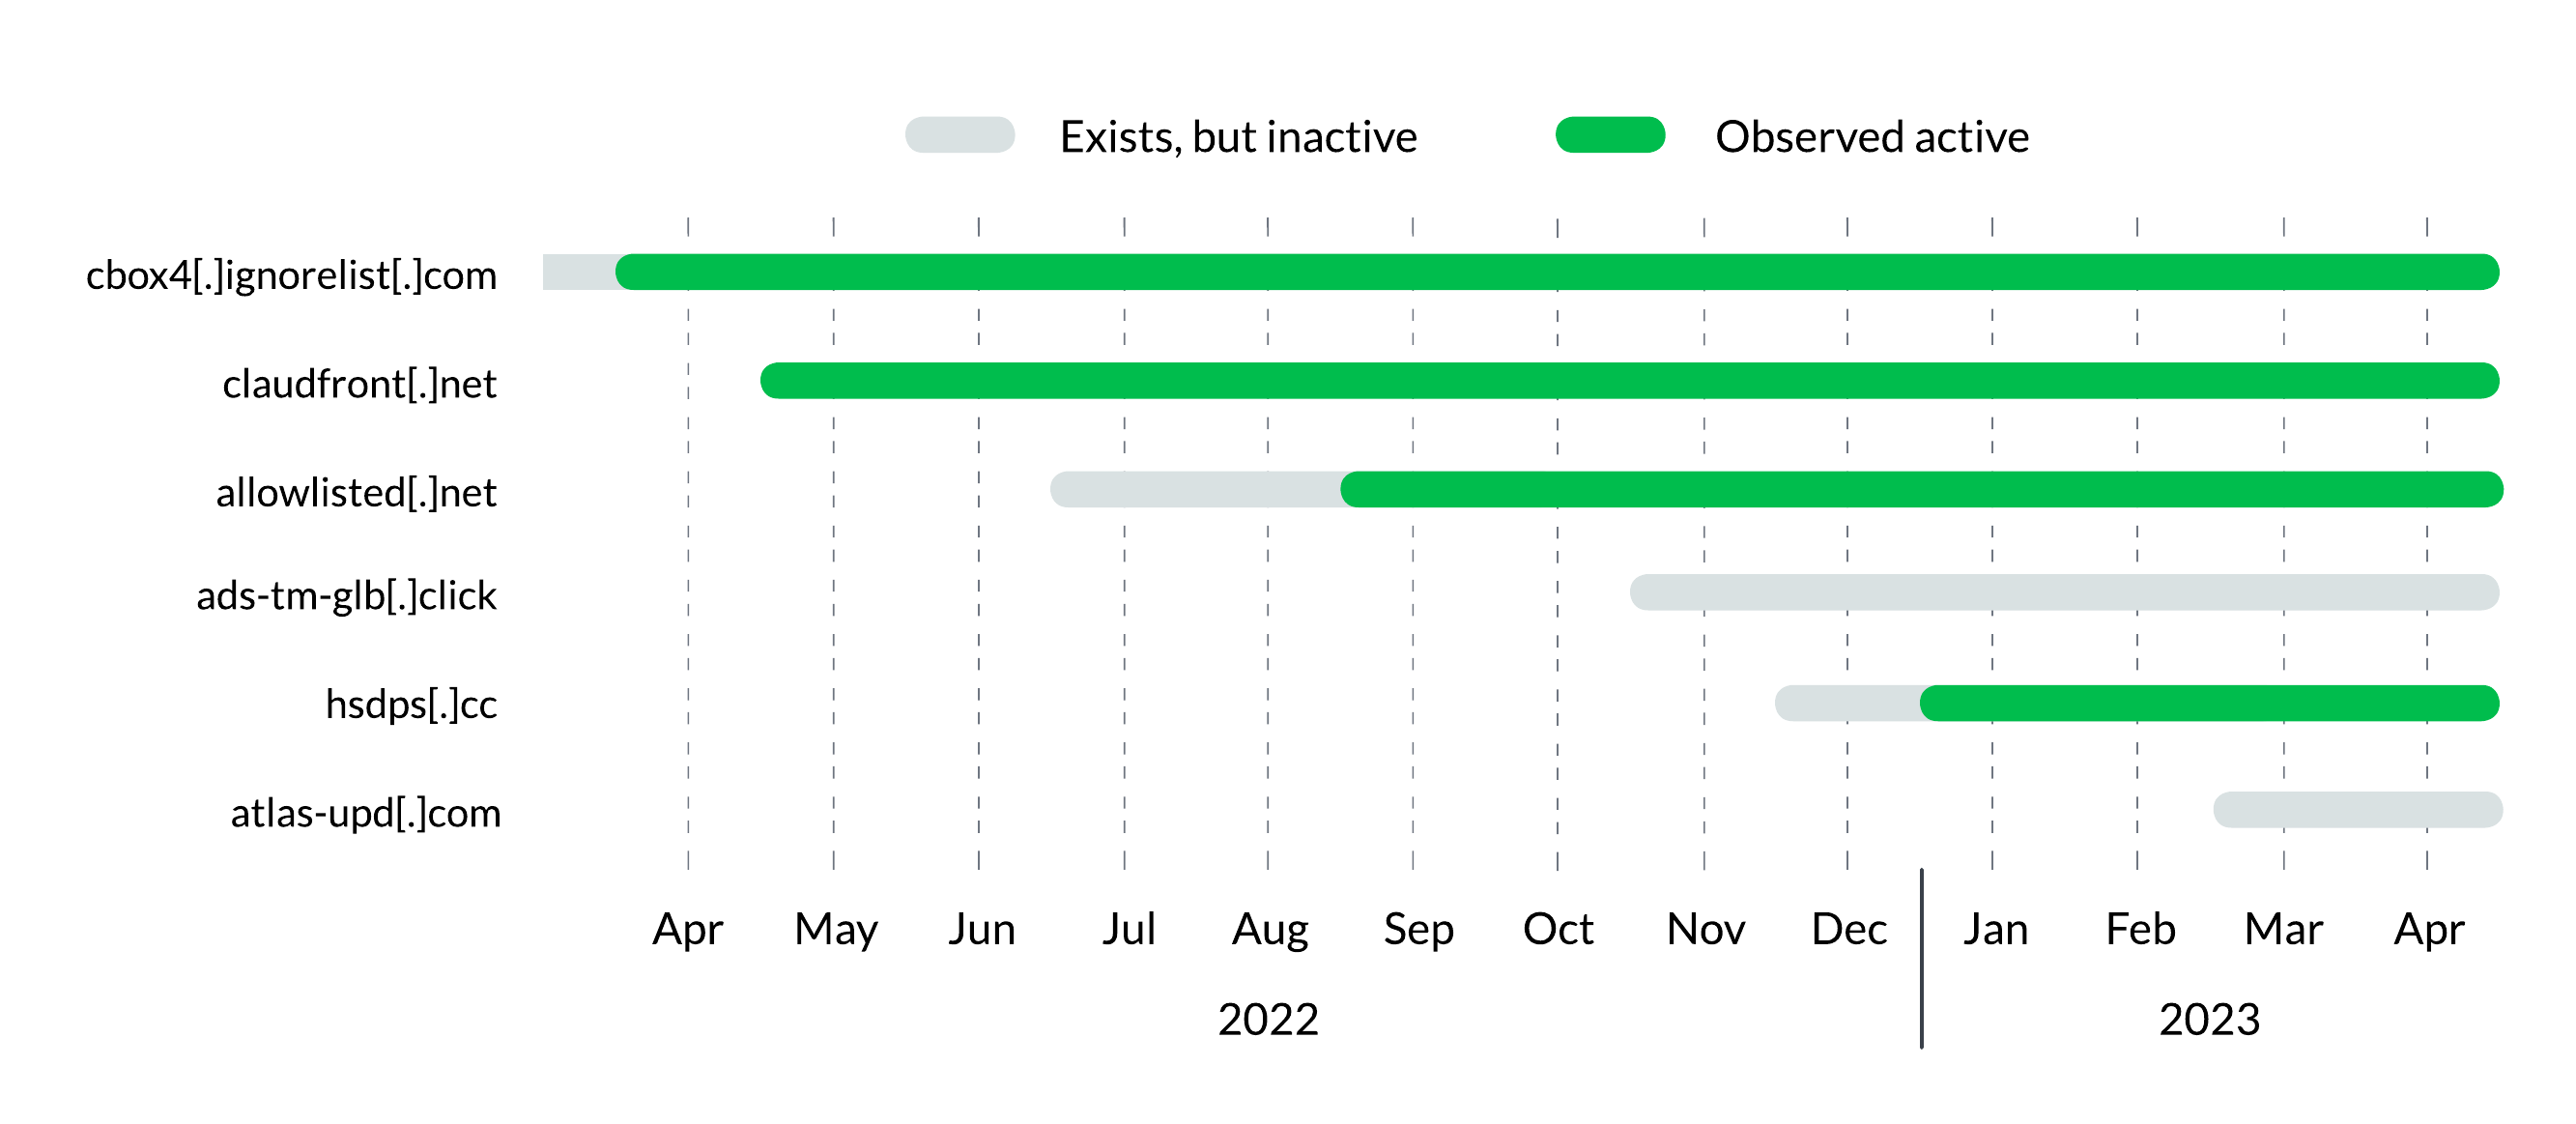
Infoblox researchers discovered a new sophisticated malware toolkit, dubbed Decoy Dog, targeting enterprise networks. While analyzing billions of DNS records, Infoblox researchers discovered a sophisticated malware toolkit, dubbed Decoy Dog, that was employed in attacks aimed at enterprise networks. Threat actors behind the malware were observed using known tricks to avoid detection such as registering a domain, […]
Security / November 12, 2026
Security / November 12, 2026


