19103 results
 Pierluigi Paganini
 March 13, 2022
A new round of the weekly Security Affairs newsletter arrived! Every week the best security articles from Security Affairs free for you in your email box. If you want to also receive for free the newsletter with the international press subscribe here. LockBit ransomware group claims to have hacked Bridgestone Americas Attackers use website contact forms […]
 Pierluigi Paganini
September 17, 2012
Cyber Threat Summit 2012 – 20th & 21th Dublin Pierluigi Paganini presents “The rise of cyber weapons and relative impact on cyber space” About Pierluigi Paganini: Chief Information Security Officer, Security Evangelist, Security Analyst and Freelance Writer. Security expert with over 20 years experience in the field. Certified Ethical Hacker at EC Council […]
 Pierluigi Paganini
September 12, 2026
AI is becoming an operational force for cybercrime, surveillance, propaganda, fraud and weapons development, lowering the cost and scale of attacks. Artificial intelligence (AI) is becoming more than a tool for people who want to do something malicious. It is increasingly becoming part of the operational machinery itself. That is the main message emerging from […]
 Pierluigi Paganini
June 04, 2026
International Operation KRATOS led by Europol dismantled illegal streaming networks, leading to 29 arrests and nine crime groups taken down. An international law enforcement operation, codenamed Operation KRATOS and involving 13 countries (Belgium, Bulgaria, Croatia, France, Greece, Ireland, Italy, the Netherlands, Poland, Romania, Spain, the UK, and the US), spent seven months quietly dismantling the […]
 Pierluigi Paganini
May 23, 2026
Attackers began exploiting Drupal SQL injection flaw CVE-2026-9082 within 48 hours of patch release. Drupal issued a highly critical security patch on May 20 for CVE-2026-9082, a SQL injection vulnerability that allows unauthenticated attackers to compromise sites running PostgreSQL databases. The project maintainers warned ahead of the release that exploits could surface within hours or […]
 Pierluigi Paganini
May 15, 2026
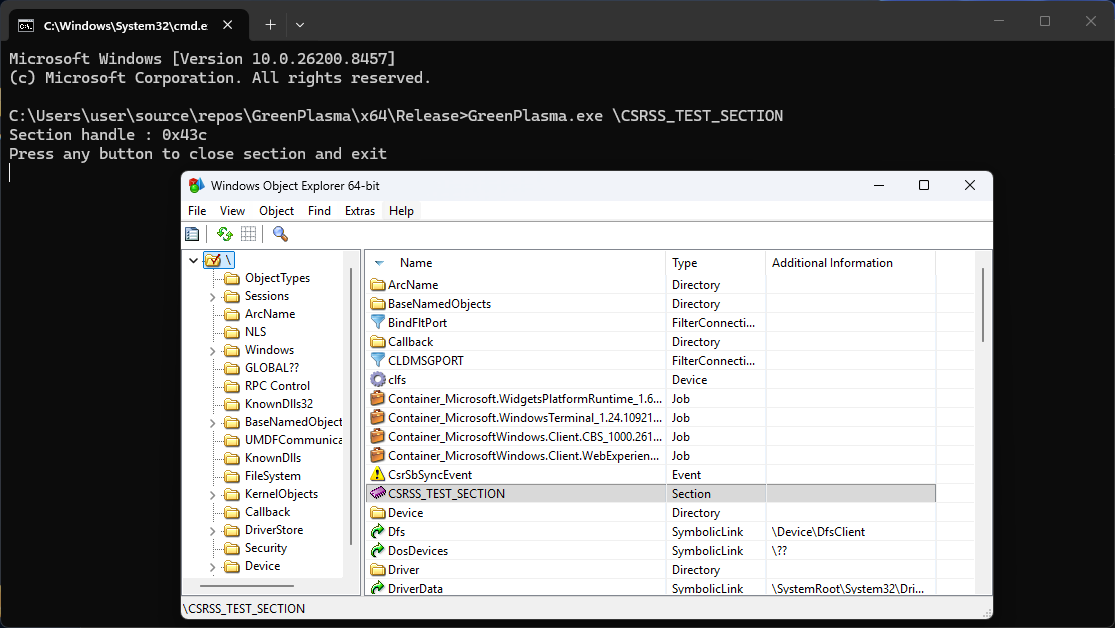
Researchers disclosed two new Windows zero-days named YellowKey and GreenPlasma affecting BitLocker and the CTFMON framework. A security researcher known as Chaotic Eclipse, also called Nightmare-Eclipse, disclosed two new Windows zero-day vulnerabilities named YellowKey and GreenPlasma. The flaws affect BitLocker and the Windows Collaborative Translation Framework (CTFMON). YellowKey could allow attackers to bypass BitLocker protections, […]
 Pierluigi Paganini
May 01, 2026
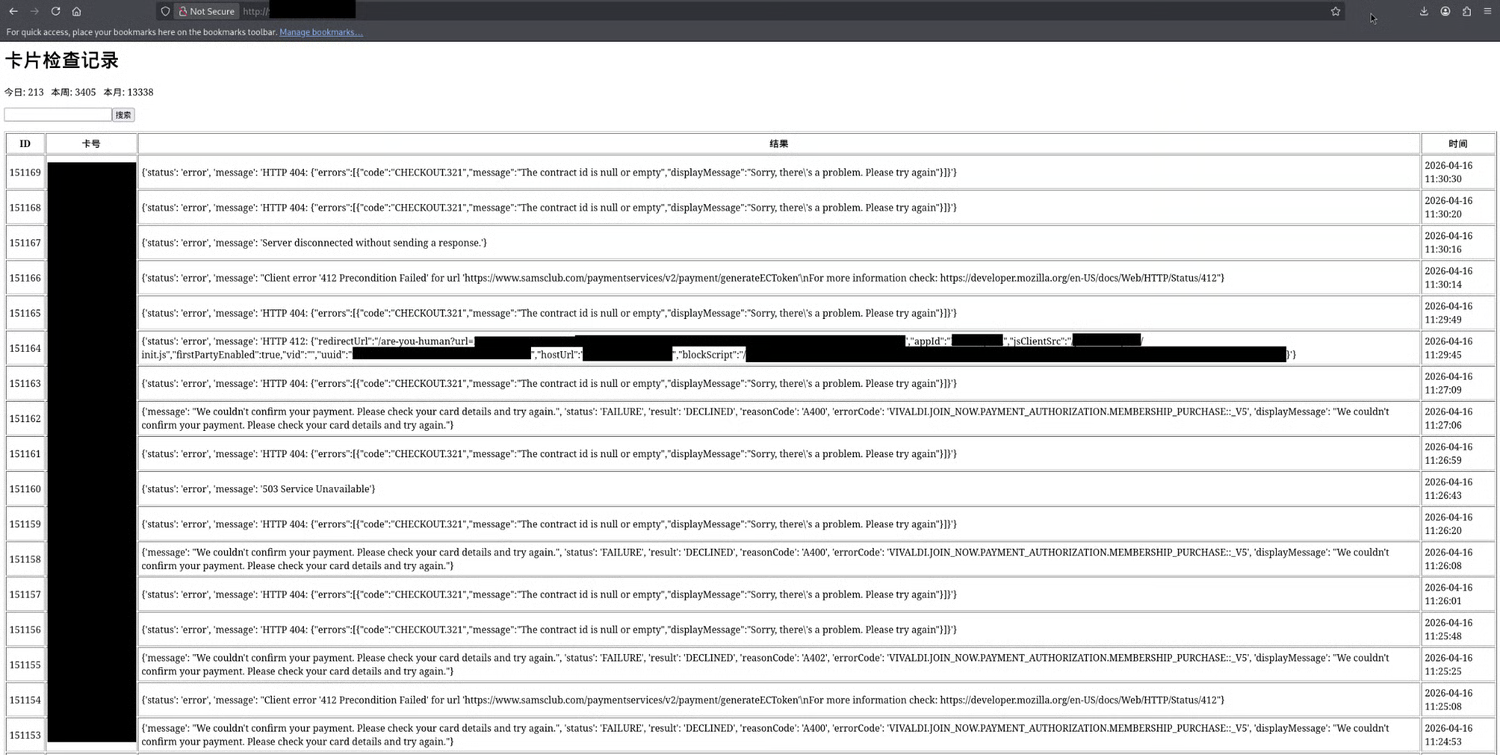
Jerry’s Store, a card-checking service used by cybercriminals, exposed 345,000 stolen payment cards after leaving its server open, revealing sensitive data. A cybercriminal operation known as Jerry’s Store has reportedly exposed a large cache of stolen payment card data after leaving its own infrastructure accessible online. The service appears to have been used to test […]
Pierluigi Paganini
April 21, 2026
Axios reports the National Security Agency uses Anthropic Mythos model despite Department of Defense concerns, blurring AI risk vs defense lines. The reported use of Anthropic’s Mythos model by the U.S. National Security Agency is a reminder that the line between AI as a defensive tool and AI as a security risk is getting harder […]
 Pierluigi Paganini
March 26, 2026
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds a flaw in Langflow to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Langflow flaw, tracked as CVE-2026-33017 (CVSS score of 9.3), to its Known Exploited Vulnerabilities (KEV) catalog. Langflow is a popular tool used for building agentic AI workflows. CVE-2026-33017 is a […]
 Pierluigi Paganini
March 02, 2026
“ClawJacked” flaw let malicious sites hijack OpenClaw AI agents to steal data; patch released in version 2026.2.26. A high-severity vulnerability called ClawJacked in OpenClaw allowed malicious websites to brute-force and take control of local AI agent instances. Oasis Security discovered the flaw, which enabled silent data theft. OpenClaw addressed the issue with version 2026.2.26, released […]