19103 results
 Pierluigi Paganini
 May 05, 2025
Kelly Benefits has determined that the impact of the recently disclosed data breach is much bigger than initially believed. Benefits and payroll solutions firm Kelly & Associates Insurance Group, aka Kelly Benefits, announced that the impact of a recently disclosed data breach is much bigger than initially estimated. The U.S.-based company provides benefits, payroll, and […]
 Pierluigi Paganini
April 18, 2025
ASUS warns of an authentication bypass vulnerability in routers with AiCloud enabled that could allow unauthorized execution of functions on the device. ASUS warns of an authentication bypass vulnerability, tracked as CVE-2025-2492 (CVSS v4 score: 9.2), which impacts routers with AiCloud enabled. A remote attacker can trigger the flaw to perform unauthorized execution of functions on the […]
 Pierluigi Paganini
March 13, 2025
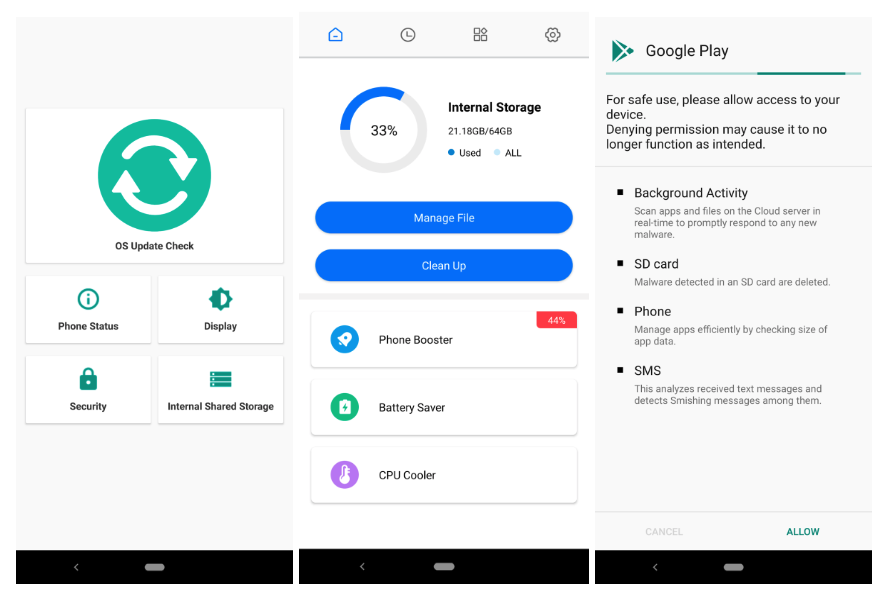
North Korea-linked APT group ScarCruft used a new Android spyware dubbed KoSpy to target Korean and English-speaking users. North Korea-linked threat actor ScarCruft (aka APT37, Reaper, and Group123) is behind a previously undetected Android surveillance tool named KoSpy that was used to target Korean and English-speaking users. ScarCruft has been active since at least 2012, it made the […]
Pierluigi Paganini
March 08, 2025
A data breach suffered by the Japanese telecom giant NTT exposed information of nearly 18,000 corporate customers. Japanese telecom giant NTT suffered a data breach that exposed information of nearly 18,000 corporate customers. On February 5th, the security team detected suspicious activity in its ‘Order Information Distribution System,’ and immediately restricted access to device A. […]
 Pierluigi Paganini
February 18, 2025
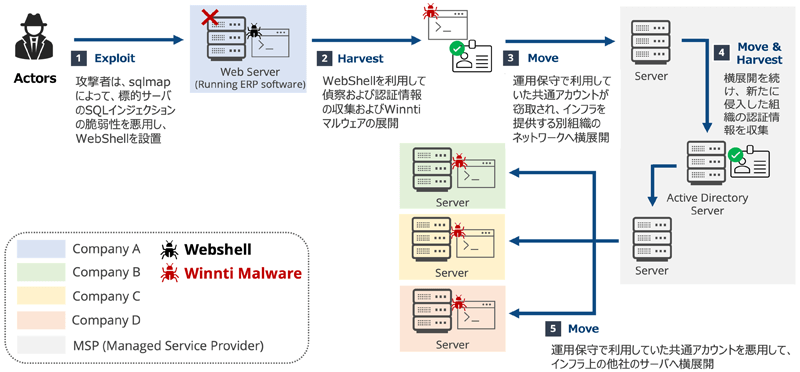
China-linked threat actor Winnti targeted Japanese companies in the manufacturing, materials, and energy sectors in March 2024 as part of a campaign dubbed RevivalStone. Researchers from cybersecurity firm LAC uncovered a new cyberespionage campaign, tracked as RevivalStone, carried out by the China-linked APT group Winnti in March 2024. Threat actors targeted Japanese companies in the manufacturing, […]
 Pierluigi Paganini
February 11, 2025
Fortinet warned of attacks using a now-patched zero-day vulnerability in FortiOS and FortiProxy to hijack Fortinet firewalls. Fortinet warned that threat actors are exploiting a new zero-day vulnerability, tracked as CVE-2025-24472 (CVSS score of 8.1), in FortiOS and FortiProxy to hijack Fortinet firewalls. The vulnerability is an authentication bypass issue that could allow a remote attacker […]
 Pierluigi Paganini
February 11, 2025
OpenSSL patched the vulnerability CVE-2024-12797, a high-severity flaw found by Apple that enables man-in-the-middle attacks. The OpenSSL Project addressed a high-severity vulnerability, tracked as CVE-2024-12797, in its secure communications library. The OpenSSL software library allows secure communications over computer networks against eavesdropping or need to identify the party at the other end. OpenSSL contains an open-source implementation […]
 Pierluigi Paganini
January 29, 2025
A critical flaw in Cacti open-source network monitoring and fault management framework that could allow remote code execution. Cacti is an open-source platform that provides a robust and extensible operational monitoring and fault management framework for users. A critical vulnerability, tracked as CVE-2025-22604 (CVSS score of 9.1), in the Cacti open-source framework could allow an authenticated […]
 Pierluigi Paganini
January 28, 2025
VMware fixed a high-risk blind SQL injection vulnerability in Avi Load Balancer, allowing attackers to exploit databases via crafted queries. VMware warns of a high-risk blind SQL injection vulnerability, tracked as CVE-2025-22217 (CVSS score of 8.6), in Avi Load Balancer, allowing attackers with network access to exploit databases via crafted queries. “VMware AVI Load Balancer […]
 Pierluigi Paganini
January 24, 2025
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds SonicWall SMA1000 vulnerability to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a SonicWall SMA1000 Appliance Management Console (AMC) and Central Management Console (CMC) vulnerability, tracked as CVE-2025-23006 to its Known Exploited Vulnerabilities (KEV) catalog. This week, SonicWall warned customers of a critical […]