19103 results
 Pierluigi Paganini
 January 02, 2025
Lumen reports that the Salt Typhoon hacking group, which targeted at least nine U.S. telecom firms, was locked out of its network. This week, a White House official confirmed that China-linked APT group Salt Typhoon has breached a ninth U.S. telecoms company as part of a cyberespionage campaign aimed at telco firms worldwide. China-linked APT group Salt Typhoon (also known as FamousSparrow and GhostEmperor) […]
 Pierluigi Paganini
December 31, 2024
Threat actors compromised at least 16 Chrome browser extensions leading to the exposure of data from over 600,000 users. A supply chain attack compromised 16 Chrome browser extensions, exposing over 600,000 users. Threat actors targeted the publishers of the extensions on the Chrome Web Store via phishing messages, then once obtained access to their account […]
 Pierluigi Paganini
December 25, 2024
Iran-linked APT group Charming Kitten has been observed using a new variant of the BellaCiao malware dubbed BellaCPP, Kaspersky researchers warn. The Iran-linked APT group Charming Kitten has been observed using a C++ variant of the BellaCiao malware, dubbed BellaCPP. BellaCiao, a .NET-based malware, combines webshell persistence with covert tunneling. The malicious code was first […]
 Pierluigi Paganini
December 17, 2024
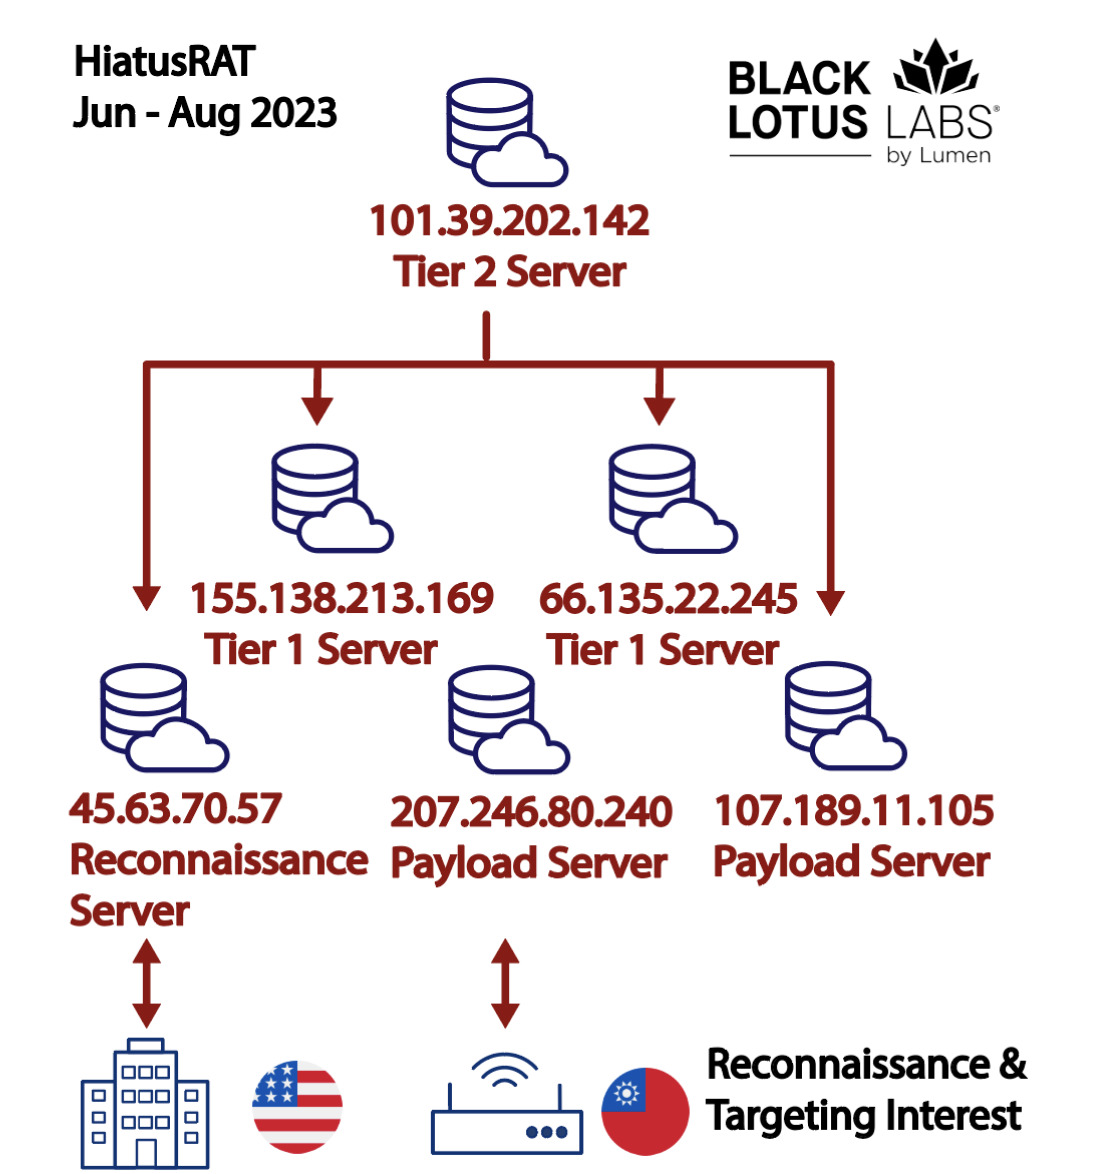
The FBI warned of a fresh wave of HiatusRAT malware attacks targeting internet-facing Chinese-branded web cameras and DVRs. The Federal Bureau of Investigation (FBI) released a Private Industry Notification (PIN) to warn of HiatusRAT malware campaigns targeting Chinese-branded web cameras and DVRs. The report includes a set of recommendations to mitigate the exposure to the […]
 Pierluigi Paganini
November 13, 2024
Microsoft Patch Tuesday security updates for November 2024 addressed 89 vulnerabilities, including two actively exploited zero-day flaws. Microsoft Patch Tuesday security updates for November 2024 fixed 89 vulnerabilities in Windows and Windows Components; Office and Office Components; Azure; .NET and Visual Studio; LightGBM; Exchange Server; SQL Server; TorchGeo; Hyper-V; and Windows VMSwitch. Four of these […]
 Pierluigi Paganini
October 14, 2024
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Fortinet products and Ivanti CSA bugs to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: Last week, Ivanti warned of three new security vulnerabilities (CVE-2024-9379, CVE-2024-9380, and CVE-2024-9381) in its Cloud Service Appliance (CSA) […]
 Pierluigi Paganini
October 13, 2024
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape. Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape. Over 300,000! GorillaBot: The New King of DDoS Attacks Hidden cryptocurrency mining and theft campaign affected over […]
 Pierluigi Paganini
October 10, 2024
Palo Alto fixed critical flaws in PAN-OS firewalls, warning that attackers could chain these vulnerabilities to hijack the devices. Palo Alto Networks addressed multiple vulnerabilities that an attacker can chain to hijack PAN-OS firewalls. The vulnerabilities reside in the Palo Alto Networks’ Expedition solution, which is a migration tool designed to help organizations move configurations […]
 Pierluigi Paganini
October 07, 2024
A critical vulnerability in the Apache Avro Java Software Development Kit (SDK) could be exploited to execute arbitrary code on vulnerable instances. A critical vulnerability, tracked as CVE-2024-47561, in the Apache Avro Java Software Development Kit (SDK) could allow the execution of arbitrary code on vulnerable instances. The flaw, tracked as CVE-2024-47561, impacts all versions of […]
 Pierluigi Paganini
October 04, 2024
Microsoft and the U.S. DoJ seized over 100 domains used by the Russia-linked Callisto Group for launching attacks on U.S. government and nonprofits. The Justice Department revealed the unsealing of a warrant to seize 41 domains used by Russia-linked Callisto Group (formerly SEABORGIUM, also known as COLDRIVER) for computer fraud in the United States. US […]