19102 results
 Pierluigi Paganini
 September 02, 2024
The Toronto District School Board (TDSB) confirmed that student information was compromised in the June Lockbit ransomware attack. The Toronto District School Board (TDSB) confirmed that students’ information was compromised following a ransomware attack that was discovered in June. The TDSB is the largest school board in Canada with 582 schools and about 235,000 students. In […]
 Pierluigi Paganini
September 02, 2024
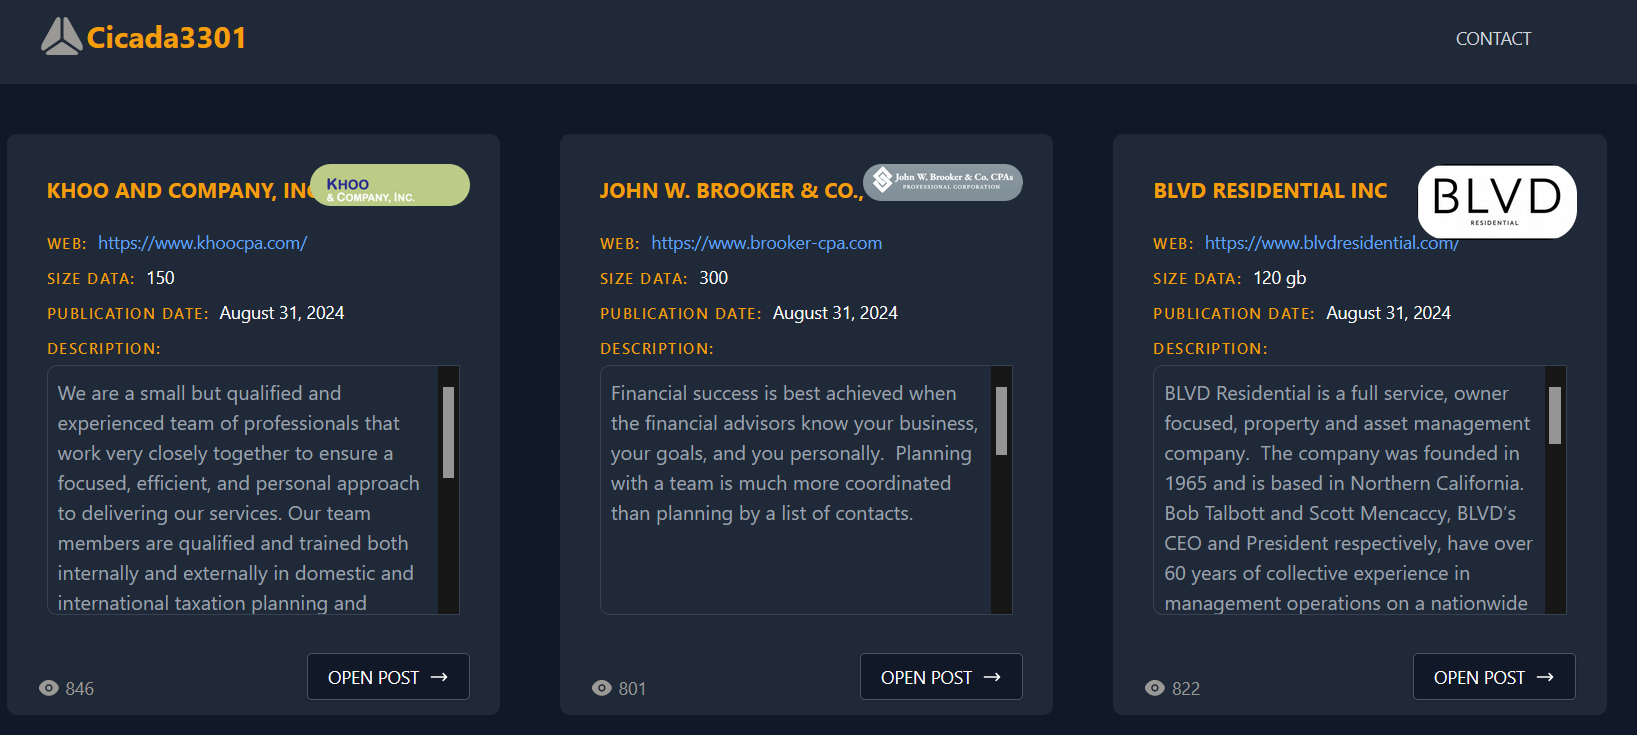
A new ransomware-as-a-service (RaaS) operation called Cicada3301 has emerged in the threat landscape and already targeted tens of companies. Cicada3301 is a new ransomware-as-a-service (RaaS) operation that appeared in the threat landscape. The group appears to be very active and already listed 23 victims on its extortion portal since mid-June. The following image shows the […]
 Pierluigi Paganini
August 09, 2024
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Apache OFBiz and Android kernel bugs to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added an Android Kernel Remote Code Execution flaw (CVE-2024-36971) and an Apache OFBiz Path Traversal issue (CVE-2024-32113) to its Known Exploited Vulnerabilities (KEV) catalog. Below are the descriptions of the […]
Pierluigi Paganini
July 21, 2024
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Adobe Commerce and Magento, SolarWinds Serv-U, and VMware vCenter Server bugs to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: Below are the descriptions of the flaws added to the KEV catalog: […]
 Pierluigi Paganini
July 17, 2024
A vulnerability in Cisco Smart Software Manager On-Prem (Cisco SSM On-Prem) license servers allows threat actors to change any user’s password. Cisco has addressed a critical vulnerability, tracked as CVE-2024-20419 (CVSS score of 10.0), in Cisco Smart Software Manager On-Prem (Cisco SSM On-Prem) license servers that allows attackers to change any user’s password. The issue […]
 Pierluigi Paganini
July 17, 2024
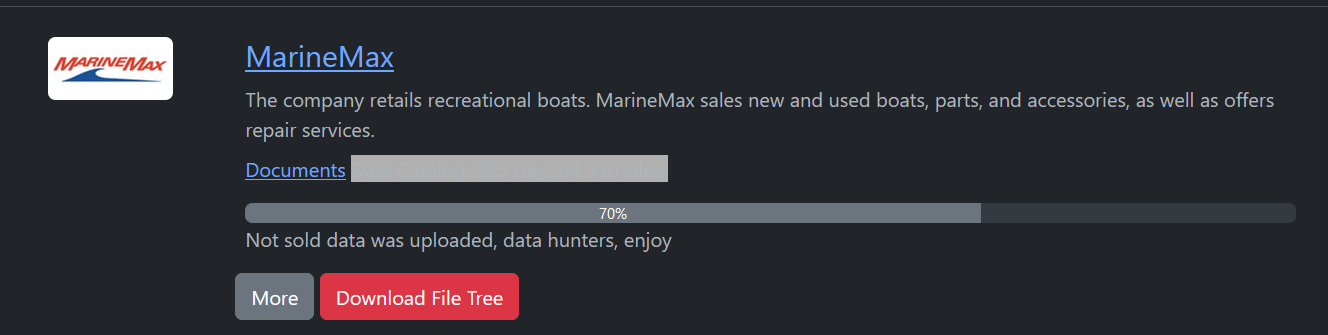
The world’s largest recreational boat and yacht retailer MarineMax, disclosed a data breach following a cyber attack. The world’s largest recreational boat and yacht retailer MarineMax disclosed a data breach that impacted over 123,000 individuals. In March, the company suffered a cyber attack, and the Rhysida ransomware gang claimed to have stolen company sensitive data. […]
 Pierluigi Paganini
July 12, 2024
Palo Alto Networks addressed five vulnerabilities impacting its products, including a critical authentication bypass issue. Palo Alto Networks released security updates to address five security flaws impacting its products, the most severe issue, tracked as CVE-2024-5910 (CVSS score: 9.3), is a missing authentication for a critical function in Palo Alto Networks Expedition that can lead to an admin […]
 Pierluigi Paganini
July 11, 2024
VMware addressed a critical SQL-Injection vulnerability, tracked as CVE-2024-22280, impacting Aria Automation. Virtualization giant VMware addressed a high-severity SQL-injection vulnerability, tracked as CVE-2024-22280 (CVSSv3 base score of 8.5), in its Aria Automation solution. VMware Aria Automation (formerly vRealize Automation) is a modern cloud automation platform that simplifies and streamlines the deployment, management, and governance of cloud infrastructure […]
 Pierluigi Paganini
July 09, 2024
The Lockbit ransomware attack on Evolve Bank has compromised the personal information of over 7.6 million individuals. At the end of June, the LockBit gang announced that it had breached the systems of the Federal Reserve of the United States and exfiltrated 33 TB of sensitive data, including “Americans’ banking secrets.” Despite the announcement, data leaked data […]
Pierluigi Paganini
July 08, 2024
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Cisco NX-OS Command Injection bug to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Cisco NX-OS Command Injection Vulnerability, tracked as CVE-2024-20399, to its Known Exploited Vulnerabilities (KEV) catalog. This week, Cisco addressed an NX-OS zero-day, tracked as CVE-2024-20399 (CVSS score […]