19323 results
 Pierluigi Paganini
 January 31, 2015
PHP applications and WordPress CMS might be affected by the GHOST vulnerability that could be exploit to compromise the hosting servers. The critical GHOST vulnerability (CVE-2015-0235) in the GNU C library (glibc) may have a greater impact than imagined, security experts have discovered that PHP applications, including the popular WordPress Content Management System (CMS), could also […]
 Pierluigi Paganini
January 30, 2015
Security researcher is investigating in a new strain of Facebook Trojan that in just two days has already infected 1110,000 Facebook users. Social networks represent a privileged attack vector for malware-based attacks, a recent investigation conducted by by the security researcher Mohammad Faghani revealed the existence of a Trojan is circulating among Facebook users. According to the researcher, […]
 Pierluigi Paganini
January 30, 2015
The Reddit social news website issued its first transparency report shows it complied with only 32 user info requests in 2014. Reddit, the popular social news website has released its first Reddit transparency report that details data related the requests for user information and requests for content removal the company received in 2014. It is not […]
 Pierluigi Paganini
January 30, 2015
Mozilla products including the Firefox browser will stop trusting SSL certificates that were issued using old root CA certificates with 1024-bit RSA keys. Mozilla products including the popular Firefox browser will stop trusting SSL certificates that were issued using old root CA certificates with 1024-bit RSA keys. With this decision Mozilla wants to stress certificate authorities (CAs) […]
 Pierluigi Paganini
January 30, 2015
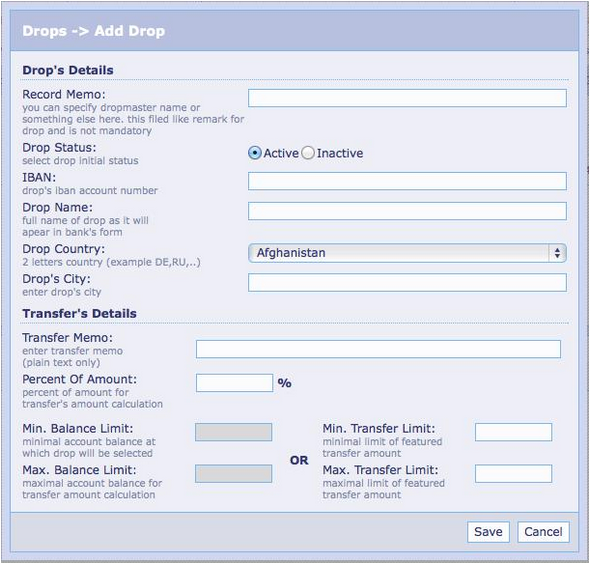
Researchers at SentinelOne have discovered a strain of the Zeus malware that includes a very sophisticated control panel and evasion techniques. Malware researchers at SentinelOne have spotted a new Zeus variant that was used to target major Canadian banks, including the National Bank of Canada, the Bank of Montreal and the Royal Bank of Canada. […]
 Pierluigi Paganini
January 30, 2015
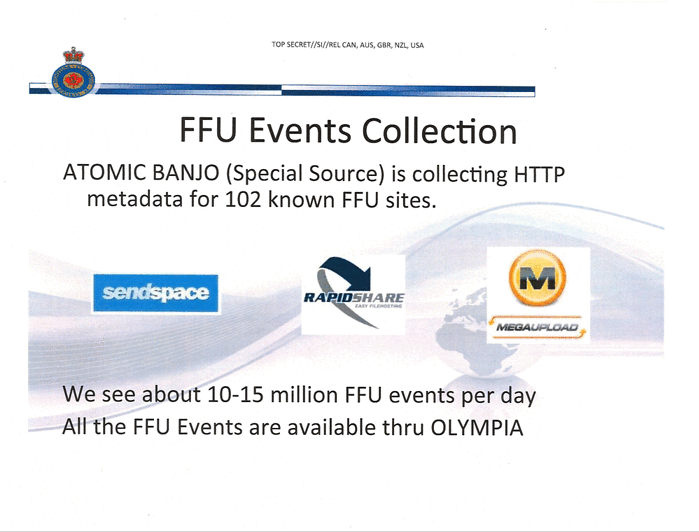
New documents leaked by Edward Snowden revealed the monitoring activities run by the Canadian Intelligence agency, the Communications Security Establishment Edward Snowden seems to be a bottomless pit, month after month his revelations are shocking the IT security community. Surveillance, hacking, cyber espionage, these are the main activities carried out by the NSA and its […]
 Pierluigi Paganini
January 29, 2015
The 17-year-old security researcher Indrajeet Bhuyan discovered two security flaws in the newborn WhatsApp Web client which menace user privacy. Just a week after the presentation of WhatsApp Web, the desktop version of the popular mobile messaging application WhatsApp, a 17-year-old security researcher Indrajeet Bhuyan discovered two security flaws. Bhuyan is already known to the IT security community because […]
 Pierluigi Paganini
January 29, 2015
Critical DNS hijacking flaw affects D-Link DSL router, the flaw affects the ZynOS firmware that is used also by other vendors, including TP-Link and ZTE. A security vulnerability affects DSL router model from D-Link, the flaw could be exploited by a remote attacker to change device DNS settings and hijack users’ traffic. The Bulgarian security […]
 Pierluigi Paganini
January 29, 2015
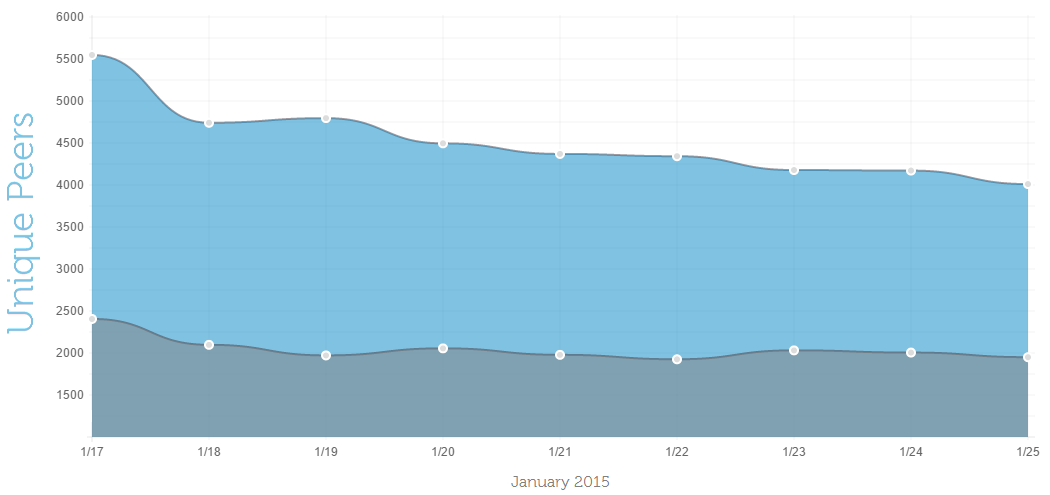
The Dell SecureWorks Counter Threat Unit (CTU) research team observed the ZeroAccess botnet resumes again with click-fraud activity. Law enforcement has destroyed the ZeroAccess botnet, also known as Sirefef, in December 2013 by a joint effort of Microsoft Digital Crimes Unit, FBI, Europol and industry partners. The ZeroAccess botnet is considered one of most insidious malicious […]
 Pierluigi Paganini
January 29, 2015
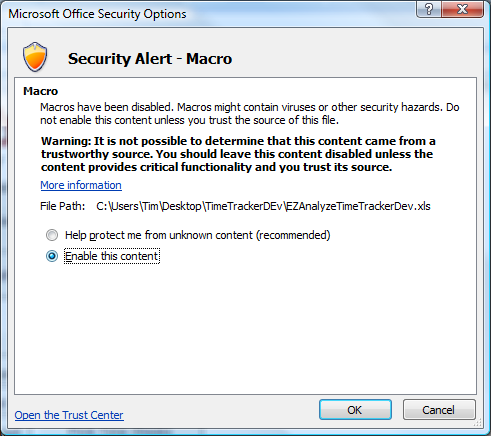
Experts at Bitdefender have discovered a spam campaign that tricks antispam filters by relying on macros in Empty Word Documents. Security experts at BitDefender observed a new tactic adopted by spammers that rely on emails with an empty Word document in the attachment to bypass anti-spam filters. The social engineering strategy adopted by spammers to lure victims into […]