 Pierluigi Paganini
 July 01, 2026
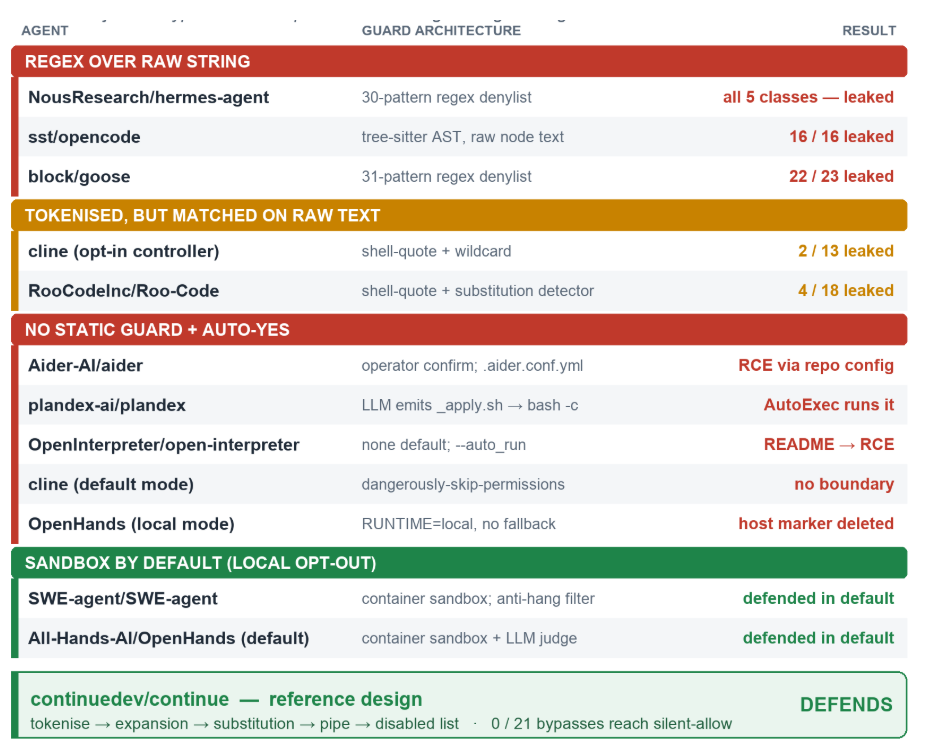
Researchers found a shell injection flaw in 10 of 11 popular open-source AI agents, allowing attackers to bypass command filters. Adversa AI just published a survey, titled “GuardFall: a universal shell injection vulnerability in open-source AI agents,” of eleven open-source AI coding and computer-use agents, and the headline finding is uncomfortable: ten of them leave […]
 Pierluigi Paganini
June 30, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds a SimpleHelp flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a SimpleHelp flaw, tracked as CVE-2026-48558 (CVSS score v3.1 of 10.0), to its Known Exploited Vulnerabilities (KEV) catalog. CVE-2026-48558 is a critical authentication bypass vulnerability in SimpleHelp versions 5.5.15 and earlier and […]
 Pierluigi Paganini
June 24, 2026
Frontier AI could drive a 10x surge in vulnerabilities. CTEM helps organizations continuously identify, prioritize, and reduce real cyber risk. Your vulnerability management program was not designed for what is coming next. More than 40,000 CVEs were reported in 2025, breaking yet another record. Today, security experts anticipate that frontier AI-powered systems could drive a […]
 Pierluigi Paganini
June 23, 2026
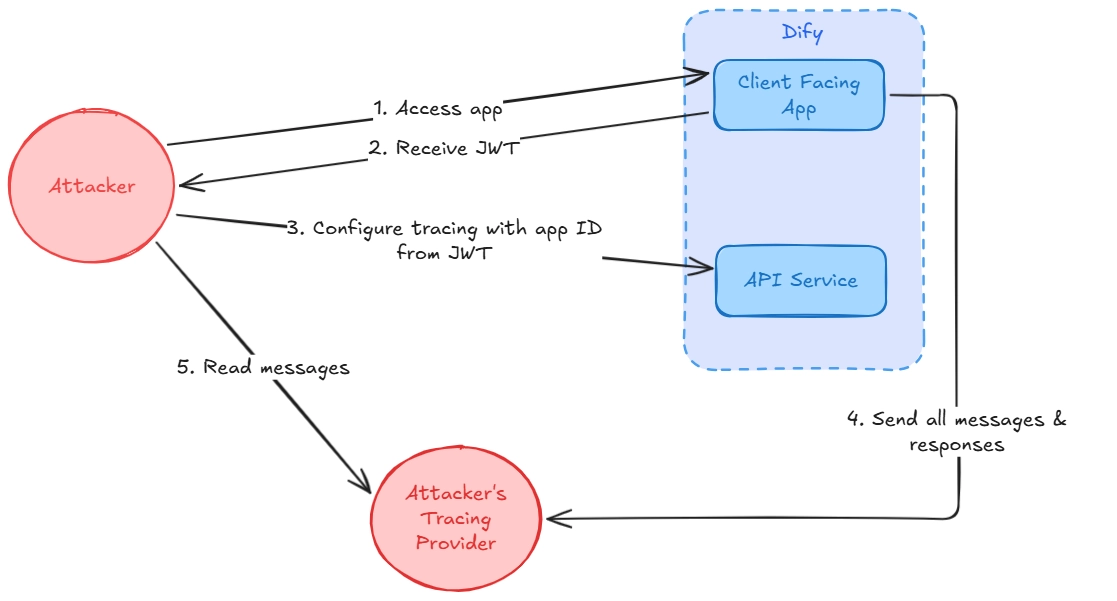
Four flaws in Dify exposed cross-tenant data, documents and AI conversations. Two critical bugs enabled unauthenticated access and data theft. Zafran Labs researchers disclosed four vulnerabilities in Dify, the open-source AI platform used by major companies like Volvo and Maersk to run over a million applications across over 60 industries. Two vulnerabilities are of critical […]
 Pierluigi Paganini
June 17, 2026
FulcrumSec leaked data stolen from Novo Nordisk, claiming to have exfiltrated 1.3TB, including clinical records and AI research assets. On June 15, 2026, a data-theft extortion group calling itself FulcrumSec began leaking files from Novo Nordisk, the Danish maker of Ozempic and Wegovy, after the company refused a $25 million ransom demand. The attackers claimed […]
 Pierluigi Paganini
June 10, 2026
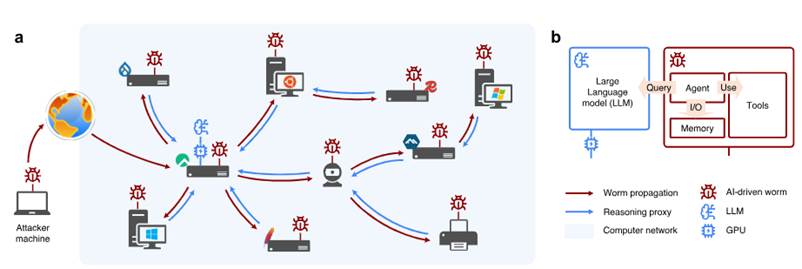
A study by the University of Toronto shows how artificial intelligence can power autonomous worms capable of tailoring attacks against Windows, Linux and IoT devices. A group of researchers from the University of Toronto has demonstrated how open-source artificial intelligence models can be used to create a new category of computer worms capable of autonomously […]
 Pierluigi Paganini
June 02, 2026
Attackers exploited Meta’s AI support chatbot to reset Instagram passwords and hijack accounts without accessing victims’ email inboxes. Attackers abused Meta’s AI-powered support chatbot to reset Instagram passwords and hijack accounts without accessing victims’ email inboxes. The issue affected several users, including high-profile accounts, before Instagram fixed the flaw. Security researcher Jane Wong and other […]
 Pierluigi Paganini
May 29, 2026
GREYVIBE, a Russia-linked group active since 2025, targets Ukraine with AI-assisted malware and five attack chains. Researchers say it’s part spy op, part crime gang. Security firm WithSecure has been tracking a previously unknown Russian-linked APT group called GREYVIBE since at least August 2025. The group targets Ukraine and Ukrainian-related organizations across military, government, civilian, […]
 Pierluigi Paganini
May 11, 2026
Google says hackers now use AI to create exploits, automate attacks, evade defenses, and target AI supply chains at scale. Artificial intelligence is rapidly changing the cyber threat landscape, and a new report from the Google Cloud Threat Intelligence team highlights how attackers already use AI to improve vulnerability exploitation and gain initial access to […]
 Pierluigi Paganini
May 09, 2026
Braintrust warned customers to rotate API keys after hackers breached an AWS account, exposing secrets tied to cloud-based AI models. AI observability startup Braintrust warned customers to rotate API keys after attackers gained unauthorized access to one of the company’s AWS accounts, potentially exposing secrets used to connect to cloud-based AI models. The company said […]