 Pierluigi Paganini
 August 19, 2018
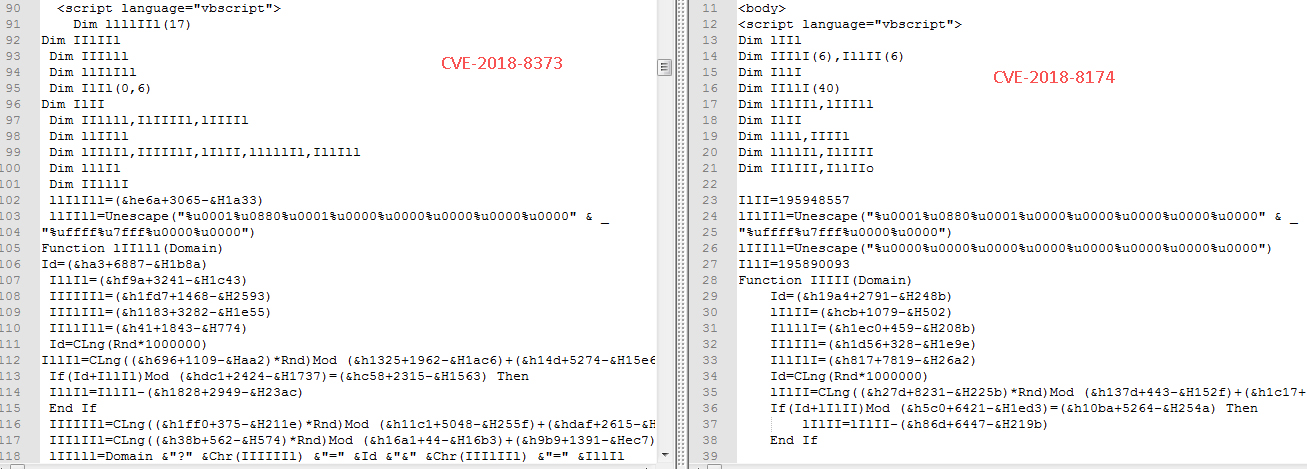
The North Korea-linked Dark Hotel APT group is leveraging the recently patched CVE-2018-8373 vulnerability in the VBScript engine in attacks in the wild. The vulnerability affects Internet Explorer 9, 10 and 11, it was first disclosed last month by Trend Micro and affected all supported versions of Windows. The flaw could be exploited by remote attackers […]
 Pierluigi Paganini
August 02, 2018
According to Dragos firm, the RASPITE cyber-espionage group (aka Leafminer) has been targeting organizations in the United States, Europe, Middle East, and East Asia. Researchers from security firm Dragos reported that a group operating out of Iran tracked as RASPITE has been targeting entities in the United States, Europe, Middle East, and East Asia, industrial cybersecurity firm Dragos warns. The group […]
 Pierluigi Paganini
July 24, 2018
The US Government is warning of continuous intrusions in National critical infrastructure and it is blaming the Kremlin for the cyber attacks. According to the US Department of Homeland Security, Russia’s APT groups have already penetrated America’s critical infrastructure, especially power utilities, and are still targeting them. These attacks could have dramatic consequence, an attack against […]
 Pierluigi Paganini
July 10, 2018
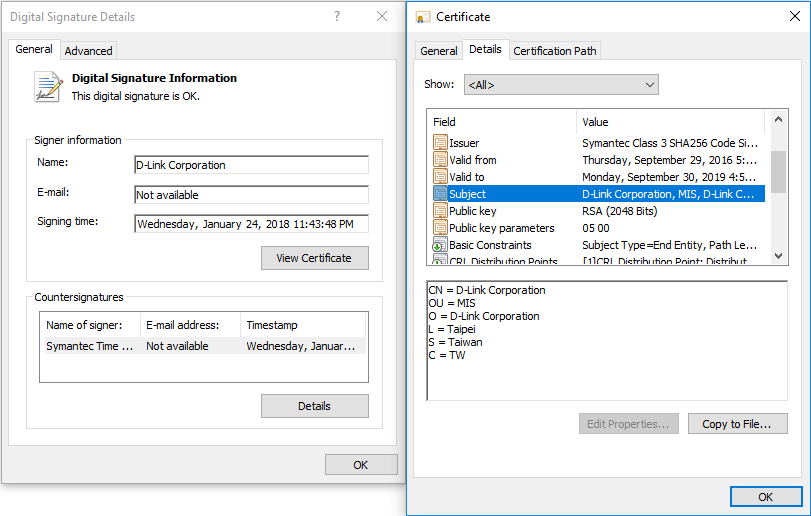
A cyber-espionage group tracked as BlackTech is abusing code-signing certificates stolen from D-Link for the distribution of their malware. Security experts from ESET discovered that an APT group tracked as BlackTech is using code-signing certificates stolen from Taiwanese-based tech firm D-Link and the security company Changing Information Technology Inc. According to the experts, the cyber espionage group […]
 Pierluigi Paganini
July 03, 2018
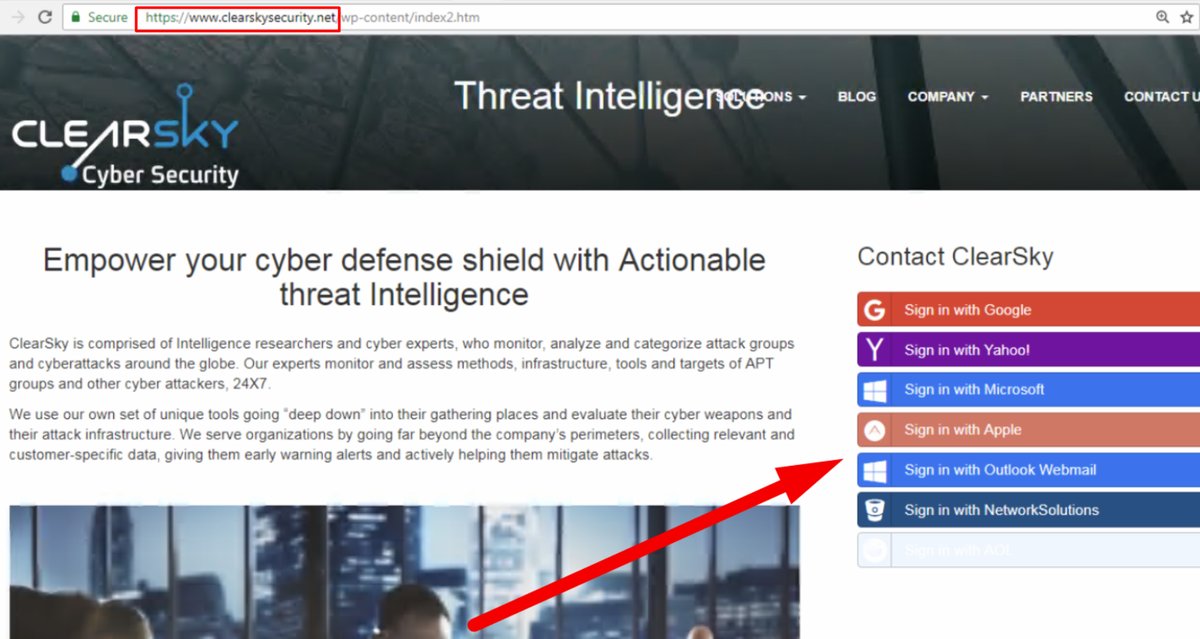
Iranian APT groups continue to very active, recently Charming Kitten cyber spies attempted to pose as an Israeli cyber-security firm that uncovered previous hacking campaigns. The Iranian Charming Kitten ATP group, aka Newscaster or Newsbeef, launched spear phishing attacks against people interested in reading reports about it. The Newscaster group made the headlines in 2014 when experts at iSight issued a report describing the […]
 Pierluigi Paganini
June 27, 2018
Security researchers at Palo Alto Networks have uncovered a new cyber espionage group tracked as RANCOR that has been targeting entities in South East Asia. According to the experts, the RANCOR APT group has been targeting political entities in Singapore, Cambodia, and Thailand, and likely in other countries, using two previously unknown strain of malware. The two […]
 Pierluigi Paganini
June 18, 2018
The US DHS and the FBI have published a new joint report that includes technical details of a piece of malware allegedly used by the Hidden Cobra APT. A new joint report published by US DHS and FBI made the headlines, past document details TTPs associated with North Korea-linked threat groups, tracked by the US government as […]
 Pierluigi Paganini
June 15, 2018
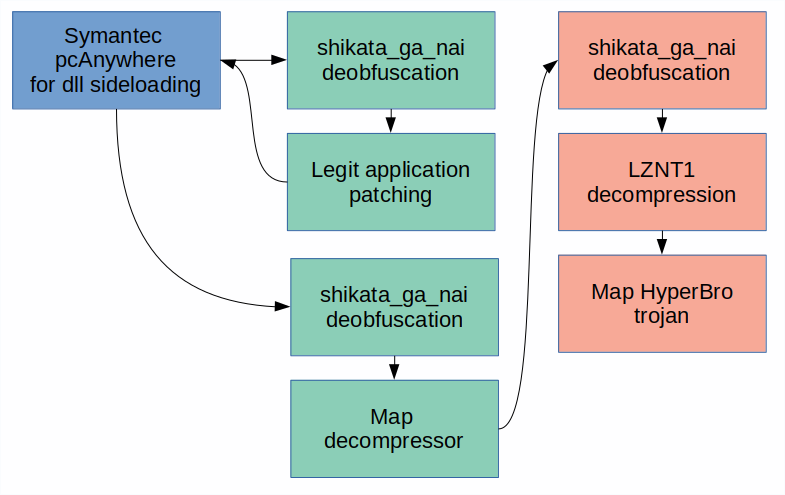
Trend Micro spotted a new attack relying on weaponized Word documents and PowerShell scripts that appears related to the MuddyWater APT. Security experts at Trend Micro have spotted a new attack relying on weaponized Word documents and PowerShell scripts that appears related to the MuddyWater cyber-espionage campaign. The first MuddyWater campaign was observed in late 2017, then researchers from […]
 Pierluigi Paganini
June 14, 2018
A China-linked APT group, LuckyMouse, Emissary Panda, APT27 and Threat Group 3390, has targeted a national data center in Central Asia. The APT group has been active since at least 2010, the crew targeted U.S. defense contractors and financial services firms worldwide. In March 2018, security experts at Kaspersky Lab have observed an attack powered by the […]
Pierluigi Paganini
June 12, 2018
North Korea-linked Lazarus APT group planted an ActiveX zero-day exploit on the website of a South Korean think tank focused on national security. According to researchers at AlienVault, North Korea-linked hackers planted an ActiveX zero-day vulnerability on the website of a South Korean think tank focused on national security. The experts attributed the attack to the notorious Lazarus APT group […]
Security / November 02, 2026