 Pierluigi Paganini
 January 19, 2018
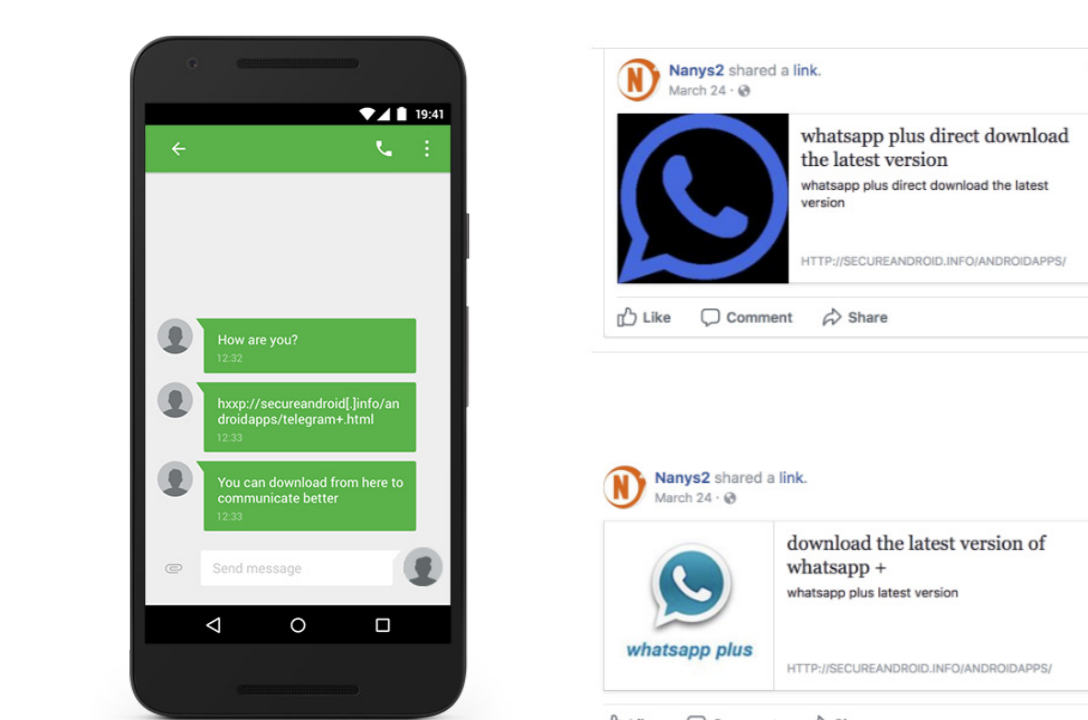
A new long-running player emerged in the cyber arena, it is the Dark Caracal APT, a hacking crew associated with to the Lebanese General Directorate of General Security that already conducted many stealth hacking campaigns. Cyber spies belonging to Lebanese General Directorate of General Security are behind a number of stealth hacking campaigns that in […]
 Pierluigi Paganini
December 16, 2017
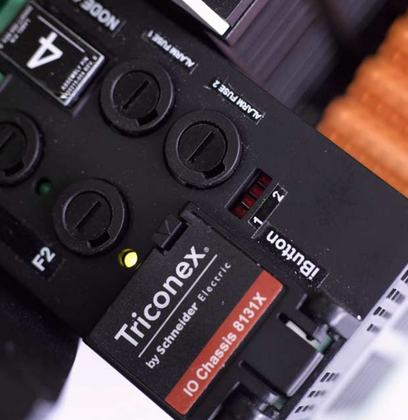
CyberX who analyzed samples of the Triton malware believes it was likely developed by Iran and used to target an organization in Saudi Arabia. Security experts from security firms FireEye and Dragos reported this week the discovery of a new strain of malware dubbed Triton (aka Trisis) specifically designed to target industrial control systems (ICS). Both FireEye and Dragos […]
 Pierluigi Paganini
December 14, 2017
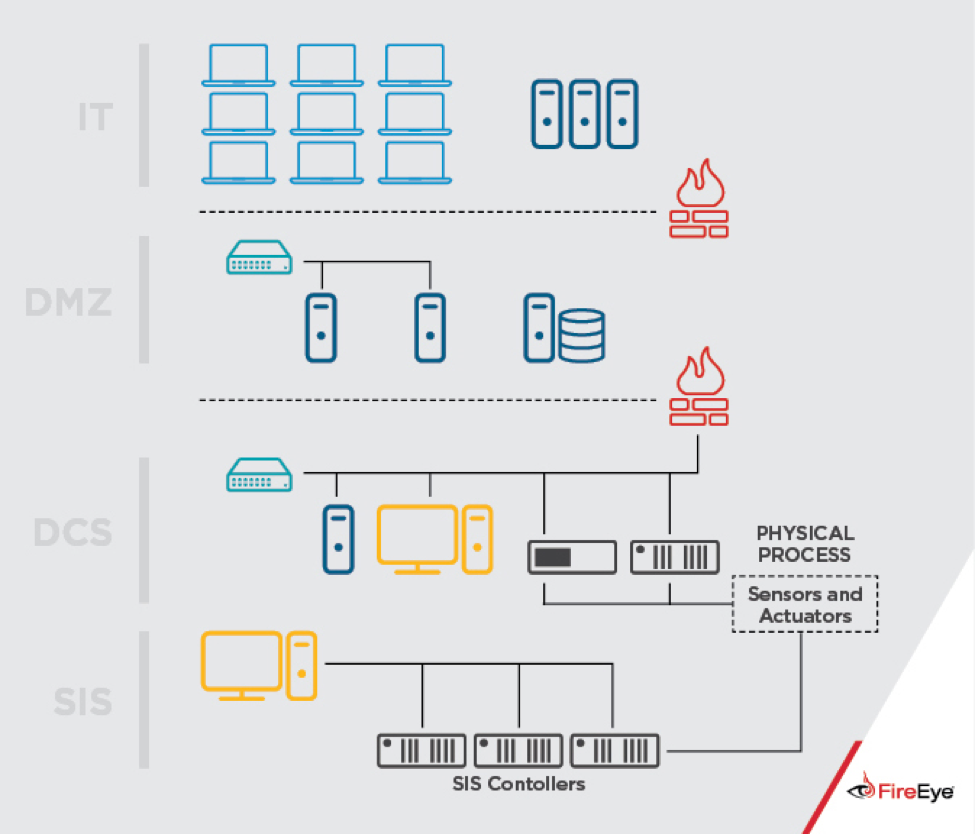
Triton malware – A new strain of malware specifically designed to target industrial control systems (ICS) system has been spotted by researchers at FireEye A new strain of malware dubbed Triton specifically designed to target industrial control systems (ICS) has been spotted by researchers at FireEye. The Triton malware has been used in attacks aimed at an unnamed critical […]
 Pierluigi Paganini
November 17, 2017
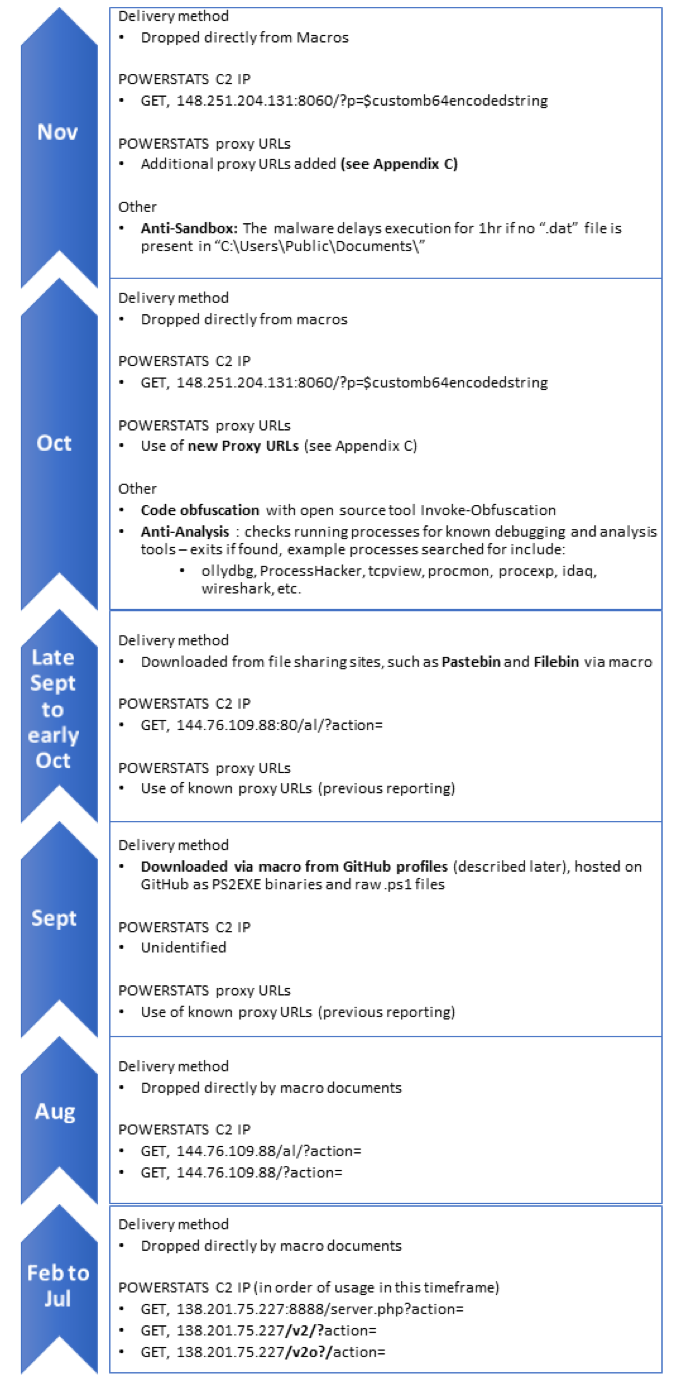
Researchers are investigating a mysterious wave of attacks in the Middle East that was dubbed MuddyWater due to the confusion in attributing the. Security experts at Palo Alto Networks are monitoring long-lasting targeted attacks aimed at entities in the Middle East and that are difficult to attribute. The experts called the campaign ‘MuddyWater’ due to the […]
 Pierluigi Paganini
November 15, 2017
US DHS published the details of the malware FALLCHILL and Volgmer used by the APT group Hidden Cobra that is linked to the North Korean government. The US Department of Homeland Security (DHS) published the details of the hacking tool FALLCHILL used one of the APT group linked to the North Korean government tracked as Hidden Cobra (aka Lazarus Group). […]
 Pierluigi Paganini
November 07, 2017
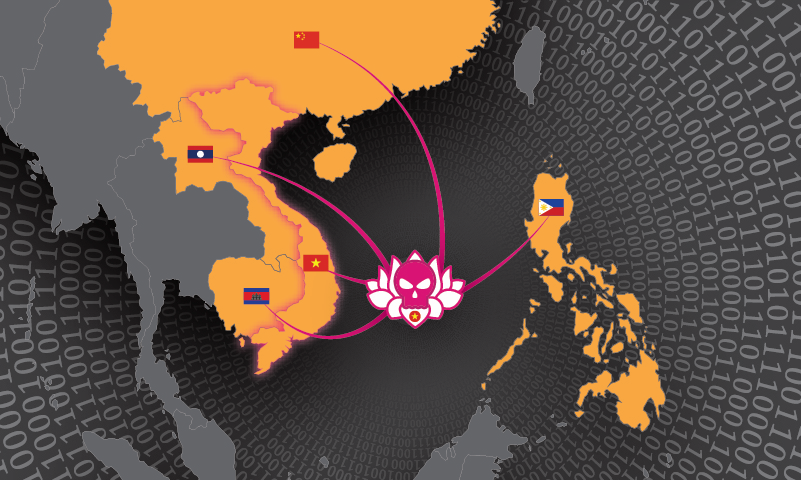
According to the incident response firm Volexity, Vietnamese APT32 group is today one of the most advanced APTs in the threat landscape According to the incident response firm Volexity, the cyber espionage campaigns associated with a group operating out of Vietnam and tracked as tracked as OceanLotus and APT32 have become increasingly sophisticated. Researchers at Volexity has been tracking the threat actor since […]
 Pierluigi Paganini
October 10, 2017
The financially-motivated FIN7 APT group (also known as Carbanak or Anunak) recently changed attack technique again to evade detection. The financially-motivated FIN7 APT group (also known as Carbanak or Anunak) recently changed attack technique again and has been implementing a new malware obfuscation method. The group that has been active since late 2015, it was highly active since the beginning of 2017. Fin7 was spotted early […]
 Pierluigi Paganini
October 01, 2017
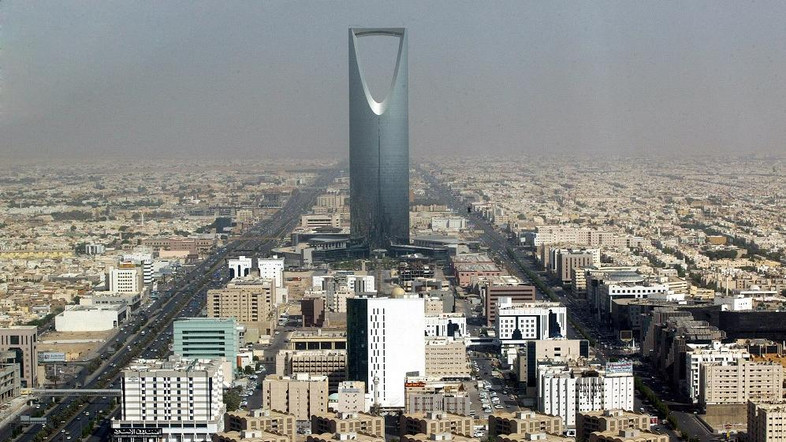
According to Kaspersky Lab, sixty percent of institutions in Saudi Arabia have experienced malware-based attacks over the past 12 months. Malware continues to be one of the most dangerous threats for organizations worldwide, and data recently disclosed by security firms. According to Kaspersky Lab, Saudi Arabia is under a constant malware-based attack, the experts reported that […]
 Pierluigi Paganini
September 26, 2017
Evidence that Russian hackers attempted to interfere with the 2016 US Election continues to pile up, DHS notified states whose systems were hit by APTs. Evidence that Russia attempted to interfere with the 2016 US Election continues to pile up. Rumours started almost as soon as the 2016 US Election was completed, individuals with the White House have […]
 Pierluigi Paganini
September 22, 2017
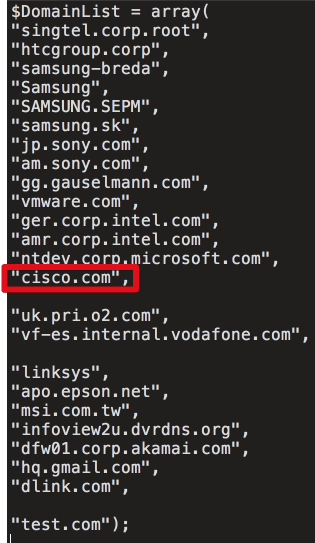
The threat actor that recently compromised the supply chain of the CCleaner software targeted at least 20 tech firms with a second-stage malware. The threat actor that recently compromised the supply chain of the CCleaner software to distribute a tainted version of the popular software targeted at least 20 major international technology firms with a […]
Security / November 02, 2026