 Pierluigi Paganini
 January 06, 2017
Forcepoint has detected two new versions of an advanced persistent threat (APT) malware dubbed MM Core APT and first discovered in 2013. The APT MM Core malware has been in the wild since April 2013 when it was spotted for the first time by experts at FireEye. The malware researchers dubbed the first release of the […]
 Pierluigi Paganini
December 22, 2016
The Russian APT group Fancy Bear used a malware implant on Android devices to track and target Ukrainian artillery units from late 2014 through 2016. The popular hacking group, known as Fancy Bear, APT 28, Pawn Storm, Sednit or Sofacy, is once again in the headlines. Experts from the cyber security firm CrowdStrike reported the alleged Russian nation-state actor used malware implant […]
 Pierluigi Paganini
December 16, 2016
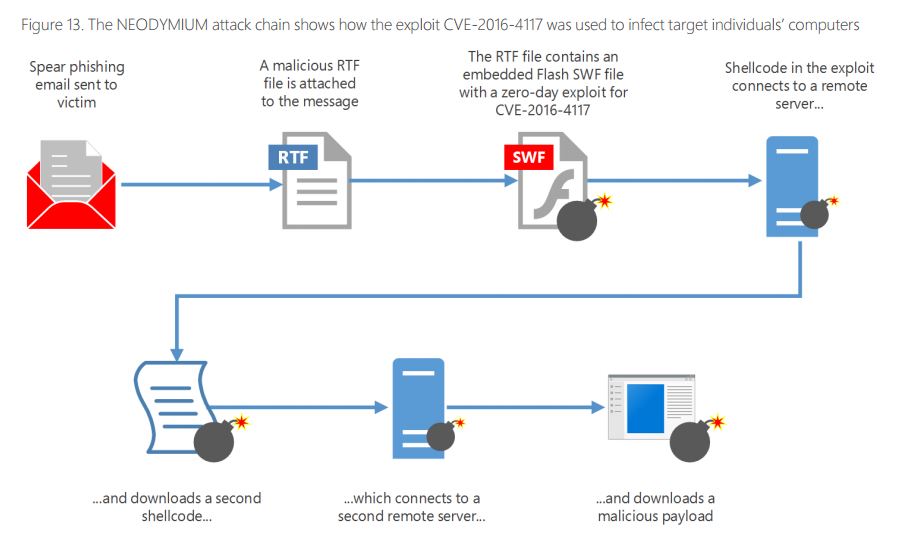
Microsoft discovered two distinct APT groups, PROMETHIUM and NEODYMIUM, that exploited the same Flash Player zero-day flaw on same targets. Security researchers have discovered two distinct APT groups, PROMETHIUM and NEODYMIUM, that exploited the same Flash Player zero-day vulnerability (CVE-2016-4117) in cyber espionage campaigns on Turkish citizens living in Turkey and various other European countries. Both […]
 Pierluigi Paganini
December 15, 2016
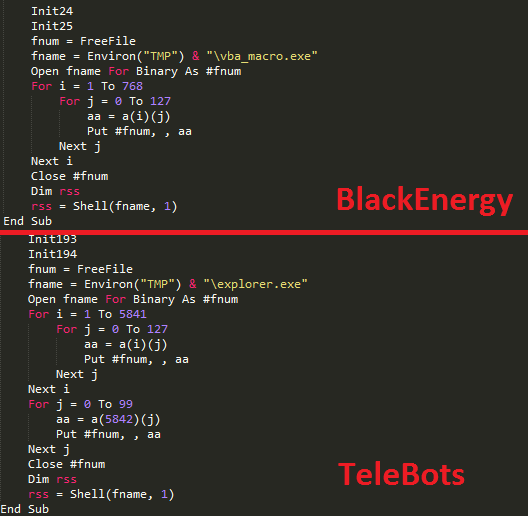
The BlackEnergy hacker group that targeted the Ukrainian grid one year ago, now identified as TeleBots, are targeting Ukrainian banks. The BlackEnergy hacker group that targeted the Ukrainian grid one year ago causing a power outage in the country are now targeting Ukrainian banks. The Ukrainian government accused Russia of being involved in the attack, […]
 Pierluigi Paganini
October 20, 2016
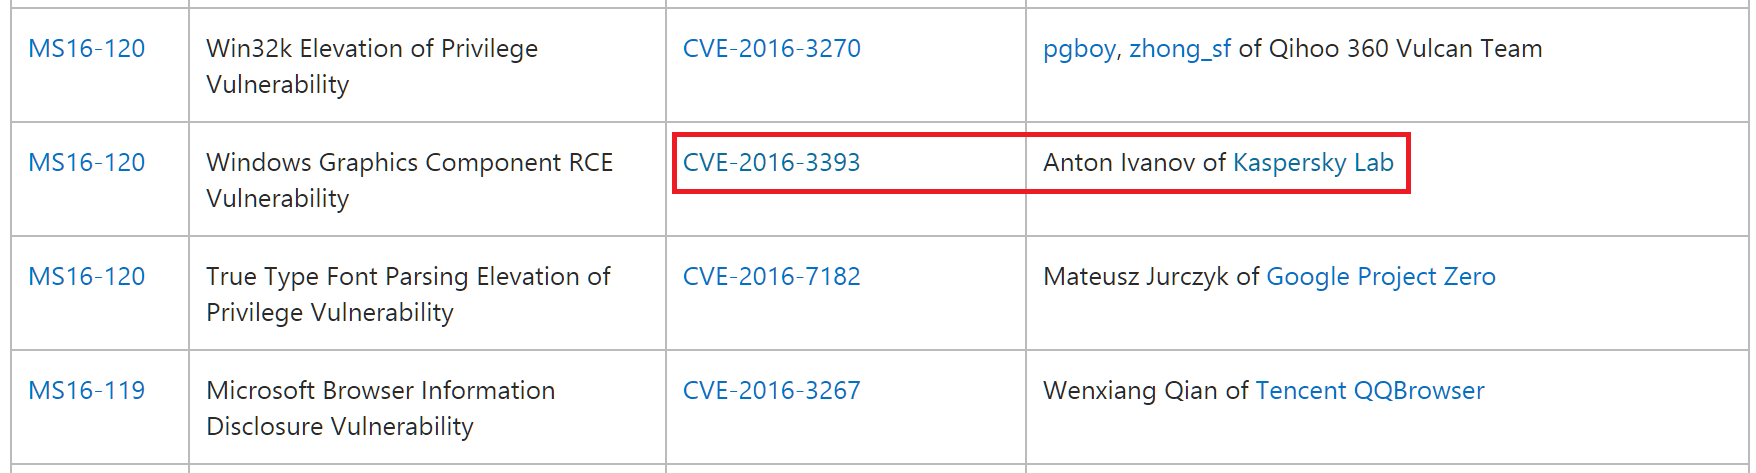
Experts from Kaspersky have discovered a new APT dubbed FruityArmor APT using a zero-day vulnerability patched this month by Microsoft. A new APT group, dubbed FruityArmor, targeted activists, researchers, and individuals related to government organizations. According to experts at Kaspersky Lab, the FruityArmor APT conducted targeted attacks leveraging on a Windows zero-day vulnerability, tracked as CVE-2016-3393, recently […]
 Pierluigi Paganini
October 19, 2016
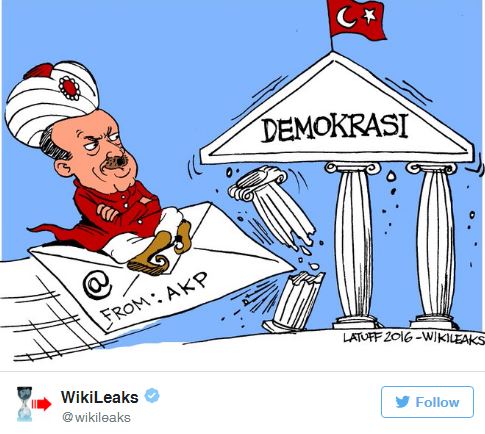
Experts at ElevenPaths, a Telefonica’s cyber security unit, provided further details on political cyberattacks leveraging on advanced malicious codes. On 19 July at 11pm Ankara time, Wikileaks published the first emails that were grabbed from the Turkish AKP. The organization led by Julian Assange, being in line with its policy on publication of secret information, […]
 Pierluigi Paganini
August 22, 2016
The US Department of Energy (DOE) has awarded $34 million in funding to projects aimed at the protection of power grid from cyber attacks. A cyber attack against a critical infrastructure is an event that government doesn’t exclude, for this reason, one of the pillars of their cyber strategy is the adoption of countermeasures to improve their […]
 Pierluigi Paganini
August 08, 2016
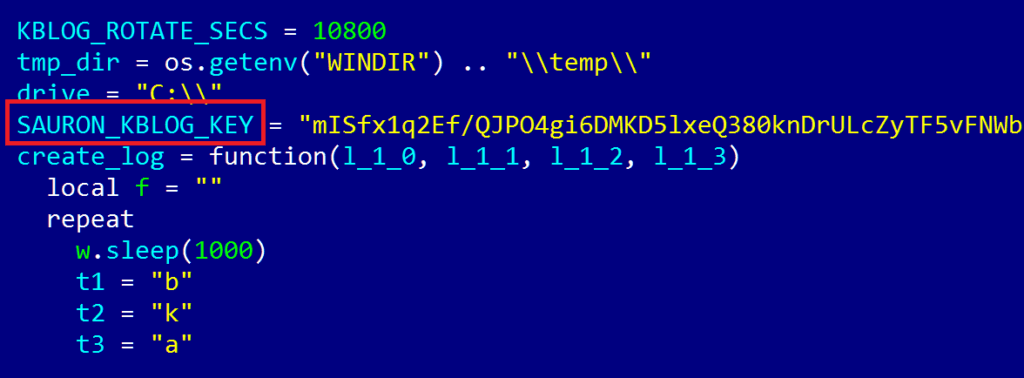
Experts spotted a previously unknown APT group dubbed Strider or ProjectSauron that carried out surgical cyber-espionage attacks against targets worldwide. A previously unknown hacking group variously dubbed ‘Strider’ or ‘ProjectSauron’ has been conducting a surgical cyber espionage campaign against targets in Russia, Belgium, China, Iran, Sweden, and Rwanda. According to experts from Symantec, the Strider crew […]
 Pierluigi Paganini
July 09, 2016
Security experts from ProofPoint have spotted a new campaign operated by the APT Group NetTraveler that is targeting Russian and European organizations. NetTraveler is an ATP group first spotted by Kaspersky in 2013, when researchers discovered an espionage activity against over 350 high profile victims from 40 countries. The name of the operation derives from the malicious […]
 Pierluigi Paganini
June 19, 2016
Adobe Flash Player 22.0.0.192 release fixes the Flash Player zero-day vulnerability (CVE-2016-4171) exploited by the APT group dubbed ScarCruft. Adobe has issued the Flash Player 22.0.0.192, a release that fixes the Flash Player zero-day vulnerability (CVE-2016-4171) exploited by the APT group dubbed ScarCruft in attacks on high-profile targets. The Flash Player flaw CVE-2016-4171 affects versions 21.0.0.242 and earlier for […]
Malware / November 02, 2026
Security / November 02, 2026