 Pierluigi Paganini
 January 17, 2016
A study conducted by TripWire over the past year revealed successful cyber attacks on the energy industry increased as never before. US oil and gas companies are under attack, over 80% of them have reported a significant increase in the number of cyber attacks. According to Tripwire, over the past year successful cyber attacks have increased […]
 Pierluigi Paganini
January 08, 2016
The Russian Sandworm APT group if the first suspect for the Ukrainian power outage, states experts at eiSight Partners. According to a report published by experts at eiSight Partners the cyber attack against a Ukraine power station has been managed by a Russian group called Sandworm. A few days ago experts at ESET reported the existence of a […]
 Pierluigi Paganini
December 06, 2015
According to a new report published by the Kaspersky Lab, the Sofacy APT has recently increased its activities. According to a new report published by the Kaspersky Lab, the Advanced persistent threat group Sofacy (also known as APT28 , Fancy Bear, Sednit, and STRONTIUM) has increased its activity. The Sofacy group has been active since 2008, targeting mostly military […]
 Pierluigi Paganini
November 10, 2015
Experts from Check Point firm published a new report on the Rocket Kitten APT that include more insight into the activities of the group. Do you remember the Rocket Kitten ATP? The Rocket Kitten group has been suspected to be active since 2011 and have been increasing their activity since 2014. The main targets are based in the Middle […]
 Pierluigi Paganini
October 23, 2015
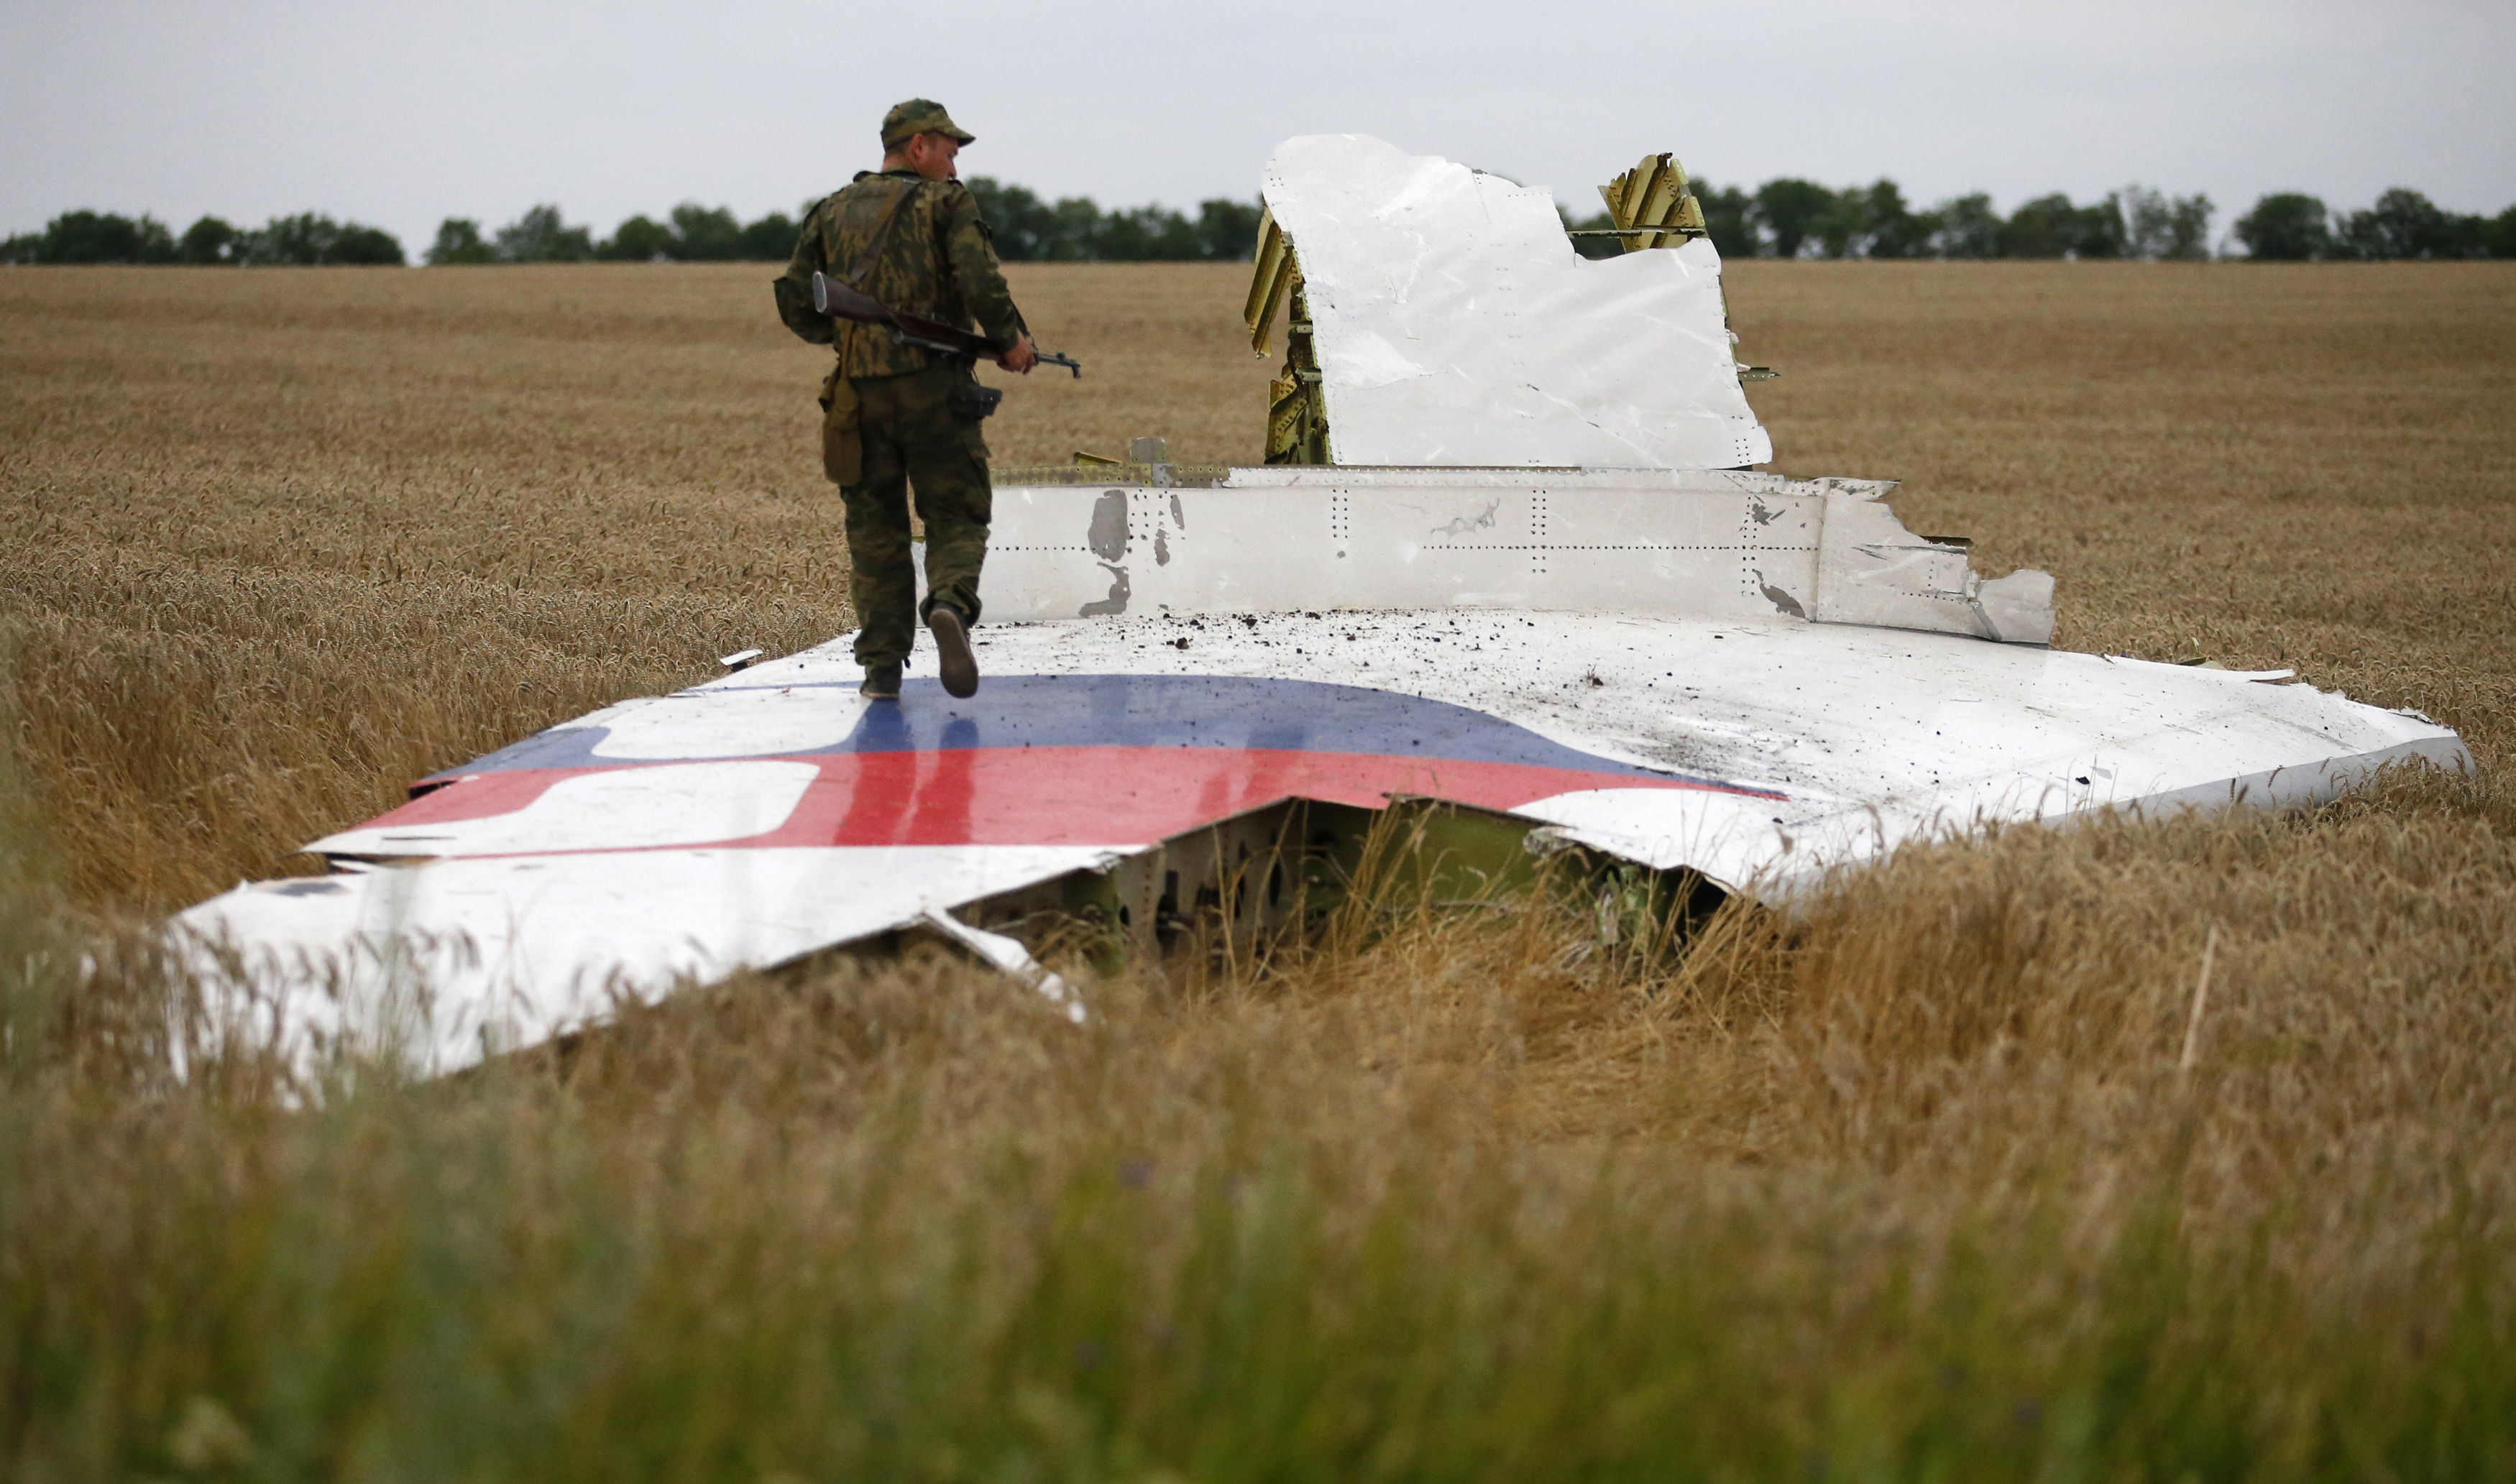
The Pawn Storm APT group set up rogue VPN and SFTP servers to target Dutch Safety Board employees involved in the MH17 crash investigation. July 17, 2014, Flight MH17, traveling from Amsterdam to Kuala Lumpur, was shot down by a missile in mysterious circumstances. Flight MH17 was flying over a conflict zone in eastern Ukraine […]
 Pierluigi Paganini
October 19, 2015
Good news, starting today, Facebook will notify you if they believe state-sponsored hackers are trying to compromise your account. Facebook announced a new initiative to protect its users from prying eyes, the popular social network will inform them on any suspected compromise from state-sponsored hackers. “Starting today, we will notify you if we believe your account […]
 Pierluigi Paganini
October 16, 2015
Despite both Microsoft and Adobe releasing patches on Tuesday (10/13/2015), a critical Flash zero-day flaw remains unpatched in Adobe’s latest update. Despite both Microsoft and Adobe releasing critical patches on Tuesday (10/13/2015), a critical zero-day vulnerability remains unpatched in Adobe’s latest update. As per Adobe APSA15-05, this vulnerability (CVE-2015-7645) remains unpatched is actively being exploited in-the-wild. Adobe plans […]
 Pierluigi Paganini
October 15, 2015
Researchers at Trend Micro discovered a new Adobe Flash Zero-Day used in Pawn Storm Campaign Targeting Foreign Affairs Ministries across the world. Once again Flash in the headlines, beware next emergency Flash Player update is critical for everybody as explained by the experts at Trend Micro. The researchers at the security firm explained that the update […]
 Pierluigi Paganini
October 08, 2015
Chinese Hackers who allegedly compromised servers at LoopPay, the Samsung subsidiary, appear interested in spying on targets through Samsung Pay technology. The Samsung subsidiary LoopPay has been the victim of a security breach that is worrying the security industry. The investigators speculate that attackers’ motivation is the cyber espionage and excluded a financial crime. If confirmed the security breach […]
 Pierluigi Paganini
September 25, 2015
According to a new report the popular Naikon APT group is actually backed by China’s PLA Unit 78020, a firm traced it through online activity. Ge Xing, also known as “GreenSky27,” is the name of an alleged member of the People’s Liberation Army unit 78020, a group of Chinese state-sponsored hackers. The man was identified […]
Malware / November 02, 2026
Security / November 02, 2026