 Pierluigi Paganini
 June 01, 2015
US financial industry is under persistent attacks, the number of incidents that compromised confidentiality, integrity and availability of data are increasing. Financial industry in US maintains symptoms of persistent cyber-attacks among surprising cyber incidents and large-scale data breaches that compromised confidentiality, integrity and availability of user’s information. Several advanced hacking methods and the exploitation of zero-day flaws […]
 Pierluigi Paganini
May 25, 2015
Security experts at FireEye have published a report that details the cyber threats targeting various sectors in the Nordic countries. According to FireEye, threat actors targeted strategic industries (i.e. aerospace and defense, energy, health and pharmaceuticals, and shipping), government and defense agencies searching for political, economic and military intelligence. Experts believe sophisticated threat groups could be […]
 Pierluigi Paganini
May 19, 2015
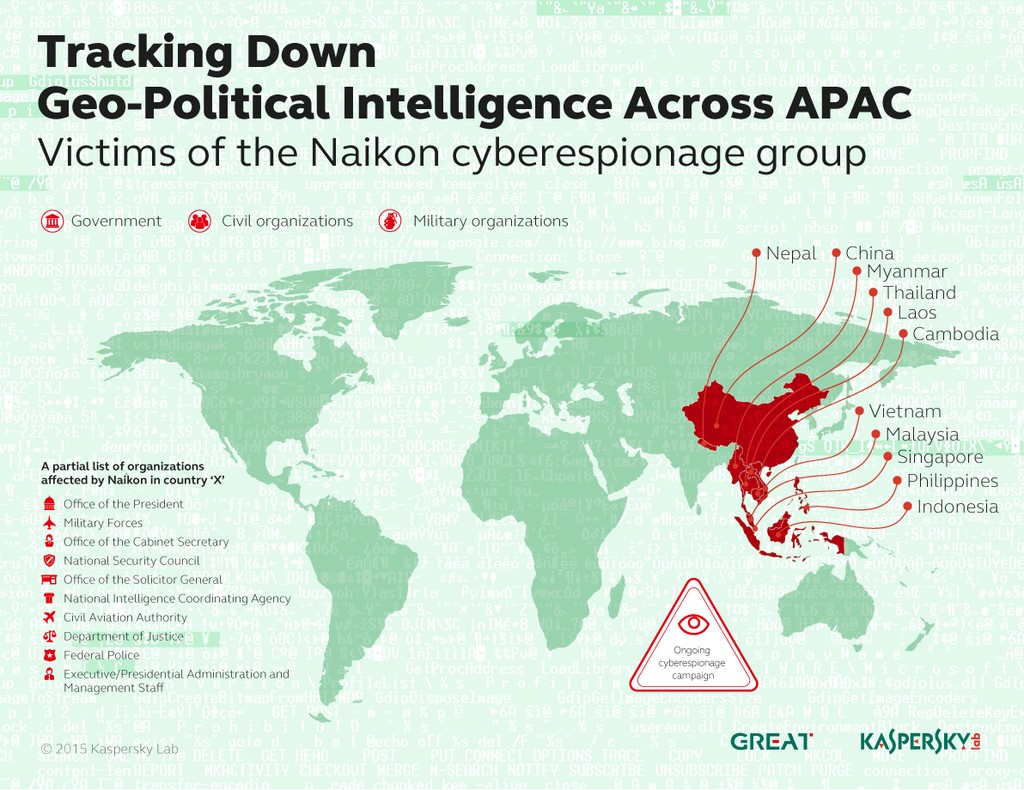
Experts at Kaspersky Lab published an interesting report on the activities of the Naikon APT revealing details on their infrastructures and TTPs. Naikon is one of the Asian largest APT gangs which has been active for several years, its operations targeted entities in various industries including governments and the military. The hacking crew targeted diplomats, law enforcement, and aviation […]
 Pierluigi Paganini
April 15, 2015
The elite cyber crime group Hellsing strikes back after attack by the rival APT crew known as Naikon. This is the first documented case of APT-on-APT attack. What happens when an APT group running a cyber espionage campaign target a second distinct APT group? The events occurred last year, when a group involved in a cyber espionage campaign […]
 Pierluigi Paganini
April 15, 2015
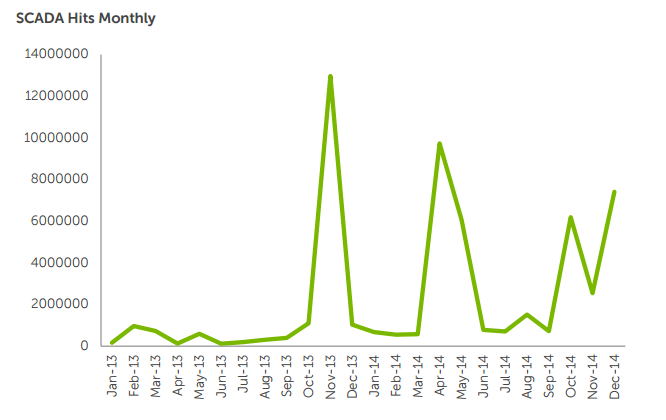
A recent report published by Dell revealed a 100 percent increase in the number of attacks on industrial control (SCADA) systems. The new Dell Annual Threat Report revealed that the number of attacks against supervisory control and data acquisition (SCADA) systems doubled in 2014 respect the previous year. Unfortunately, the majority of incidents occurred in SCADA systems is […]
 Pierluigi Paganini
March 21, 2015
Security experts at Trend micro uncovered a new hacking campaign dubbed Operation Woolen Goldfish likely run by a threat actor group known as Rocket Kitten. Security experts at Trend Micro have uncovered a new cyber espionage campaign that is targeting a number of European organisations and businesses. The attackers run a spear phishing campaign that […]
 Pierluigi Paganini
March 16, 2015
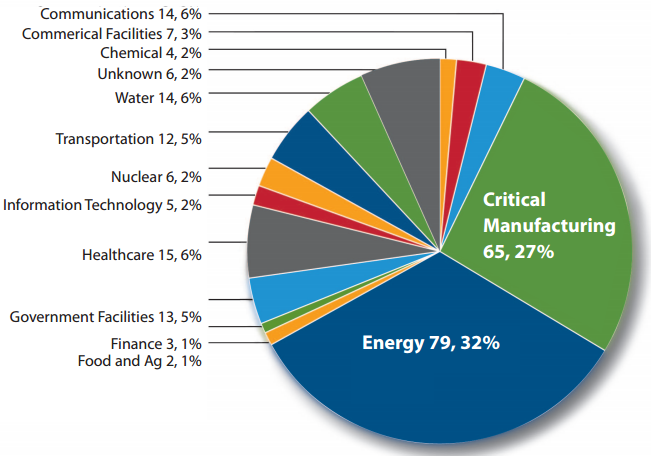
DHS ICS-CERT MONITOR report reveals that most critical infrastructure attacks involve APTs, but organizations lack monitoring capabilities. The DHS’s Industrial Control Systems Cyber Emergency Response Team (ICS-CERT) has issued its new ICS-CERT MONITOR report related to the period September 2014 – February 2015. The ICS-CERT MONITOR report According to the report, the Industrial Control Systems […]
 Pierluigi Paganini
March 02, 2015
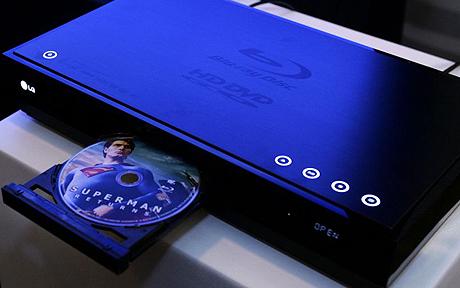
A British hacker has found two Blu-Ray-borne attacks that could be run to infect machines, a technique that remind the method used by the Equation Group. Security expert Stephen Tomkinson from NCC Group has discovered a couple of vulnerabilities in the software used to play Blu-ray discs. The exploitation of the flaw could be used to implant […]
 Pierluigi Paganini
February 23, 2015
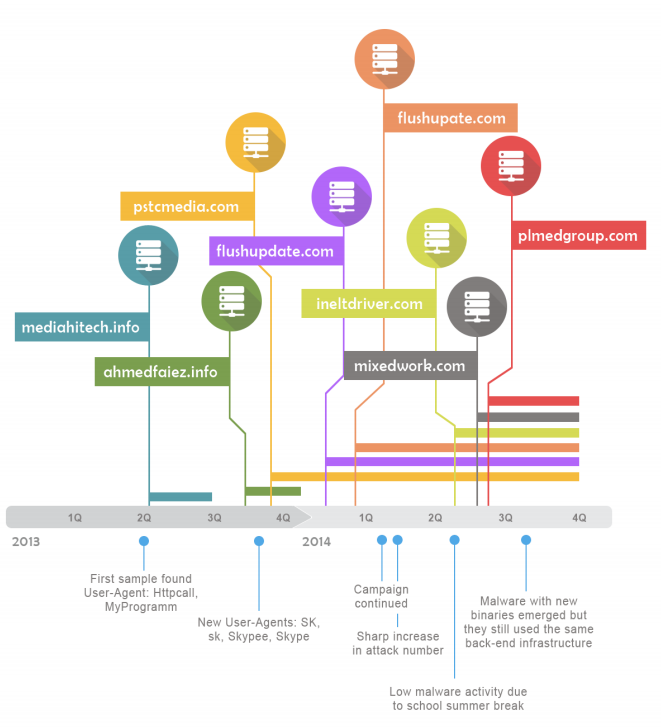
The cyber security expert Ashiq JA analyzed the principal characteristics of APT (Advanced Persistent Threat) and AVT (Advanced Volatile Threat) . Cybercriminals and their techniques in the APT and AVT attacks “APT is an attack in the persistent memory that resides in the victims machine without getting noticed and the attacker exfiltrates sensitive information from […]
 Pierluigi Paganini
February 19, 2015
Attackers behind the Arid Viper and the Yanbian Gang exploited sex content for their campaigns against victims in Israel and Kuwait, and South Korea. Security experts at Trend Micro have uncovered a cyber espionage campaign, dubbed Operation Arid Viper, that targeted Israeli institutions. The Operation Arid Viper is run by Arab-speaking hackers that sought to extract […]
Malware / November 02, 2026
Security / November 02, 2026