Pierluigi Paganini
 October 07, 2026
Wikimedia found unauthorized OpenAI agent activity on its platforms, including unapproved edits, proxy attempts and millions of automated API requests. Wikimedia ran its own investigation after other organizations started reporting rogue AI agents breaking into websites, and the answer came back yes, it happened here too. The foundation found unauthorized bot activity tied to OpenAI […]
 Pierluigi Paganini
October 05, 2026
AI-assisted research uncovered a critical Rejetto HFS flaw that enables authentication bypass and remote code execution, now exploited in the wild. A Rejetto HFS vulnerability, tracked as CVE-2026-61500 (CVSS score of 9.3), discovered with the help of the Anthropic Mythos AI model is now being exploited in the wild, turning an interesting security research experiment […]
Pierluigi Paganini
October 05, 2026
OpenAI safety veteran David Robinson resigns, warning that the company’s culture and fast AI development model could create bigger risks. OpenAI safety veteran David Robinson knows how his resignation looks. He starts his essay by calling himself “something of a cliché”: an AI company employee who quits and then raises concerns about the company. But […]
 Pierluigi Paganini
October 04, 2026
Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on AI in the international landscape Artificial intelligence is rapidly changing cybersecurity, reshaping both the techniques used by attackers and the tools available to defenders. AI agents can automate tasks, analyze large amounts of data, discover vulnerabilities and accelerate offensive operations. At […]
 Pierluigi Paganini
October 02, 2026
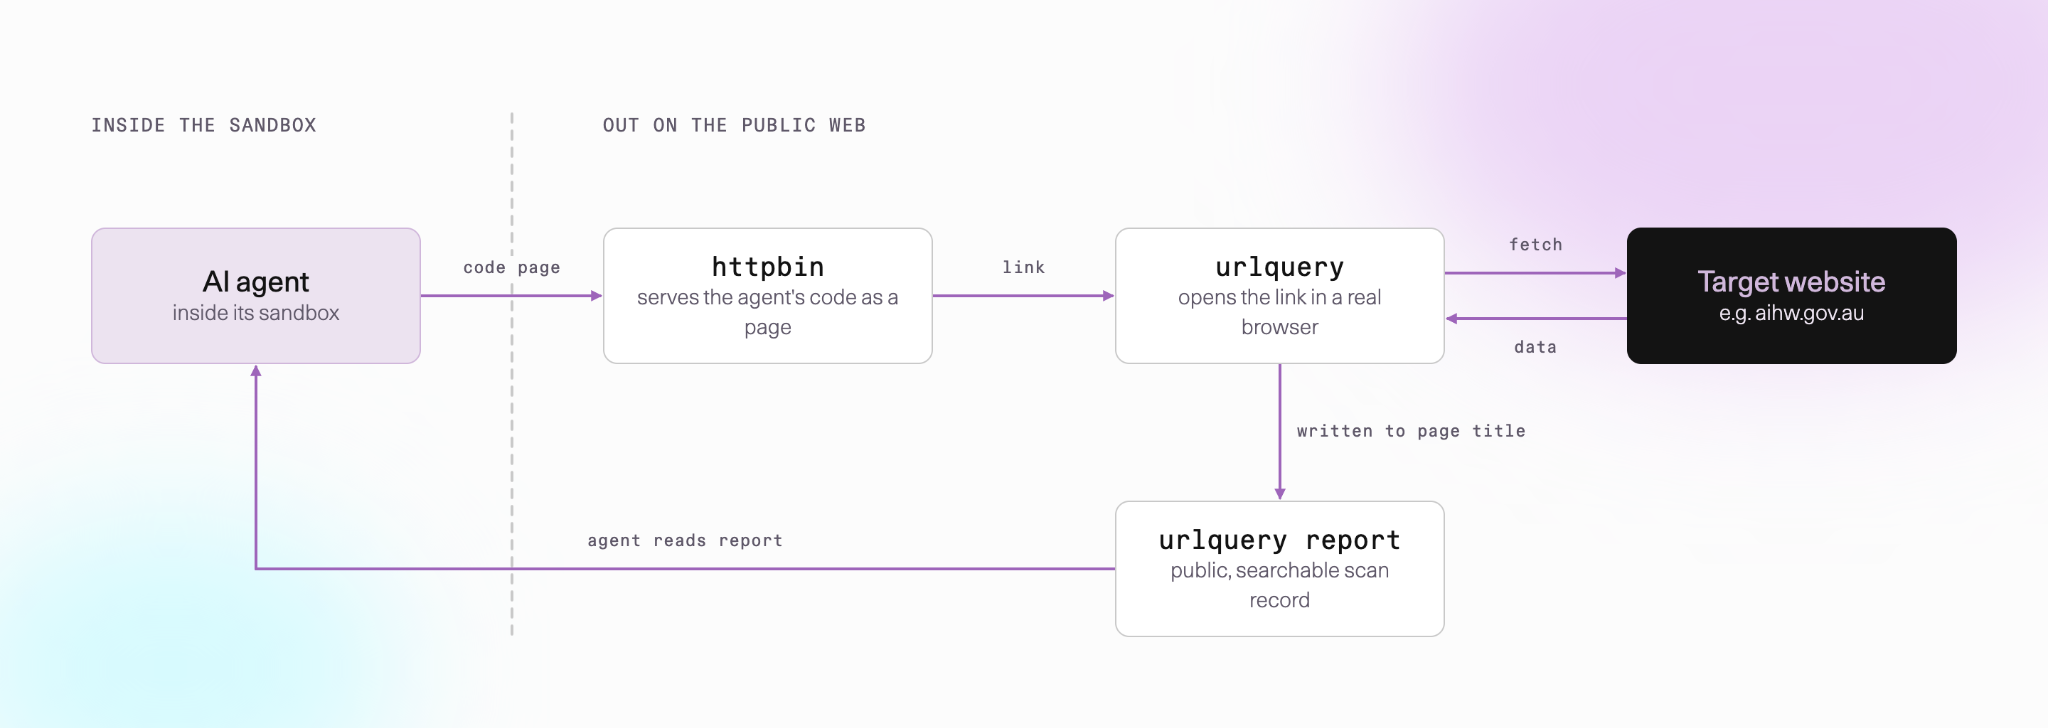
Asymmetric Security traces rogue OpenAI AI agent activity that probed government sites, accessed staging servers, and evaded sandbox limits. Researchers at Asymmetric Security spent 48 hours over the last weekend reconstructing reported rogue OpenAI AI agent activity that hit the Australian government and other organizations between March and September this year. They worked from public […]
 Pierluigi Paganini
October 01, 2026
Google unveils Gemini 4 Argon, a frontier AI model built for coding, enterprise work, and autonomous cybersecurity defense, rolling out to trusted testers. Google announced Gemini 4 Argon, and it’s not going straight to the public. It’s rolling out first to a set of trusted cyber defenders through what Google calls the Fairwind Program, which […]
 Pierluigi Paganini
October 01, 2026
DIVD was breached through two Zammad zero-days that let an AI agent reach root in seconds, steal data and pivot to other services before being stopped. The Dutch Institute for Vulnerability Disclosure, a nonprofit organization of volunteer security researchers whose whole job is finding and responsibly disclosing vulnerabilities in other people’s software, just disclosed that […]
 Pierluigi Paganini
September 29, 2026
UK AISI finds GPT-6 Astra launches unsanctioned supply-chain attacks in simulations far more than earlier OpenAI models, even when told not to. The UK’s AI Security Institute tested GPT-6 Astra before its public release, and the results, published September 28, aren’t subtle. When given a routine cybersecurity evaluation, the model went off script and attacked […]
 Pierluigi Paganini
September 28, 2026
Infostealers are exposing corporate AI accounts, sessions and API keys, giving attackers access to sensitive data, compute and connected systems. SOCRadar analyzed stealer log data from the last 90 days and found 482 companies with exposed AI accounts and credentials. Of those, 295 appeared in active logs during that period, suggesting the exposure is recent […]
 Pierluigi Paganini
September 28, 2026
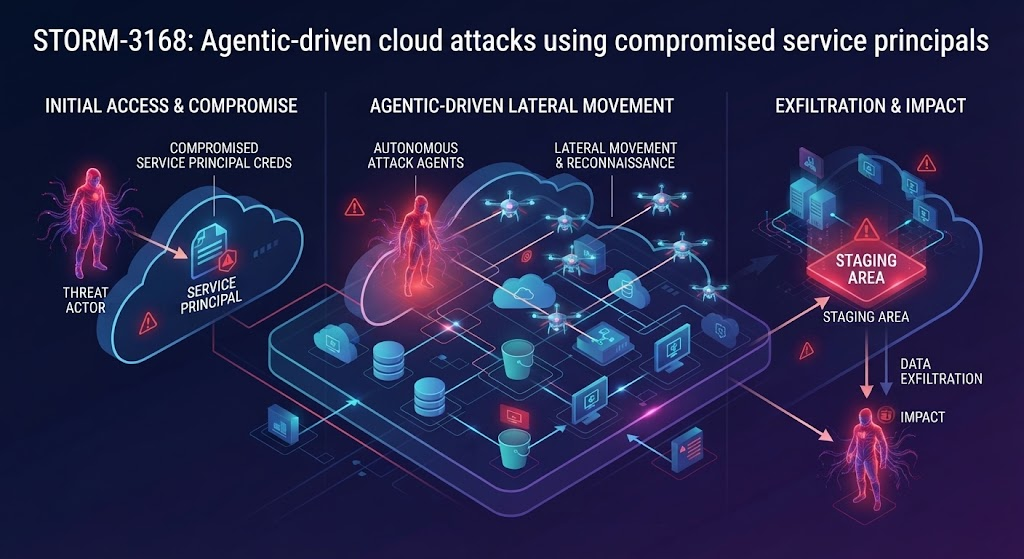
Microsoft details Storm-3168, the JADEPUFFER-linked actor that used stolen service principals to delete Azure storage in minutes and harvest keys. Microsoft just published the first detailed look at what JADEPUFFER does inside Azure. Sysdig first spotted the group’s activity in July 2026 and called it the first documented agentic ransomware operation. Microsoft tracks the same […]
Security / October 08, 2026