 Pierluigi Paganini
 June 18, 2020
Researchers uncovered an ongoing campaign delivering the Qbot malware to steal credentials from customers of dozens of US financial institutions. Security researchers at F5 Labs have spotted ongoing attacks using Qbot malware payloads to steal credentials from customers of dozens of US financial institutions. Qbot, aka Qakbot, is a data stealer worm with backdoor capabilities that […]
 Pierluigi Paganini
May 12, 2020
The Zeus Sphinx banking Trojan continues to evolve while receiving new updates it is employed in ongoing coronavirus-themed scams. IBM security researcher continues to monitor the evolution of the infamous Zeus Sphinx banking Trojan (aka Zloader or Terdot) that receives frequent updates and that was involved in active coronavirus scams. The Zeus Sphinx banking Trojan is based […]
 Pierluigi Paganini
May 07, 2020
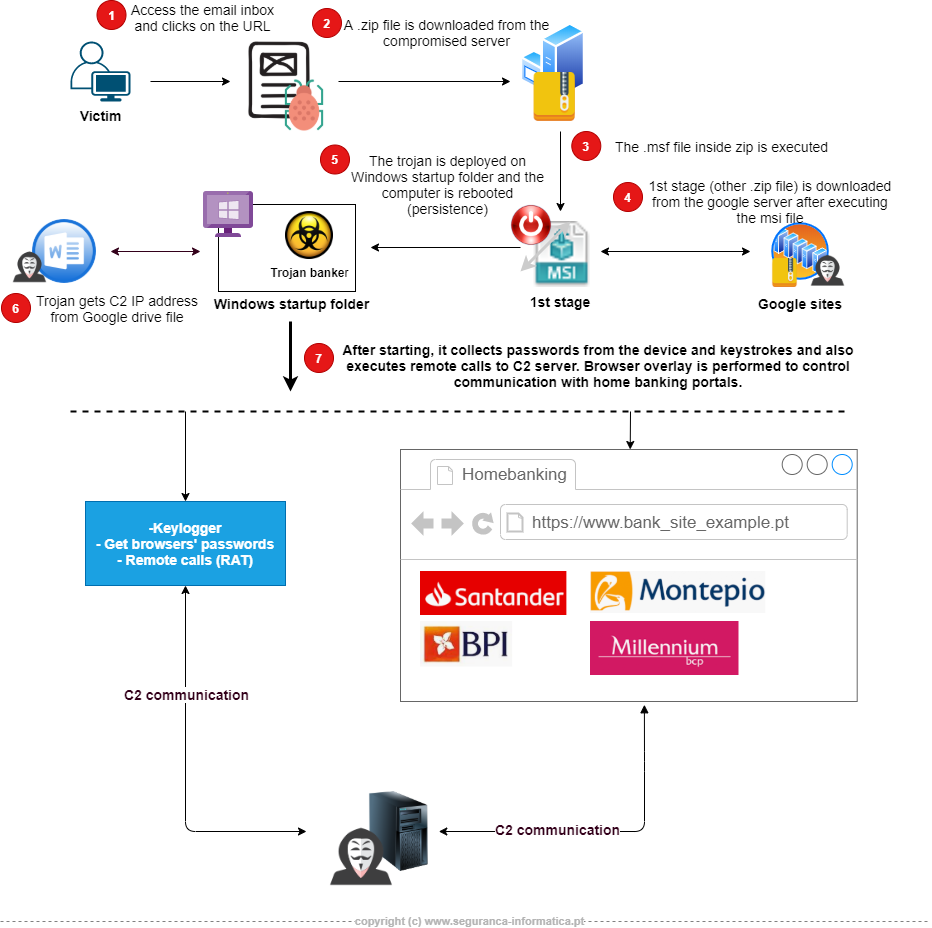
Since the end of April 2020, a new trojan has been affecting Portuguese users from several bank organizations. The modus operandi of this piece of malware is not new in Portugal. At least since the year of 2014 that new variants have been observed, with minor changes, and with the objective of collecting bank details […]
 Pierluigi Paganini
February 26, 2020
DDoS extortionists are blackmailing Australian banks asking for payments of large sums in Monero cryptocurrency threatening DDoS attacks. Cybercriminals are threatening Australian banks of DDoS attacks if they will not pay large sums in Monero cryptocurrency. The extortion campaign was observed over the past week, attackers are sending emails to the banks threatening to carry […]
 Pierluigi Paganini
February 14, 2020
Nedbank bank announced on Thursday that a security breach at a third-party supplier has compromised the details of as many as 1.7 million of its clients. Nedbank bank disclosed on Thursday a security breach at a third-party supplier that has compromised the details of as many as 1.7 million of its clients. The bank revealed that […]
 Pierluigi Paganini
February 11, 2020
Unauthorized use of customer information by Woori Bank, ‘crime act’ for customers. The bank changed 23,000 passwords in 2018 without consent. It is controversial that Woori Bank changed the passwords of 23,000 customer dormant accounts without consent in July 2018. The accounts are deactivated if there is no transaction for one year after their opening. […]
 Pierluigi Paganini
February 10, 2020
The president of the European Central Bank (ECB), Christine Lagarde, is warning that a cyber-attack on a major financial institution could trigger a liquidity crisis. The president of the European Central Bank (ECB), Christine Lagarde, has warned that a coordinated cyber-attack on major banks could trigger a liquidity crisis. President Lagarde cited findings of a […]
 Pierluigi Paganini
January 15, 2020
P&N Bank discloses data breach, customer account information, balances exposed The Australian P&N Bank is notifying its customers a data breach that has exposed personally identifiable information (PII) and sensitive account data. P&N Bank, a division of Police & Nurses Limited and operating in Western Australia, suffered a data breach and is reporting the incident […]
 Pierluigi Paganini
September 03, 2019
Criminals have stolen more than €1.5 million from the German bank OLB by cloning customer debit cards and using them to cash out user funds across Brazil. ZDnet first reported that last week cyber criminals have stolen more than €1.5 million from the German bank Oldenburgische Landesbank (OLB) by cloning customer debit cards and using […]
 Pierluigi Paganini
August 28, 2019
Recent campaigns show threat actors behind the Dridex and Locky malware families, the TA505 group, have updated tactics and expanded its target list. Trend Micro revealed that the TA505 group that is behind the Dridex and Locky malware families continue to make small changes to its operations. TA505 hacking group has been active since 2014 […]