 Pierluigi Paganini
 October 01, 2026
Operation KillSwitch: Europol says the KillSec ransomware group, allegedly led by a 16-year-old, was dismantled after attacks on about 1,000 victims. Law enforcement seized control of KillSec ‘s dark web leak site, the Tor website the group used to threaten victims with publishing stolen files unless they paid up. That single action locked down more […]
 Pierluigi Paganini
September 30, 2026
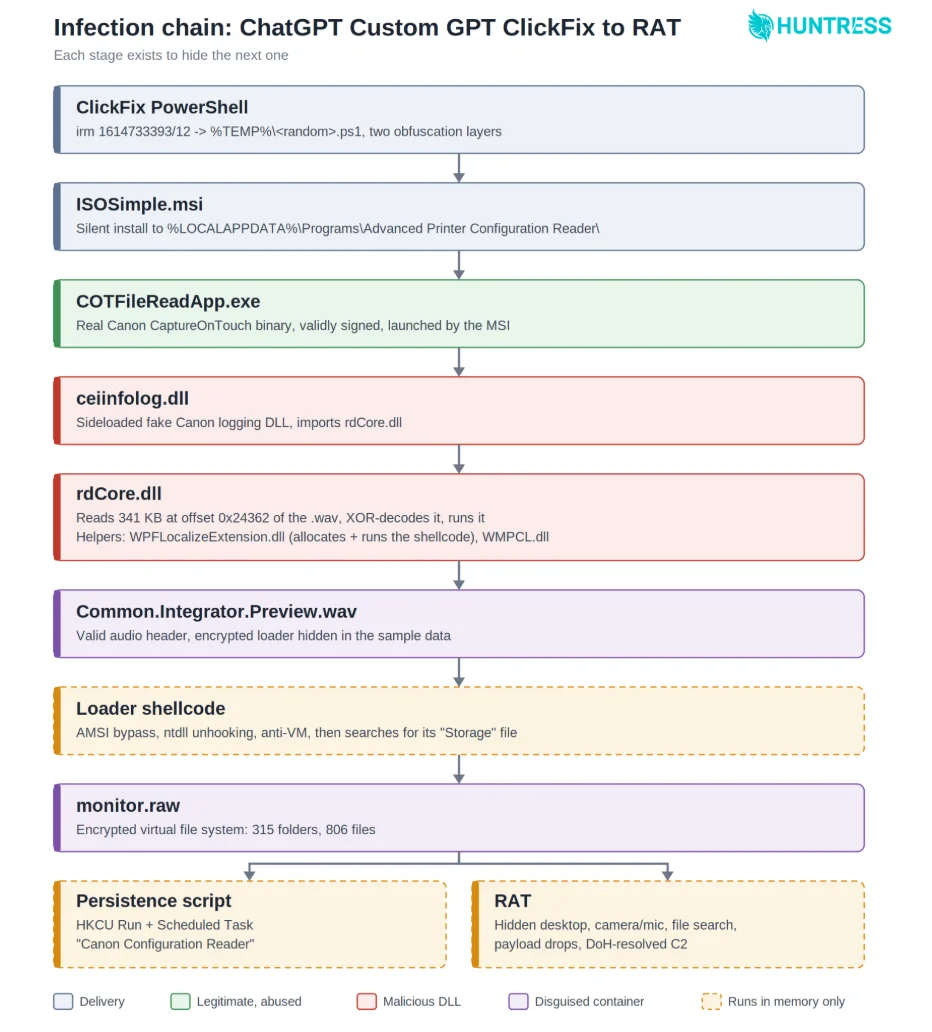
Threat actors abused fake ChatGPT Custom GPTs and ClickFix to deliver a multi-stage RAT. ChatGPT’s Custom GPT feature is the latest legitimate surface being turned into a delivery mechanism, and Huntress researchers caught it in action across at least 40 incidents. A Custom GPT (now simply called a GPT) is essentially a version of ChatGPT […]
 Pierluigi Paganini
September 29, 2026
Keio, a major Japanese railway operator, was hit by ransomware, disrupting business systems and forcing the company to shut down its network. Keio Corporation, one of Japan’s major private railway operators, was hit by a ransomware attack over the weekend, disrupting some of its business systems. The company detected a system failure early Saturday and […]
 Pierluigi Paganini
September 29, 2026
Dutch police confirm the arrest of a 24-year-old Amsterdam man as part of an investigation into the ShinyHunters hacking group. Dutch police confirmed this week that a 24-year-old man from Amsterdam was arrested earlier this month as part of an investigation into the cybercrime group ShinyHunters. The suspect appears before Rotterdam District Court today, September […]
 Pierluigi Paganini
September 28, 2026
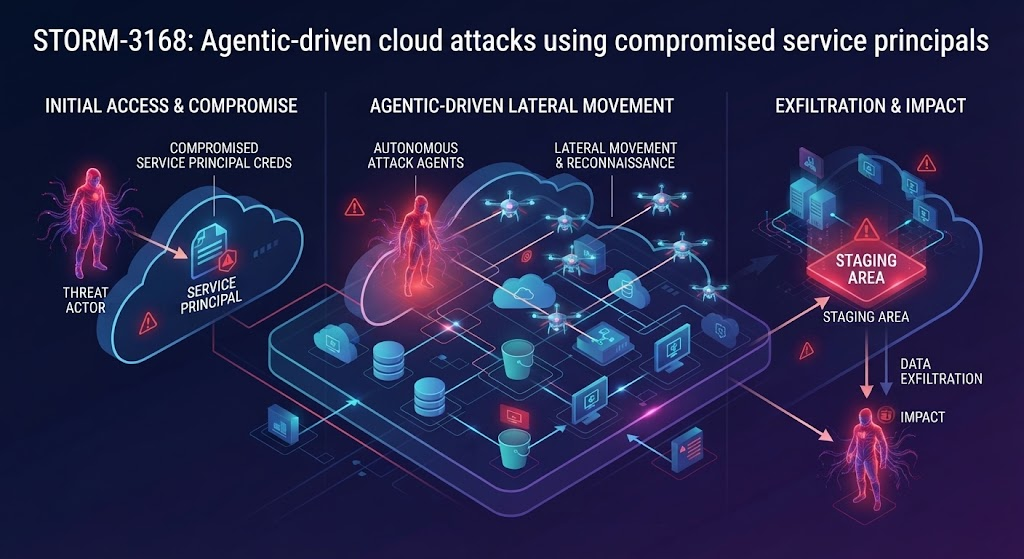
Microsoft details Storm-3168, the JADEPUFFER-linked actor that used stolen service principals to delete Azure storage in minutes and harvest keys. Microsoft just published the first detailed look at what JADEPUFFER does inside Azure. Sysdig first spotted the group’s activity in July 2026 and called it the first documented agentic ransomware operation. Microsoft tracks the same […]
 Pierluigi Paganini
September 27, 2026
Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on AI in the international landscape Artificial intelligence is rapidly changing cybersecurity, reshaping both the techniques used by attackers and the tools available to defenders. AI agents can automate tasks, analyze large amounts of data, discover vulnerabilities and accelerate offensive operations. At […]
 Pierluigi Paganini
September 27, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Threat Intel | One Kit, Forty Companies: How a Malware-as-a-Service Platform Used GitHub as a Distribution Network for its Campaign Group Policy hijacked: PAYLOAD ransomware weaponizes Active Directory GPO ChainScript: Tracing a Node.js RAT […]
 Pierluigi Paganini
September 27, 2026
Kosovo national Ardit Kutleshi pleaded guilty to running Rydox, a cybercrime marketplace that sold stolen identities and credentials for years. Ardit Kutleshi, 28 years old and a citizen of Kosovo, pleaded guilty last week to building and running the cybercrime marketplace Rydox. The Rydox marketplace has been active since February 2016; it facilitated over 7,600 […]
 Pierluigi Paganini
September 26, 2026
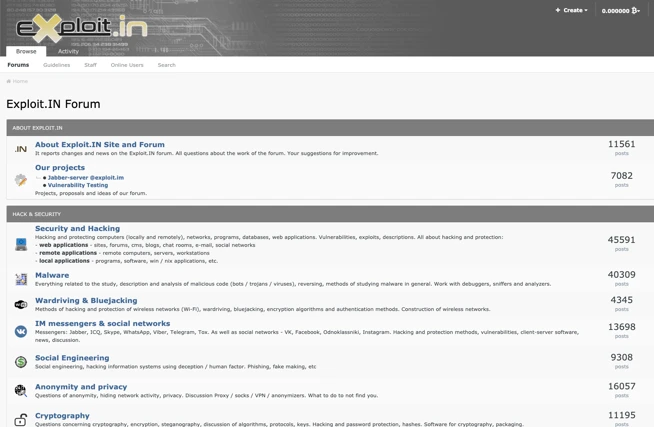
Exploit.in data shows how a 2005 cybercrime forum helped shape today’s ransomware ecosystem, with users and practices surviving for decades. Ransomnews researcher Dancho Danchev dug up a database dump of Exploit.in covering its first three years, from February 2005 to May 2008, and the numbers inside it tell a story about Russian cybercrime that enforcement […]
 Pierluigi Paganini
September 25, 2026
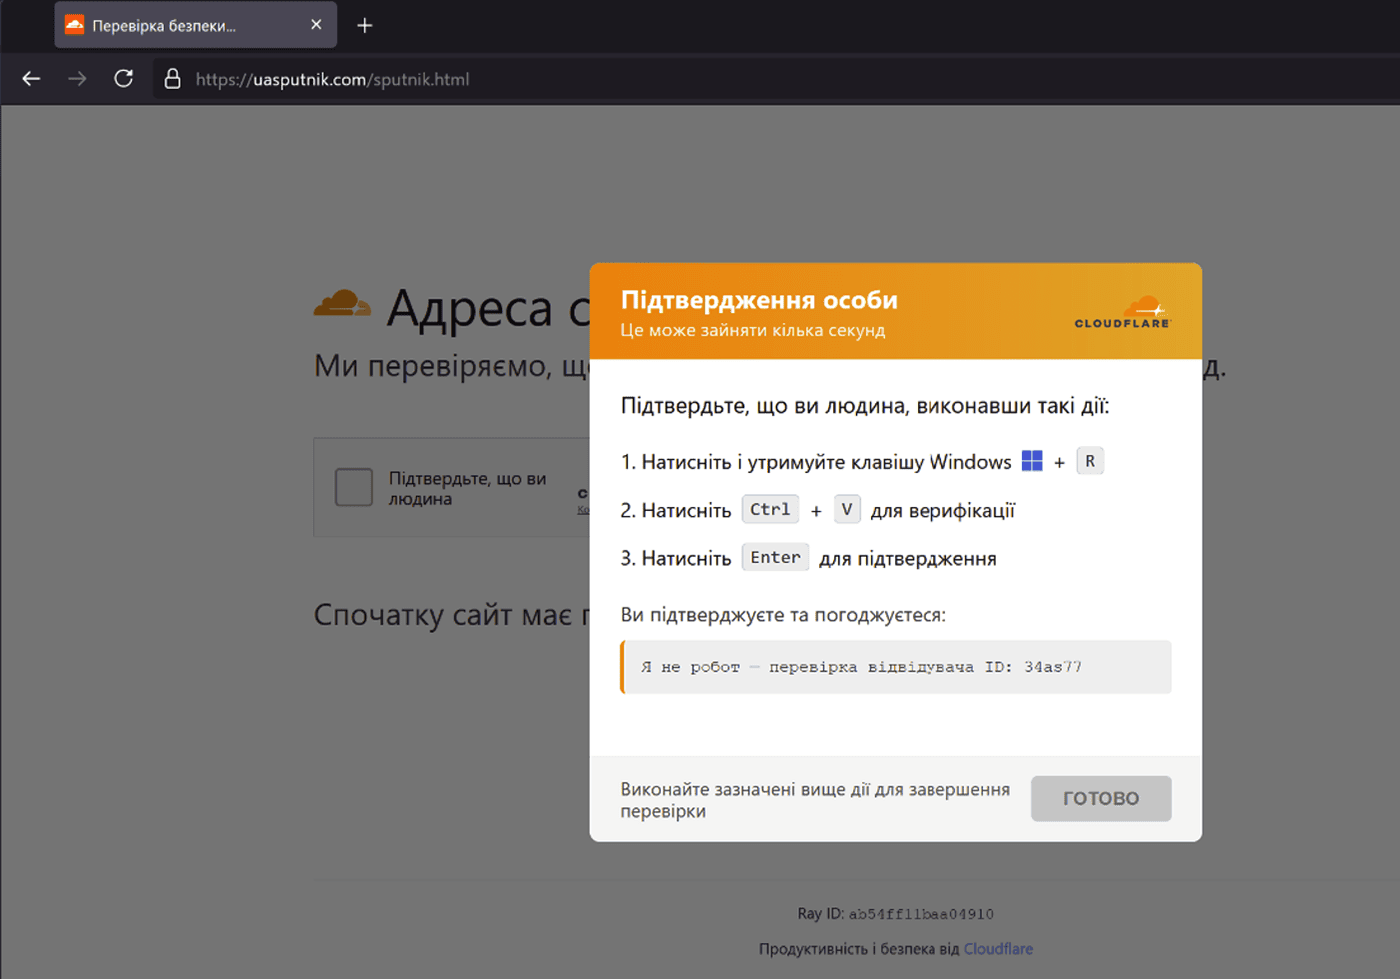
Attackers hijacked Ukrainian websites to deliver a fake Cloudflare CAPTCHA that installs Psychedelic Stealer and steals browser and crypto credentials. Psychedelic Stealer is being distributed through compromised Ukrainian business websites. Attackers injected hidden iframes into legitimate pages and used them to display a fake Cloudflare verification screen to visitors. The affected sites included a hair-treatment […]