 Pierluigi Paganini
 November 20, 2021
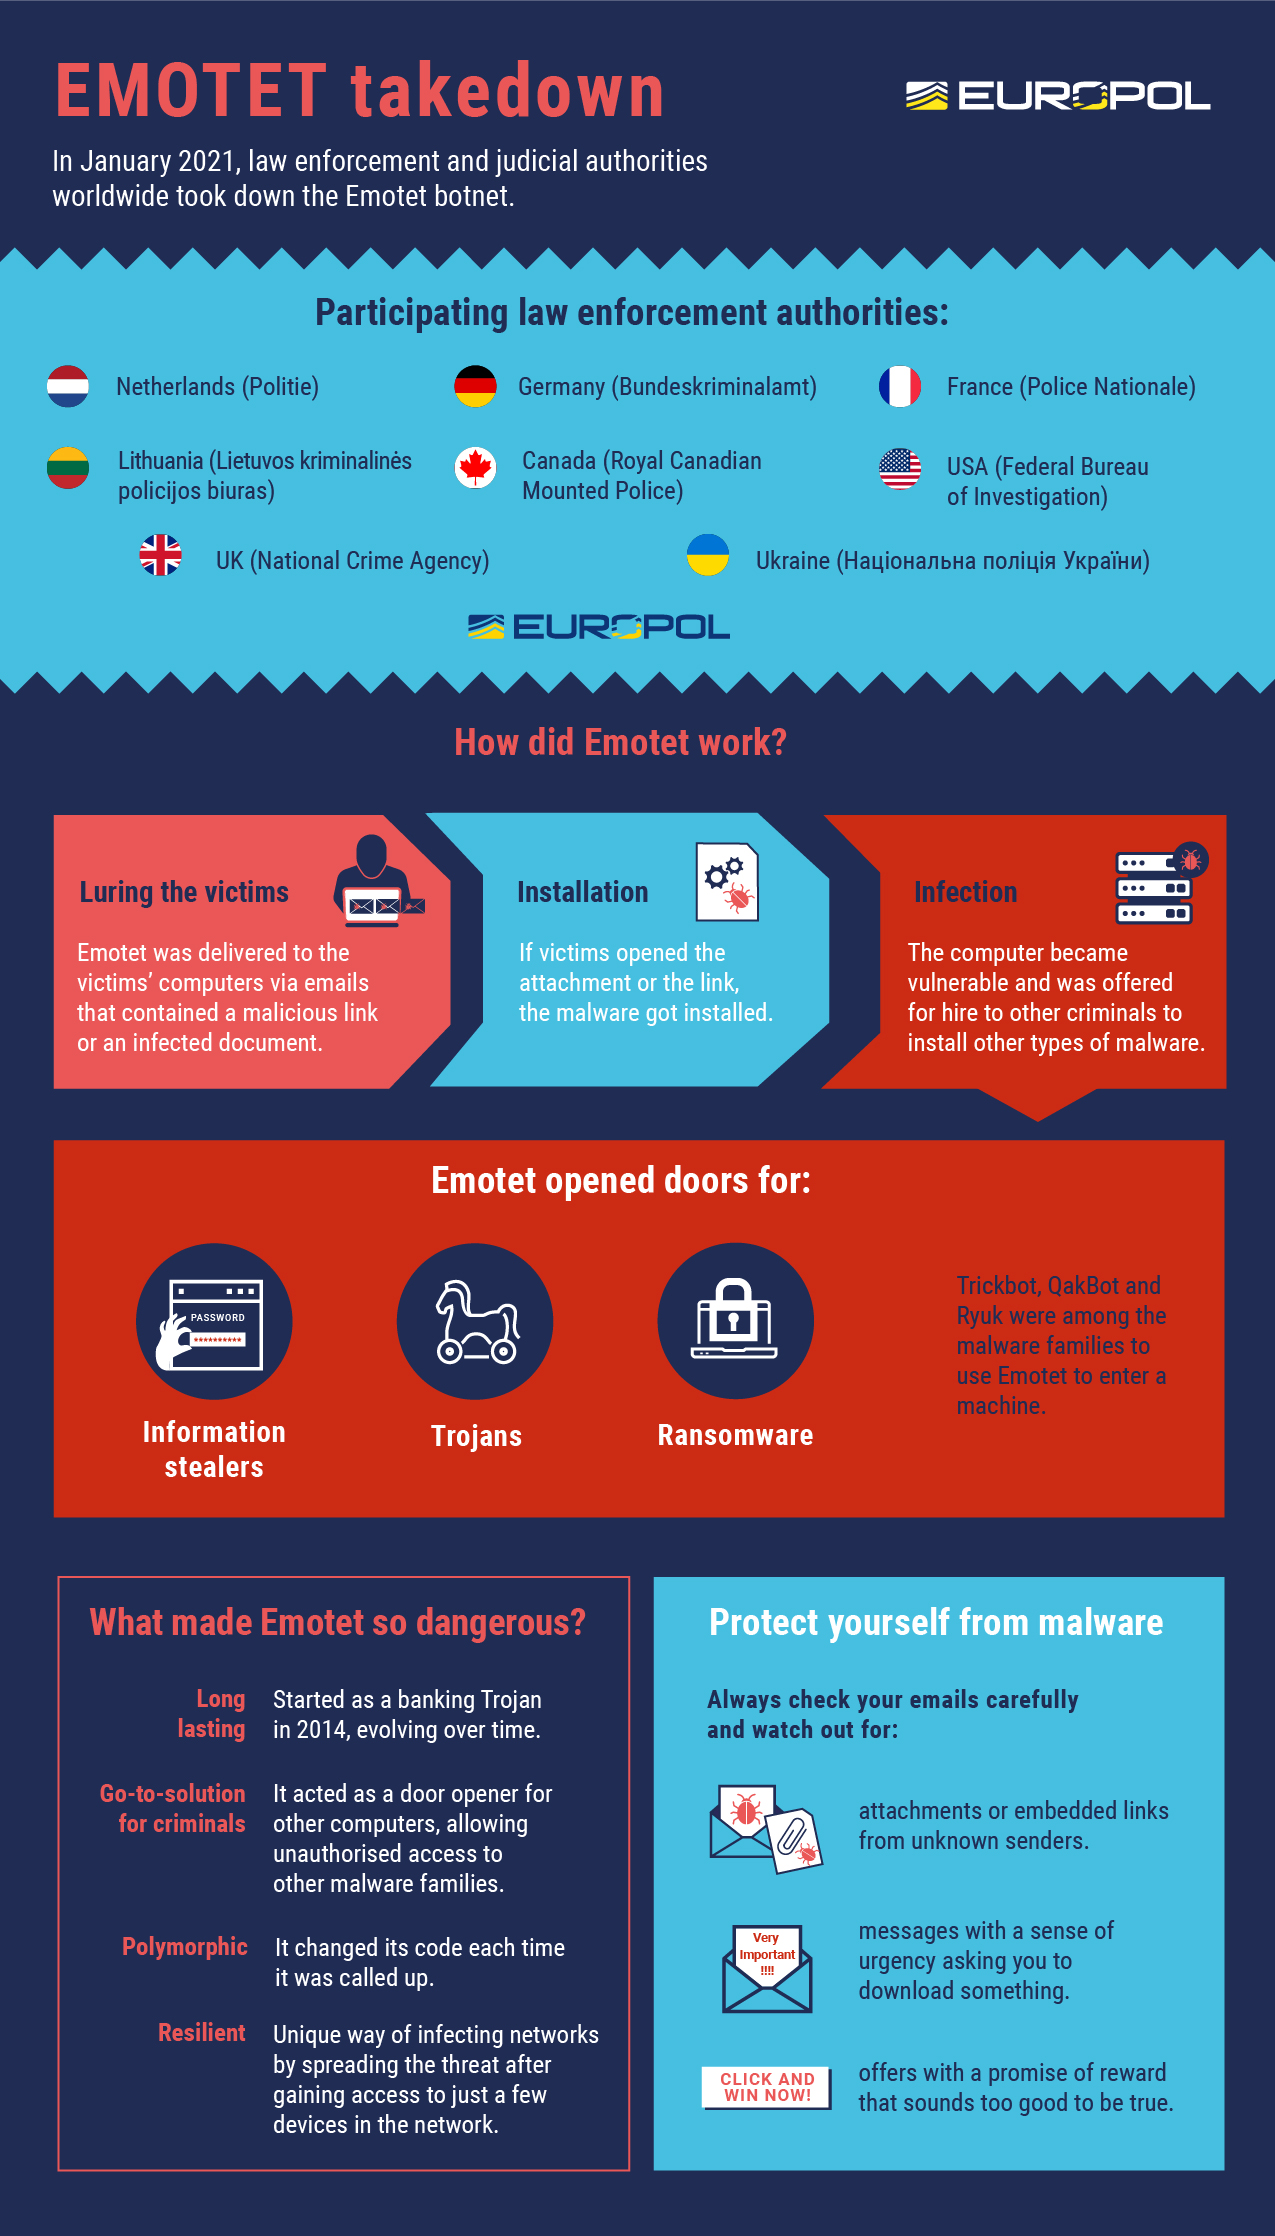
Advanced Intelligence researchers argue that the restarting of the Emotet botnet was driven by Conti ransomware gang. Early this year, law enforcement and judicial authorities worldwide conducted a joint operation, named Operation Ladybird, which disrupted the EMOTET botnet. At the time the investigators have taken control of its infrastructure in an international coordinated action. This operation was […]
 Pierluigi Paganini
November 19, 2021
American pizza chain California Pizza Kitchen (CPK) suffered a data breach that might have exposed personal information of its employees. American pizza chain California Pizza Kitchen (CPK) suffered a data breach, the company has already notified employees whose personal information might have been exposed. According to a data breach notification sent to the impacted employees, […]
 Pierluigi Paganini
November 19, 2021
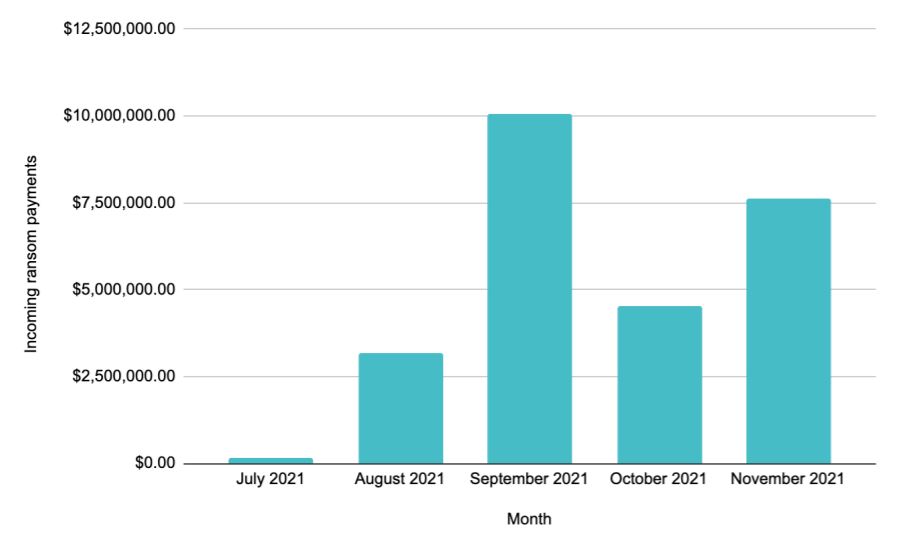
Researchers revealed that Conti ransomware operators earned at least $25.5 million from ransom payments since July 2021. A study conducted by Swiss security firm Prodaft with the support of blockchain analysis firm Elliptic revealed that the operators of the Conti ransomware have earned at least $25.5 million from attacks and subsequent ransoms carried out since […]
 Pierluigi Paganini
November 19, 2021
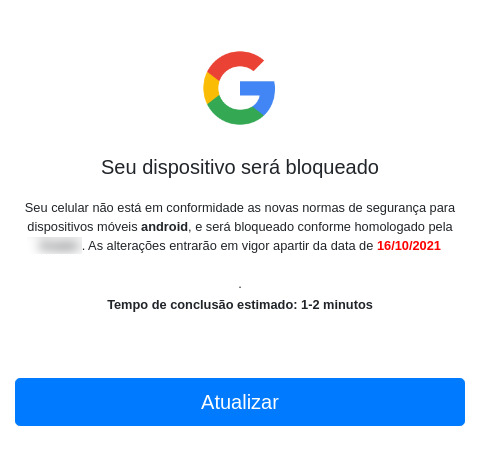
The BrazKing Android banking trojan is back with significant improvements and dynamic banking overlays to avoid detection. Researchers from IBM spotted a new version of the BrazKing Android banking trojan that pull fake overlay screens from the command and control (C2) server in real-time. In the previous version, BrazKing abused the accessibility service to detect which app […]
 Pierluigi Paganini
November 18, 2021
Researchers discovered threat actors installing a Linux backdoor on compromised e-commerce servers after deploying a credit card skimmer into e-stores. Security researchers from Sansec Threat Research Team discovered a Linux backdoor during an investigation into the compromised of an e-commerce server with a software skimmer. The attackers initially conducted a reconnaissance phase by probing the […]
 Pierluigi Paganini
November 16, 2021
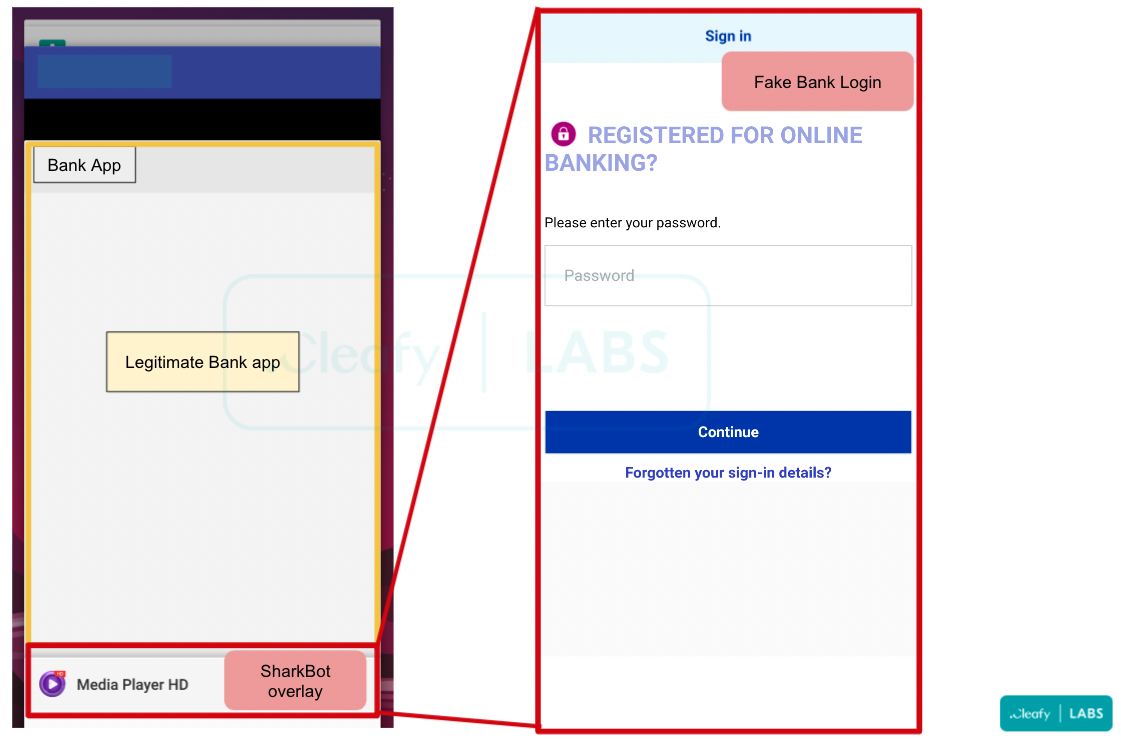
Security researchers from Cleafy discovered a new Android banking trojan, named SharkBot, that is targeting banks in Europe. At the end of October, researchers from cyber security firms Cleafy and ThreatFabric have discovered a new Android banking trojan named SharkBot. The name comes after one of the domains used for its command and control servers. […]
 Pierluigi Paganini
November 15, 2021
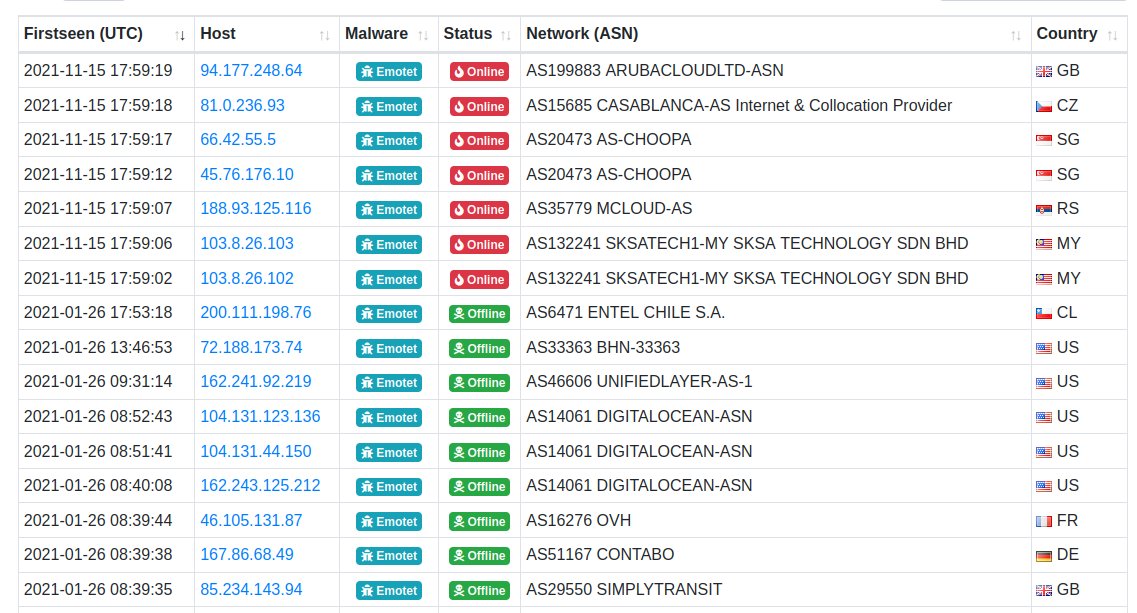
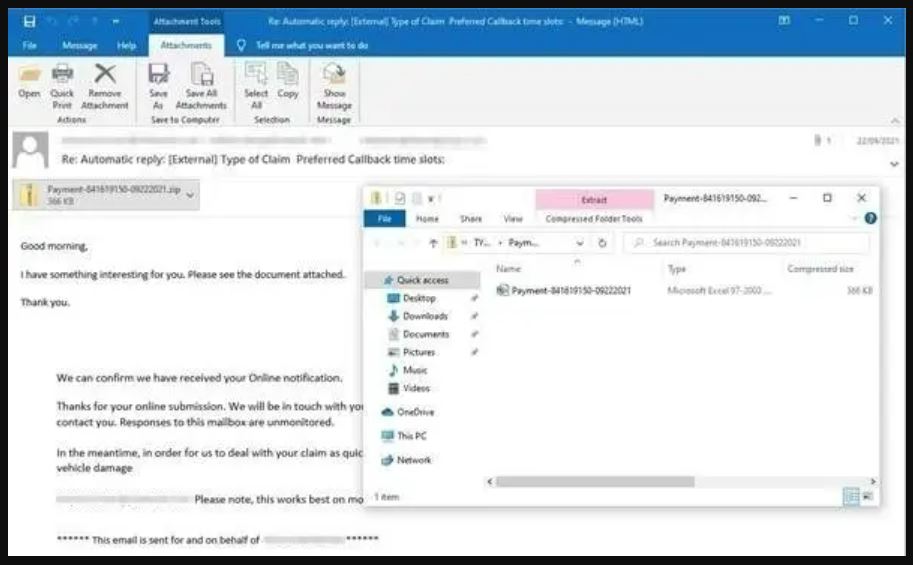
The Emotet botnet is still active, ten months after an international operation coordinated by Europol shut down its infrastructure. Early this year, law enforcement and judicial authorities worldwide conducted a joint operation, named Operation Ladybird, which disrupted the EMOTET botnet. At the time the investigators have taken control of its infrastructure in an international coordinated action. […]
 Pierluigi Paganini
November 15, 2021
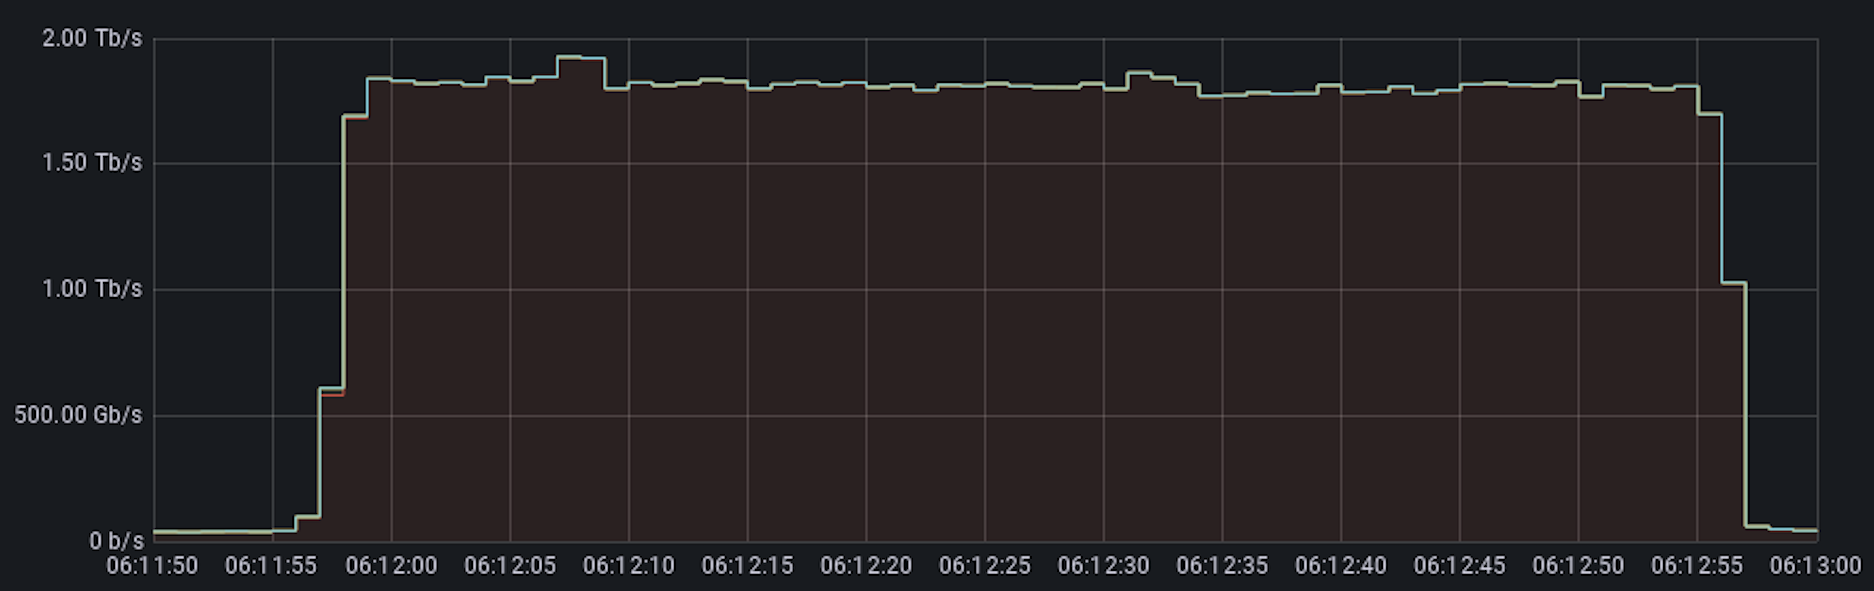
Cloudflare announced to have mitigated a distributed denial-of-service (DDoS) attack that peaked at almost 2 terabytes per second (Tbps). Cloudflare, Inc. is an American web infrastructure and website security company that provides content delivery network and DDoS mitigation services. The company announced to have mitigated a distributed denial-of-service (DDoS) attack that peaked just below 2 terabytes per second (Tbps), which […]
 Pierluigi Paganini
November 15, 2021
Ten years together! I’m very excited. I launched Security Affairs for passion in 2011 and millions of readers walked with me. Thanks Ten years ago I launched Security Affairs, the blog over the past decade obtained important successes in the cyber security community, but the greatest one is your immense affection. Over the past decade, […]
 Pierluigi Paganini
November 15, 2021
Experts warn of a surge in infections of the QBot (aka Quakbot) banking trojan which seems to be associated with the rise of Squirrelwaffle. Researchers warn of a new wave of QBot (aka Qakbot) banking trojan infections that appears to be associated with the rise of Squirrelwaffle. “Toward the end of September 2021, we noted […]
Malware / November 11, 2026