 Pierluigi Paganini
 October 11, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter ClingSTUN Linux Backdoor Abuses Public STUN Infrastructure UAC-0277: ClickFix on compromised websites to spread LUNEXSTEALER MALFEX – A malicious npm postinstall no advisory has caught for fourteen months Canto incognito: tracking the PoeLLM malware […]
 Pierluigi Paganini
October 11, 2026
Bitdefender finds Midnight Mimosa, preinstalled Android malware on cheap MediaTek phones that fakes ad clicks, drops apps and builds a proxy botnet. Bitdefender researchers discovered a campaign called Midnight Mimosa involving preinstalled Android malware on low-cost phones from different brands that use MediaTek platforms. The malware is built into the device firmware and may be […]
 Pierluigi Paganini
October 11, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. Anthropic Restricts Live Internet Access After Claude Evaluation Failures Silent Ransom Group Allegedly Extorted $207 Million Without […]
 Pierluigi Paganini
October 10, 2026
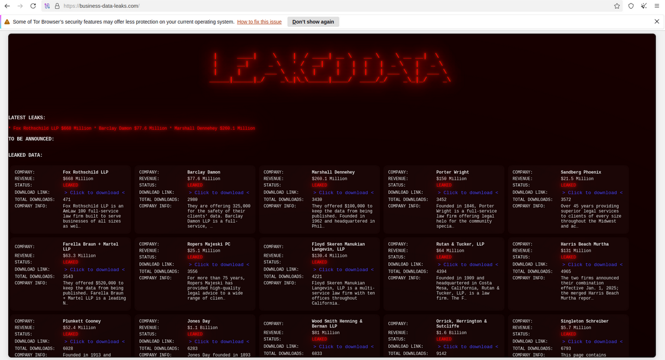
Silent Ransom Group allegedly extorted $207 million from 27 law firms in six months using phone calls and social engineering, not encryption. Silent Ransom Group doesn’t rely on encryption. No malware payload, no locked files, just phone calls and social engineering aimed almost entirely at law firms, and apparently it works extraordinarily well. A new […]
 Pierluigi Paganini
October 10, 2026
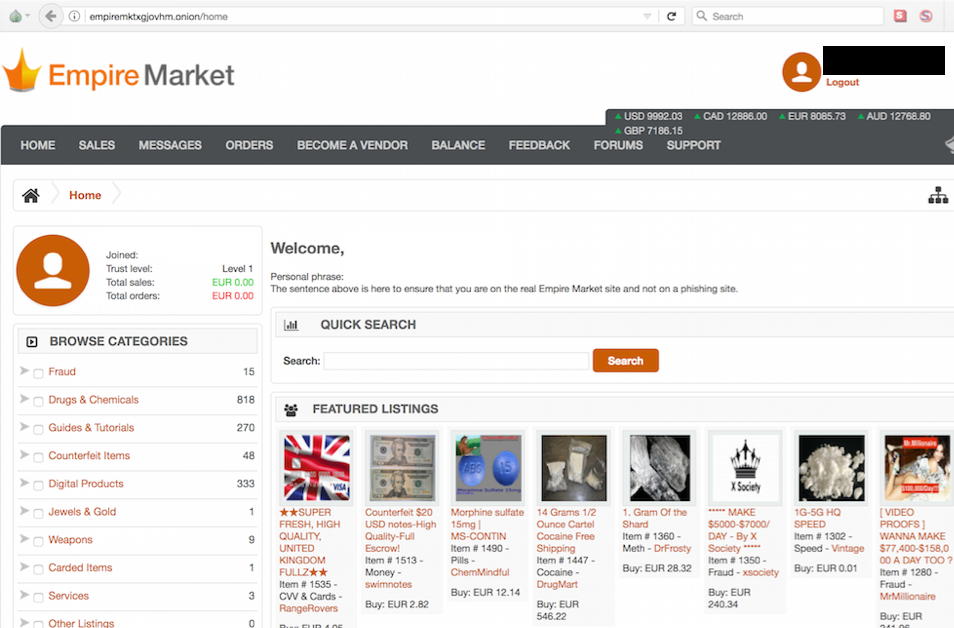
Empire Market co-creator Raheim Hamilton was sentenced to 40 years in prison for running a dark web marketplace linked to $430 million in illegal trades. The case against Empire Market shows how a dark web marketplace can become a major criminal business, bringing together drug trafficking, stolen credentials, personal data and hacking tools. “A Virginia […]
 Pierluigi Paganini
October 09, 2026
Japan helped extradite a Russian suspect linked to Qilin ransomware to Germany, but the gang continued attacking victims after his arrest. Germany has arrested a Russian national believed to be a leading figure in the Qilin ransomware group, and Japan’s National Police Agency just put its own role in that arrest on the record. The […]
 Pierluigi Paganini
October 08, 2026
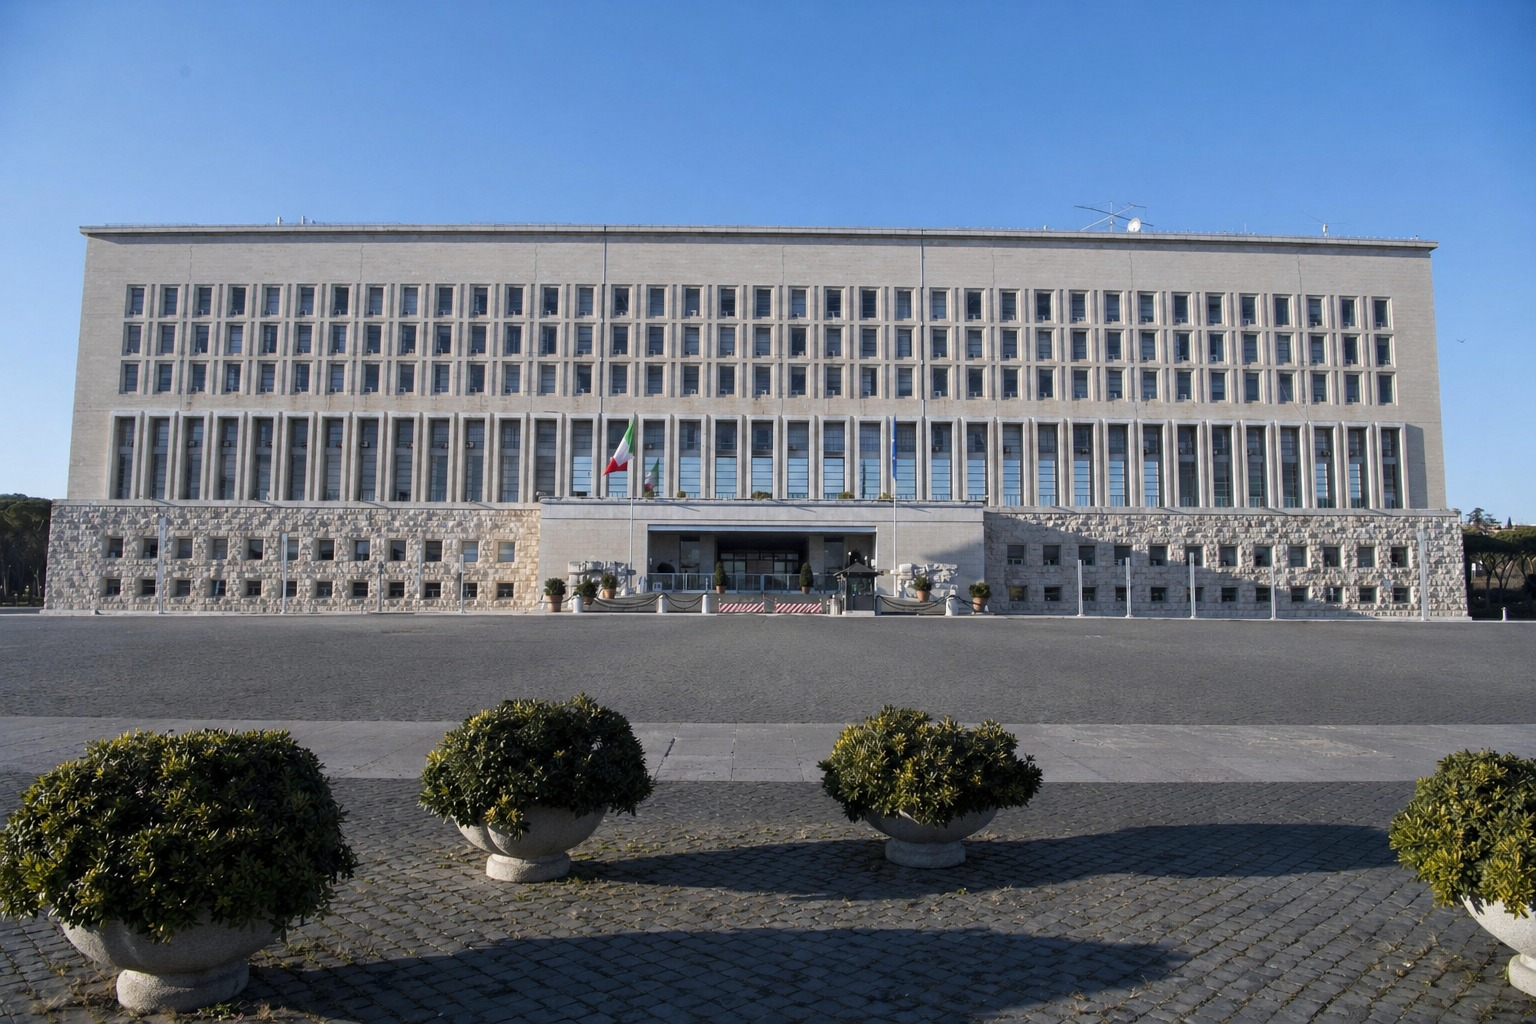
Italy’s Foreign Ministry is defending its website against a cyberattack, checking embassy sites and pushing for EU action to identify attackers. On the morning of October 8, Italy’s Ministry of Foreign Affairs said its website was being attacked. According to the ministry’s own statement, its protection systems have mitigated the attack so far, with no […]
 Pierluigi Paganini
October 08, 2026
MonsterCloud owner Zohar Pinhasi allegedly paid ransomware demands behind clients’ backs, then charged them millions for the supposed recovery. Zohar Pinhasi, the owner of Florida-based MonsterCloud, was charged this week with wire fraud. Federal prosecutors say his clients were scammed twice during the same ransomware crisis. Pinhasi (50) also used the names “Zack Silver” and […]
 Pierluigi Paganini
October 07, 2026
FBI and Secret Service warn FortiBleed, a credential-harvesting campaign against Fortinet firewalls, has compromised 86,644 devices and is locking out admins. The FBI and the U.S. Secret Service issued a joint advisory about FortiBleed, and the headline number alone is worth sitting with: more than 86,644 compromised Fortinet FortiGate devices across 194 countries, according to […]
 Pierluigi Paganini
October 06, 2026
Accenture lost an FBI contract after a missed security patch exposed sensitive employee data, raising serious concerns over operational security. The FBI pulled an Accenture contractor off its account on Monday, and the reason is almost mundane compared to the damage it caused. One update didn’t get installed on time. “The Federal Bureau of Investigation […]