 Pierluigi Paganini
 May 28, 2014
Spotify company is investigating unauthorized access to its systems and internal company data. Android users urge to update the app and change the password. The popular Music streaming service Spotify is the last illustrious victim of hackers. The Swedish company today has issued an advisory to inform its the users of its Android app that it has suffered a […]
 Pierluigi Paganini
May 27, 2014
CYBERPOL the International Cyber-Security Organization (ICSO) is looking into the ID theft of personalities on social websites online that offers very little, if any protection of your identity being used by third parties. This comes after a fake Ban Ki Moon ID profile was discovered by CYBERPOL on LinkedIn on Sunday past. During the examination, […]
 Pierluigi Paganini
May 26, 2014
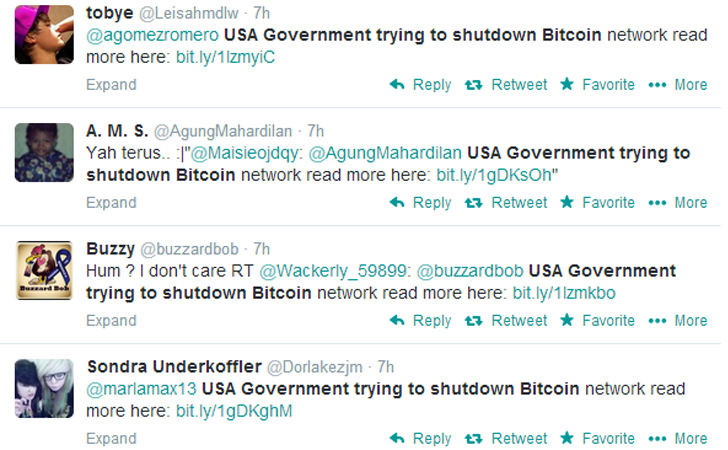
US Government was working on taking down Bitcoin, this is the theme of a new spam campaign via Twitter to spread malicious links. Security Experts at Malwarebytes have discovered a malicious scam spreading malicious links via Twitter. The cyber criminals behind the spam campaign are spreading malware through rogue tweets by a number of bogus Twitter accounts, they […]
 Pierluigi Paganini
May 24, 2014
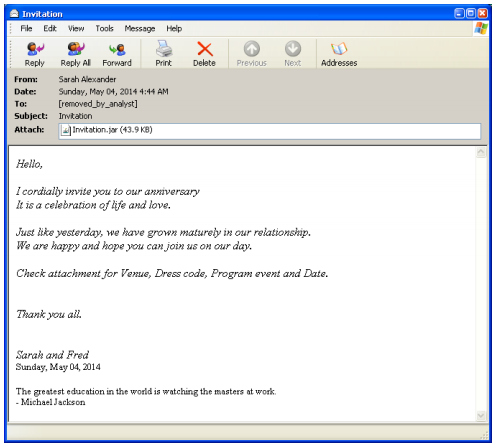
Security Experts at Fidelis Cyber Security firm have recently discovered a new phishing campaign using the Unrecom RAT (remote access trojan). Fidelis Cyber Security firm has recently issued the Fidelis Threat Advisory #1013 to detail a phishing campaign using the Unrecom RAT (remote access trojan). Experts at Fidelis during the last two weeks have observed an increase […]
 Pierluigi Paganini
May 23, 2014
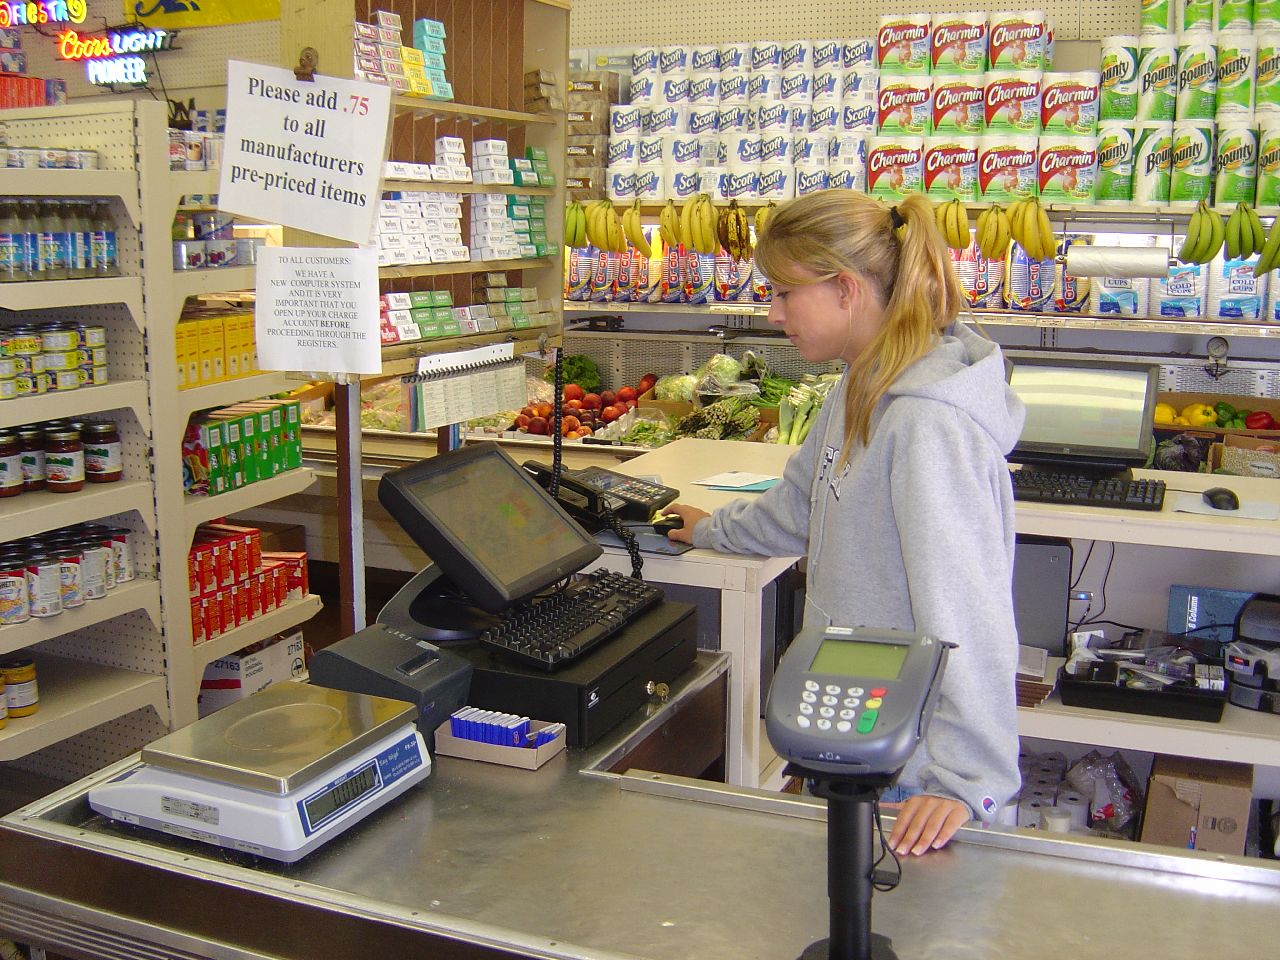
Experts at Intelligence firm IntelCrawler have detected a new botnet dubbed Nemanja composed by compromised POS terminals, accounting systems and grocery management platforms. On March 2014 experts at IntelCrawler have identified Nemanja, one of the biggest botnets based on compromised POS terminals, accounting systems and grocery management platforms. Cyber-threat intelligence company IntelCrawler is one of the companies most active […]
 Pierluigi Paganini
May 23, 2014
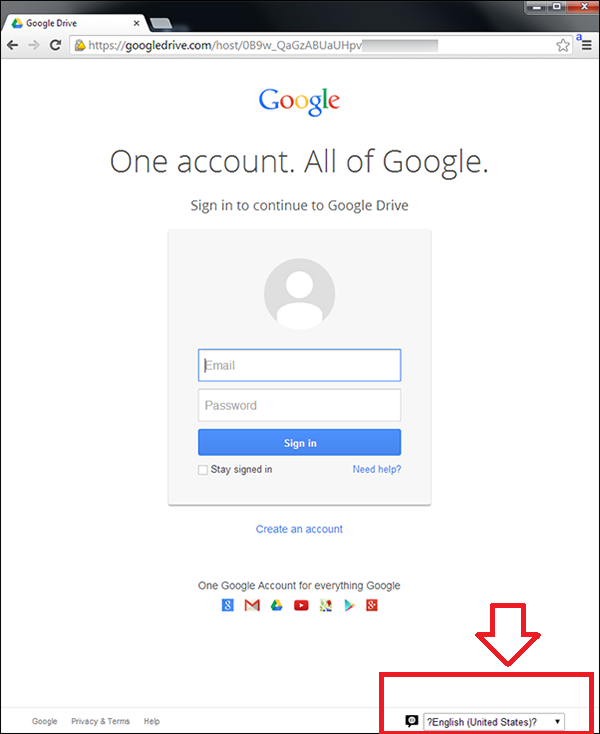
Security experts at Symantec have discovered a new phishing scheme based on Google Drive that is being used by hackers to steal Google Account credentials Phishing scammers are exploring new technique to conduct illicit activities, in the recent weeks we have already discussed on the efficiency to use Google Docs and Google Drive for phishing campaigns. Google Drive popularity […]
 Pierluigi Paganini
May 22, 2014
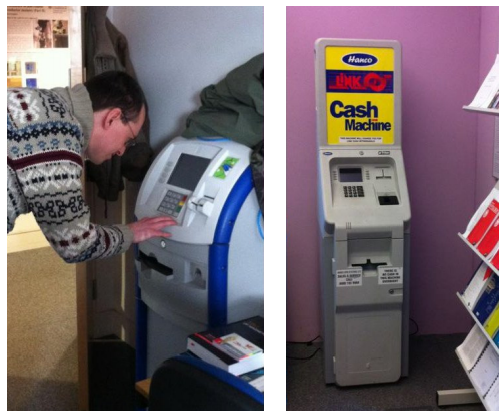
A team of British researchers discovered a series of security flaw, Pre-Play Vulnerability, which allow Chip-and-PIN Payment Card Cloning. The recent incident to the US giant retailers Target and Neiman Marcus has raised the debate on the real level of security of credit/debit cards used by US citizens, in response VISA and Mastercard are accelerating the migration […]
 Pierluigi Paganini
May 18, 2014
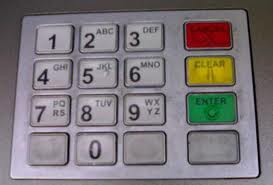
Criminals are exploiting news tactics to steal user’s PIN from ATMs, capturing them over wireless network instead risky tampering of the banking machine. Cyber criminals are adopting even more creative and sophisticated methods to collect user’s personal information, of course banking data is very attractive for hackers that could decide to directly use it for cyber frauds, […]
 Pierluigi Paganini
May 18, 2014
Security Experts at Intercrawler have discovered in the underground a new Exploit-Kit dubbed “Infinity” which might be a new replacement of “Blackhole” Security expert at IntelCrawler, a cyber threat intelligence firm based in Los Angeles, discovered a new private exploit-kit called “Infinity” in the underground. It isn’t a distribution on a large-scale, authors reserved it […]
 Pierluigi Paganini
May 16, 2014
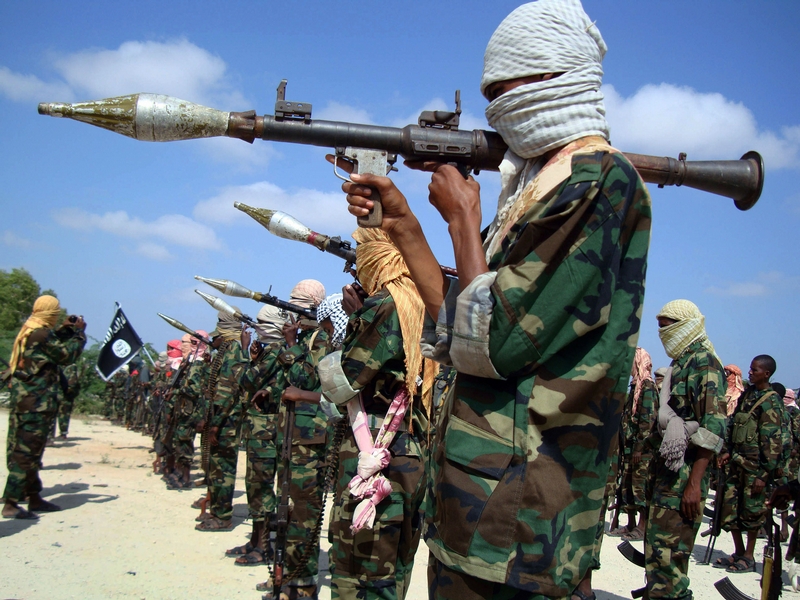
Recorded Future published a report to show that members of Al-Qaeda are developing a series of new encryption software in response to NSA surveillance. The revelation based on the document leaked by Edward Snowden on the NSA surveillance programs have had also a serious impact on the methods of terrorist organizations like Al-Qaeda. The information revealed […]