Pierluigi Paganini
 April 15, 2014
The APWG report 2H2013 seeks to understand trends and their significance by quantifying the scope of the global phishing problem. Last Anti-Phishing Working Group APWG report titled “Global Phishing Survey: Trends and Domain Name Use in 2H2013” confirms that threat of phishing has never been so high, the number of domains registered to conduct this kind of […]
 Pierluigi Paganini
April 14, 2014
Raoul Chiesa gives us his view on the current cyber threat landscape, from Snowden’s case to the links between cyber crime and state-sponsored hacking. Next week the forth Cybercrime Conference will be held in Rome (http://www.tecnaeditrice.com/eventi/cyber_crime_conference_2014/presentazione), two days in which top experts in the field will analyze high-profile cyber attacks discussing also about legal issues, privacy, and cyber strategies […]
 Pierluigi Paganini
April 10, 2014
According principal security firms, extortion, ransom and blackmail are pillars of illicit activities, cyber criminals are adapting them to the cyber context. Extrotion is becoming a worrying inclination in the cyber criminal ecosystem, the number of targeted attacks that request money in change of a suspension of the hostilities and to give back to the victims […]
 Pierluigi Paganini
April 08, 2014
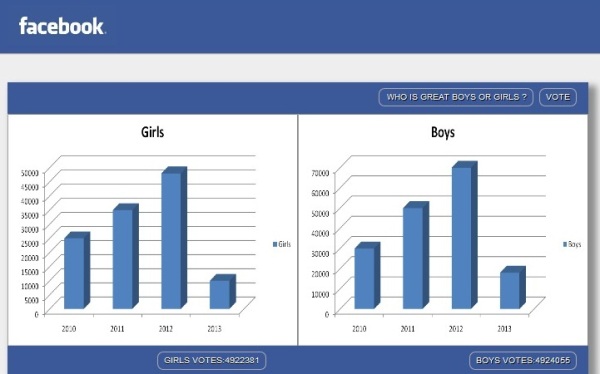
Security experts at Symantec observed a new phishing campaign based on a fake voting application used to steal victim’s credentials. Phishing is a very dangerous threat for Internet users, nearby classic techniques new forms of phishing are exploiting new platforms like mobile and social networks. Phishers continuously improve their techniques to be able to harvest […]
 Pierluigi Paganini
April 07, 2014
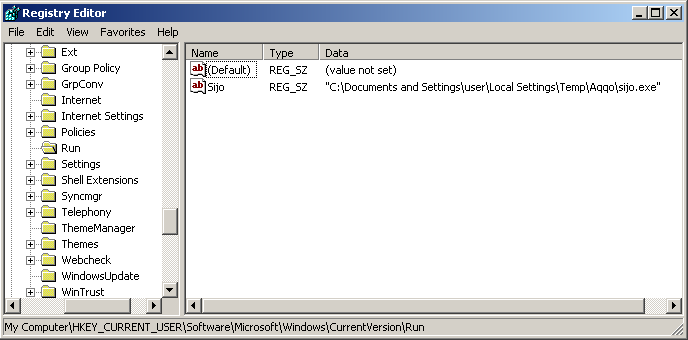
Security researchers at Comodo have detected a new Zeus trojan variant enhanced with digital signature of its source code to avoid detection. The security community is once again menaced by Zeus banking trojan, a new variant of the malicious ZeuS Trojan has been identified by researchers at Comodo AV labs. This instance presents an interesting feature, it is […]
 Pierluigi Paganini
April 05, 2014
Incapsula firm discovered the exploitation of a persistent XSS vulnerability in one of the world most popular website to run a large scale DDoS attack. Recently Cloud-based security service provider Incapsula detected an application layer DDoS attack conducted hijacking a huge volume of traffic to victims website. The website of Incapsula customer was flooded by a DDoS attack, over […]
 Pierluigi Paganini
April 04, 2014
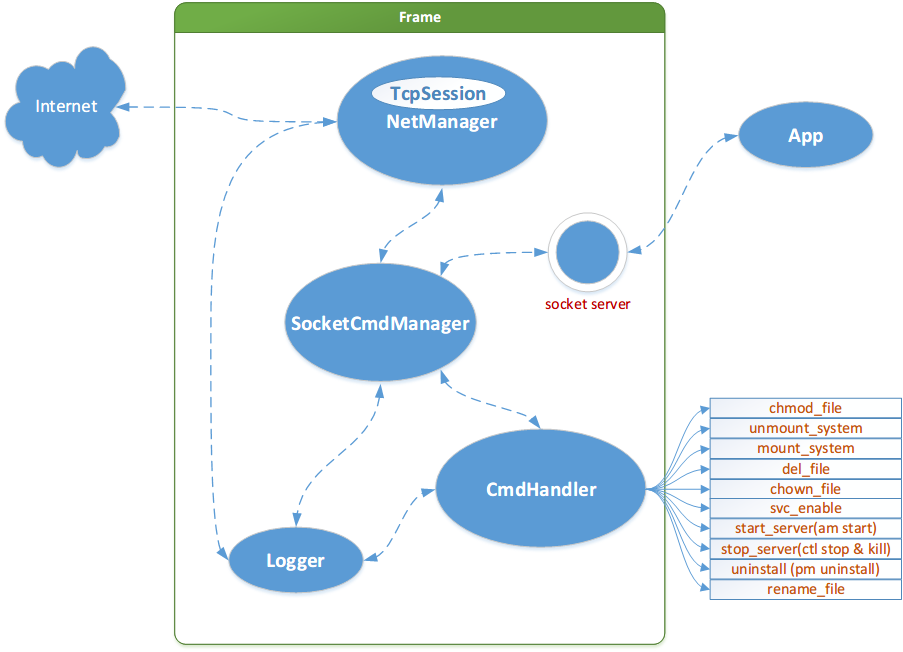
Chinese researchers from “360 Mobile Security” detected Android Oldboot.B malware, until today the most complex bootkit which infected millions of devices. A new sophisticated Android Bootkit has been detected by Chinese Security Researchers from “360 Mobile Security“, its name is Oldboot.B and appears as an evolution of its predecessor Oldboot.A. According the researchers Oldboot.B could be considerable as […]
 Pierluigi Paganini
April 02, 2014
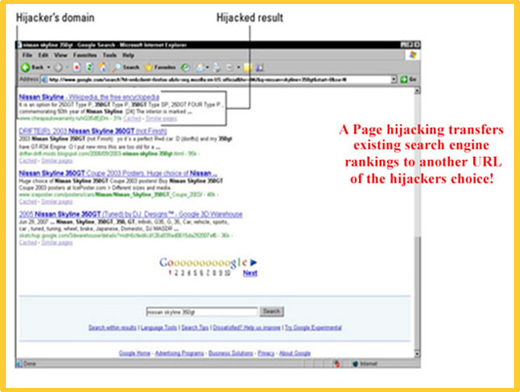
F-Secure has identified a malware dubbed Coremex that takes advantage of plugin functionality provided by browsers to hijack search engine results. Search engine are a strategic component in the successful execution of any attacks, we saw in the past Black SEO campaigns conducted with the primary intent to provide results that help the attackers to […]
 Pierluigi Paganini
March 29, 2014
The Global Threat Intelligence Report (GTIR) addresses the security challenges of organizations globally analyzing 3 billion worldwide attacks occurred in 2013. The NTT Innovation Institute has released the new Global Threat Intelligence Report (GTIR), a document structured to raise awareness of the rapidly evolving global threat landscape. The GTIR was based on threat intelligence and attack data from […]
 Pierluigi Paganini
March 28, 2014
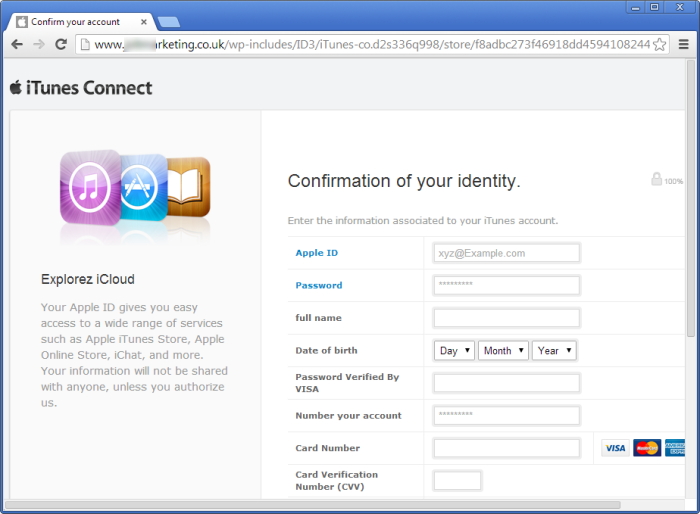
More than 12,000 phishing sites analyzed by Netcraft are hosted on compromised WordPress installations, the websites were used also to serve malicious code. Netcraft internet services company published a statistic which shows that nearly 12,000 WordPress instances were compromised in February, the attackers used the popular CMS to conduct phishing campaigns against targeted family of users, […]