 Pierluigi Paganini
 September 07, 2026
StyleSmuggler Magento zero-day is under active attack, letting unauthenticated attackers execute code and install backdoors on stores that may already be patched. A new zero-day flaw, dubbed StyleSmuggler, in Magento and Adobe Commerce is under active attack, giving unauthenticated attackers a path to run code on vulnerable online stores. Sansec researchers say it affects current […]
 Pierluigi Paganini
September 07, 2026
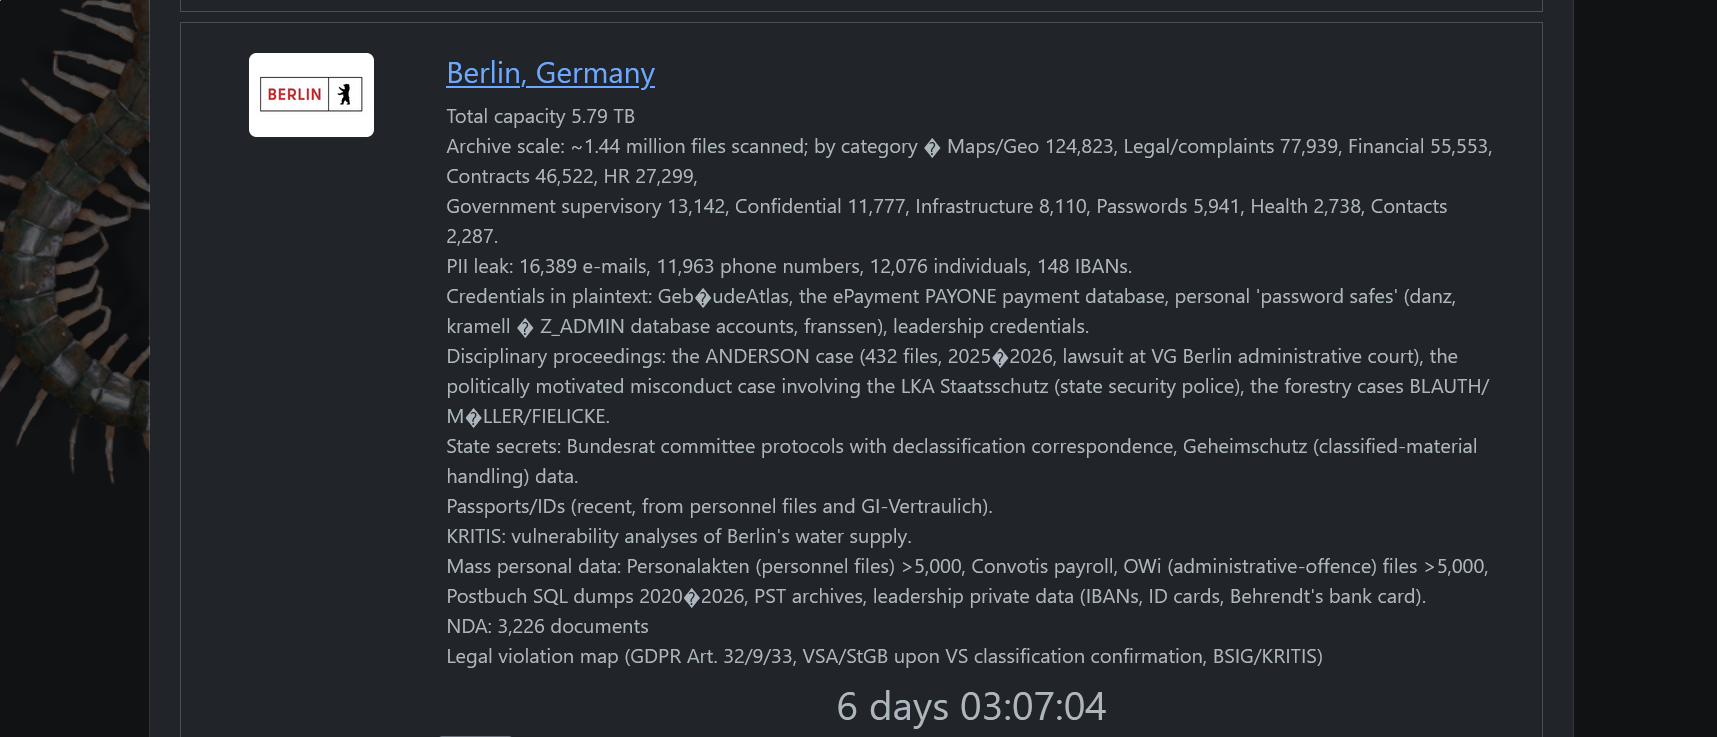
Berlin refused a 30 Bitcoin ransom, leading hackers to leak 6TB of sensitive state administration and national defense data on the dark web. When a ransomware gang dumps nearly six terabytes of state administration files onto the dark web, ignoring them does not make the problem go away. The Rhysida ransomware group recently carried out […]
 Pierluigi Paganini
September 06, 2026
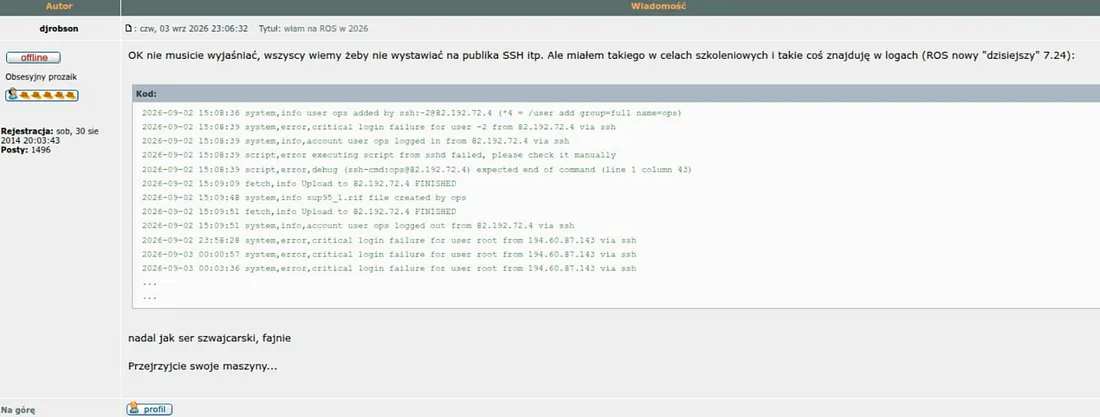
MikroTik RouterOS SSH zero-day (MikroTrick chain) under active exploitation since Sept 2. Patch to 7.24.2, 7.23.5, or 6.49.21 immediately and check logs. Anyone running a MikroTik router with SSH exposed to the internet should treat it as compromised until proven otherwise. The popular cybersecurity expert Costin Raiu published a detailed technical breakdown of the active […]
 Pierluigi Paganini
September 06, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Hackers Steal Claude Login Sessions With Infostealer Malware to Hijack Accounts Fire Ant Evolves: From Hypervisors to Trusted Infrastructure Gryxa: The AI-Built Toolkit That Watches How You Remove It ValleyRAT masquerading as adware […]
 Pierluigi Paganini
September 06, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. PaperCut Flaws Exploited in Attacks on U.S. and European Schools Broadcom Patches Critical VMware Workstation and Fusion […]
 Pierluigi Paganini
September 05, 2026
Attackers are exploiting two new PaperCut flaws to steal credentials and gain privileged access in education-sector attacks across the U.S. and Europe. Attackers are exploiting two recelty disclosed PaperCut flaws, CVE-2026-81578 and CVE-2026-82078, in attacks targeting schools and other education organizations in the U.S. and Europe, as reported by TheHackerNews. Arctic Wolf researchers observed threat […]
 Pierluigi Paganini
September 04, 2026
Manchester Airports Group (MAG) data allegedly leaked by FulcrumSec exposes emails and phone numbers of 8.8 million people. Manchester Airports Group, which operates Manchester, London Stansted and East Midlands airports, has confirmed a data breach involving customer information held in a third-party database. The company says airport operations, passenger safety and aviation security were not […]
 Pierluigi Paganini
September 04, 2026
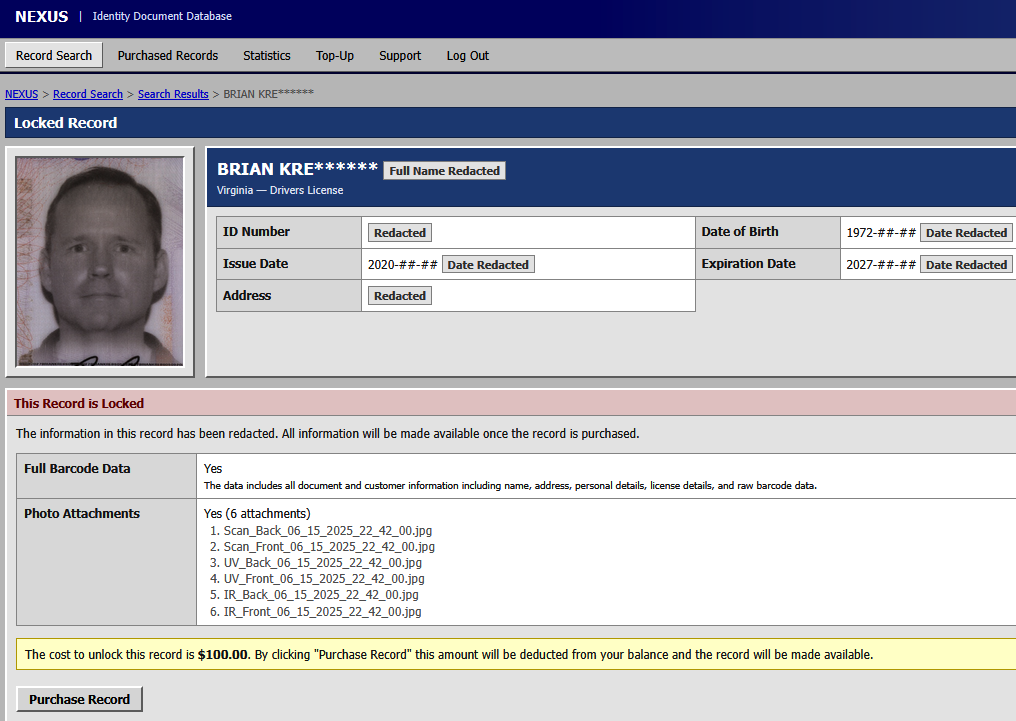
FBI probes suspected breach at IDScan.net after dark web service Nexus offered 153M+ US and Canadian driver’s license scans. A dark web identity theft service called Nexus appeared on September 1, 2026, offering searchable access to more than 153 million scanned driver’s licenses belonging to people in the United States and Canada. The FBI’s New […]
 Pierluigi Paganini
September 03, 2026
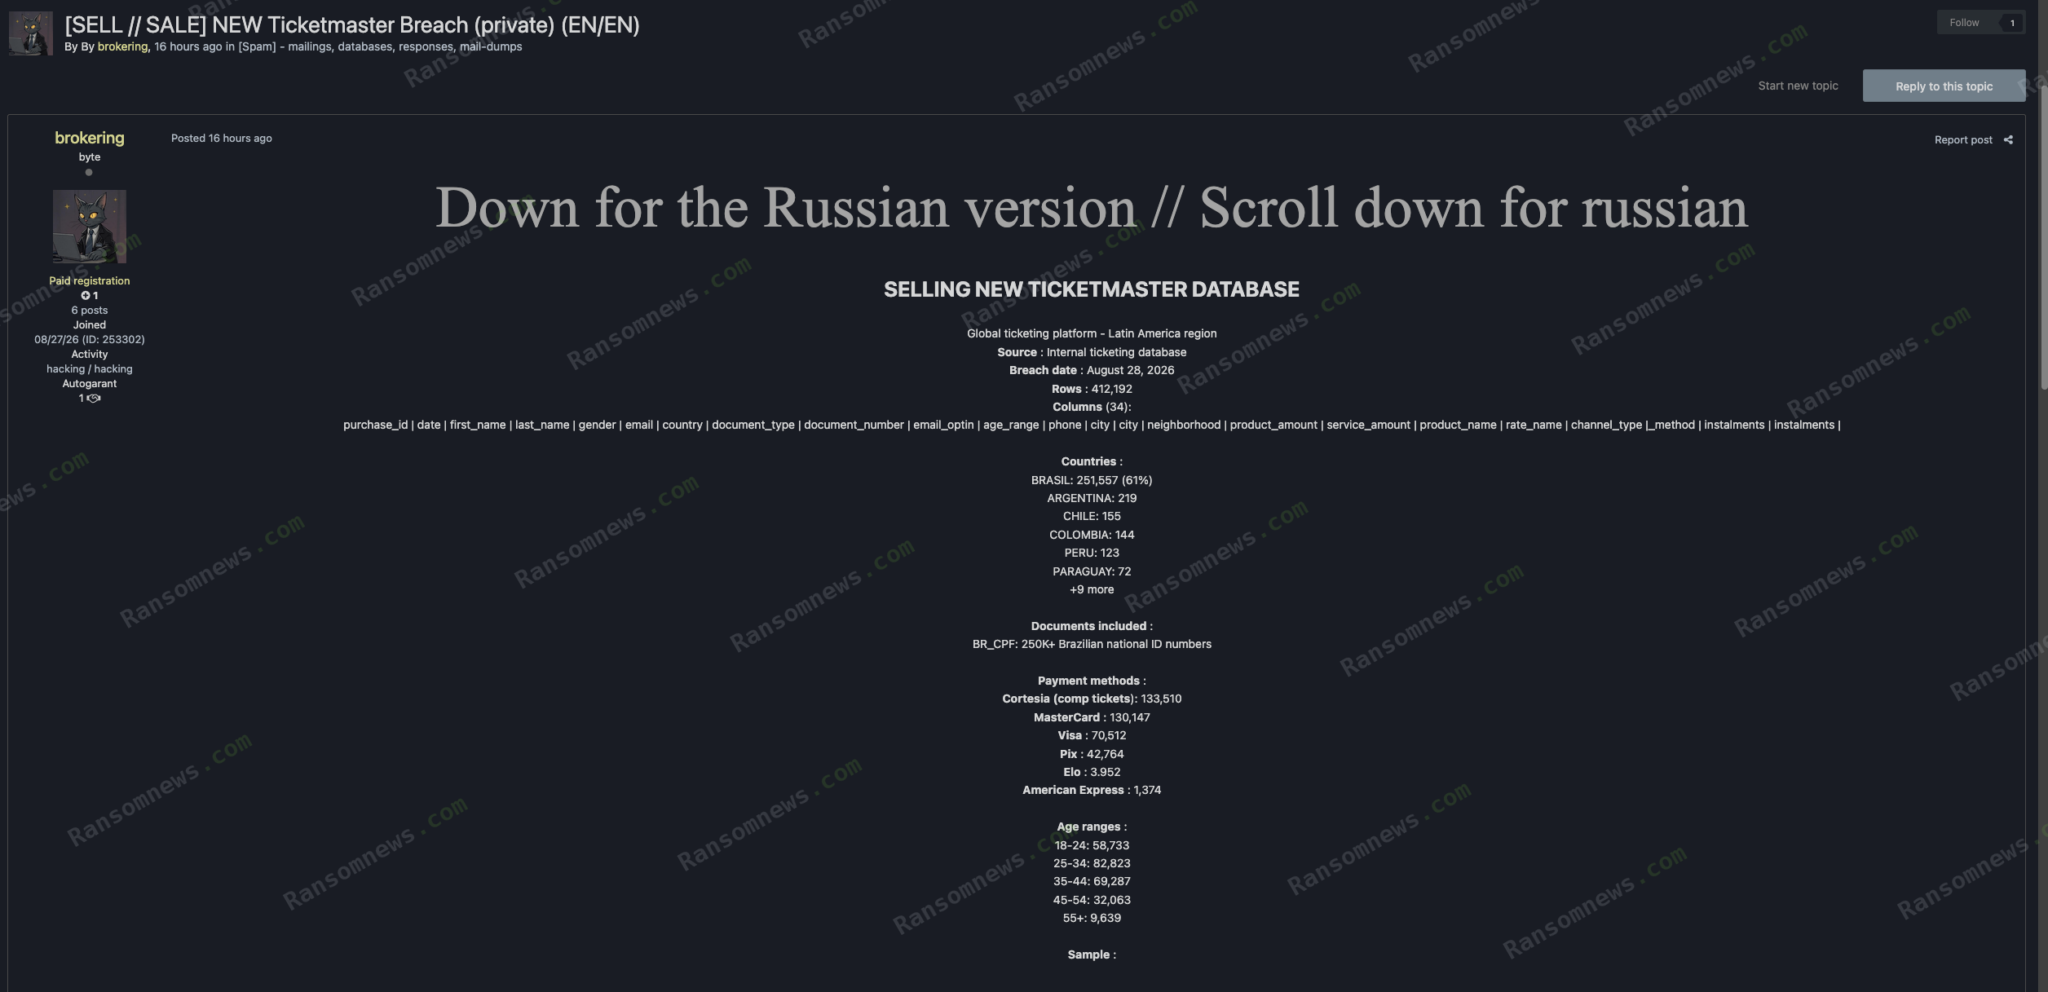
412,000 The Town 2025 festival buyer records are being sold for $10,000, with Brazil’s data openly marketed for bank fraud, loans and SIM registration. A seller on a Russian-language data-trading forum listed what they’re calling a Ticketmaster database on September 2, claiming over 412,000 Latin American purchase records with a heavy concentration of Brazilian data. […]
 Pierluigi Paganini
September 01, 2026
Aesto Health suffered a breach exposing personal and health data of more than 9.5 million people after attackers accessed its AWS infrastructure. Aesto Health, a U.S. healthcare technology company, disclosed a data breach that exposed personal and health information belonging to more than 9.5 million people. The company discovered the incident on December 18, 2025, […]