 Pierluigi Paganini
 April 17, 2021
SolarWinds supply chain attack also impacted six European Union institutions, European Commissioner for Budget and Administration confirmed. European Commissioner for Budget and Administration Johannes Hahn confirmed the hack of some EU agencies as result of the SolarWinds supply chain attack in a response to a question filed by an EU Parliament member in February 2021. […]
 Pierluigi Paganini
April 16, 2021
Cybersecurity provider Juniper Networks addressed a critical vulnerability that could be exploited by attackers to remotely hijack or disrupt vulnerable devices. Cybersecurity vendor Juniper Networks addressed a critical vulnerability in Junos OS, tracked as CVE-2021-0254, that could allow an attacker to remotely hijack or disrupt affected devices. This flaw stems from the improper buffer size […]
 Pierluigi Paganini
April 16, 2021
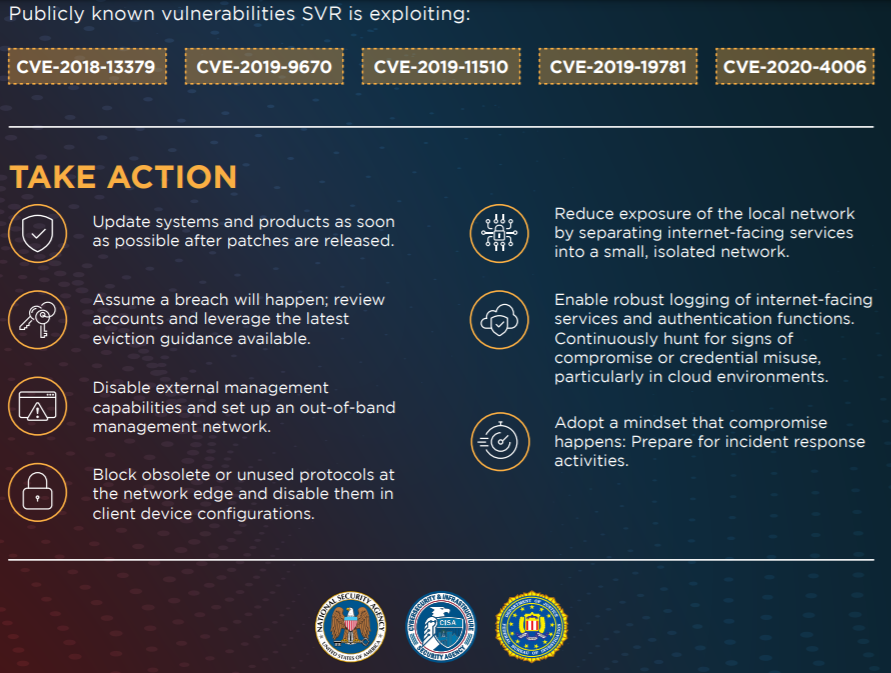
The US government warned that Russian cyber espionage group SVR is exploiting five known vulnerabilities in enterprise infrastructure products. The U.S. National Security Agency (NSA), the Cybersecurity and Infrastructure Security Agency (CISA), and the Federal Bureau of Investigation (FBI) have published a joint advisory that warns that Russia-linked APT group SVR (aka APT29, Cozy Bear, and The Dukes). […]
 Pierluigi Paganini
April 15, 2021
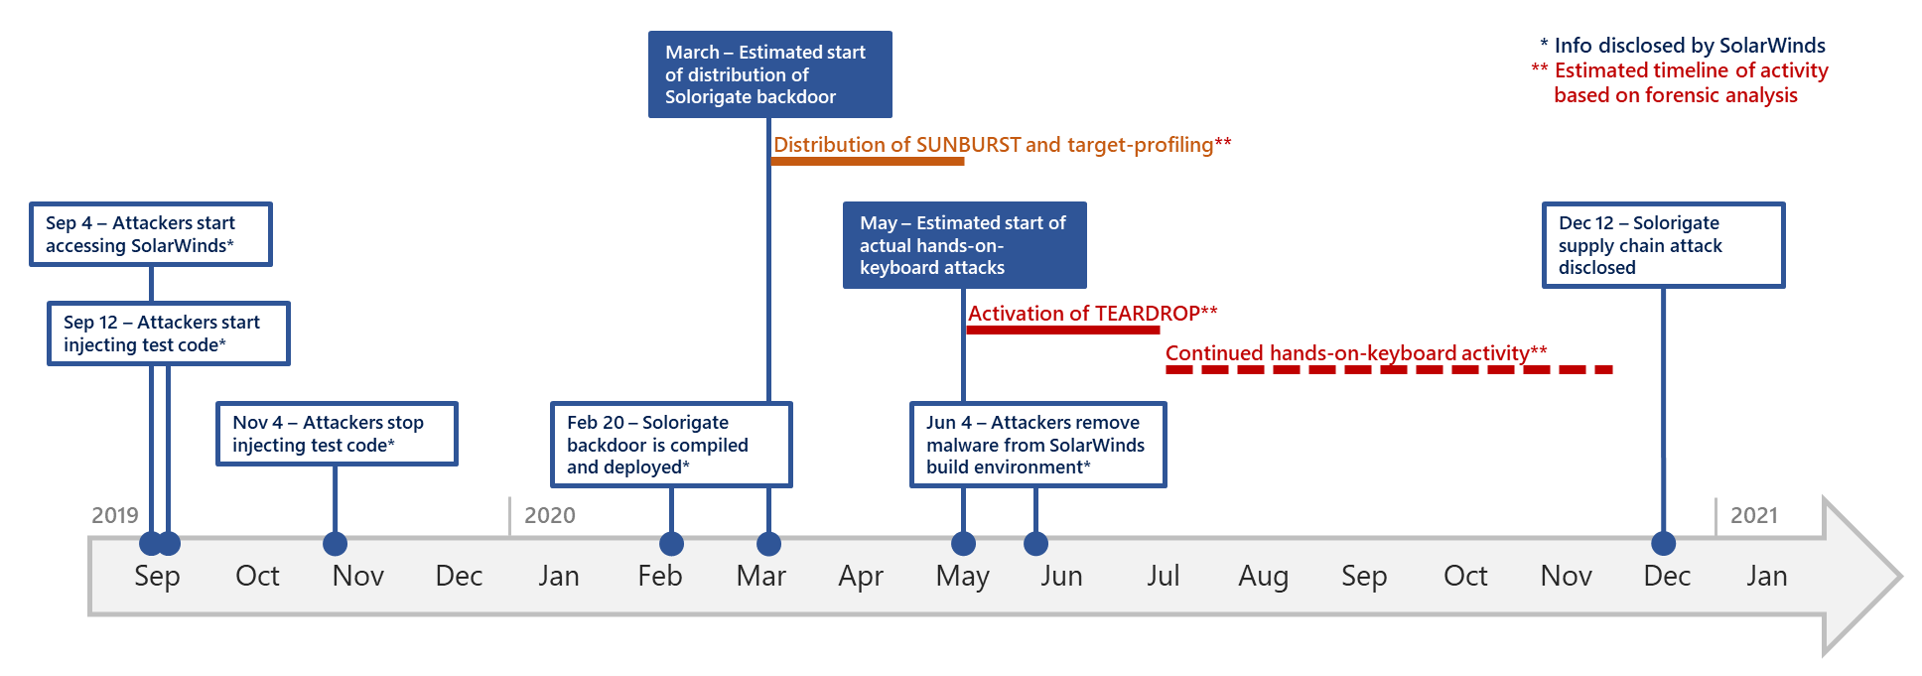
The U.S. and UK attributed with “high confidence” the recently disclosed supply chain attack on SolarWinds to Russia’s Foreign Intelligence Service (SVR). The U.S. and U.K. attributed with “high confidence” the supply chain attack on SolarWinds to operatives working for Russia’s Foreign Intelligence Service (SVR) (aka APT29, Cozy Bear, and The Dukes). The UK, US […]
 Pierluigi Paganini
April 15, 2021
April 2021 Security Patch Day includes 14 new security notes and 5 updates to previously released notes, one of them fixes a critical issue in SAP Commerce. April 2021 Security Patch Day includes 14 new security notes and 5 updates to previously released ones, among the issues addressed by the software giant there is a […]
 Pierluigi Paganini
April 15, 2021
For the second time in a week, a Chromium zero-day remote code execution exploit code has been released on Twitter, multiple browsers impacted. A new Chromium zero-day remote code execution exploit has been released on Twitter this week, like the previous one that affects current versions of Google Chrome, Microsoft Edge, and likely other Chromium-based browsers. The […]
 Pierluigi Paganini
April 14, 2021
WhatsApp addressed two security vulnerabilities in its app for Android that could have been exploited to remotely hack the victim’s device. WhatsApp recently addressed two security vulnerabilities in its app for Android that could have been exploited by remote attackers to execute malicious code on a target device and potentially eavesdrop on communications. The vulnerabilities […]
 Pierluigi Paganini
April 14, 2021
FireEye published its M-Trend 2021 report based on the data collected during the investigation, 650 new threat groups were tracked in 2020 FireEye published its annual report, titled M-Trend 2021, which is based on the data collected during the investigation on security incidents it managed. Most of the incidents investigated by Mandiant (59%) in 2020 […]
 Pierluigi Paganini
April 14, 2021
FBI log into web shells that hackers installed on Microsoft Exchange email servers across the US and removed the malicious code used by threat actors. A US judge granted the FBI the power to log into web shells that were injected by nation-state hackers on Microsoft Exchange servers across the US and remove the malware, […]
 Pierluigi Paganini
April 14, 2021
The Swedish Sports Confederation organization was compromised in 2017-18 by hackers working for Russian military intelligence, officials said. The Swedish Sports Confederation is the umbrella organisation of the Swedish sports movement, it was hacked by Russian military intelligence in a campaign conducted between December 2017 and May 2018, officials said. In the same period, Russia-linked […]


Artificial Intelligence / September 19, 2026