 Pierluigi Paganini
 March 01, 2017
Zscaler has fixed persistent XSS vulnerabilities affecting Zscaler Cloud management software that allow logged attackers to hack coworkers. Serious cross-site scripting (XSS) flaws in the Zscaler Cloud management software could be exploited by attackers to inject malicious HTML and JavaScript into the browsers of other users who visit the portal. In order to exploit the flaws, the attacker […]
 Pierluigi Paganini
March 01, 2017
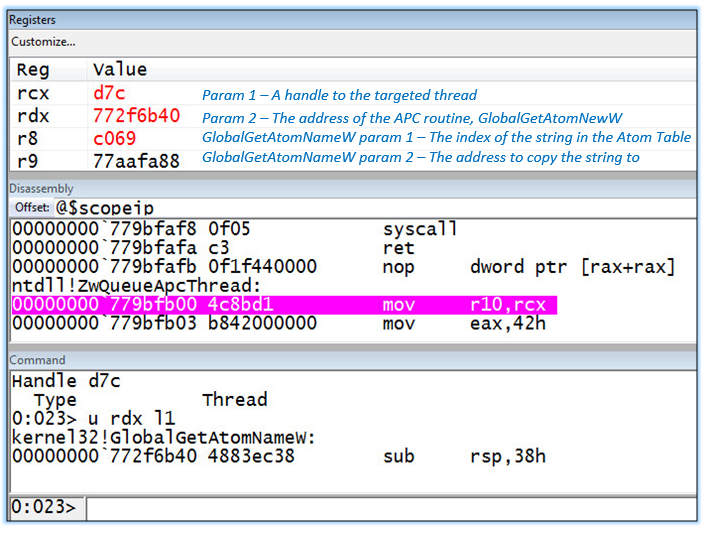
Malware author are using Dridex v4 in the wild, an improved version of the Trojan that includes a new injection method known as AtomBombing. According to researchers with IBM X-Force, vxers have improved the Dridex banking Trojan adding a new injection method for evading detection, the technique is known as AtomBombing. The researchers have spotted […]
 Pierluigi Paganini
February 28, 2017
The Singaporean Defence Ministry confirmed that threat actors have breached government systems stealing personal information of its employees. On Tuesday, the Defence Ministry confirmed that unknown hackers have breached government system and have stolen personal information belonging about 850 Singapore national servicemen and employees. Data accessed by hackers includes telephone numbers, dates of birth, and national […]
 Pierluigi Paganini
February 28, 2017
A flaw in ESET Endpoint Antivirus is exploitable to get remote root execution on Apple Mac systems via Man-In-The-Middle (MiTM) attacks. According to the security advisory published by Google Security Team’s Jason Geffner and Jan Bee on Seclists, it is possible to get remote root execution on Apple Mac systems via Man-In-The-Middle (MiTM) attacks. The attackers […]
 Pierluigi Paganini
February 27, 2017
The Necurs botnet is evolving and recently the experts at BitSight’s Anubis Labs discovered that it was improved to launch DDoS attacks. The Necurs botnet continues to evolve and recently it was used by crooks not only to spread the dreaded Locky ransomware but he was improved to launch DDoS attacks. According to the researchers BitSight’s […]
 Pierluigi Paganini
February 27, 2017
EHR data are precious commodities in the cyber criminal underground because of the lack of cyber security of healthcare industry. Electronic health record databases are becoming the most precious commodities in the cyber criminal underground. The healthcare sector has been the industry with the highest number of data breaches in 2015 when a total of […]
 Pierluigi Paganini
February 26, 2017
The tour company Roberts Hawaii is warning its customers about a security breach that may affect people who purchased tours and other services on its website. Did you visit the Hawaii in last year? The tour company Roberts Hawaii is warning its customers about a data breach that may affect people who purchased tours from July […]
 Pierluigi Paganini
February 26, 2017
A study commissioned by Siemens revealed that US oil and gas industry is unprepared to mitigate cybersecurity risks in operational technology environments. A new study commissioned by the engineering firm Siemens revealed that oil and gas industry in the United States is largely unprepared to mitigate cybersecurity risks in operational technology (OT) environments. The survey was conducted […]
 Pierluigi Paganini
February 25, 2017
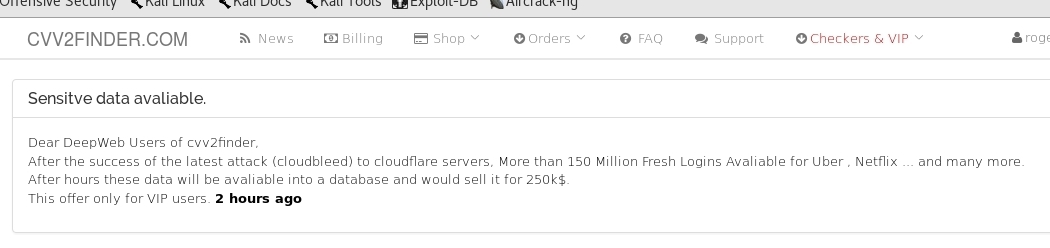
The carder forum CVV2Finder claims to have more than 150 million logins from several popular services, including Netflix and Uber. The carder forum CVV2Finder claims to have more than 150 million logins, from several popular services, including Netflix and Uber. The operators in the forum are offering the precious commodity to the VIP members. According to […]
 Pierluigi Paganini
February 24, 2017
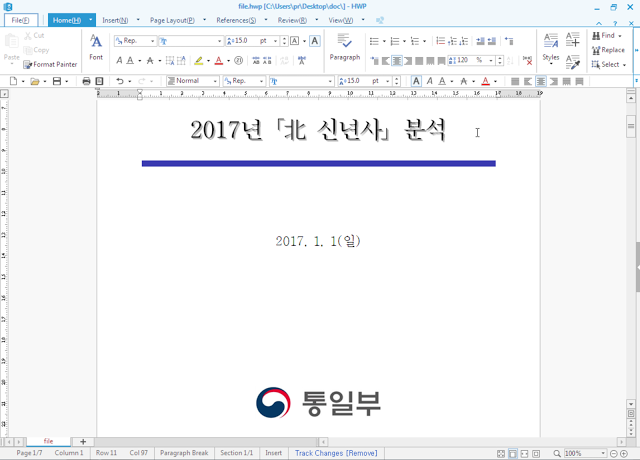
South Korea is once against under attack, alleged nation-state hackers have launched a sophisticated cyber espionage campaign on organizations in the public sector. According to the experts at Cisco Talos, the cyber espionage campaign was active between November 2016 and January 2017 and leveraged on vulnerabilities in a Korean language word processing program (Hangul Word […]