 Pierluigi Paganini
 February 24, 2017
Cloudflare was leaking a wide range of sensitive information, including authentication cookies and login credentials, the flaw was dubbed Cloudbleed. The notorious Google security researcher, Tavis Ormandy, recently made and astonishing discovery, Cloudflare was leaking a wide range of sensitive information, including authentication cookies and login credentials, the flaw was dubbed Cloudbleed. “On February 17th 2017, […]
 Pierluigi Paganini
February 24, 2017
A security researcher discovered an Out-of-band resource load flaw in Google’s servers that allowed him to perform a DDoS attack on remote hosts. Young security researcher, Luka Sikic from Croatia found a serious vulnerability in Google. He was able to servers of the IT giant to perform a DDoS attack on remote hosts. Out-of-band resource load (classified […]
 Pierluigi Paganini
February 23, 2017
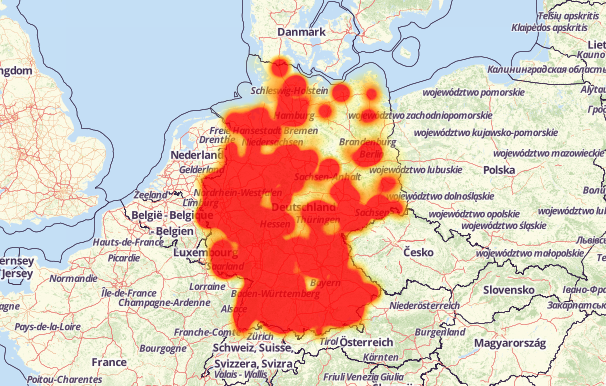
The prosecutor’s office in Cologne and the Federal Criminal Police Office have arrested the alleged mastermind of the MIRAI attack on Deutsche Telekom The agents at the UK National Crime Agency (NCA) have a man that is suspected to be involved with the massive attack on Deutsche Telekom that affected more than 900k routers in […]
 Pierluigi Paganini
February 23, 2017
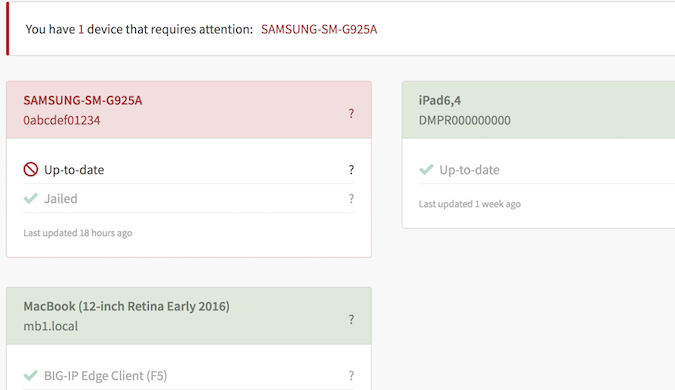
Netflix has released the Stethoscope open source web application that provides recommendations for securing their devices. Netflix has released Stethoscope, an open source web application that provides recommendations for securing computers, smartphones, and tablets. Netflix intends to follow a “user focused security” approach that aims to provide employees information to improve their security posture, rather than […]
 Pierluigi Paganini
February 23, 2017
A team of Israeli researchers has devised a new technique to exfiltrate data from a machine by using a malware that controls hard drive LEDs. Across the years, numerous studies demonstrated that it is possible to exfiltrate data from air-gapped networks in various ways and security experts warned to cover our webcam to avoid being spied by […]
 Pierluigi Paganini
February 22, 2017
Security expert discovered a new 11-year old privilege escalation vulnerability, tracked as CVE-2017-6074, in the Linux kernel. A new privilege escalation vulnerability, tracked as CVE-2017-6074, has been discovered in the Linux kernel and the astonishing new is that it is an 11-year old flaw. The local privilege-escalation vulnerability, discovered by security researcher Andrey Konovalov, affects all the major […]
 Pierluigi Paganini
February 22, 2017
For the second time in a few months Montenegro suffered massive and prolonged cyberattacks against government and media websites. According to the Balkan Insight, attackers have launched a renewed attack on the Montenegrin government and media. The last wave of cyber attacks started on February 15 and lasted several days, according to the government experts it was […]
 Pierluigi Paganini
February 22, 2017
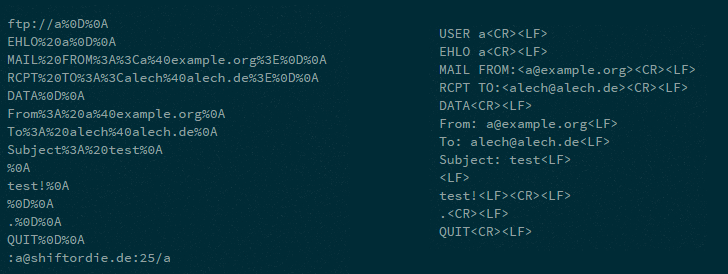
The two programming languages, Java and Python, are affected by serious FTP Injection flaws that can be exploited by hackers to bypass any firewall. Attackers can trick Java and Python applications to execute rogue FTP commands that would open ports in firewalls The unpatched flaws reside in the way the two programming languages handle File Transfer […]
 Pierluigi Paganini
February 21, 2017
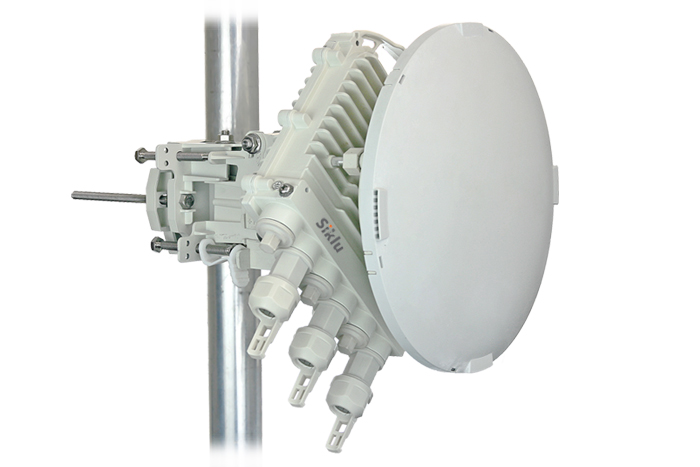
The security researcher Ian Ling discovered a serious remote command execution (RCE) flaw in the Siklu EtherHaul Radios devices. Security expert Ian Ling has discovered a severe remote command execution (RCE) vulnerability in the Siklu’s EtherHaul wireless point-to-point radios. The flaw could be exploited by remote unauthenticated attackers to execute commands and retrieve sensitive information, including […]
 Pierluigi Paganini
February 21, 2017
Security firm CyberX uncovered the Operation Bugdrop, a cyber espionage campaign that mostly targeted Ukrainian organizations. Researchers at Security firm CyberX have discovered a cyber espionage campaign that siphoned more than 600 gigabytes from about 70 targets in several industries, including critical infrastructure and news media. The list of targets includes: A company that designs […]