


 Pierluigi Paganini
 July 12, 2014
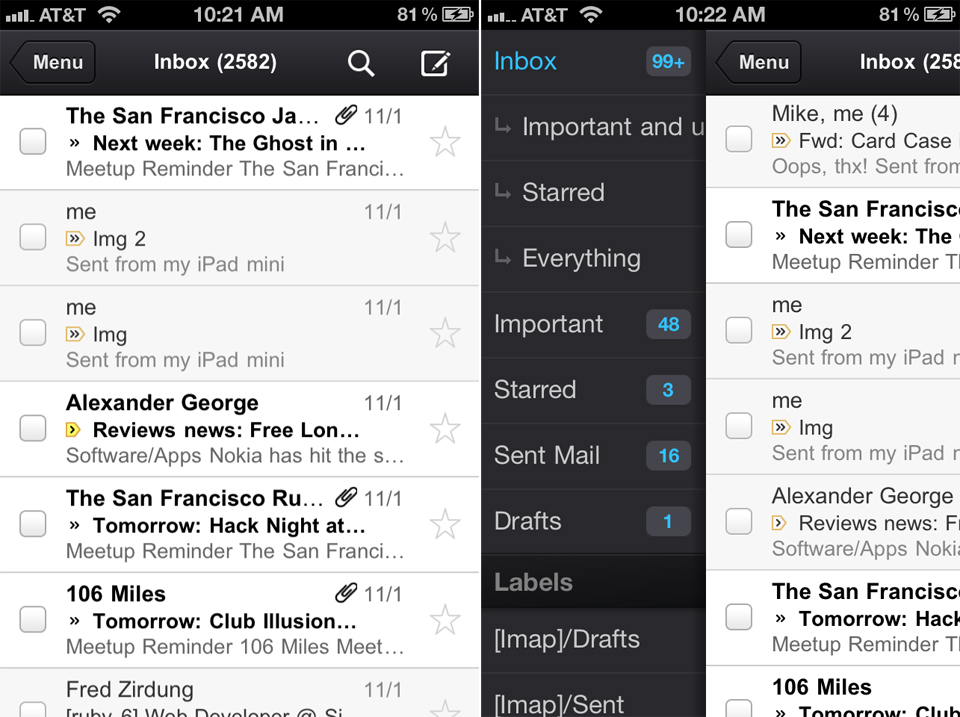
Security experts at Lacoon discovered a vulnerability in the Gmail iOS app which enables a bad actor to perform a Man-in-the-Middle. Google Gmail application for iOS is exposed to risks of Man-in-the-Middle (MitM) attacks which allow bad actors to monitor encrypted email communications. An expert at mobile security firm Lacoon has discovered that version of Gmail […]
 Pierluigi Paganini
July 11, 2014
The New York Times revealed that in March Chinese hackers hacked systems at Office of Personnel Management stealing files of thousands of Federal employees According to the New York Times, senior American officials revealed that a group of Chinese hackers violated the computer networks of the United States government agency in March. The Chinese bad actors hacked US government systems […]
 Pierluigi Paganini
July 10, 2014
Analysis of the compliance measures to be put in place in order to face data protection issues affecting the Internet of Things. The Internet of Things is expected to lead to 50 billion connected devices by 2020 collecting and exchanging personal data about their users, their lives, their preferences and tastes. This will lead not […]
 Pierluigi Paganini
July 09, 2014
Context Information Security firm has discovered a security vulnerability in LIFX smart LED light bulbs that can be remotely controlled by mobile devices. Researchers at Context Information Security have discovered a security flaw in a WiFi enabled, smart LED light LIFX bulb that can be remotely controlled via mobile devices. The discovery was the result of a […]
 Pierluigi Paganini
July 08, 2014
The Director of the Pentagon’s Missile Defense Agency reported to the Congress that missile defenses of the US military are vulnerable to cyber attacks. The Director of the Pentagon’s Missile Defense Agency reported to the Congress last week that missile defenses deployed by the US Army are vulnerable to cyber attacks. Security experts are aware that every […]
 Pierluigi Paganini
July 08, 2014
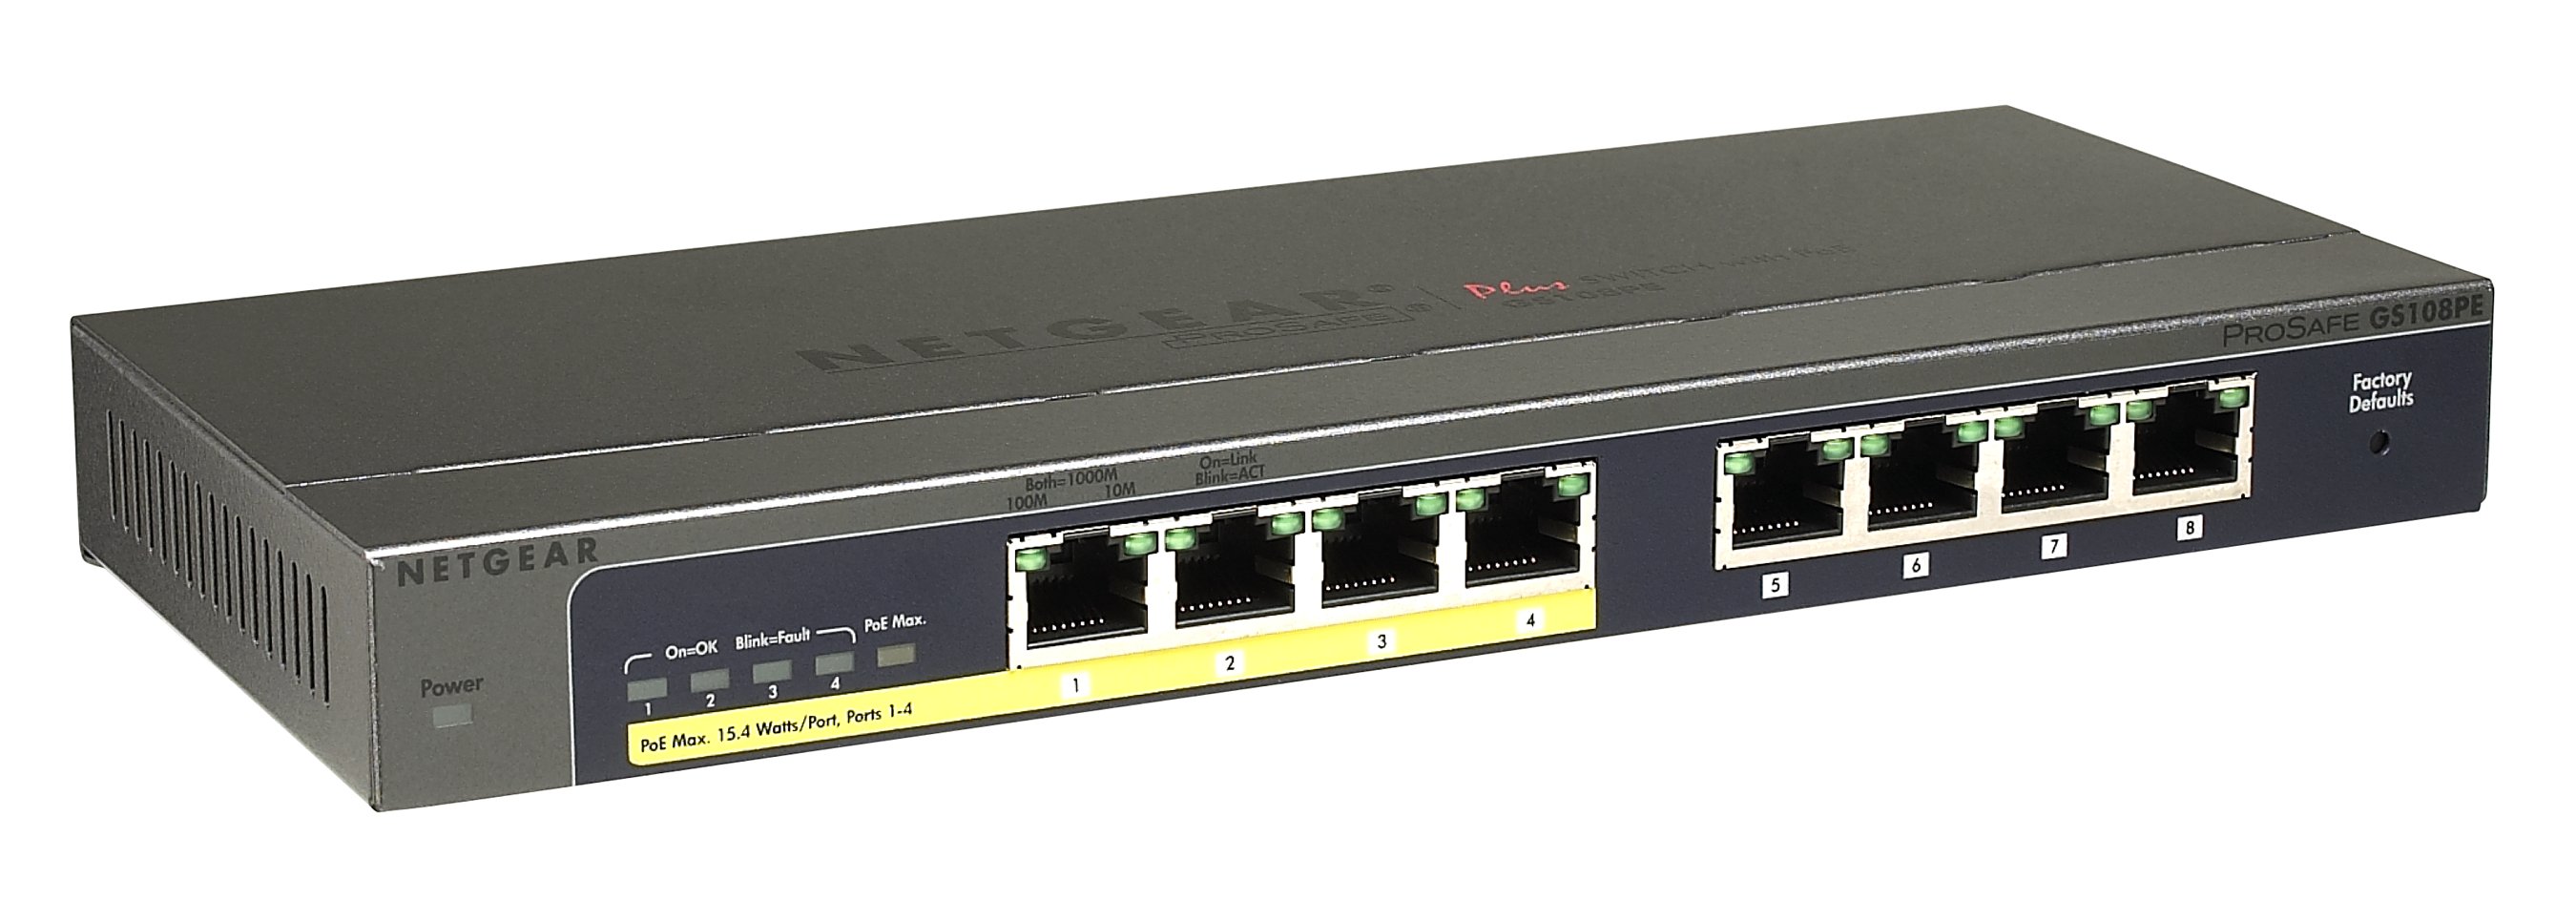
A vulnerability analyst at CERT/CC reported a security issue in Netgear GS108PE Prosafe Plus Switch which contains hard-coded login credentials. The CERT/CC has recently issued an alert for the presence of hard-coded login credentials in the Netgear GS108PE Prosafe Plus Switch (Vulnerability Note VU#143740). An attacker could exploit the security issue in the Netgear GS108PE Prosafe Plus Switch […]
 Pierluigi Paganini
July 07, 2014
Cisco’s Threat Research Analysis and Communications (TRAC) uncovered an extremely targeted spear phish attack on high-profit companies in Europe. A new APT has been discovered by CISCO targeting high-profit companies in Europe, including businesses working in banking, oil and entertainment industries. The attackers adopted as attack vector the email in a spear phishing campaign. According to the alert […]
 Pierluigi Paganini
July 06, 2014
Security experts Alexander Volynkin and Michael McCord will present at the next Black Hat 2014 a method to break Tor network anonymity with just USD 3000. Is the popular Tor network broken? In the recent months, after the Showden’s revelations, many security experts have started to investigate on the possibility that the US intelligence, and […]
 Pierluigi Paganini
July 04, 2014
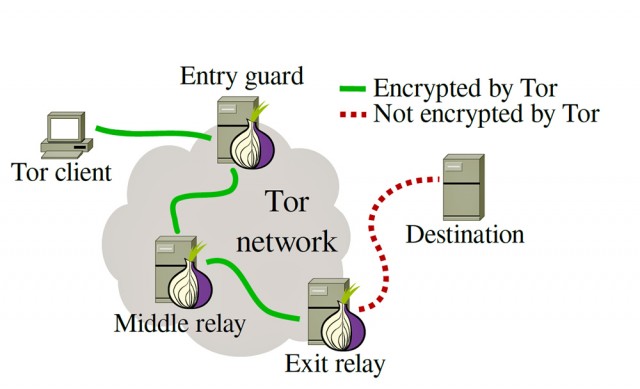
The German broadcaster ARD published a report that reveals that NSA XKeyscore has targeted two Germany-based Tor Directory Authority servers. The NSA surveillance program XKeyscore, according to a report published by German public broadcaster ARD, two Germany-based Tor Directory Authority servers have been targeted by the US intelligence. According to the report, the two cases are not isolated, in the past […]
 Pierluigi Paganini
July 03, 2014
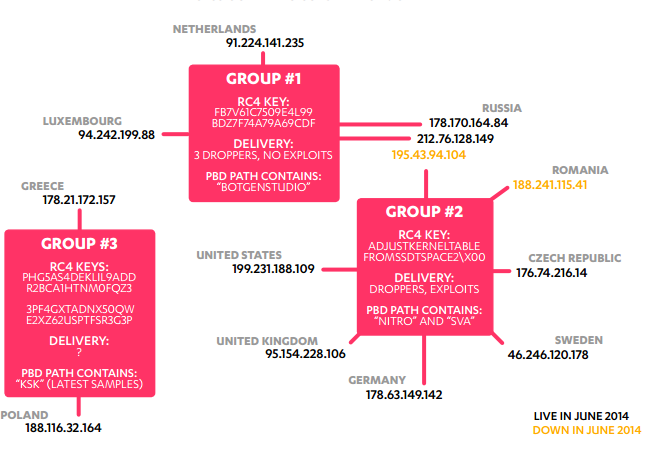
While investigating on MiniDuke malware, experts at F-Secure discovered a surprising link to a new malware, dubbed CosmicDuke, belonging to Cosmu family. Early 2013 experts at Kaspersky Lab and Hungary’s Laboratory of Cryptography and System Security (CrySyS) uncovered a cyber espionage campaign dubbed Miniduke which targeted dozens of computers at government agencies across Europe. The hackers exploited a […]





