


 Pierluigi Paganini
 May 24, 2014
Security experts have discovered three new critical eBay vulnerabilities, the privacy and data of more than 145 million users is still at risk. Just a few days after the disclosure of a major data breach at eBay, in the Internet is circulating the news of three new critical eBay vulnerabilities in the company website. eBay admitted […]
 Pierluigi Paganini
May 22, 2014
A team of British researchers discovered a series of security flaw, Pre-Play Vulnerability, which allow Chip-and-PIN Payment Card Cloning. The recent incident to the US giant retailers Target and Neiman Marcus has raised the debate on the real level of security of credit/debit cards used by US citizens, in response VISA and Mastercard are accelerating the migration […]
 Pierluigi Paganini
May 22, 2014
Zero Day Initiative website has disclosed a new zero-day Internet Explorer 8 vulnerability which was reported to Microsoft four months ago but not yet fixed Microsoft had kept hidden a critical Zero-Day vulnerability in Internet Explorer 8 since October 2013, this is the last disconcerting news that is circulating within the security community. Peter ‘corelanc0d3r’ Van […]
 Pierluigi Paganini
May 21, 2014
The giant eBay suffered a serious data breach which exposed data in its database. Customer information, including personal data and password were violated. The Giant Ebay is victim of data breach, during a cyber attack the hackers violated company database accessing to personal data and user credentials. In response to the incident the company is notifying its customers […]
 Pierluigi Paganini
May 20, 2014
The United States has filed criminal charges against five Chinese military PLA officials for cyber espionage and hacking against several US companies. The United States early this week charged five Chinese military PLA officers and accused them of hacking into computers of American companies. US authorities accused the China’s People’s Liberation Army officers of hacking […]
 Pierluigi Paganini
May 20, 2014
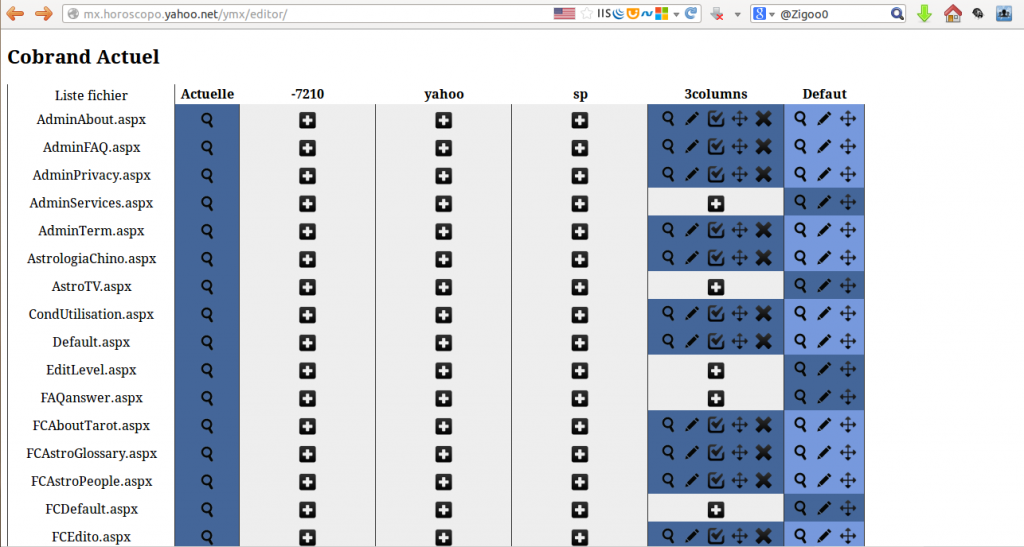
Security researcher Ebrahim Hegazy has identified a remote code injection vulnerability affecting several subdomains of Microsoft, Yahoo, Orange and others. Fortunately, the security Vulnerability has been fixed. While participating in the Yahoo Bug Bounty program, Hegazy has found a “Unauthorized Admin Access” Vulnerability in one of Yahoo domains “mx.horoscopo.yahoo.net.”, that vulnerability led him to find […]
 Pierluigi Paganini
May 19, 2014
The FBI (Federal Bureau of Investigation) has issued a solicitation for malware development confirming the use of malicious code for investigation. The proliferation of malware in the cyber space is not a surprise, according recent reports the number of new malicious code instance is rapidly increasing. State-sponsored hackers and cyber criminals are principally responsible for […]
 Pierluigi Paganini
May 19, 2014
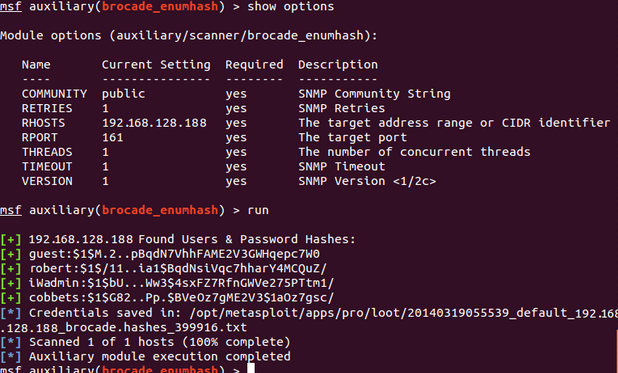
Researchers at Rapid7 disclosed a series of vulnerabilities in many devices that allow data disclosure from the SNMP community string. Researchers at Rapid7 have discovered problems in SNMP on embedded devices which can can cause the exposure of critical information. As explained in the official blog post during the analysis the experts discovered devices which expose information that would […]
 Pierluigi Paganini
May 18, 2014
Criminals are exploiting news tactics to steal user’s PIN from ATMs, capturing them over wireless network instead risky tampering of the banking machine. Cyber criminals are adopting even more creative and sophisticated methods to collect user’s personal information, of course banking data is very attractive for hackers that could decide to directly use it for cyber frauds, […]
 Pierluigi Paganini
May 17, 2014
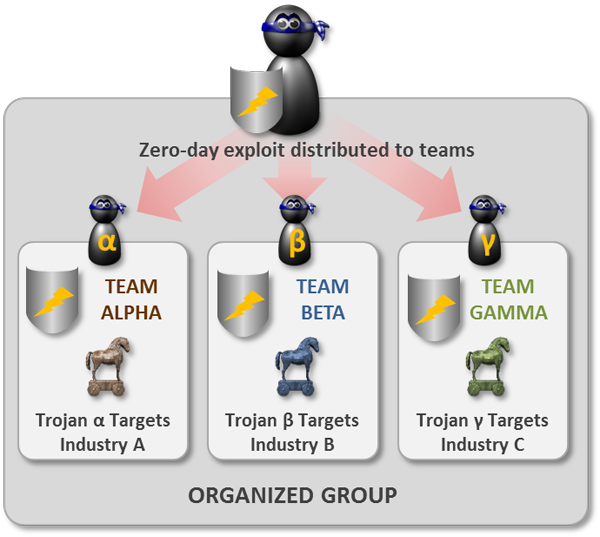
Experts at Symantec have discovered that behind the Elderwood Platform there is a still active group which is providing Zero-Day exploit used recently. Do you remember the Elderwood project? It was September 2012 when Symantec security firm published an analysis that demonstrate the link between a series of cyber attacks against more than 30 companies and the cyber […]







