


 Pierluigi Paganini
 May 06, 2014
Discover how it is possible to apply steganography to hide secret messages in common tweets (or any text) with steg.js-of-the-dump. In the past we have discussed many times on the adoption of steganography to hide messages within images and video, a technique exploited also by authors of malware to hide configuration file and command sent by the C&C […]
 Pierluigi Paganini
May 05, 2014
Technion students Find a security vulnerability in the Internet DNS protocol which allows the attackers to redirect users to a website they control. A significant new security vulnerability has been found in the DNS protocol by a group of Israeli students from the Technion’s Department of Computer Sciences. After the Heartbleed case and the assumptions […]
 Pierluigi Paganini
May 04, 2014
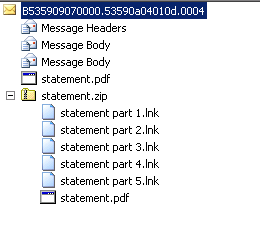
Expert at Trustwave explained the tactics adopted by cyber criminals how to serve malware in phishing attacks exploiting .lnk files. Phil Hay, expert at Trustwave SpiderLab, explained how cyber criminals are using .lnk files to serve malware via email. I have chosen to detail this tactic to demonstrate how much creative is the criminal ecosystem, even if it […]
 Pierluigi Paganini
May 03, 2014
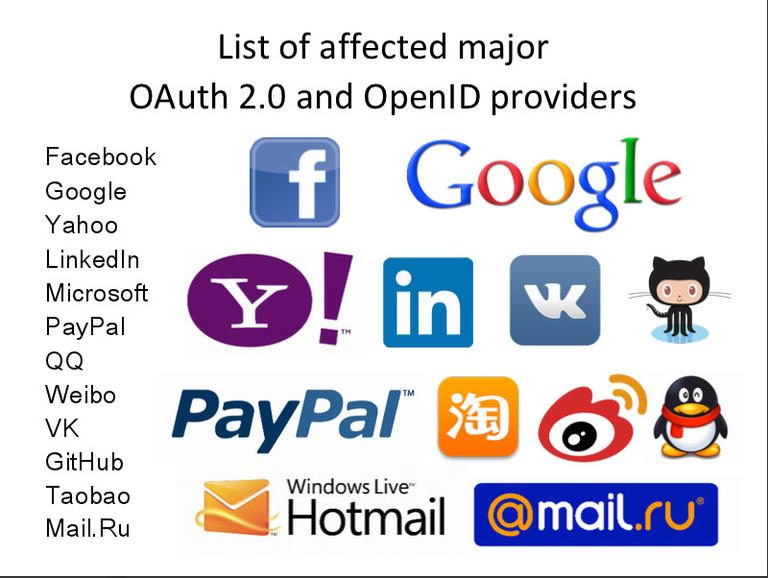
Covert Redirect vulnerability is the security flaw in the open standards for authorization OAuth and OpenID that is menacing IT industry. Another security flaw in the open standards for authorization OAuth and OpenID is scaring IT industry. Just a few weeks after the disclosure of the Heartbleed vulnerability, another major flaw was discovered in the open […]
 Pierluigi Paganini
May 02, 2014
Security Experts at PhishLabs revealed that a vishing campaign targeted banking industry to harvest credit/debit card data from customers. The security firm PhishLabs revealed that numerous US banks are victims of a recent Vishing (VoIP-based phishing) campaign that is targeting the payment card information of up to 250 Americans per day. Assuming that the withdrawal limits on ATM […]
 Pierluigi Paganini
May 02, 2014
Security Researcher Andreas Kurtz noticed that email attachments within different iOS versions are not protected by Apple’s data protection mechanisms. Mobile platform security is becoming even more crucial due to the large number of applications daily used by billion of users, but we must be aware of security flaws that could also affect the mobile OS. […]
 Pierluigi Paganini
May 01, 2014
Security Experts at Symantec discovered scammers are exploiting Facebook users’ intention to hack friends’ account to compromise their profile. Symantec has discovered a new insidious scam against Facebook users, scammers targeted the social media users proposing a bogus Facebook hacking tool that promises to give the access to their friends’ accounts … unfortunately the unique account hacked is the […]
 Pierluigi Paganini
May 01, 2014
Security experts Cesar Cerrudo conducted a study on the security of components within control traffic lights and similar electronic systems. The hacking of control systems for traffic lights or cyber grids is a prerogative of sci-fi series and movies, hackers could be able to target them causing serious problems. Cesar Cerrudo, CTO at IOActive, has conducted a study to investigate […]
 Pierluigi Paganini
April 30, 2014
AOL Inc. confirms security breach, email accounts of a significant number users may have been exposed, no financial data has been stolen. AOL Inc. last Monday has confirmed with an official blog post that the company suffered a massive data breach which may have compromised the email accounts of a significant number users, for this reason it is suggested to the clients of […]
 Pierluigi Paganini
April 30, 2014
Romanian Researcher discovered that Skype application store sensitive User Data Unencrypted on a local database. A Romanian programmer at Hackyard Security Group, Dragoş Gaftoneanu, revealed through a blog post that the popular VOIP application Skype leaves its local database unencrypted. Unfortunately the problem is very common, many applications, especially mobile apps, don’t encrypt application data exposing user’s information to serious risks for their privacy. According Gaftoneanu, […]






