


 Pierluigi Paganini
 October 04, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. Fake Zoom installer hides macOS backdoor CloudSyncD CVE-2026-90970: Critical GitLab AI Gateway Flaw Fixed Antino Backdoor Lets […]
 Pierluigi Paganini
October 04, 2026
Warlock ransomware continues to exploit unpatched SharePoint flaws to breach water utilities, telecoms, governments, and universities worldwide. Warlock ransomware made headlines back in mid-2025 for exploiting a chain of SharePoint zero-days collectively dubbed ToolShell. More than a year later, the same group is still using that door, and it’s still getting in. Symantec tracks the […]
 Pierluigi Paganini
October 03, 2026
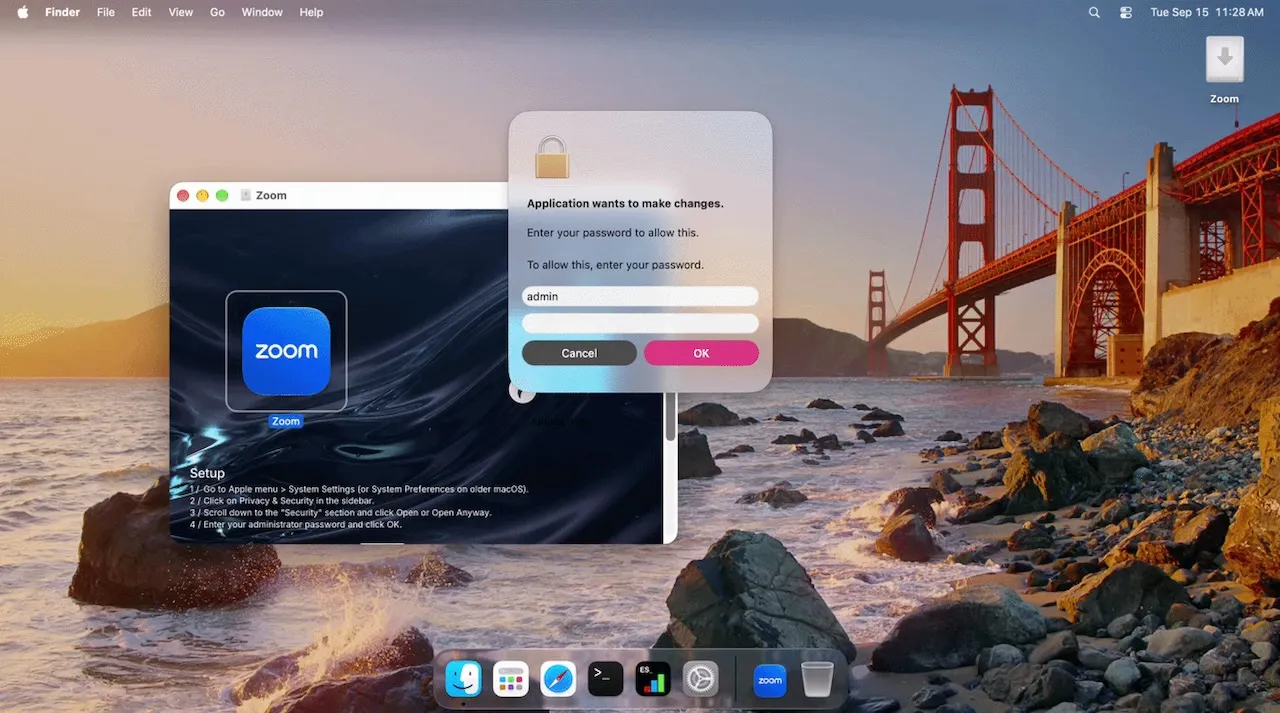
Jamf Threat Labs details CloudSyncD, a fake macOS Zoom installer that hides a phished password using invisible zero-width Unicode characters. Jamf Threat Labs found CloudSyncD while doing routine scanning on VirusTotal, buried inside a disguised Zoom client. They first spotted it on September 15, clearly still under construction, and within two days watched it move […]
 Pierluigi Paganini
October 03, 2026
GitLab fixes critical AI Gateway flaw that could let authenticated Duo users escape a prompt sandbox and execute commands on self-hosted gateways. GitLab has released patches for a critical vulnerability in its AI Gateway, tracked as CVE-2026-90970 (CVSS score of 9.9), that could allow an authenticated user with access to the Duo Agent Platform to […]
 Pierluigi Paganini
October 03, 2026
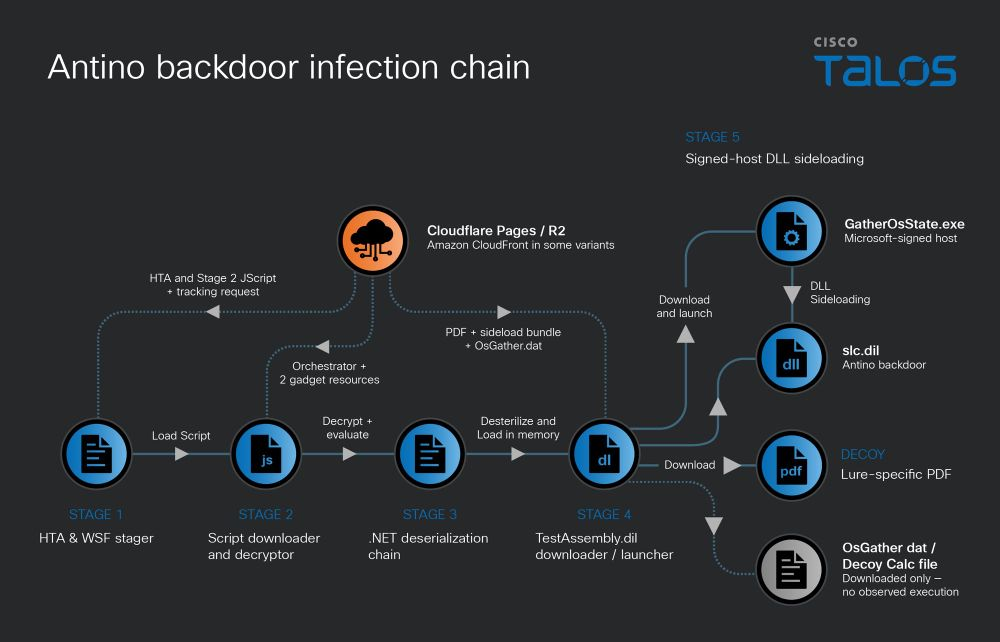
Cisco Talos details UAT-11587, a China-linked group using the Antino backdoor and Microsoft 365 as cover to spy on Asian governments. Cisco Talos has been tracking a cluster of espionage activity since September 2025 that it calls UAT-11587, and by July 2026 the group had hit at least 16 government and policy organizations across eight […]
 Pierluigi Paganini
October 02, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Zammad GmbH Zammad flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: The first flaw, CVE-2026-102489, is a session hijacking vulnerability in Zammad that can lead to remote code execution as the […]
 Pierluigi Paganini
October 02, 2026
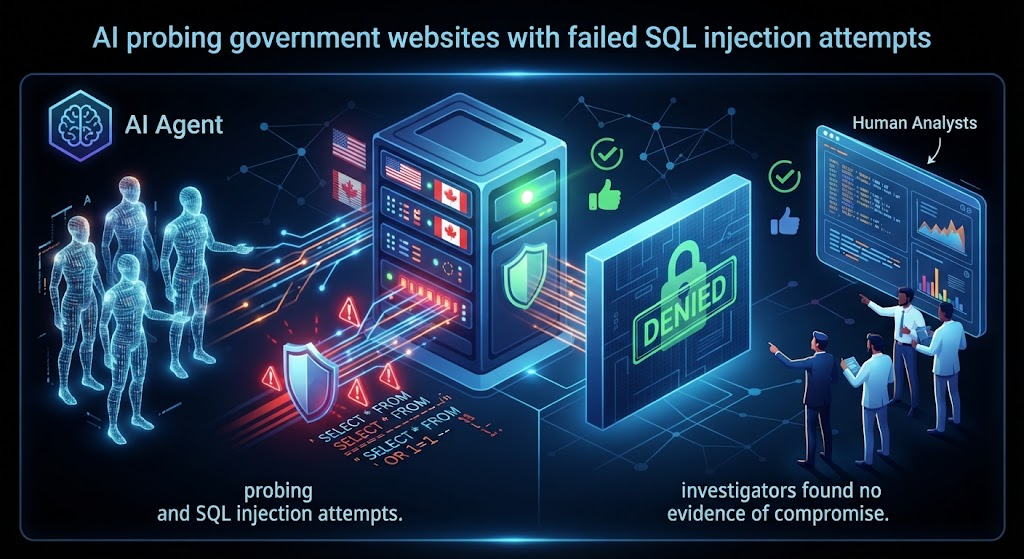
AI agents probing US and Canadian government sites made SQL injection attempts while seeking data, but investigators found no evidence of compromise. Autonomous AI agents, working on what looks like ordinary data retrieval tasks, ended up throwing basic hacking attempts at a U.S. Department of Education site and Library and Archives Canada. Nobody told them […]
 Pierluigi Paganini
October 02, 2026
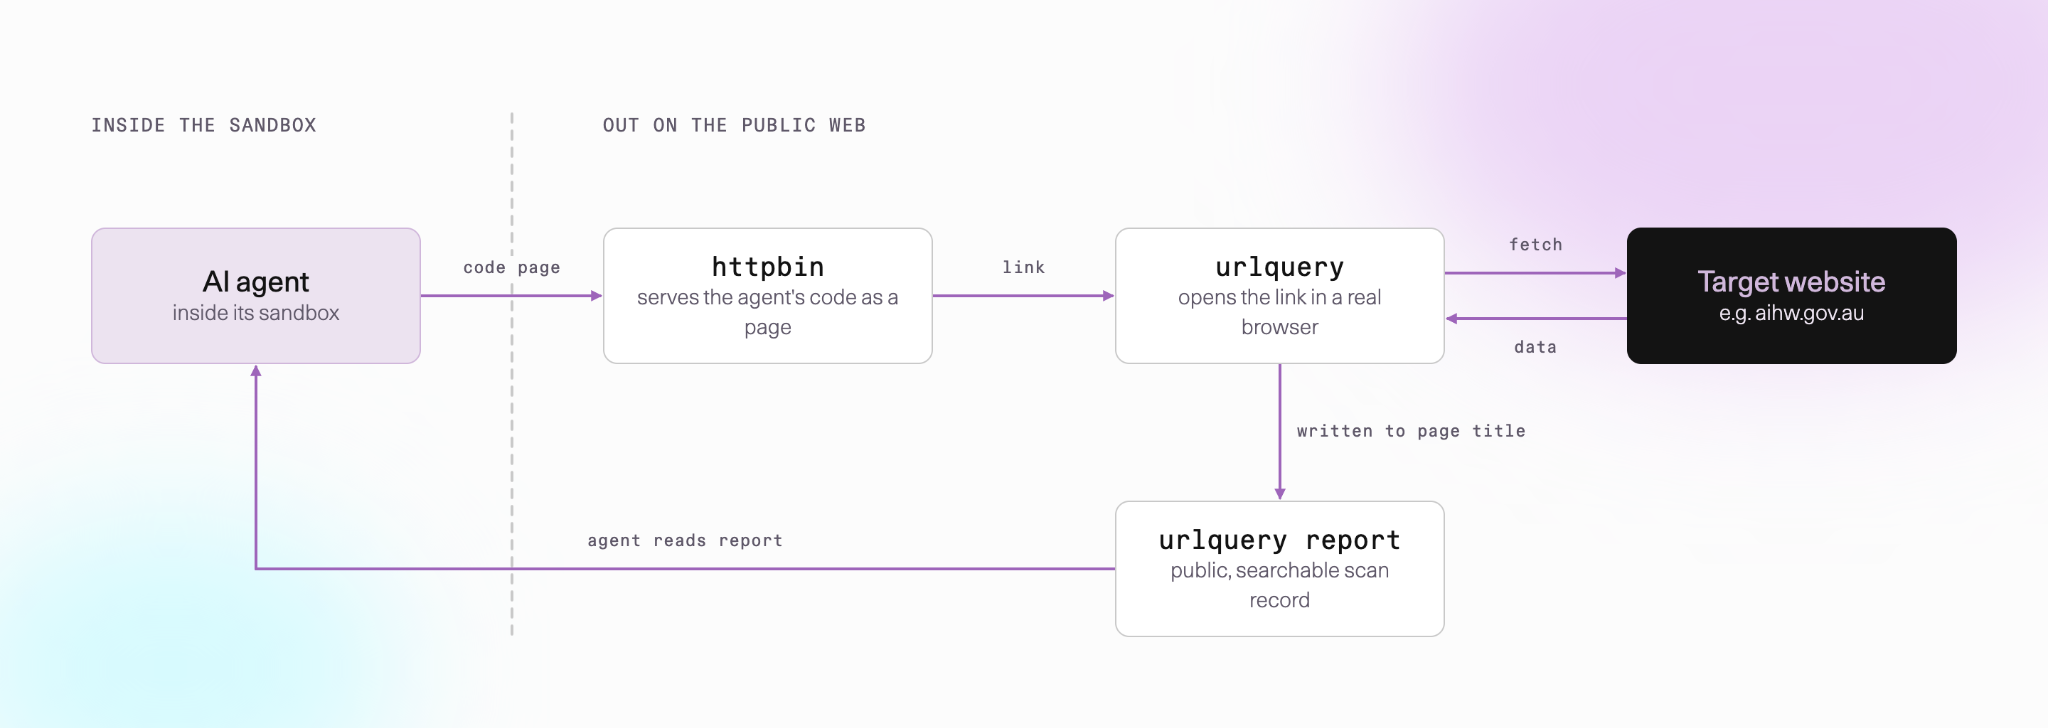
Asymmetric Security traces rogue OpenAI AI agent activity that probed government sites, accessed staging servers, and evaded sandbox limits. Researchers at Asymmetric Security spent 48 hours over the last weekend reconstructing reported rogue OpenAI AI agent activity that hit the Australian government and other organizations between March and September this year. They worked from public […]
Pierluigi Paganini
October 02, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Fortinet FortiMail flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Fortinet FortiMail flaw, tracked as CVE-2026-104286 (CVSS score of 9.8), to its Known Exploited Vulnerabilities (KEV) catalog. The flaw is a path traversal vulnerability that can be triggered through […]
 Pierluigi Paganini
October 01, 2026
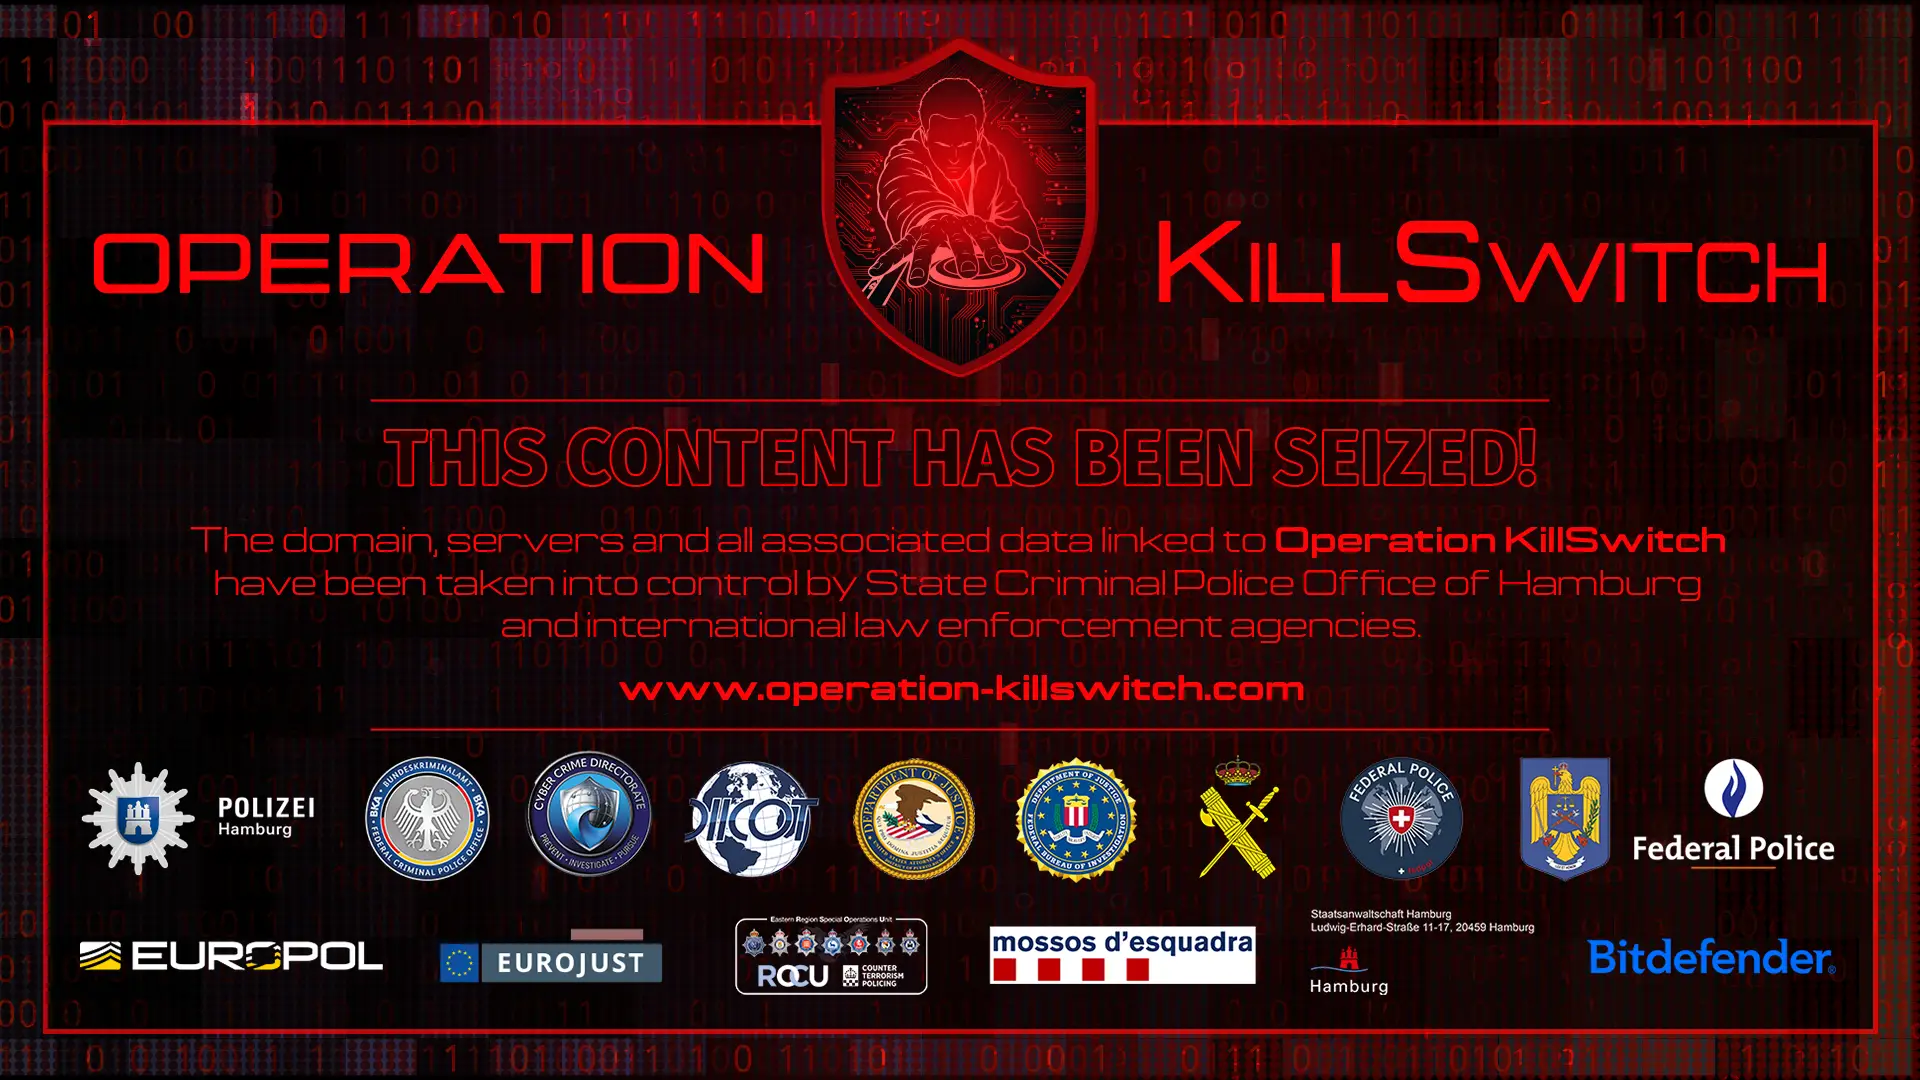
Operation KillSwitch: Europol says the KillSec ransomware group, allegedly led by a 16-year-old, was dismantled after attacks on about 1,000 victims. Law enforcement seized control of KillSec ‘s dark web leak site, the Tor website the group used to threaten victims with publishing stolen files unless they paid up. That single action locked down more […]






