Pierluigi Paganini
 October 22, 2022
US government agencies warned that the Daixin Team cybercrime group is actively targeting the U.S. Healthcare and Public Health sector with ransomware. CISA, the FBI, and the Department of Health and Human Services (HHS) warned that the Daixin Team cybercrime group is actively targeting U.S. businesses, mainly in the Healthcare and Public Health (HPH) Sector, […]
 Pierluigi Paganini
October 21, 2022
Electricity company EnergyAustralia suffered a security breach, threat actors had access to information on 323 customers. Another Australian organization was hit by a severe cyber attack, this time the victim is the Electricity company EnergyAustralia. EnergyAustralia is the country’s third-largest energy retailer. The company confirmed that threat actors had access to information on 323 residential and […]
Pierluigi Paganini
October 21, 2022
CISA added a Linux kernel vulnerability, tracked as CVE-2021-3493, to its Known Exploited Vulnerabilities Catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) this week added a Linux kernel vulnerability, tracked as CVE-2021-3493, to its Known Exploited Vulnerabilities Catalog. According to Binding Operational Directive (BOD) 22-01: Reducing the Significant Risk of Known Exploited Vulnerabilities, FCEB agencies have to address the […]
 Pierluigi Paganini
October 20, 2022
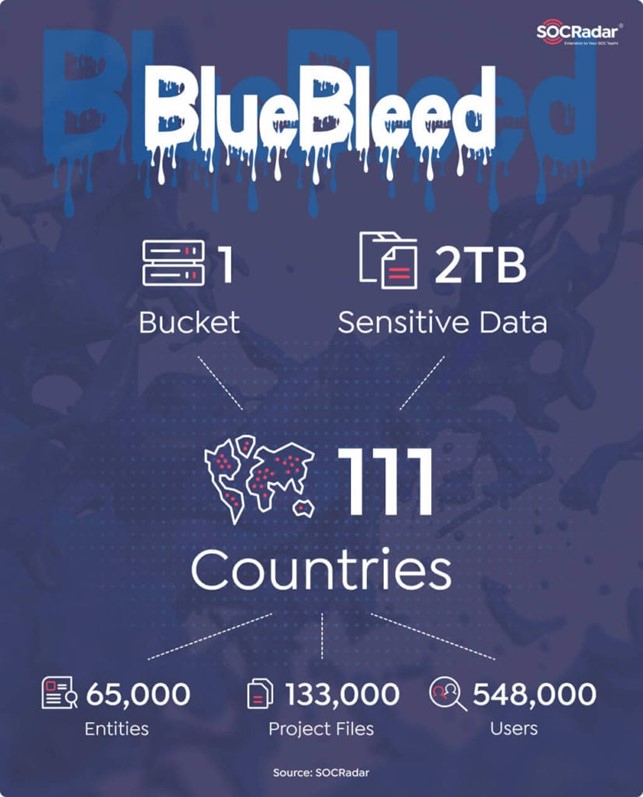
Microsoft disclosed a data leak, sensitive data of some of its customers were exposed by a misconfigured Microsoft server accessible online. Microsoft announced that sensitive data belonging to some of its customers were exposed on the Internet due to a misconfigured Microsoft server. The data leak was discovered by the security threat intelligence firm SOCRadar […]
 Pierluigi Paganini
October 20, 2022
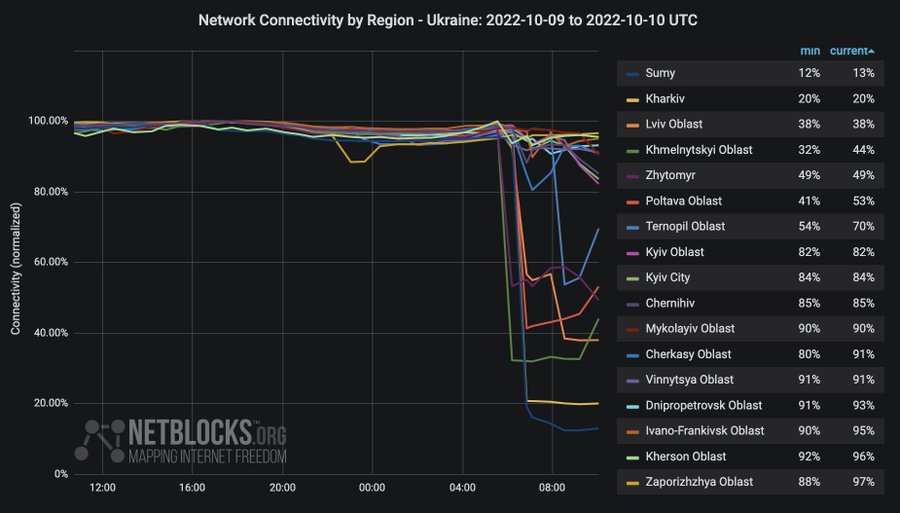
While the Russian army is conducting coordinated missile and drone strikes in Ukraine experts observed Internet disruptions in the country. Starting on the morning of Monday, October 10, the Russian army is targeting several cities in Ukraine with coordinated missile and drone strikes. The escalation is a retaliation for the bombing of a bridge connecting […]
 Pierluigi Paganini
October 20, 2022
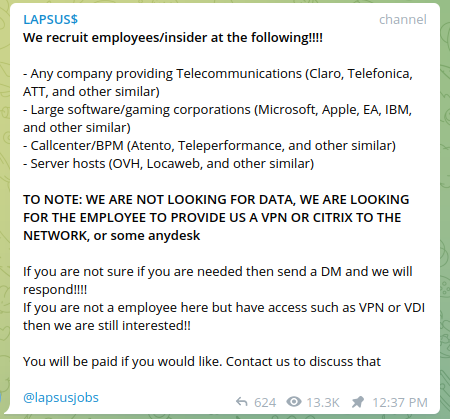
The Federal Police of Brazil arrested an individual who is suspected of being a member of the notorious LAPSUS$ extortionist group. The Federal Police of Brazil yesterday announced the arrest of an individual suspected of being linked to the LAPSUS$ extortionist gang. The authorities did not disclose info about the individual, it seems that the […]
 Pierluigi Paganini
October 20, 2022
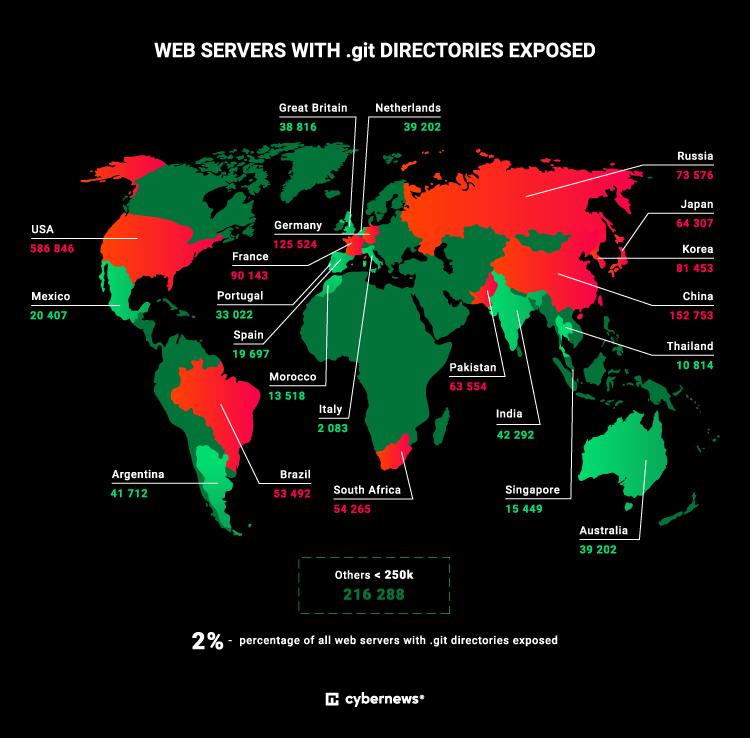
Nearly two million .git folders containing vital project information are exposed to the public, the Cybernews research team found. Original Post at https://cybernews.com/security/millions-git-folders-exposed/ Git is the most popular open-source, distributed version control system (VCS) developed nearly 20 years ago by Linus Torvalds for development of the Linux kernel, with other kernel developers contributing to its initial […]
 Pierluigi Paganini
October 19, 2022
A bug in the message encryption mechanism used by Microsoft in Office 365 can allow to access the contents of the messages. Researchers at the cybersecurity firm WithSecure discovered a bug in the message encryption mechanism used by Microsoft in Office 365 that can allow to access message contents due. The experts pointed out that Microsoft Office […]
 Pierluigi Paganini
October 18, 2022
An international law enforcement operation led by Europol disrupted a cybercrime ring focused on hacking wireless key fobs to steal cars. The French authorities in cooperation with their Spanish and Latvian peers, and with the support of Europol and Eurojust, have dismantled a cybercrime organization specializing in the theft of cars by hacking key fobs. […]
 Pierluigi Paganini
October 18, 2022
China-linked threat actors APT41 (a.k.a. Winnti) targeted organizations in Hong Kong, in some cases remaining undetected for a year. Symantec researchers reported that cyberespionage group APT41 targeted organizations in Hong Kong in a campaign that is a likely continuation of the Operation CuckooBees activity detailed by Cybereason in May. Winnti (aka APT41, Axiom, Barium, Blackfly) is a cyberespionage […]