 Pierluigi Paganini
 August 04, 2022
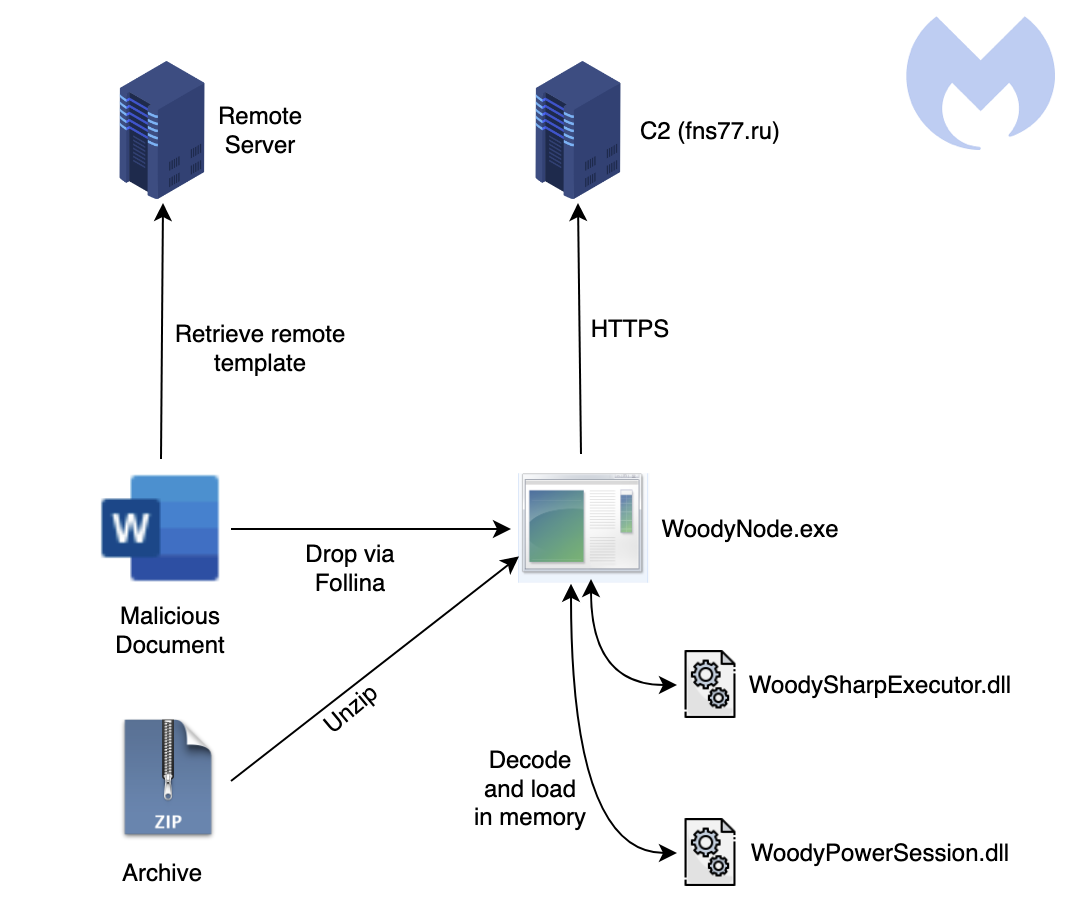
An unknown threat actor is targeting Russian organizations with a new remote access trojan called Woody RAT. Malwarebytes researchers observed an unknown threat actor targeting Russian organizations with a new remote access trojan called Woody RAT. The attackers were delivering the malware using archive files and Microsoft Office documents exploiting the Follina Windows flaw (CVE-2022-30190). The assumption […]
 Pierluigi Paganini
August 04, 2022
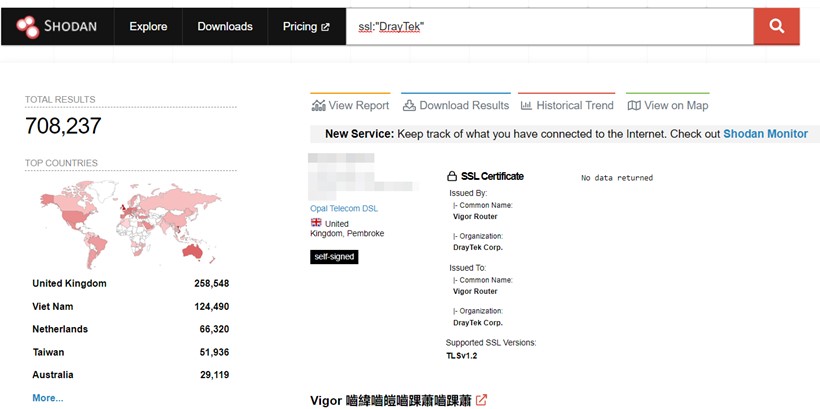
A critical flaw in multiple models of DrayTek Vigor routers can allow unauthenticated, remote attackers to fully compromise affected devices. Tens of router models from Taiwanese SOHO manufacturer DrayTek are affected by a critical, unauthenticated, remote code execution vulnerability, tracked as CVE-2022-32548, that can be exploited to fully compromise a vulnerable device and gain unauthorized […]
 Pierluigi Paganini
August 04, 2022
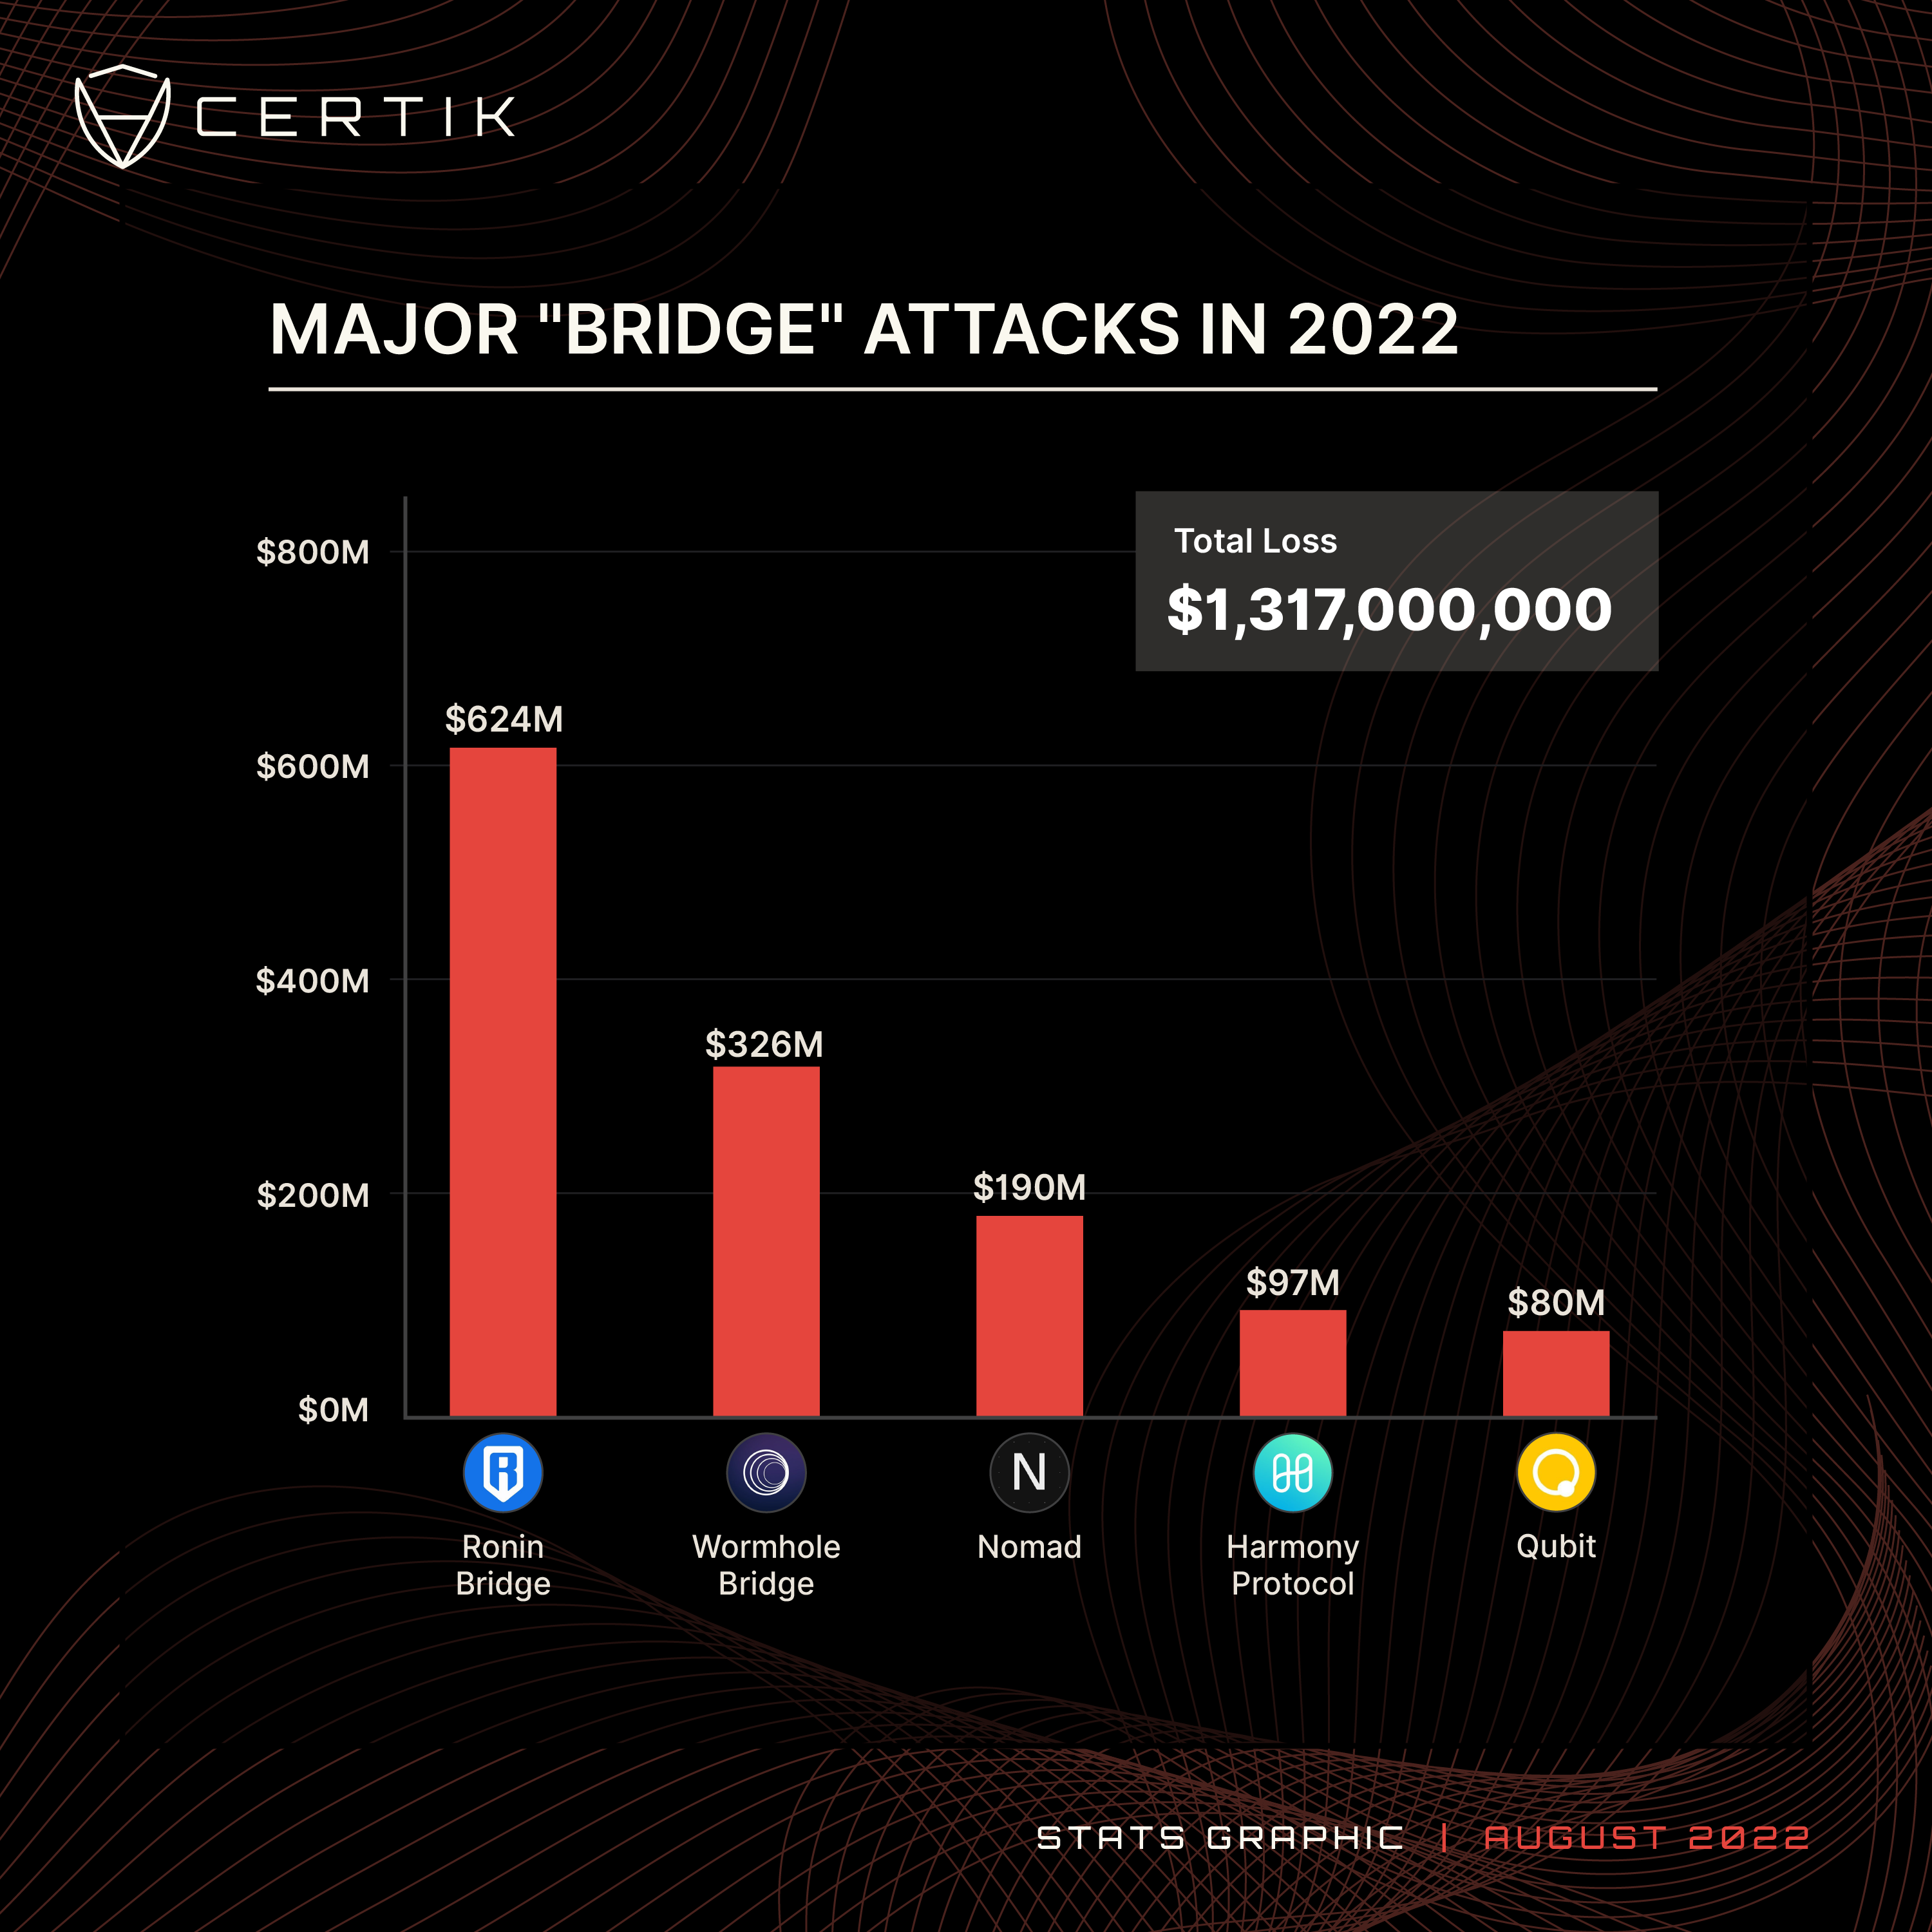
The cryptocurrency bridge Nomad is the last victim of a cyber heist, threat actors stole almost $200 million of its funds. Another crypto heist made the headlines, threat actors stole nearly $200 million worth of cryptocurrency from the bridge Nomad. Nomad Bridge is a cross-chain bridge between Ethereum, Moonbeam, Avalanche, Evmos and Milkomeda. The project […]
 Pierluigi Paganini
August 03, 2022
Semikron, a German-based independent manufacturer of power semiconductor components, suffered a ransomware cyberattck. Semikron is a German-based independent manufacturer of power semiconductor components, it employs more than 3,000 people in 24 subsidiaries worldwide, with production sites in Germany, Brazil, China, France, India, Italy, Slovakia and the USA. The company confirmed it has suffered a cyberattack conducted by a professional […]
 Pierluigi Paganini
August 02, 2022
VMware patched a critical authentication bypass security flaw, tracked as CVE-2022-31656, impacting local domain users in multiple products. VMware has addressed a critical authentication bypass security flaw, tracked as CVE-2022-31656, impacting local domain users in multiple products. An unauthenticated attacker can exploit the vulnerability to gain admin privileges. “A malicious actor with network access to the […]
 Pierluigi Paganini
August 02, 2022
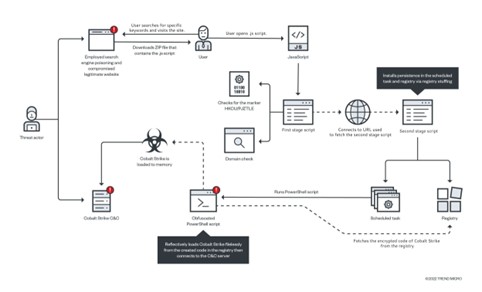
Gootkit access-as-a-service (AaaS) malware is back with tactics and fileless delivery of Cobalt Strike beacons. Gootkit runs on an access-a-as-a-service model, it is used by different groups to drop additional malicious payloads on the compromised systems. Gootkit has been known to use fileless techniques to deliver threats such as the SunCrypt, and REvil (Sodinokibi) ransomware, Kronos trojans, […]
 Pierluigi Paganini
August 02, 2022
Austria is investigating a report that an Austrian firm DSIRF developed spyware targeting law firms, banks and consultancies. At the end of July, Microsoft Threat Intelligence Center (MSTIC) and the Microsoft Security Response Center (MSRC) researchers linked a threat group known as Knotweed to an Austrian surveillance firm named DSIRF, known for using multiple Windows […]
 Pierluigi Paganini
August 01, 2022
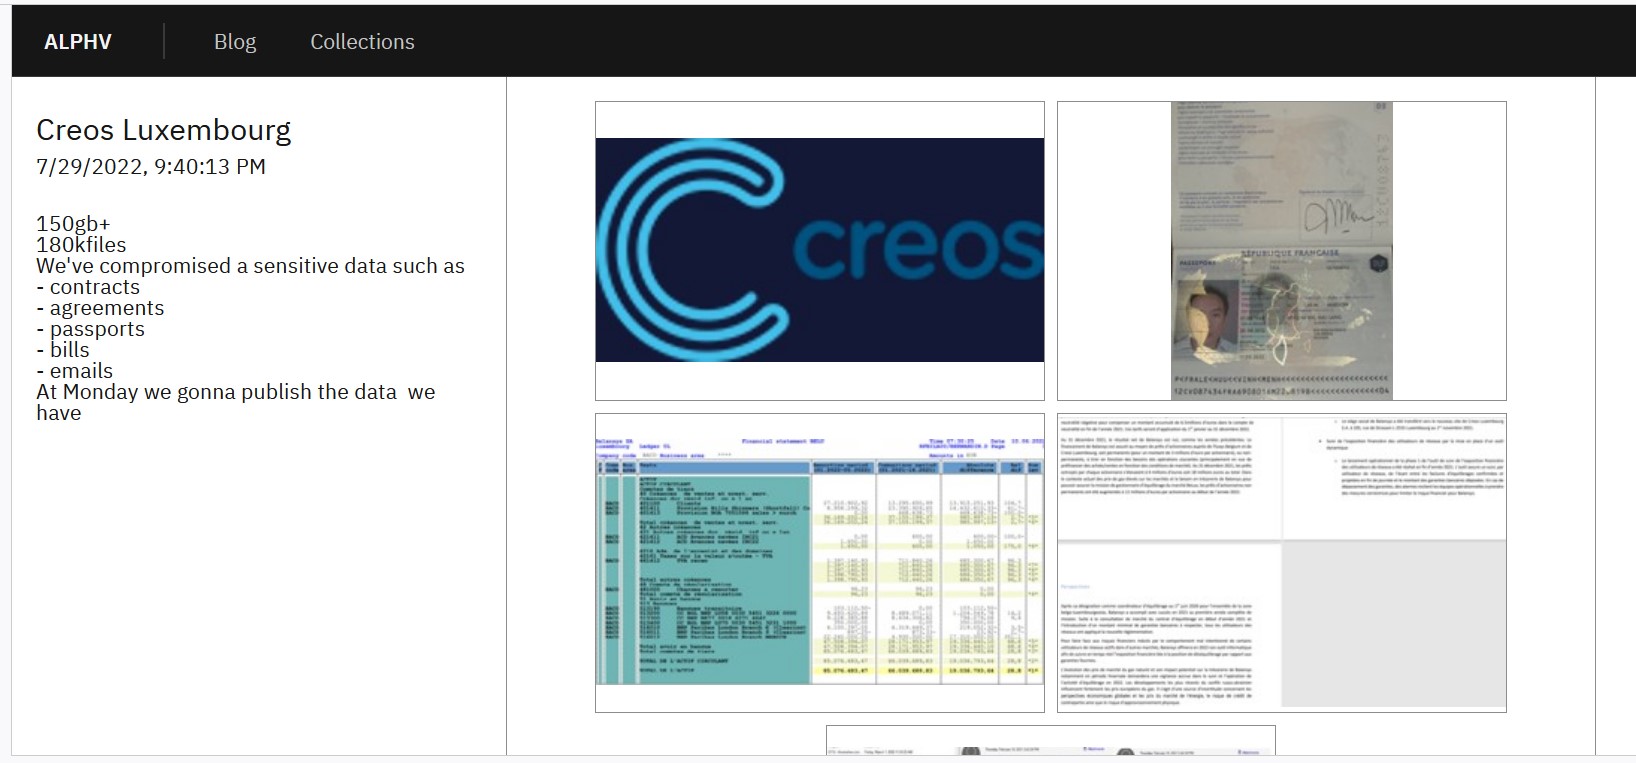
The ALPHV/BlackCat ransomware gang claims to have breached the European gas pipeline Creos Luxembourg S.A. The ALPHV/BlackCat ransomware gang claims to have hacked the European gas pipeline Creos Luxembourg S.A. Creos Luxembourg S.A. owns and manages electricity networks and natural gas pipelines in the Grand Duchy of Luxembourg. In this capacity, the company plans, constructs […]
 Pierluigi Paganini
August 01, 2022
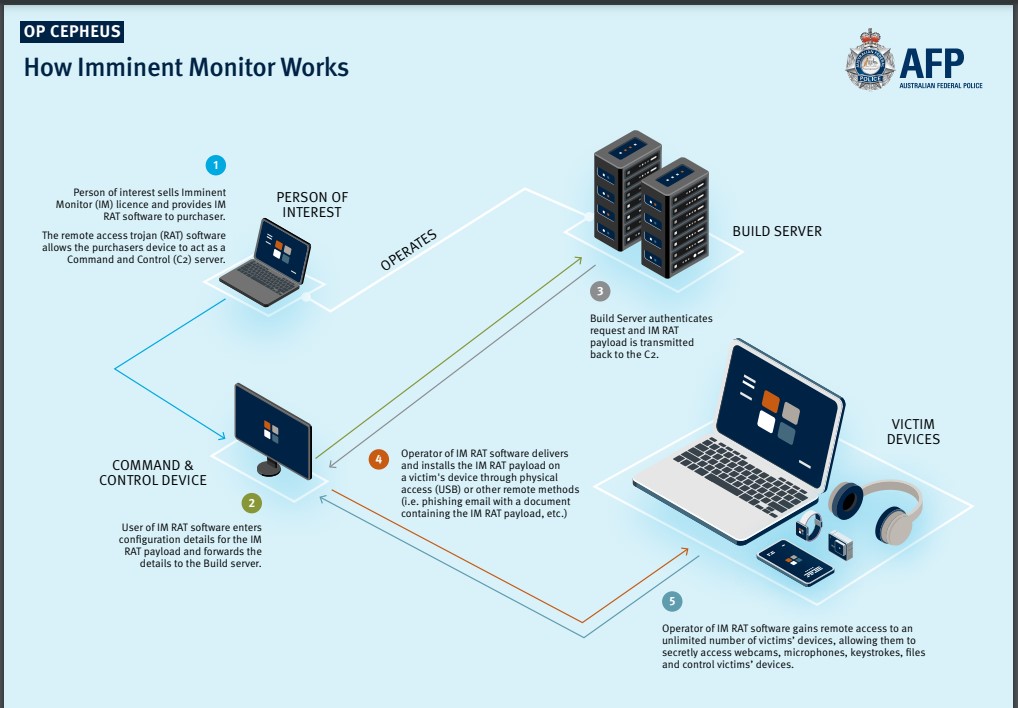
An Australian national has been charged for the creation and sale of the Imminent Monitor (IM) spyware, which was also used for criminal purposes. The 24-year-old Australian national Jacob Wayne John Keen has been charged for his alleged role in the development and sale of spyware known as Imminent Monitor (IM). The Australian Federal Police (AFP) launched […]
 Pierluigi Paganini
August 01, 2022
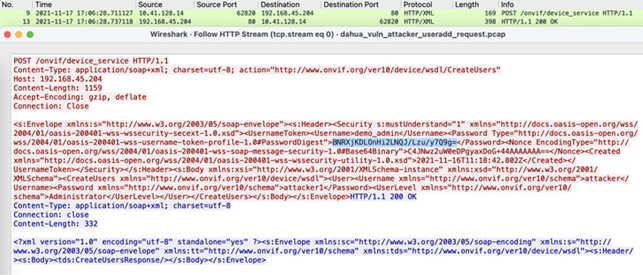
A vulnerability, tracked as CVE-2022-30563, impacting Dahua IP Camera can allow attackers to seize control of IP cameras. The CVE-2022-30563 vulnerability impacting Dahua IP Camera can allow attackers to seize control of IP cameras. The issue affects Dahua’s implementation of the Open Network Video Interface Forum (ONVIF). ONVIF provides and promotes standardized interfaces for effective […]
Cyber Crime / September 26, 2026

Security / September 26, 2026