 Pierluigi Paganini
 June 18, 2022
The U.S. Department of Justice (DoJ) announced to have shut down the infrastructure associated with the Russian botnet RSOCKS. The U.S. Department of Justice (DoJ) announced to have shut down the infrastructure associated with the Russian botnet RSOCKS as part of an international police operation that involved law enforcement partners from Germany, the Netherlands, and […]
 Pierluigi Paganini
June 17, 2022
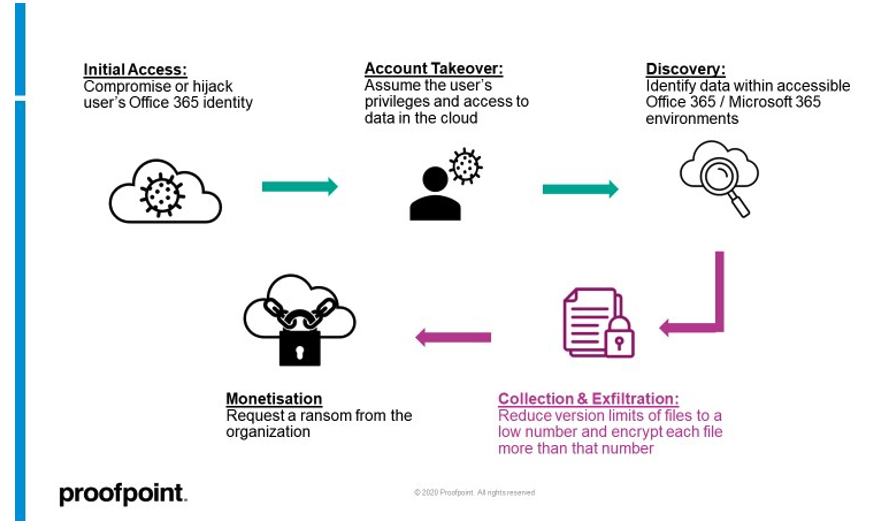
Experts discovered a feature in Microsoft 365 suite that could be abused to encrypt files stored on SharePoint and OneDrive and target cloud infrastructure. Researchers from Proofpoint reported that a feature in the in Microsoft 365 suite could be abused to encrypt files stored on SharePoint and OneDrive. “Proofpoint has discovered a potentially dangerous piece […]
 Pierluigi Paganini
June 16, 2022
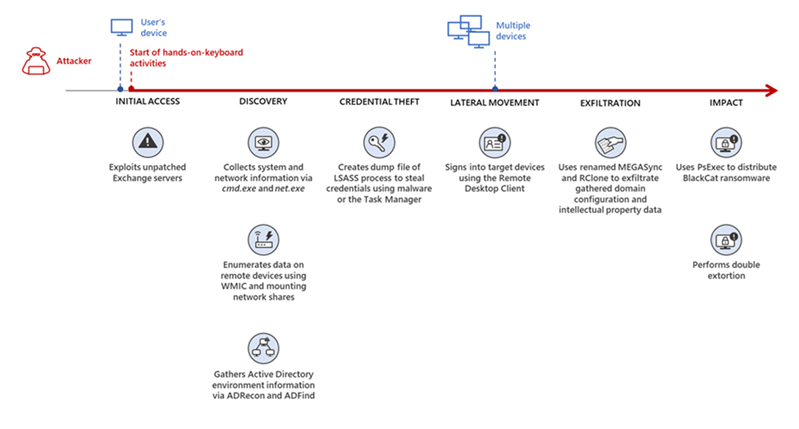
The BlackCat ransomware gang is targeting unpatched Exchange servers to compromise target networks, Microsoft warns. Microsoft researchers have observed BlackCat ransomware gang targeting unpatched Exchange servers to compromise organizations worldwide. The compromise of Exchange servers allows threat actors to access the target networks, perform internal reconnaissance and lateral movement activities, and steal sensitive documents before encrypting them. “For example, […]
 Pierluigi Paganini
June 16, 2022
ALPHV/BlackCat ransomware group began publishing victims’ data on the clear web to increase the pressure on them and force them to pay the ransom. ALPHV/BlackCat ransomware group has adopted a new strategy to force victims into paying the ransom, the gang began publishing victims’ data on the clear web to increase the pressure. Publishing data online will […]
 Pierluigi Paganini
June 16, 2022
Researchers at antivirus firm Dr. Web discovered malware in the Google Play Store that was downloaded two million times. An investigation conducted by the antivirus firm Dr. Web in May resulted in the discovery of multiple adware and information-stealing malware on the official Google Play Store. However, the experts warn that info-stealing Trojans are the […]
 Pierluigi Paganini
June 15, 2022
Hertzbleed attack: Researchers discovered a new vulnerability in modern Intel and AMD chips that could allow attackers to steal encryption keys. Researchers from University of Texas, University of Illinois Urbana-Champaign, and the University of Washington, devised a new side-channel attack technique dubbed Hertzbleed that could allow remote attackers to steal encryption keys from modern Intel […]
 Pierluigi Paganini
June 15, 2022
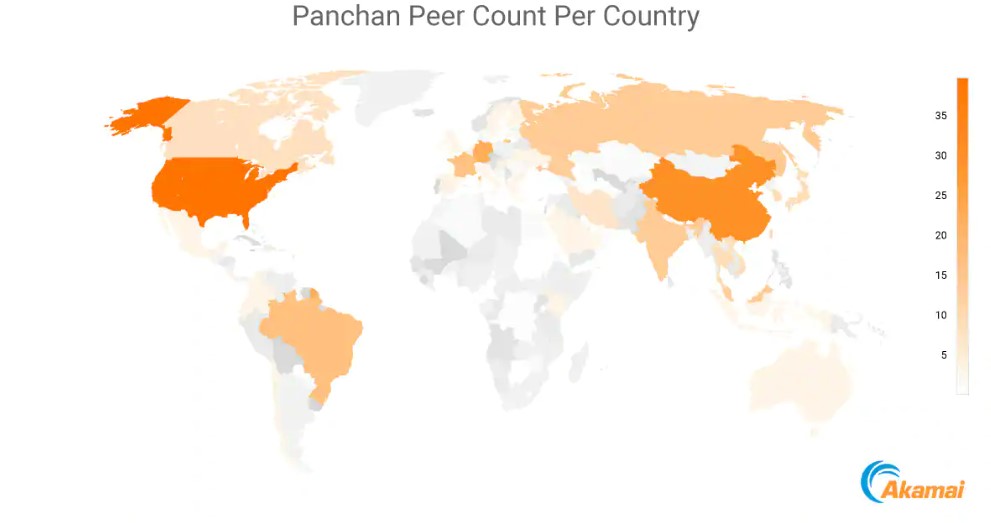
Researchers discovered a new Golang-based peer-to-peer (P2P) botnet, dubbed Panchan, targeting Linux servers in the education sector since March 2022. Akamai security researchers discovered a new Golang-based P2P Botnet, tracked as Panchan, that is targeting Linux servers that has been active since March 2022. Panchan uses basic SSH dictionary attack to implement wormable behavior, it also […]
 Pierluigi Paganini
June 15, 2022
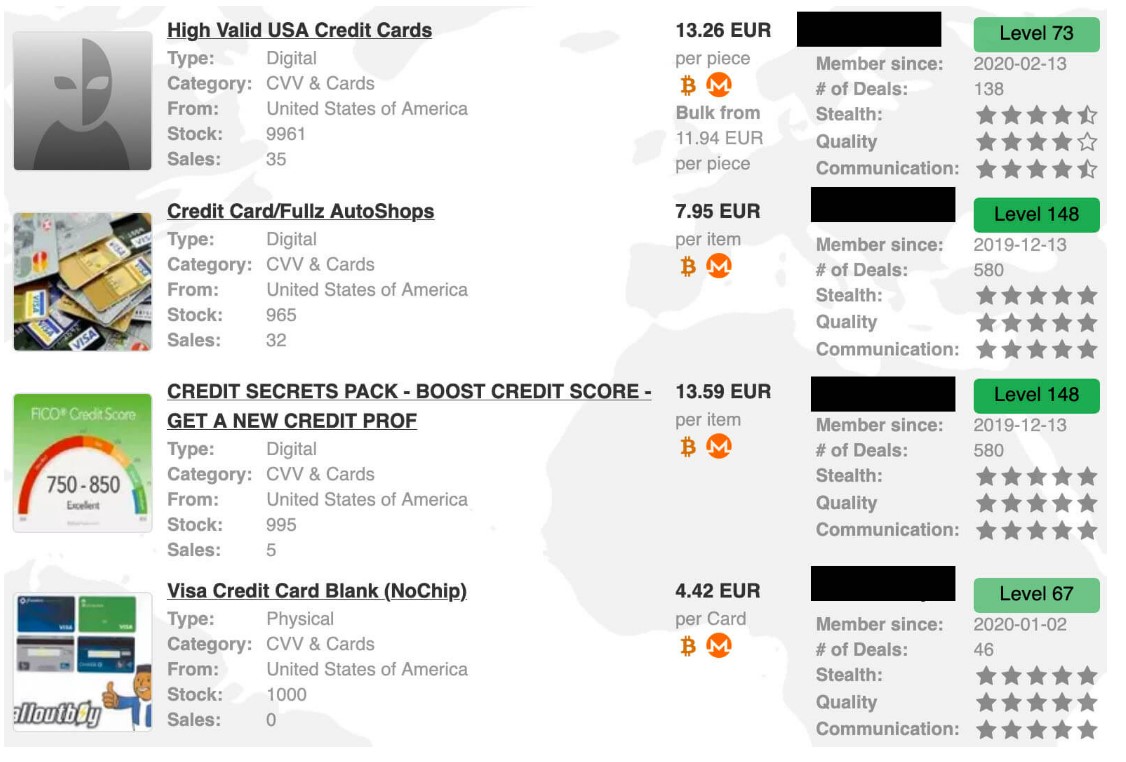
PrivacyAffairs released the Dark Web Index 2022, the document provides the prices for illegal services/products available in the black marketplaces. Privacy Affairs published the Dark Web Index, an analysis of prices for illegal services/products available in the black marketplaces and related to the period between February 2021 and June 2022. The document updates the information […]
 Pierluigi Paganini
June 14, 2022
A high-severity vulnerability in the Zimbra email suite could be exploited by an unauthenticated attacker to steal login credentials of users. Researchers from Sonarsource have discovered a high-severity vulnerability impacting the Zimbra email suite, tracked as CVE-2022-27924 (CVSS score: 7.5), that can be exploited by an unauthenticated attacker to steal login credentials of users without user […]
 Pierluigi Paganini
June 14, 2022
Organizations face the constant need to protect these APIs from attacks so they can protect organizational data. Organizations are rapidly opening their ecosystem through Application Programming Interfaces (API) by ensuring seamless access to data and interaction with external software components and services. APIs are the gateway to providing the high security of data in an […]
Malware / November 02, 2026