



 Pierluigi Paganini
 January 23, 2019
PHP PEAR official site hacked, attackers replaced legitimate version of the package manager with a tainted version in the past 6 months. Bad news for users that have downloaded the PHP PEAR package manager from the official website in the past 6 months because hackers have replaced it with a tainted version. The PHP Extension and […]
 Pierluigi Paganini
January 21, 2019
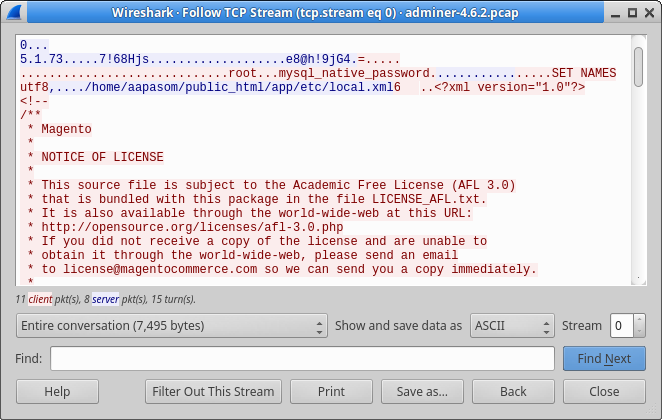
A rogue MySQL server could be used to steal files from clients due to a design flaw in the popular an open source relational database management system (RDBMS). The flaw resides in the file transfer process between a client host and a MySQL server, it could be exploited by an attacker running a rogue MySQL server to access […]
 Pierluigi Paganini
January 21, 2019
The electronics firm Omron released a security update to address flaws in its CX-Supervisor product that can be exploited DoS attacks and remote code execution. CX-Supervisor allows to rapidly create human-machine interfaces (HMIs) for supervisory control and data acquisition (SCADA) systems thanks to the availability of a large number of predefined functions and libraries. The software […]
 Pierluigi Paganini
January 21, 2019
Unpatched critical flaw CVE-2018-15439 could be exploited by a remote, unauthenticated attacker to gain full control over the device. Cisco Small Business Switch software is affected by a critical and unpatched vulnerability (CVE-2018-15439) that could be exploited by a remote, unauthenticated attacker to gain full control over the device. Cisco Small Business Switch SOHO devices allow […]
 Pierluigi Paganini
January 20, 2019
Bulgaria has extradited a Russian hacker that was indicted by a US court for mounting a sophisticated hacking scheme to the United States. According to the Russian embassy in Washington, the Russian hacker Alexander Zhukov was extradited on January 18. The Russian embassy has chosen to disclose the news on the VK social network, the […]
 Pierluigi Paganini
January 20, 2019
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. Let me inform you that my new book, “Digging in the Deep Web” is online with a special deal 20% discount Kindle Edition Paper Copy Once again thank you! TA505 Group adds new ServHelper Backdoor and FlawedGrace […]
 Pierluigi Paganini
January 20, 2019
Security experts attributed new malicious campaigns to the DarkHydrus APT group (aka Lazy Meerkat), threat actors used a new variant of the RogueRobin Trojan and leveraged Google Drive as an alternative C2 channel. DarkHydrus was first discovered by experts at Palo Alto Networks’ Unit 42 team in July when the group carried out attacks aimed at […]
 Pierluigi Paganini
January 20, 2019
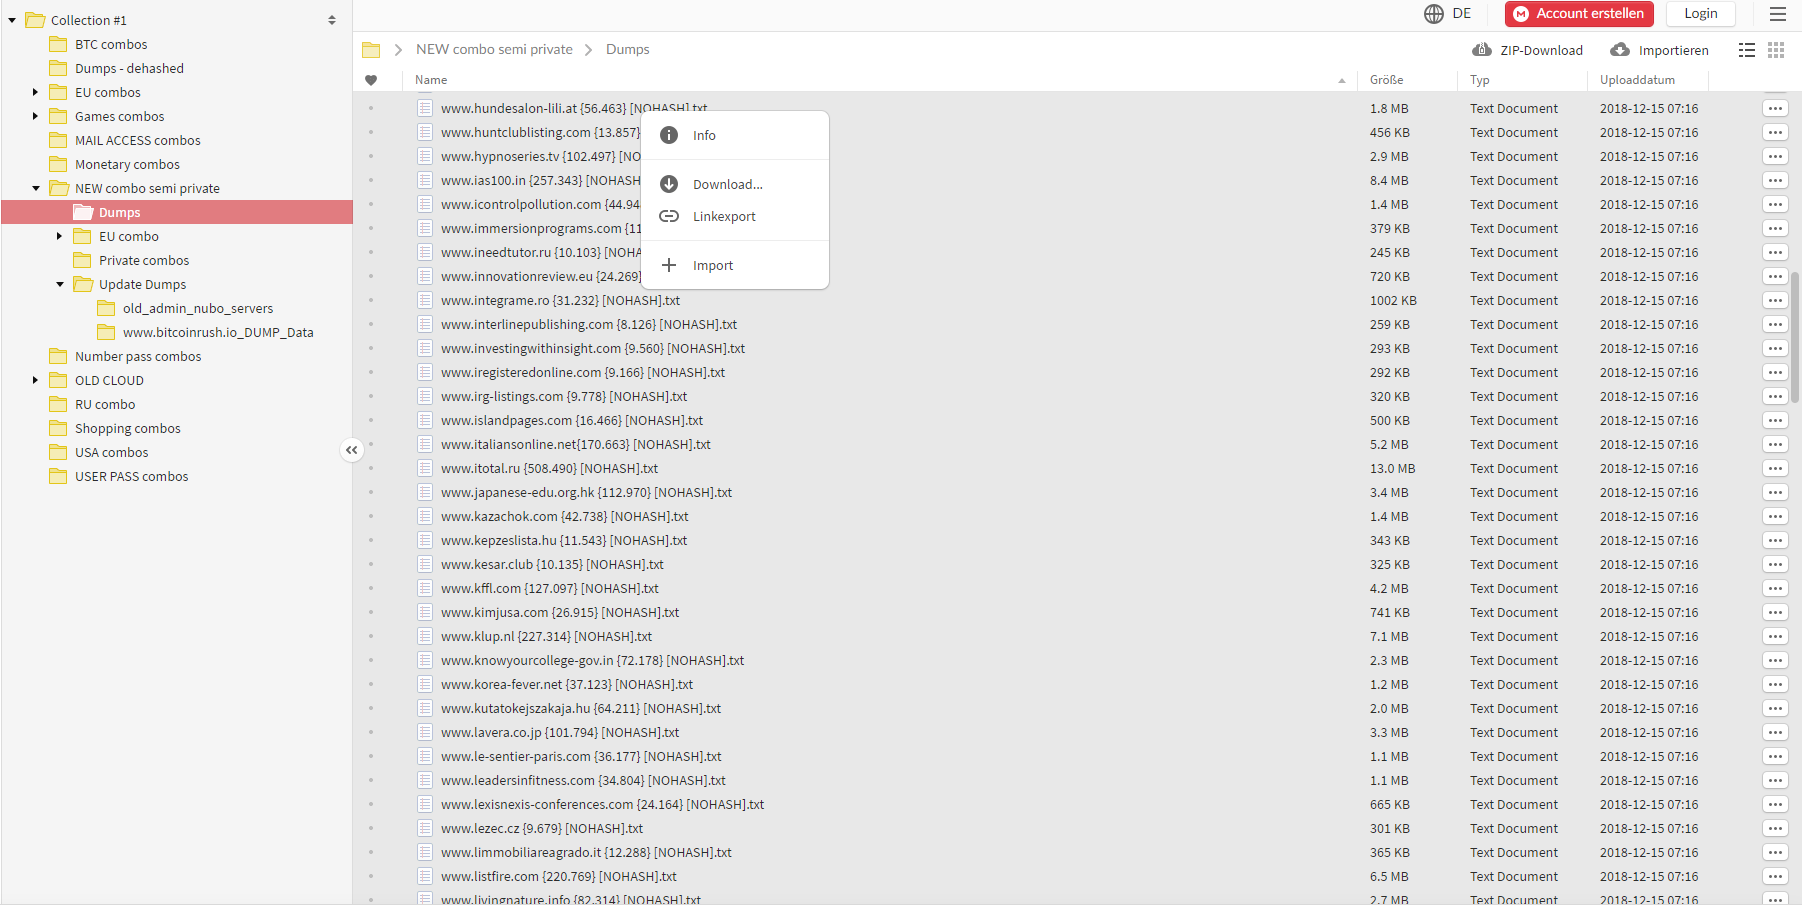
Cybersecurity expert Marco Ramilli has analyzed the huge trove of data, called Collection #1, that was first disclosed by Troy Hunt. Few weeks ago I wrote about “How Data Breaches Happen“, where I shared some public available “pasties” within apparently (not tested) SQLi vulnerable websites. One of the most famous data breaches in the past […]
 Pierluigi Paganini
January 19, 2019
Paying attention to cybersecurity is more important than ever in 2019. But, some companies are still unwilling to devote the necessary resources to securing their infrastructures against cyberattacks, and naive individuals think they’re immune to the tactics of cybercriminals, too. For people who still need some convincing that cybersecurity is an essential point of focus, […]
 Pierluigi Paganini
January 19, 2019
Security expert Robert Baptiste (akaElliot Alderson) discovered a vulnerability (CVE-2019-6447) in the ES File Explorer that potentially expose hundreds of million Android installs. The ES File Explorer is an Android file manager that has over 100,000,000 installs and more than 500 million users worldwide according to its developer. Baptiste discovered that the application uses a local […]

Cyber Crime / September 23, 2026
Cyber Crime / September 23, 2026
Malware / September 23, 2026


