 Pierluigi Paganini
 October 07, 2026
SonicWall patched a CVSS 10 pre-auth SSRF flaw in SMA1000 appliances that could let unauthenticated attackers reach internal functions. SonicWall released hotfixes for four vulnerabilities in its SMA1000 remote access appliances, including a critical flaw tracked as CVE-2026-102255 (CVSS score of 10.0. The issue is a pre-authentication SSRF bug in the WorkPlace portal that could […]
 Pierluigi Paganini
October 07, 2026
FBI and Secret Service warn FortiBleed, a credential-harvesting campaign against Fortinet firewalls, has compromised 86,644 devices and is locking out admins. The FBI and the U.S. Secret Service issued a joint advisory about FortiBleed, and the headline number alone is worth sitting with: more than 86,644 compromised Fortinet FortiGate devices across 194 countries, according to […]
 Pierluigi Paganini
October 07, 2026
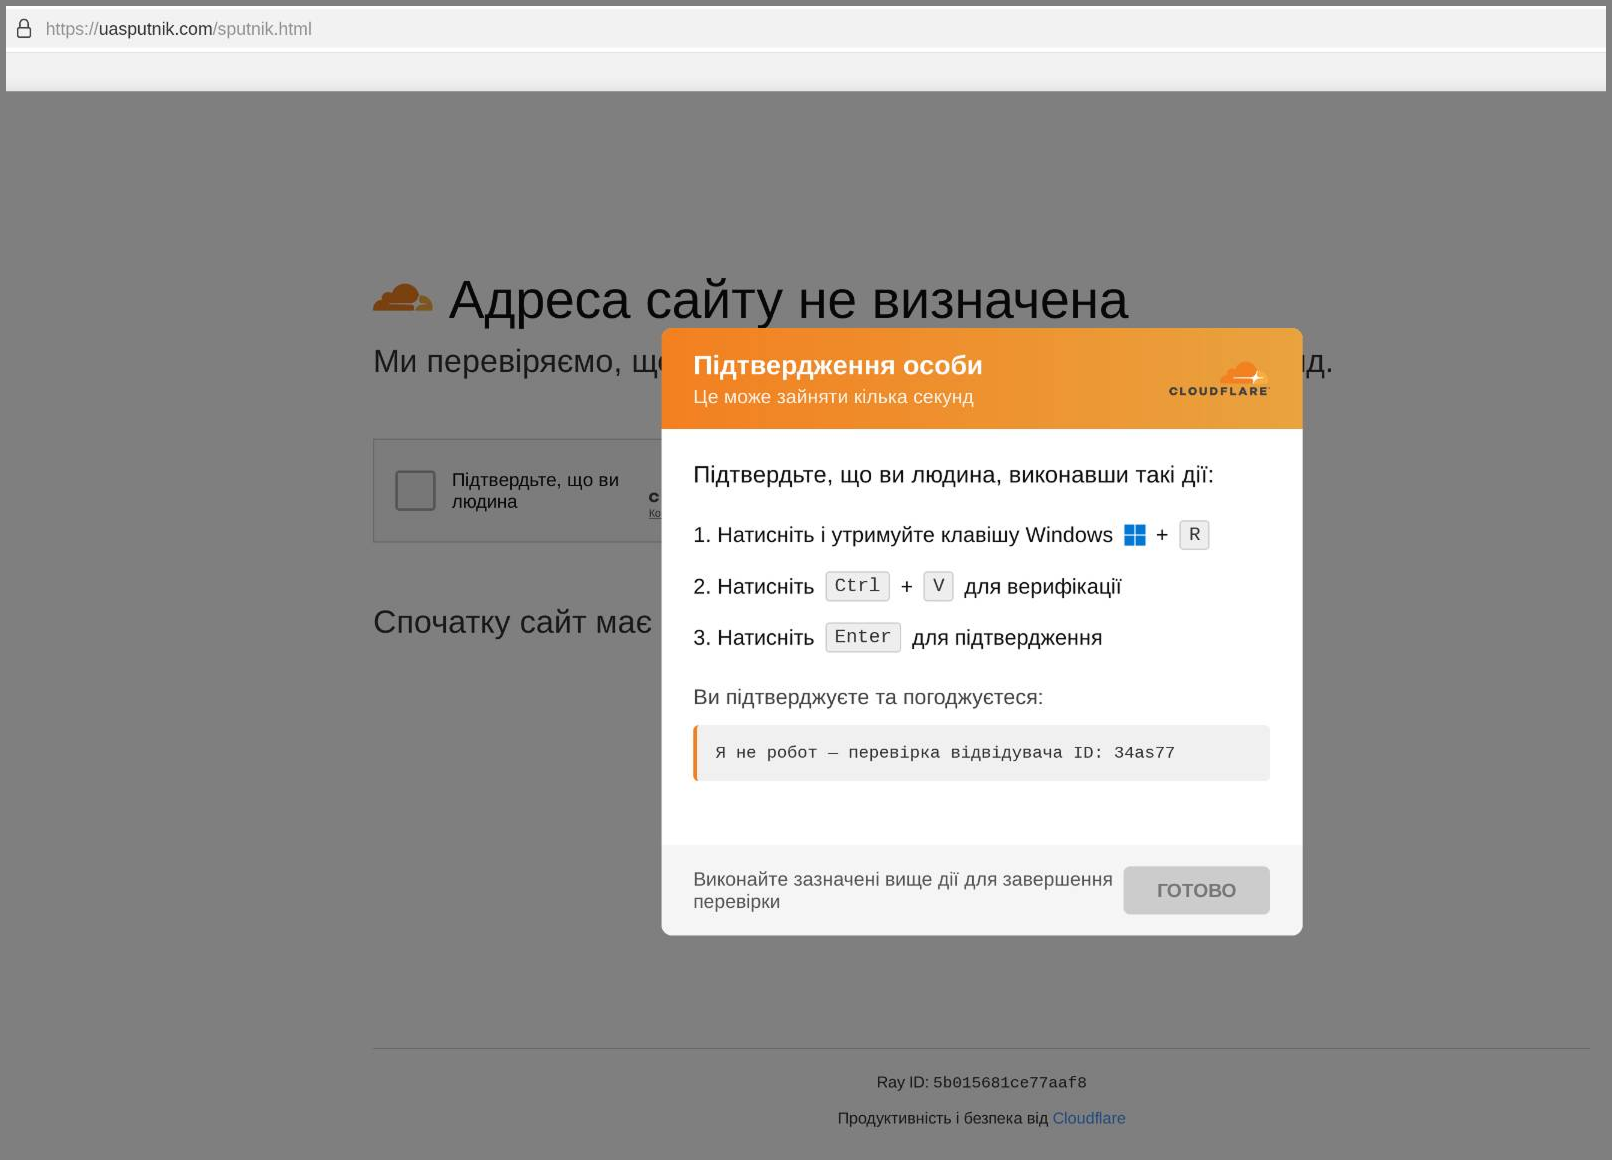
Over 100 hacked websites used fake Cloudflare checks to trick visitors into installing LunexStealer through ClickFix commands. The lure is the now-familiar ClickFix technique, dressed up as Cloudflare’s standard bot check. The fake page asks you to run a command, supposedly to confirm you’re not a bot, and that command quietly downloads and installs an […]
 Pierluigi Paganini
October 07, 2026
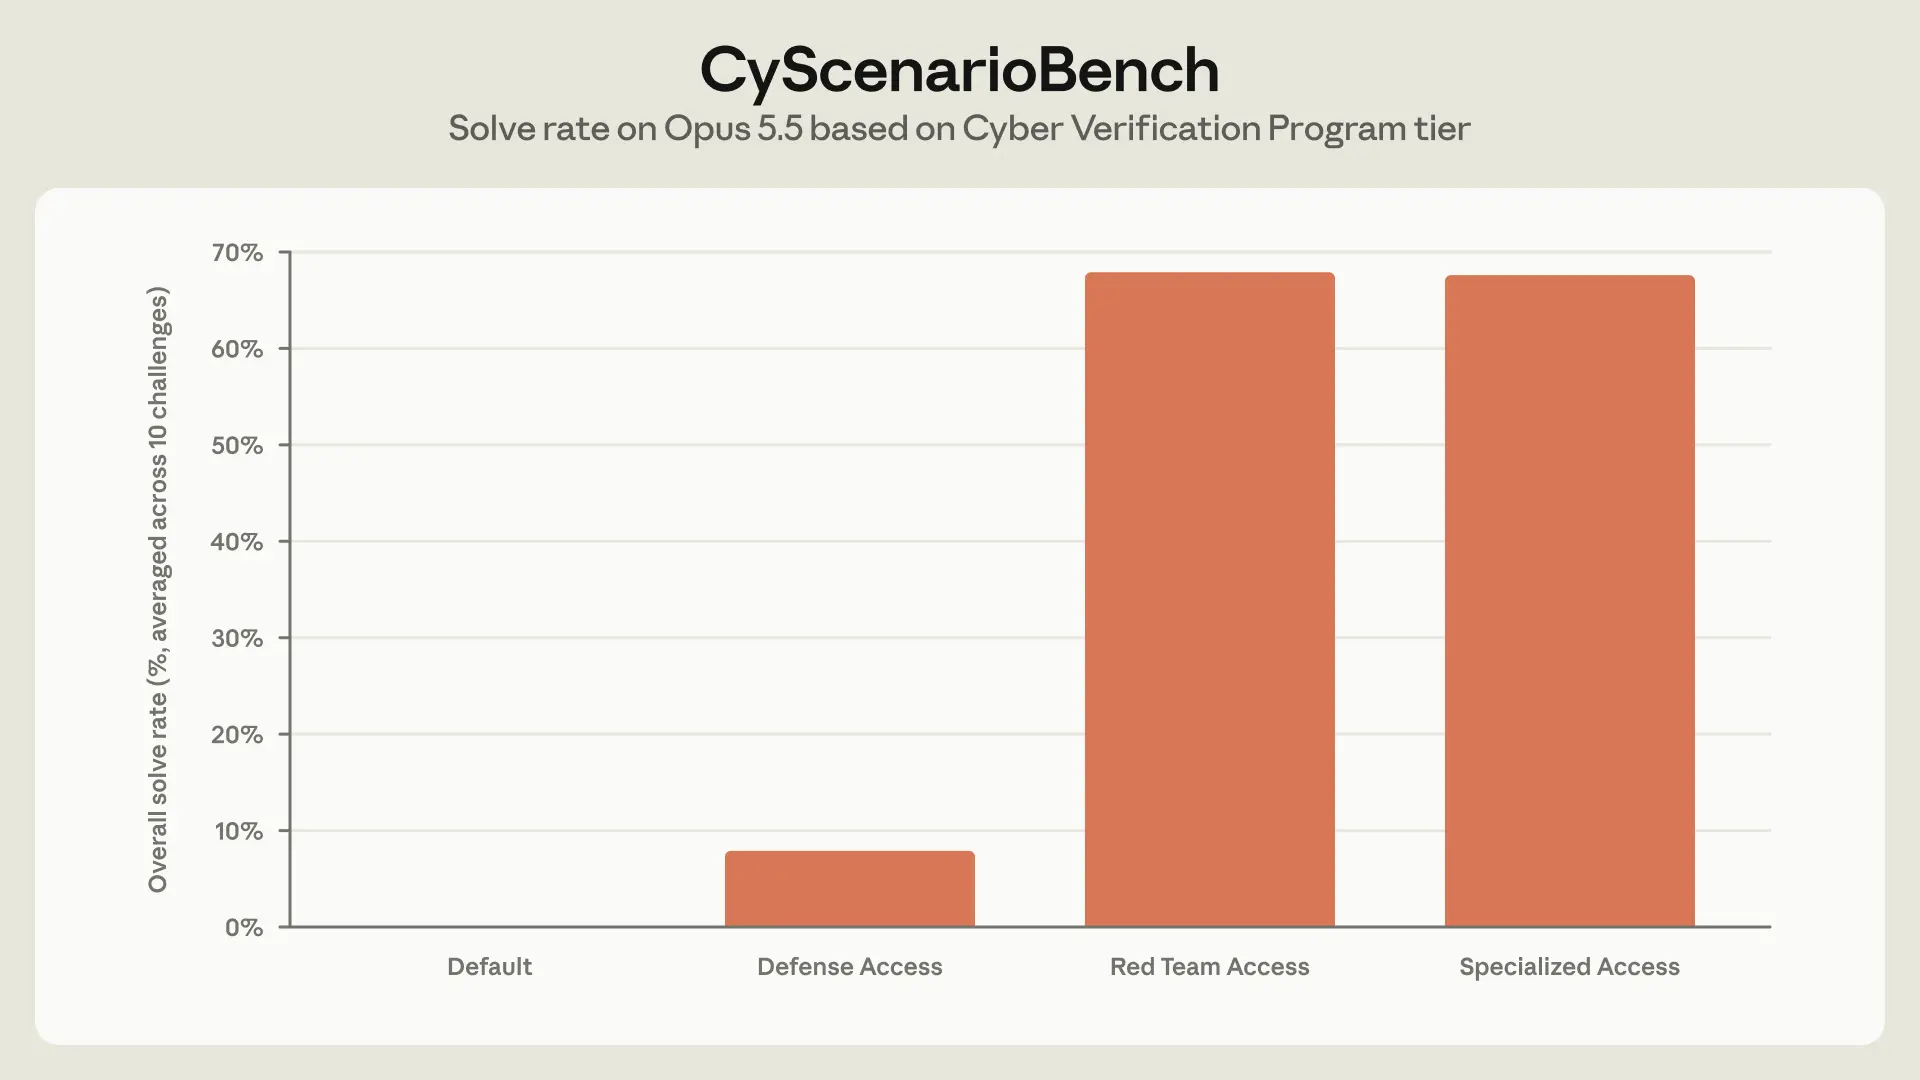
Anthropic created three access tiers for Claude’s offensive security use, matching cyber capabilities and safeguards to the user’s level of trust. Anthropic is trying to solve the difficult balance between using AI for cybersecurity and preventing misuse. The same model that helps security teams fix vulnerabilities can also help attackers break into systems. Its answer, […]
 Pierluigi Paganini
October 07, 2026
Wikimedia found unauthorized OpenAI agent activity on its platforms, including unapproved edits, proxy attempts and millions of automated API requests. Wikimedia ran its own investigation after other organizations started reporting rogue AI agents breaking into websites, and the answer came back yes, it happened here too. The foundation found unauthorized bot activity tied to OpenAI […]
 Pierluigi Paganini
October 06, 2026
Microsoft released emergency updates for Exchange Server to fix CVE-2026-96940, a high-severity flaw that can let attackers gain higher privileges. Microsoft has released out-of-band security updates for Exchange Server to fix a high-severity vulnerability tracked as CVE-2026-96940 (CVSS score of 8.8). The flaw is caused by weak authorization and can allow an authenticated attacker to […]
 Pierluigi Paganini
October 06, 2026
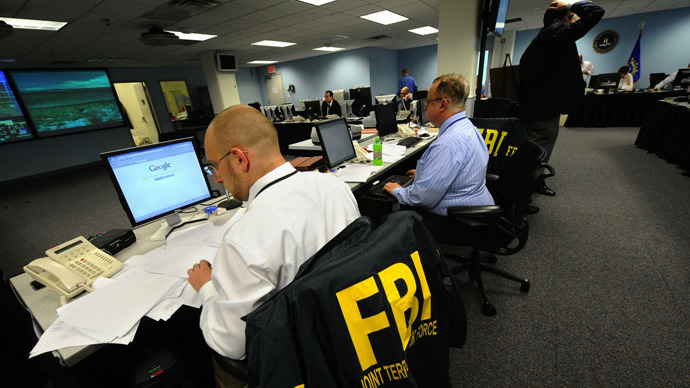
Accenture lost an FBI contract after a missed security patch exposed sensitive employee data, raising serious concerns over operational security. The FBI pulled an Accenture contractor off its account on Monday, and the reason is almost mundane compared to the damage it caused. One update didn’t get installed on time. “The Federal Bureau of Investigation […]
 Pierluigi Paganini
October 06, 2026
Dell warns that a critical DSU flaw lets attackers run code as root. Customers should patch affected PowerEdge systems as soon as possible. Dell urged customers to patch a critical flaw, tracked as CVE-2026-86360 (CVSS score of 9.6), in its System Update (DSU) tool. The vulnerability is a path traversal issue that can let attackers […]
 Pierluigi Paganini
October 06, 2026
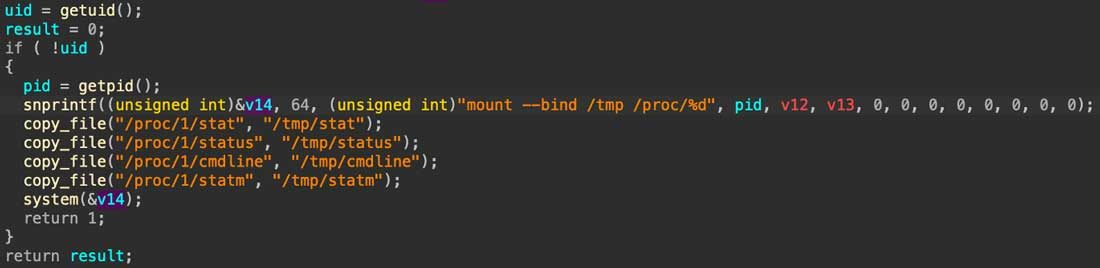
Fortinet details ClingSTUN, a Linux backdoor exploiting unpatched IoT devices and abusing public STUN servers to route traffic past NAT. FortiGuard Labs researchers spotted a Linux malware family they call ClingSTUN, and the name gives away its trick immediately. Instead of relying on a dedicated command server, the malicious code leans on STUN, the protocol […]
 Pierluigi Paganini
October 05, 2026
AI-assisted research uncovered a critical Rejetto HFS flaw that enables authentication bypass and remote code execution, now exploited in the wild. A Rejetto HFS vulnerability, tracked as CVE-2026-61500 (CVSS score of 9.3), discovered with the help of the Anthropic Mythos AI model is now being exploited in the wild, turning an interesting security research experiment […]