 Pierluigi Paganini
 October 12, 2026
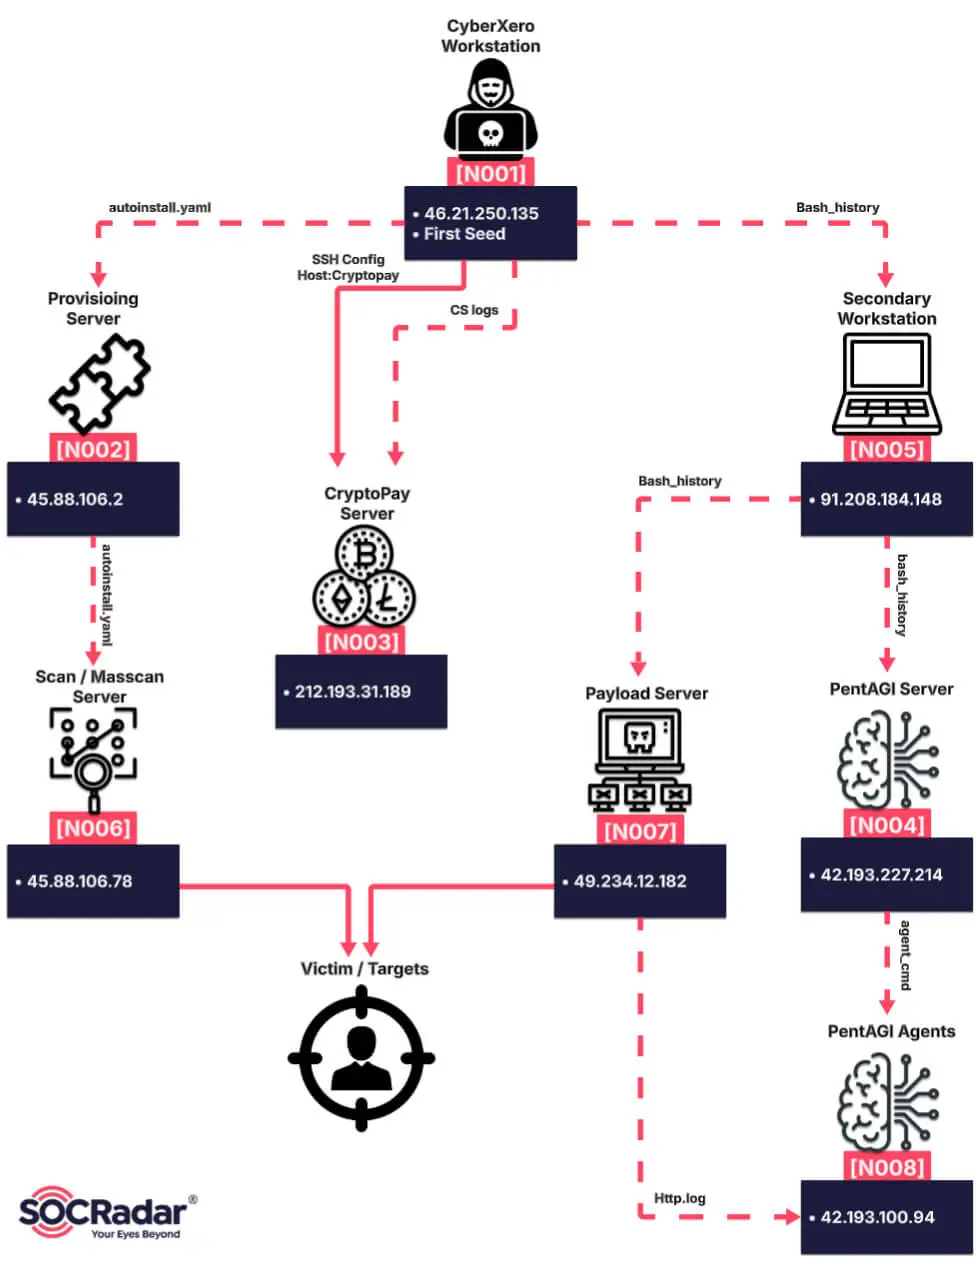
CyberXero used 51 AI agents to support cyberattacks, stealing 628,000 Ukrainian records, including sensitive data from energy infrastructure. CyberXero is an operation that combines traditional hacking tools with AI agents to carry out cyberattacks. According to SOCRadar researchers, the attackers use the same infrastructure for two different campaigns: one targets WordPress websites and e-commerce platforms […]
 Pierluigi Paganini
October 08, 2026
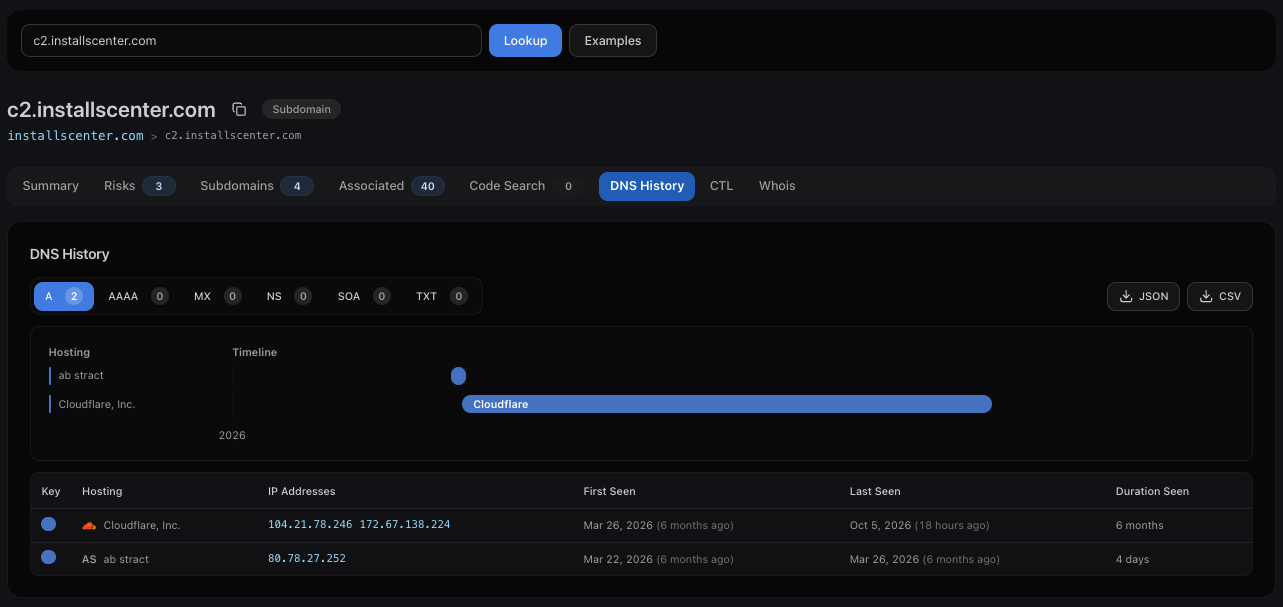
Hunt.io traced BraZetsu ‘s infrastructure and found that hosting patterns and certificate data remained useful after published IOCs became outdated. Group-IB researchers published a detailed writeup on BraZetsu back on August 31, naming it a Python framework compiled with Nuitka and tying it to a Brazilian actor called Exilware with high confidence. Hunt.io checked whether […]
 Pierluigi Paganini
June 24, 2026
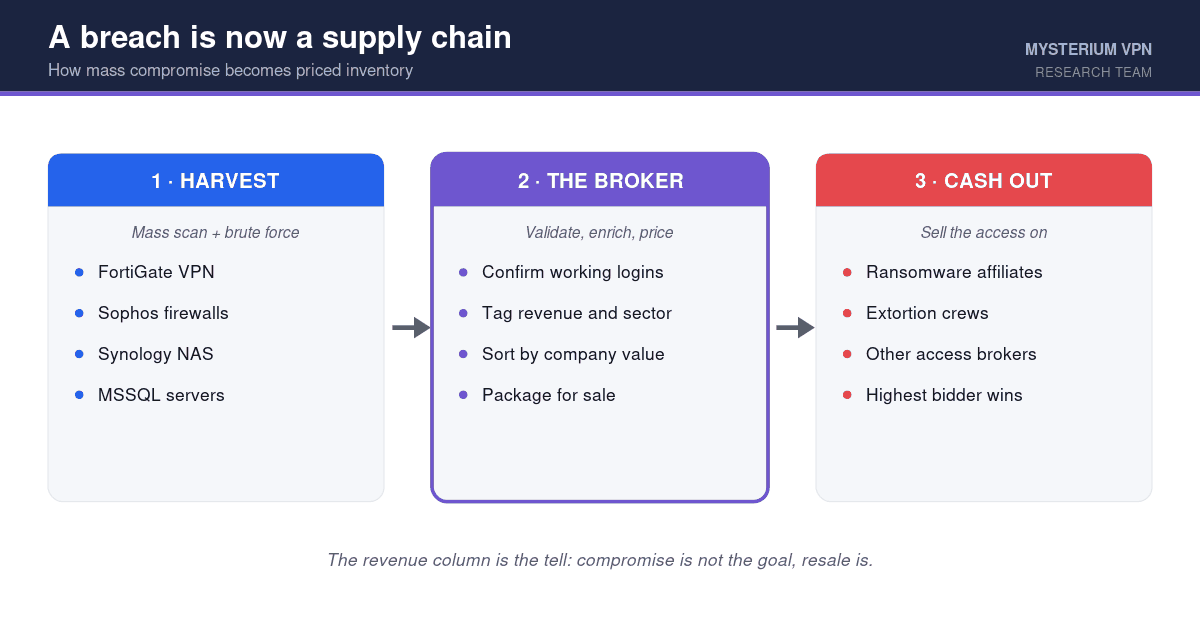
FortiBleed exposed valid credentials for 73,000+ Fortinet firewalls, revealing a large-scale access-brokering operation targeting organizations worldwide. In mid-June 2026, researcher Volodymyr “Bob” Diachenko found a live, exposed server containing working login credentials for tens of thousands of Fortinet firewalls, a data leak code-named FortiBleed. The headline number, valid remote-access logins for 73,932 devices across 21,632 […]
 Pierluigi Paganini
January 20, 2026
A Jordanian man pleaded guilty in the US to selling illegal access to 50 compromised enterprise networks after an undercover sting. A Jordanian national Feras Khalil Ahmad Albashiti (40), living in Georgia, pleaded guilty in a US court to acting as an access broker, selling unauthorized access to the networks of at least 50 companies. […]
 Pierluigi Paganini
April 25, 2025
A zero-day in SAP NetWeaver is potentially being exploited, putting thousands of internet-facing applications at risk. Researchers warn that a zero-day vulnerability, tracked as CVE-2025-31324 (CVSS score of 10/10), in SAP NetWeaver is potentially being exploited. Thousands of internet-facing applications are potentially at risk. The flaw in SAP NetWeaver Visual Composer Metadata Uploader stems from a lack […]